

RED_HAWK
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
crawlerdns-analysisinformation-gathering+5
3.8k
tuhinshubhra/red_hawkAll in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 im-hanzou/fubucker
Automatic Mass Tool for checking vulnerability in CVE-2022-1386 - Fusion Builder < 3.6.2 - Unauthenticated SSRF
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 atarantini/wpbf
Remotely test password strength of WordPress bloging software
 ggusoft/inforfinder
Inforfinder is a tool to collect information of any domains pointing at some server (ip, domain, range, file). Is able to detect all domains pointing…
 alessiodallapiazza/wpscan
WordPress security scanner that enumerates vulnerable plugins, themes, and users to identify misconfigurations and known vulnerabilities for…
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
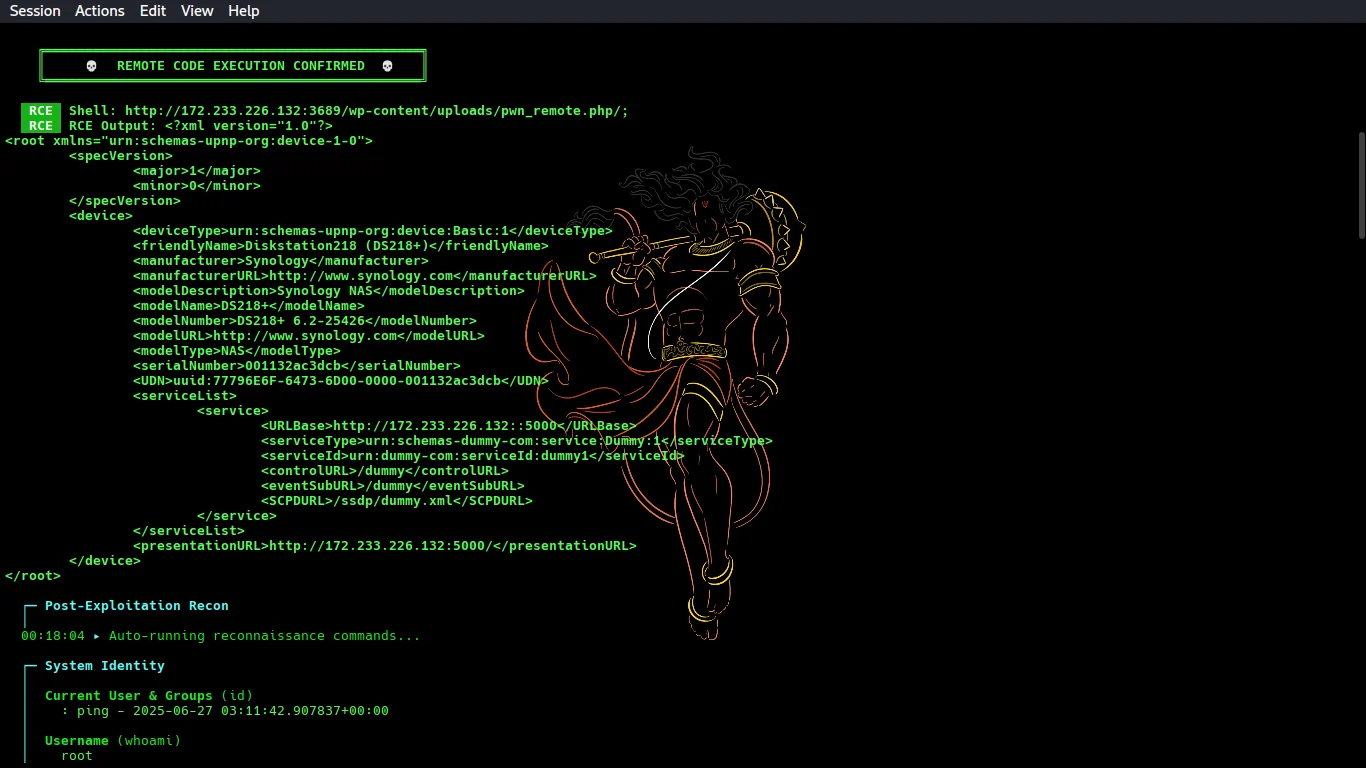 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 taurusomar/wpjuicer
WP Juicer Tool for quick scanning of confidential information on WordPress endpoints.
 k3ystr0k3r/cve-2017-5487-exploit
A PoC exploit for CVE-2017-5487 - WordPress User Enumeration.
 shawnng078-ops/cve-2024-28000-exploit-lab
Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 pog007/cve-2023-5561-poc
WordPress does not properly restrict which user fields are searchable via the REST API, allowing unauthenticated attackers to discern the email…
 gh-ost00/cve-2024-27954
Automatic Plugin for WordPress < 3.92.1 Multiples Vulnerabilities
 own2pwn-fr/wp2shell-detect
Blackbox, non-intrusive detector for wp2shell (WordPress core pre-auth RCE, CVE-2026-63030 / CVE-2026-60137). Detection only.