
CVE-2026-12227
 murrez/cve-2026-12227
Python 3 PoC and scanner for CVE-2026-12227, an unauthenticated local file inclusion in WordPress Visual Composer Website Builder via the…
exploitationinformation-gatheringpenetration-testing+5
murrez/cve-2026-12227Python 3 PoC and scanner for CVE-2026-12227, an unauthenticated local file inclusion in WordPress Visual Composer Website Builder via the…
 themehackers/cve-2025-24071
Windows File Explorer Spoofing Vulnerability (CVE-2025-24071)
 x00byte/putscanner
A tool that identifies writable web directories in Apache Tomcat via HTTP PUT method [CVE-2025-24813]
 th-secforge/cve-2025-24071
Security Vulnerability Report: CVE-2025-24071 - Windows File Explorer Spoofing Vulnerability
 abdugafforov-bobur/cve-2026-65694-poc
PoC for CVE-2026-65694 — Microweber CMS (<=2.0.20) unauthenticated path traversal → arbitrary file read (.env / secrets)
 hugobond/cve-2024-31497-poc
Proof Of Concept that exploits PuTTy CVE-2024-31497.
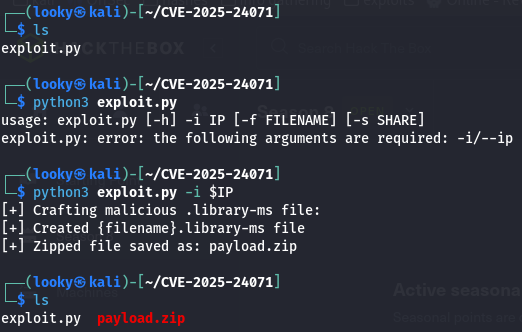 looky243/cve-2025-24071-poc
CVE-2025-24071 Proof Of Concept
 xdev05/cve-2020-3452-poc
Automates downloading and running an Nmap NSE script to scan hosts for CVE-2020-3452 vulnerability, using a list of target hosts.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 kathanp19/gxss
A tool to check a bunch of URLs that contain reflecting params.
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
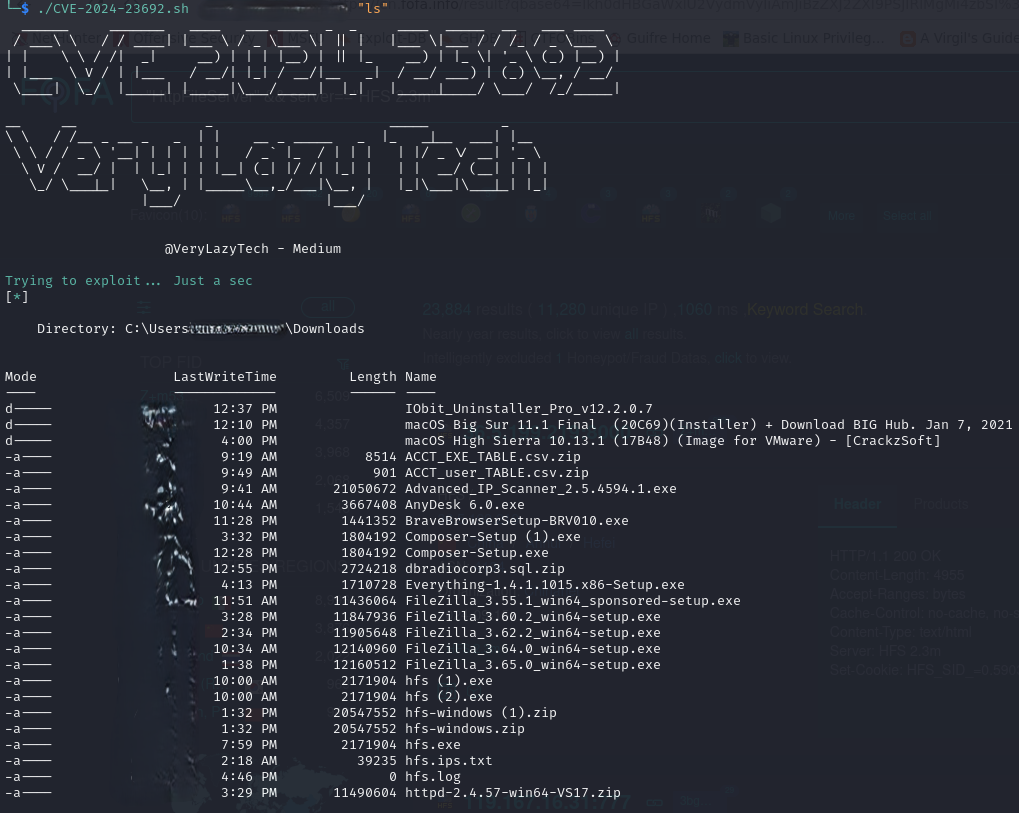 verylazytech/cve-2024-23692
POC - Unauthenticated RCE Flaw in Rejetto HTTP File Server - CVE-2024-23692
 0x0jackal/cve-2022-24716
Arbitrary File Disclosure Vulnerability in Icinga Web 2 <2.8.6, <2.9.6, <2.10
 lhc321-source/cve-2024-36837
Proof-of-concept exploit for CVE-2024-36837, an unauthenticated arbitrary file read vulnerability in Zhilianyun SRM2.0. Includes batch scanning and…
 willygailo/wg-cve-2026-1555-linux
Automated exploit toolkit for CVE-2026-1555, a critical unauthenticated file upload RCE in the WebStack WordPress theme. Features PyQt5 GUI,…
 harisaidhin/poc_cve-2025-68645
Zimbra Path Traversal (CVE-2025-68645) - Unauthenticated file read vulnerability in Zimbra Collaboration Suite
 th-secforge/cve-2025-30208
CVE‑2025‑30208 is a medium-severity arbitrary file read vulnerability in the Vite development server (a popular frontend build tool)
 crow5-oss/cve-2025-68645
Proof-of-Concept scanner for CVE-2025-68645, detecting Local File Inclusion (LFI) in Zimbra Collaboration Suite via the /h/printcalendar endpoint…