
HijackLibs
 wietze/hijacklibs
Project for tracking publicly disclosed DLL Hijacking opportunities.
curated-resourceseducationinformation-gathering+3
wietze/hijacklibsProject for tracking publicly disclosed DLL Hijacking opportunities.
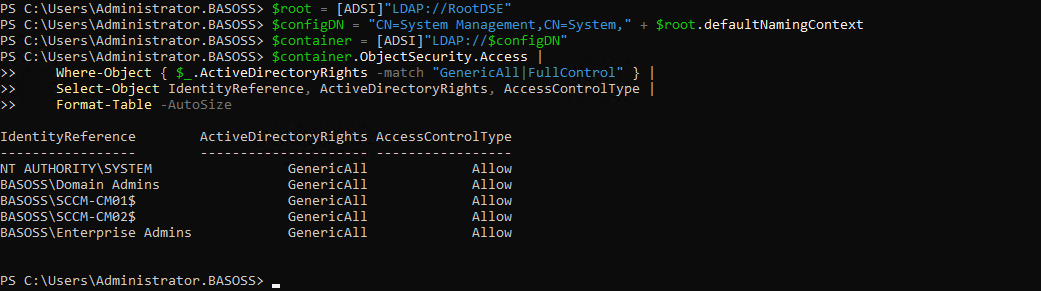 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 daddycocoaman/azbelt
AAD related enumeration in Nim
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
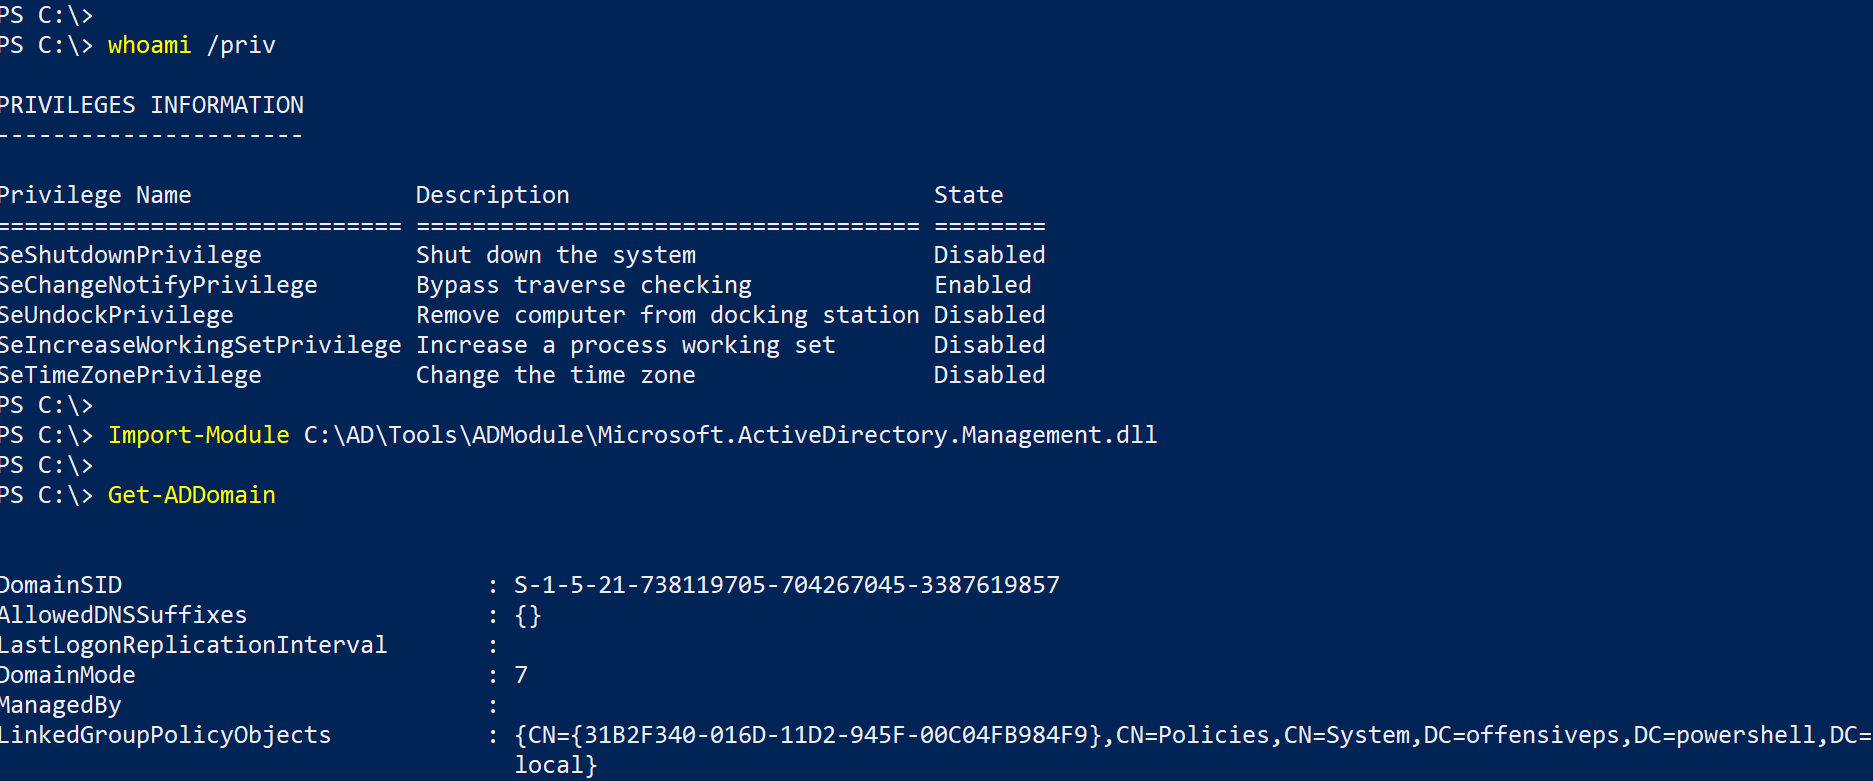 samratashok/admodule
Microsoft signed ActiveDirectory PowerShell module