

OpenHunterAI
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
ai-securityapi-securityapi-security-testing+9
328
lumoslab-innovation/openhunteraiLocal-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 dylvie/cve-2026-30824-flowise-nvidia-nim-authentication
A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…
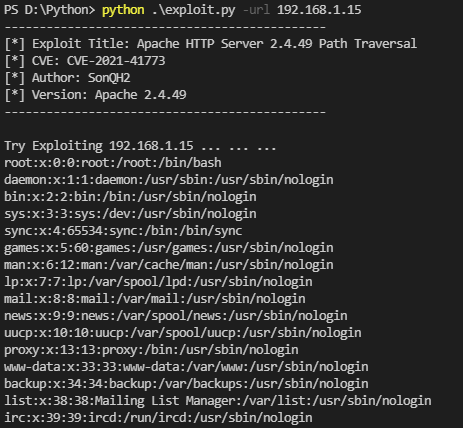 zer0qs/cve-2021-41773
Exploit script for CVE-2021-41773 (Apache Path Traversal) with Docker setup and multi-target scanning via URL or list.

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 oscerd/cve-2026-64640
Reproducer for CVE-2026-64640 — Apache Polaris Iceberg REST register/register-view vends storage credentials and reads an attacker-chosen metadata…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 cyeezy08/kimai-cve-2026-49865-poc
PoC exploits for CVE-2026-52824 (GHSA-jr9p-4h4j-6c58) — Kimai time-tracking default APP_SECRET authentication bypass affecting versions ≤ 2.57.0
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 regaan/cve-2026-33340
CVE-2026-33340: Critical SSRF in lollms-webui /api/proxy - Unauthenticated arbitrary request forgery (CVSS 9.1)
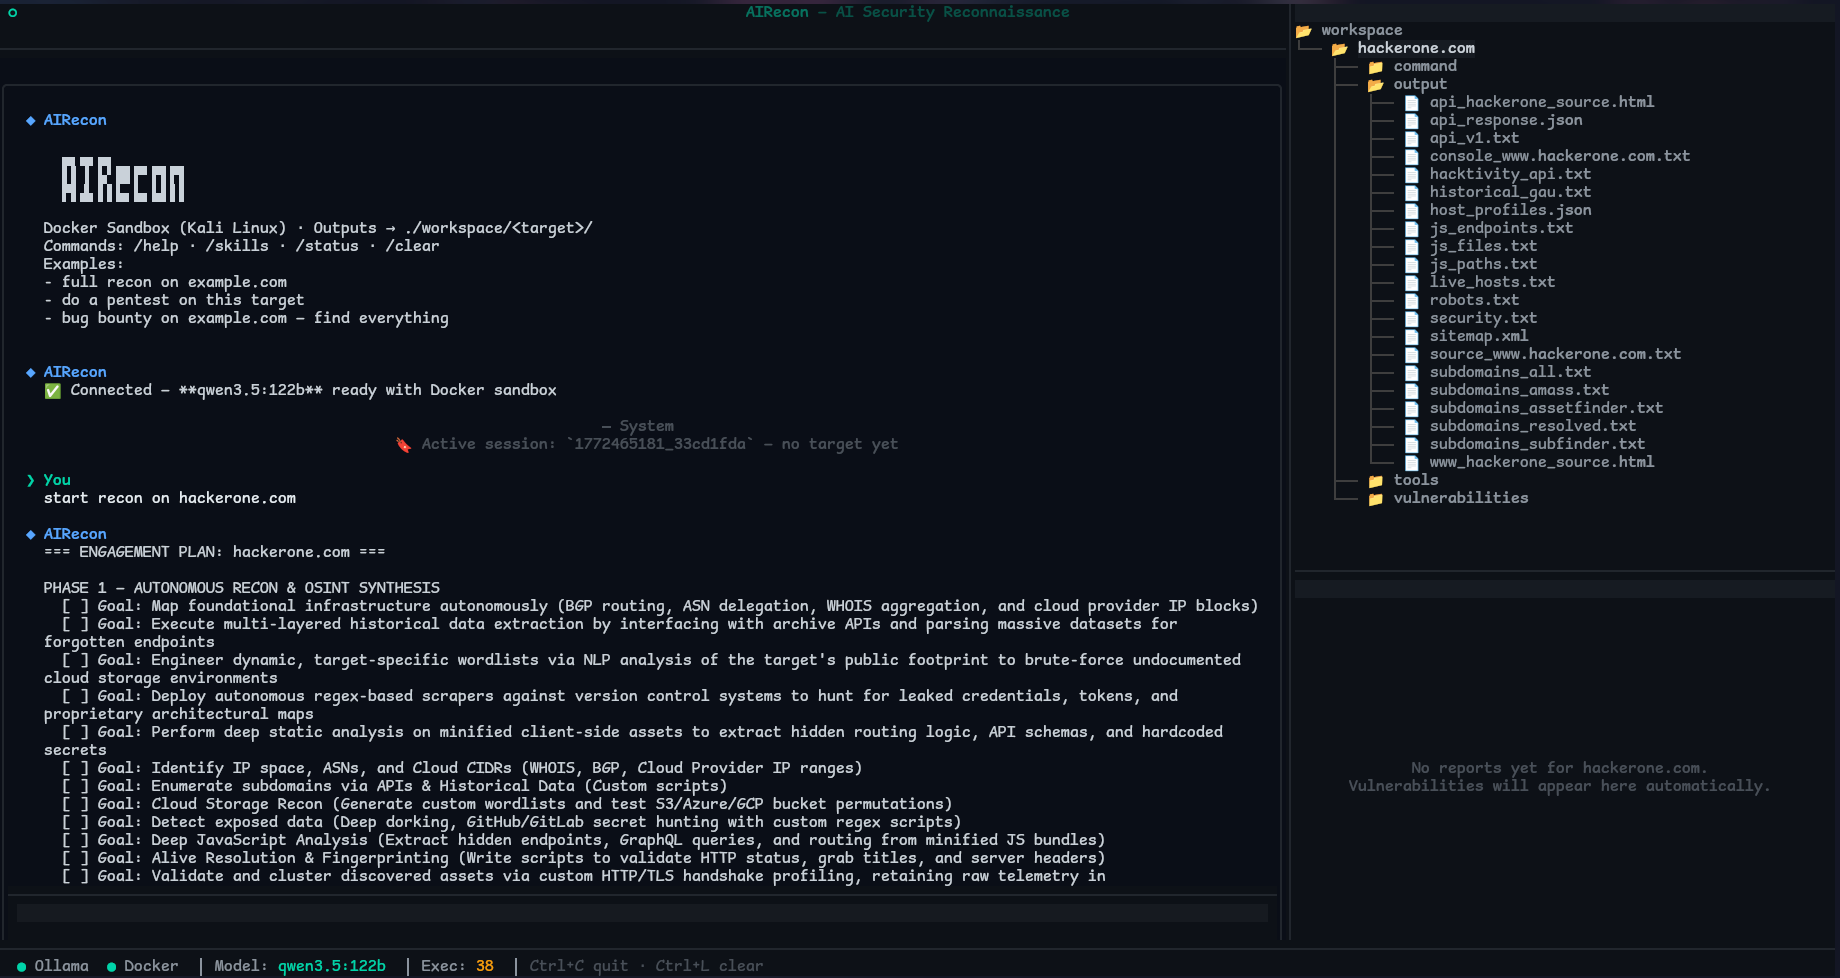 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
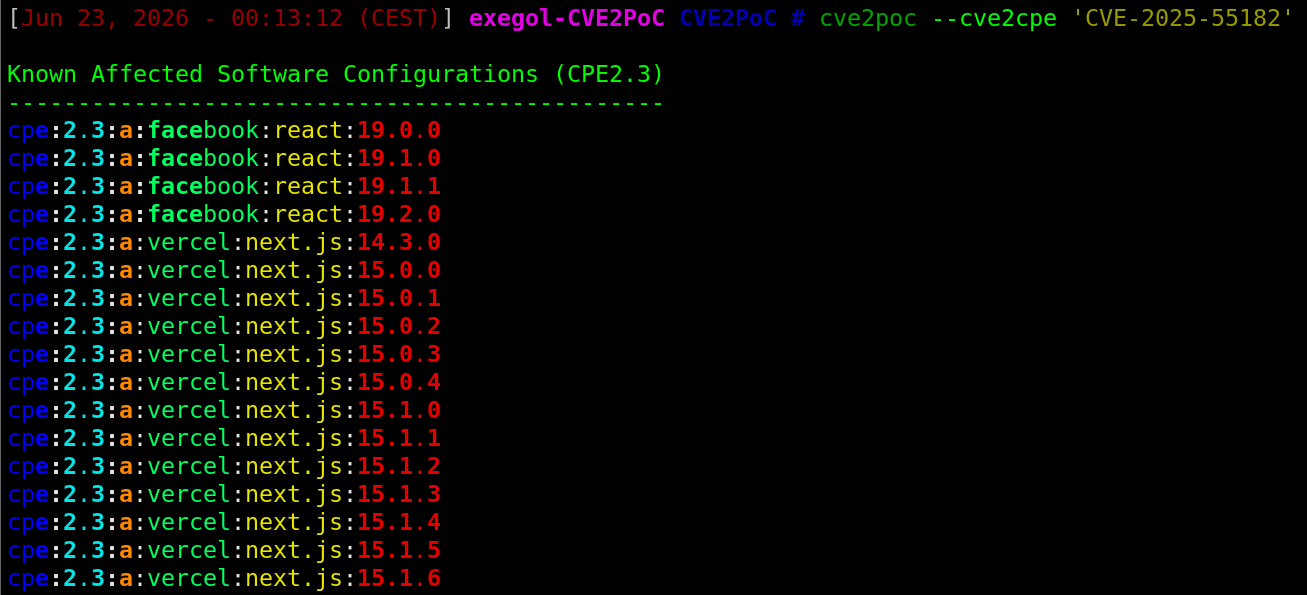 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
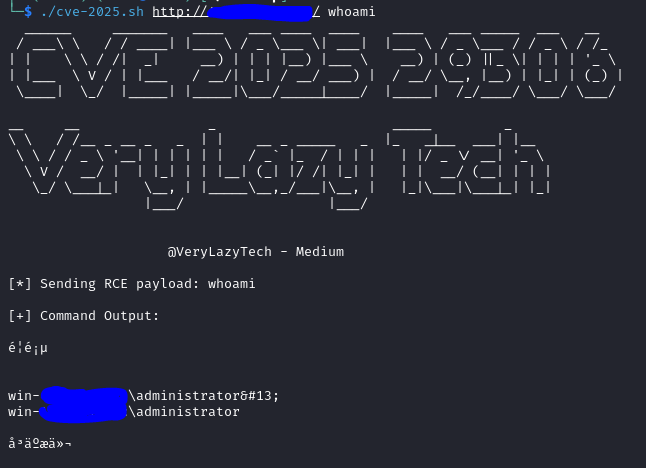 verylazytech/cve-2025-29306
Proof-of-concept exploit for FoxCMS v1.2.5 remote code execution via the index.html component, with FOFA dork for target discovery.
 erikwynter/cve-2023-22515-scan
Scanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence