ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
988
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 trappsec-dev/trappsec
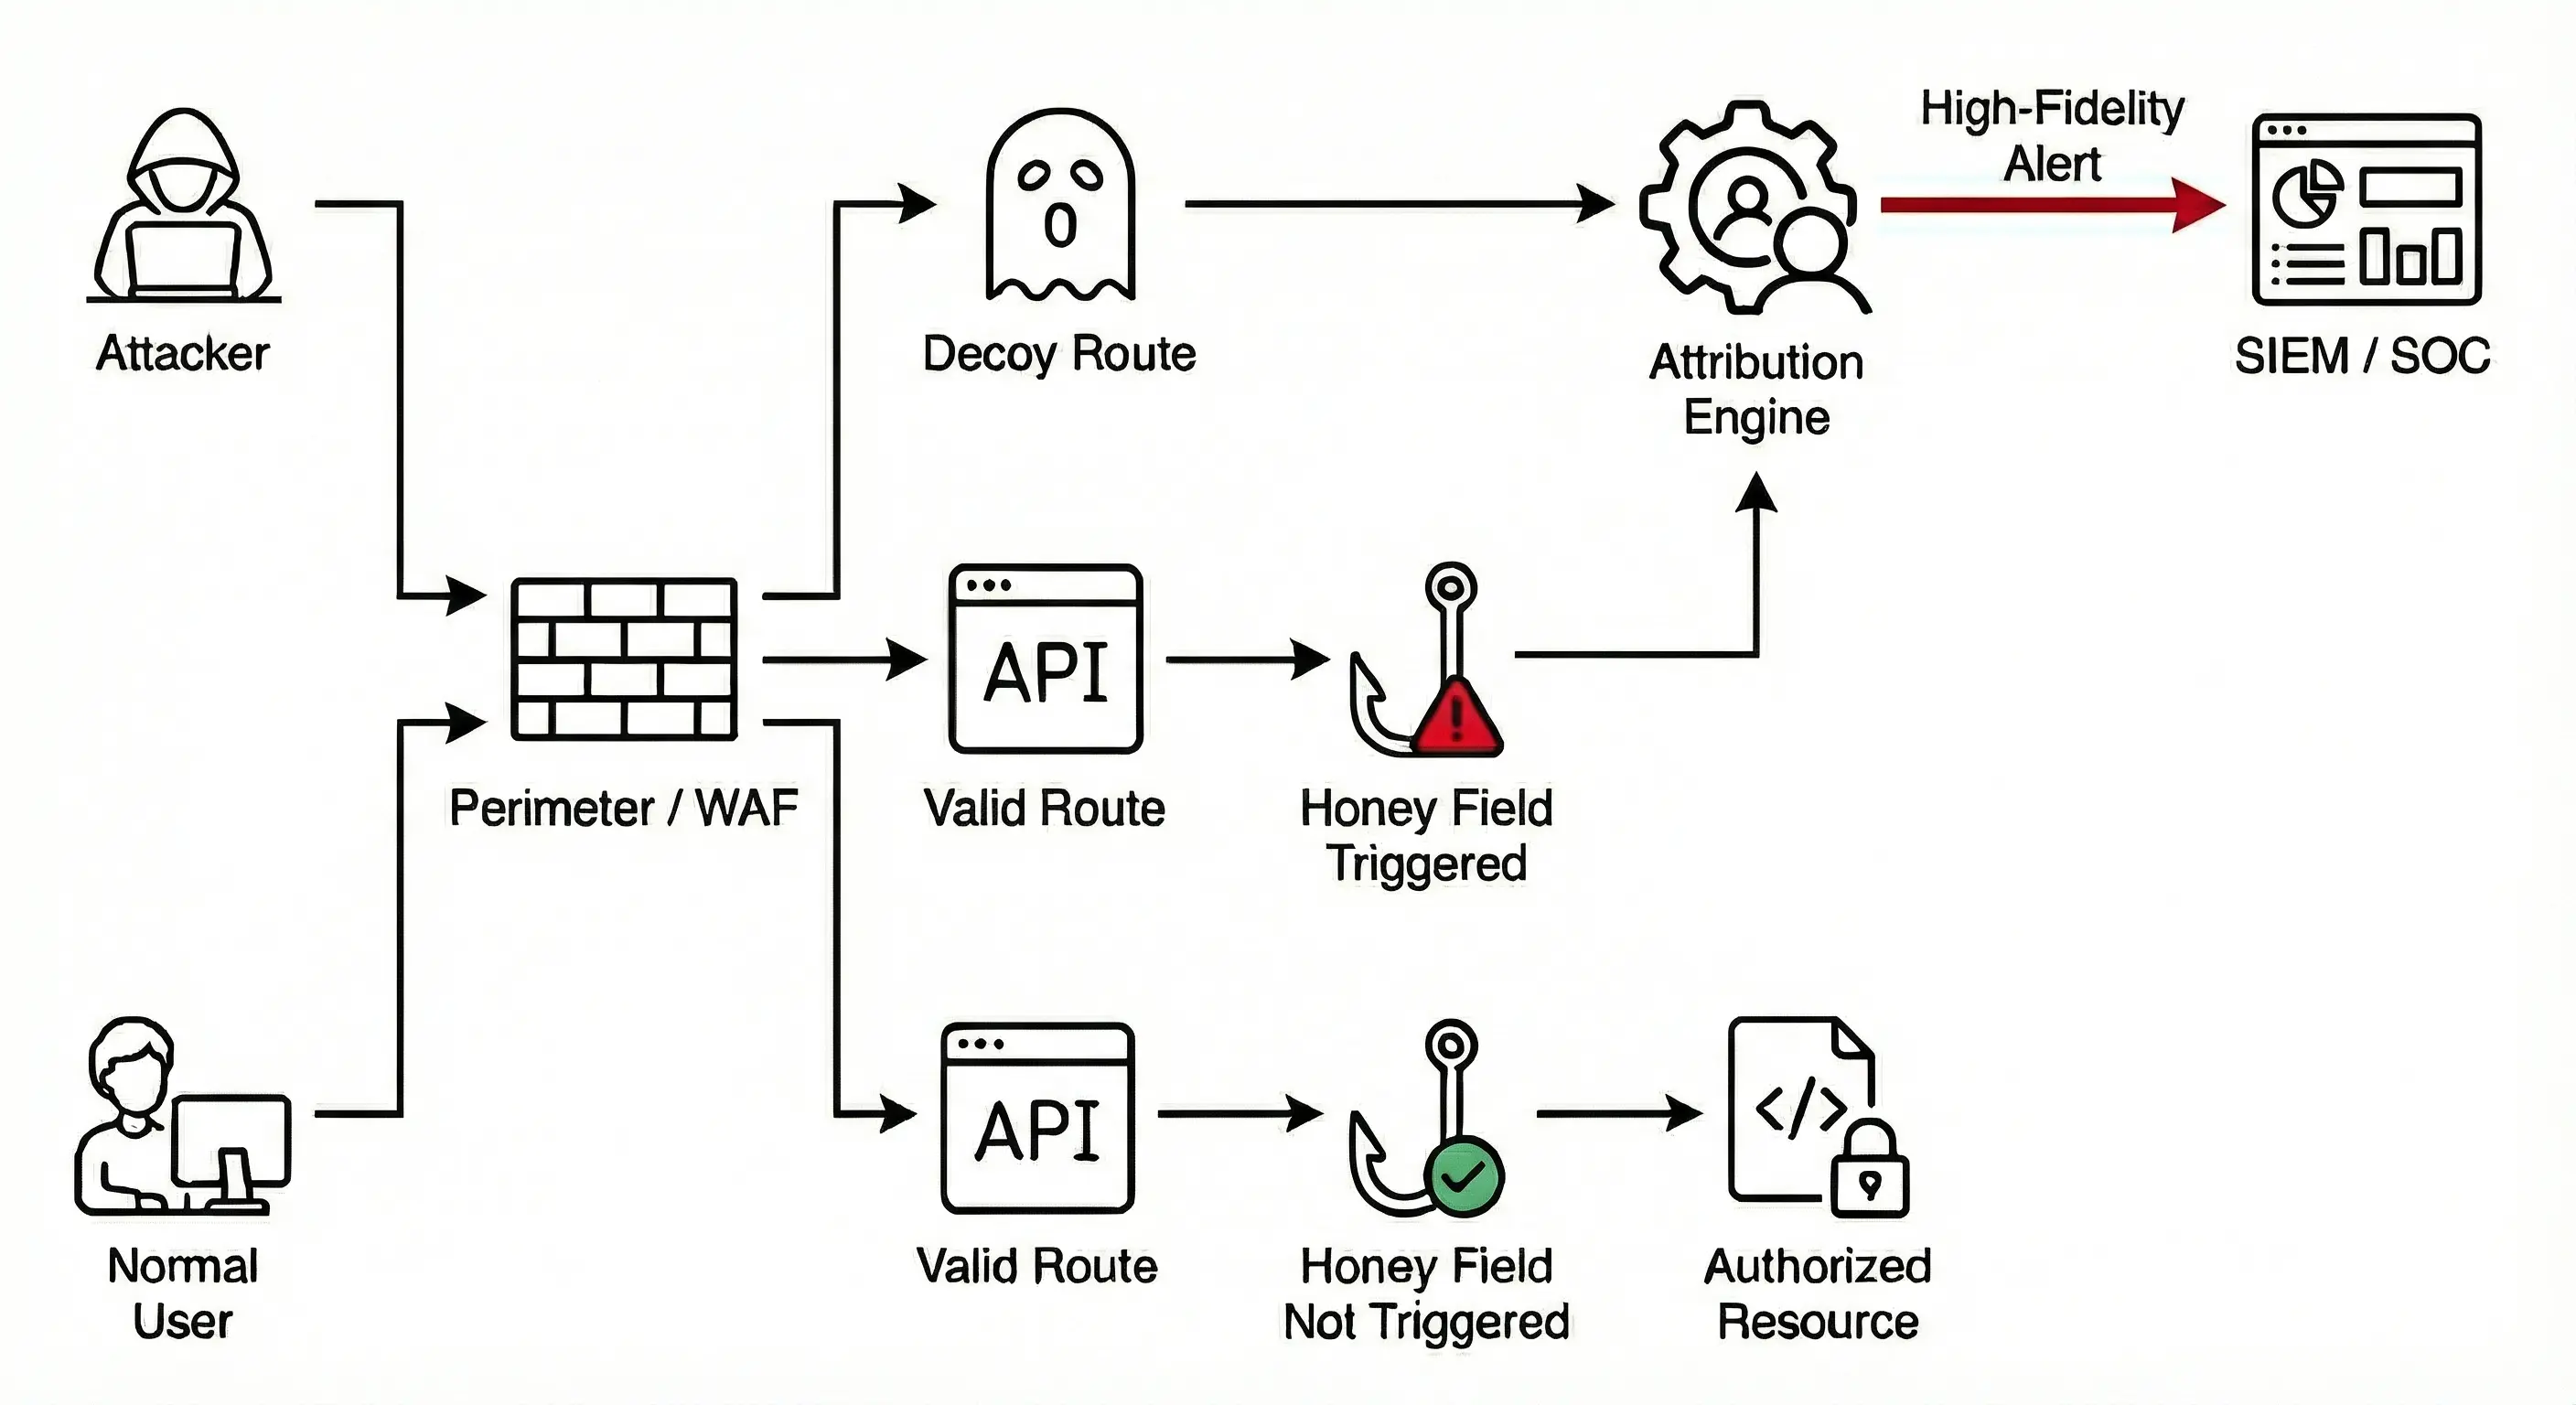
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
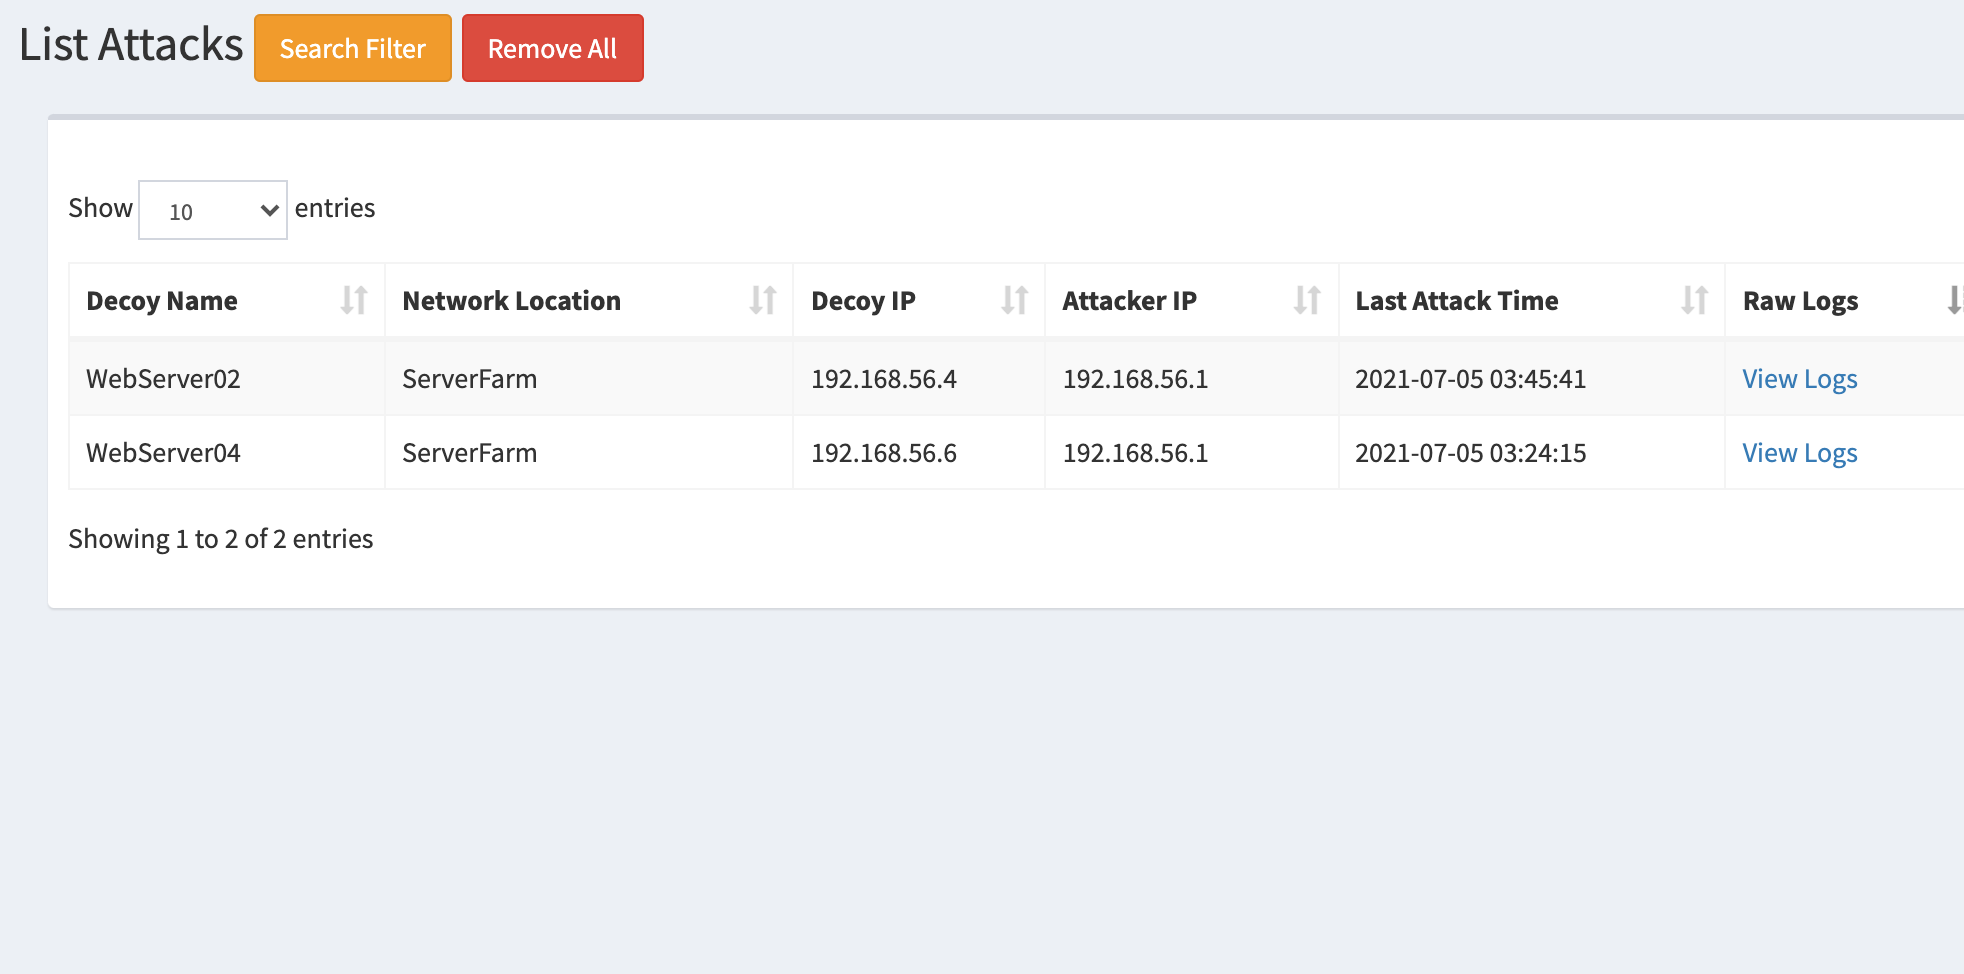 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.