
Argus
 divinelabio/argus
The Ultimate Information Gathering Toolkit
crawlerdns-subdomain-enumerationemail-harvesting+8
divinelabio/argusThe Ultimate Information Gathering Toolkit
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 lloydlabs/process-enumeration-stealth
Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
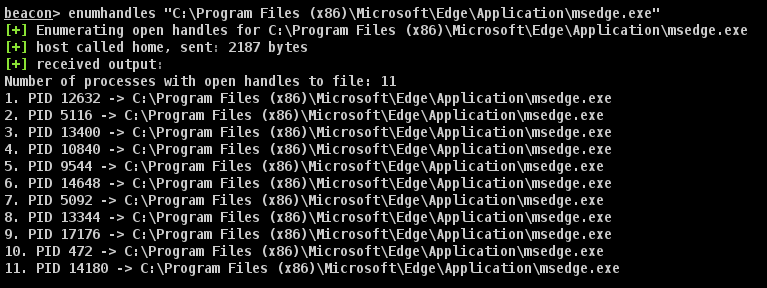 octoberfest7/enumhandles_bof
Cobalt Strike BOF for live Windows enumeration of open file handles, revealing which process has locked a target file on disk during…
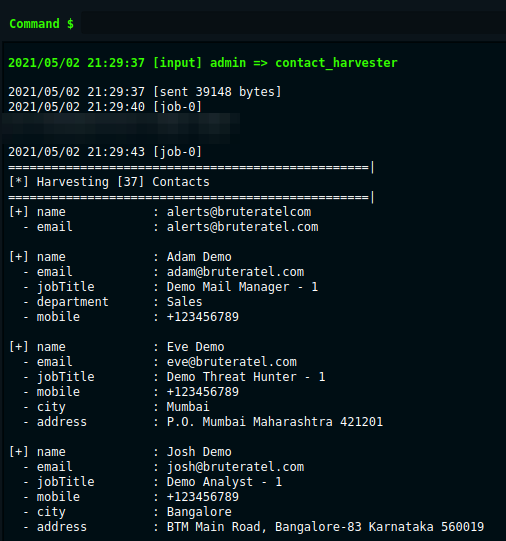 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
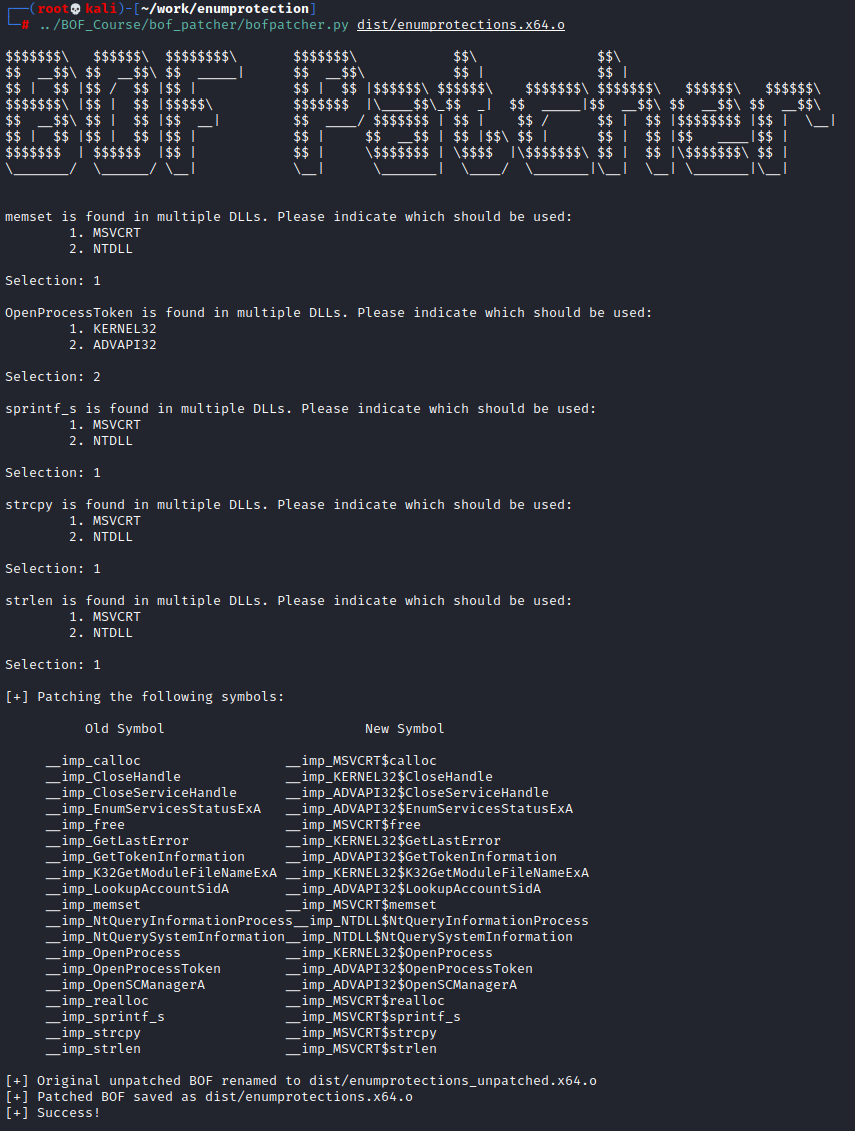 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.

 al14s/rawr
Rapid Assessment of Web Resources
 tanasescualexandrugabriel/vulnerability-assessment-and-osint-cve-2012-1823
This repository documents the process of identifying, analyzing, and gathering Open Source Intelligence (OSINT) on a specific security vulnerability…
 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
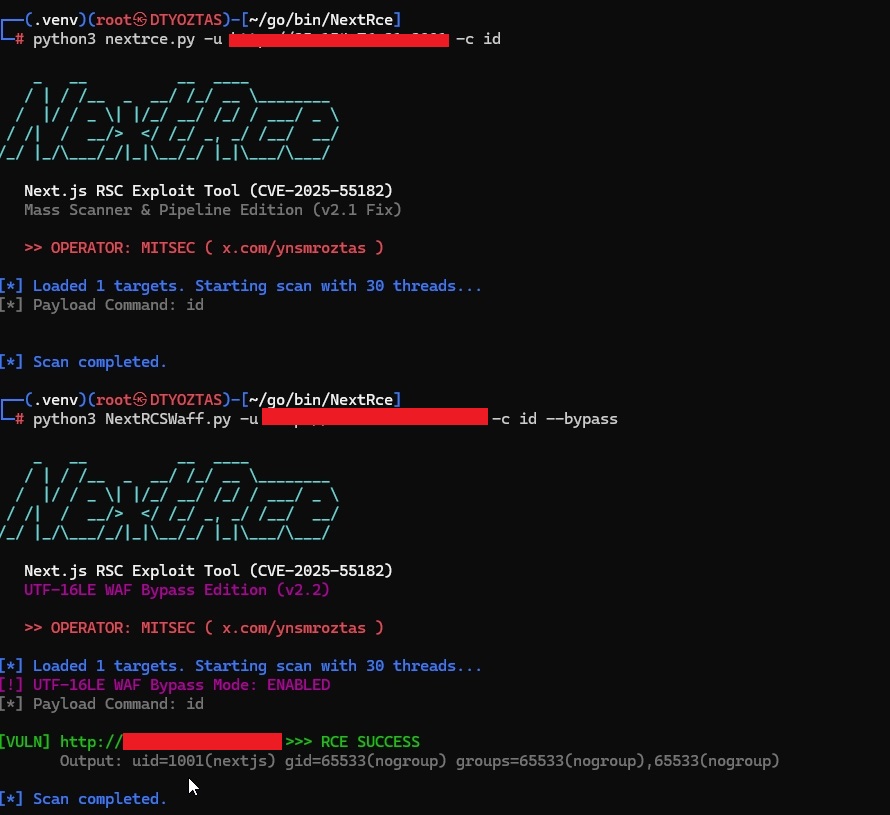 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 josekutty-k/frontpage-server-extensions-vulnerability-scanner
Python script to scan for CVE-2000-0114 vulnerability in Frontpage Server Extensions. Automates subdomain enumeration and vulnerability scanning…
 sumeet-darekar/cve-2025-30208
mass scan for CVE-2025-30208
 mind2hex/cve-2023-38035-mobileiron-rce
Script to exploit CVE-2023-38035
 jhaddix/lazyrecon
This script is intended to automate your reconnaissance process in an organized fashion
 baroi-ai/cve-2024-42657
CVE-2024-42657 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the lack of…
 vanshuk-bhagat/apache-http-server-vulnerabilities-cve-2021-41773-and-cve-2021-42013
In this project, I documented a detailed penetration testing process targeting Apache HTTP Server vulnerabilities, specifically CVE-2021-41773 and…