

LBFH
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
educationexploitationhash-analysis+9
naimkowshik/lbfhAbout All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 emrekybs/veiled-eye
OSINT identity investigation tool. Pivot from an e-mail, username, phone or wallet across 46 sources into one profile and relationship graph.
 pennacle-security/summit
Open-source web security testing platform: proxy, scanner and fuzzer in one CLI. By Pennacle Security.
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 ambitsecurity/jshound
Find every API request a web app makes, from the JavaScript it ships: method, URL, body, headers and GraphQL operations. One command.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 crypt0p3g/adnullenum
One-pass anonymous Active Directory enumeration over SAMR and LSARPC — null session, no credentials, with structured reusable output.
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
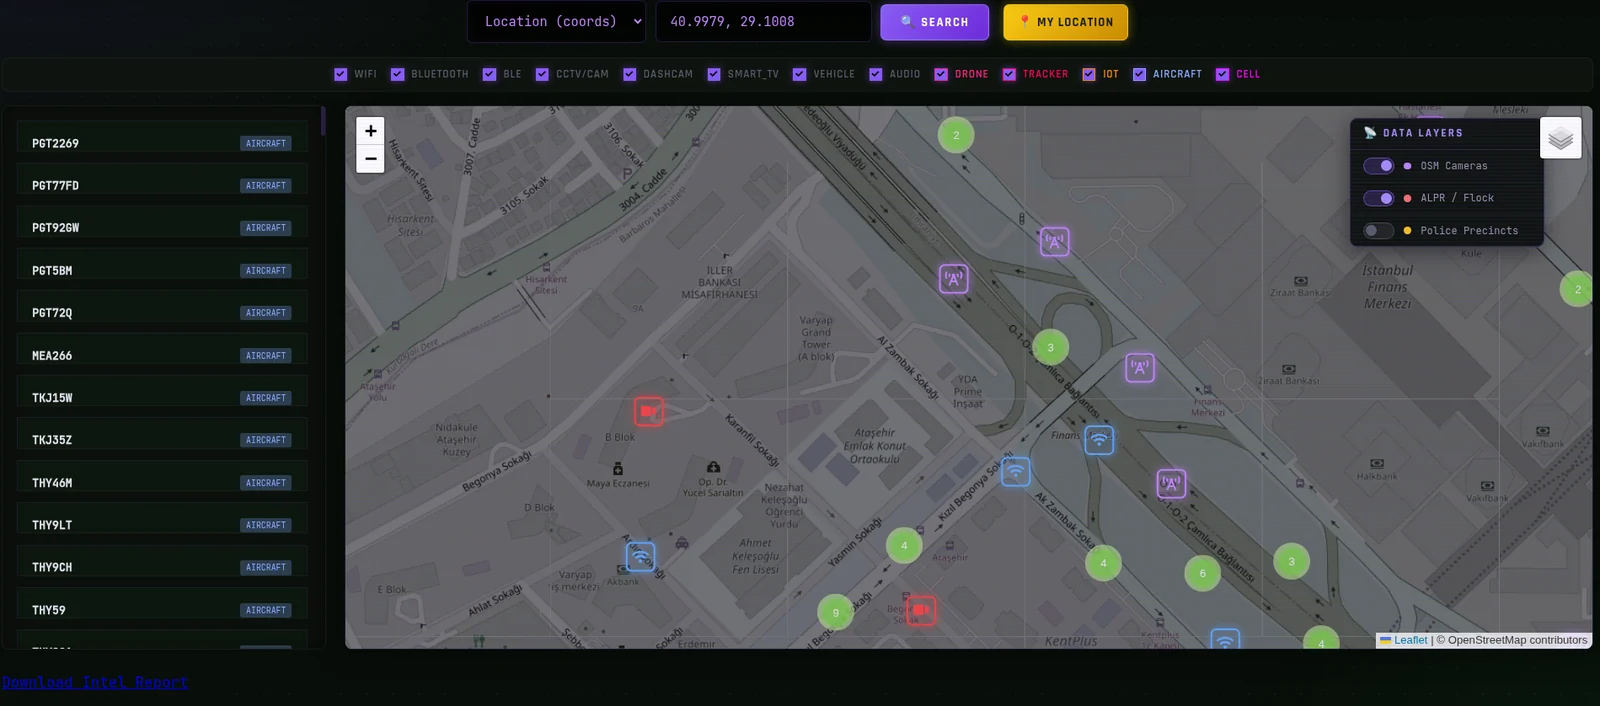 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 keraattin/cve-2026-33032
One missing function call on the route registration was enough to turn the MCP interface into an unauthenticated RCE gateway.
 al4n4n/cve-2026-25253-research
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click RCE on OpenClaw via Cross-Site WebSocket Hijacking. Includes attacker server and…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.