

LFITester
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
crawlerexploitationfuzzing+7
112
kostas-pa/lfitesterPython3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 affolter-engineering/xssearch
Rust-based XSS scanner with context-aware payload selection, WAF detection and bypass, crawling, blind XSS callbacks, and static DOM sink analysis.
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 murrez/cve-2026-18143
Python PoC that checks and exploits CVE-2026-18143, an unauthenticated arbitrary file upload in Addify Request a Quote for WooCommerce ≤ 2.9.2 via…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 e4zyy/project-cve-2026-50751
IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 chiefyoru/exploit-cve-2026-56705
CVE-2026-56705 — Adminer < 5.4.3 Unauthenticated RCE via MSSQL PDO DSN Injection
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 al4n4n/cve-2026-25253-research
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click RCE on OpenClaw via Cross-Site WebSocket Hijacking. Includes attacker server and…
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
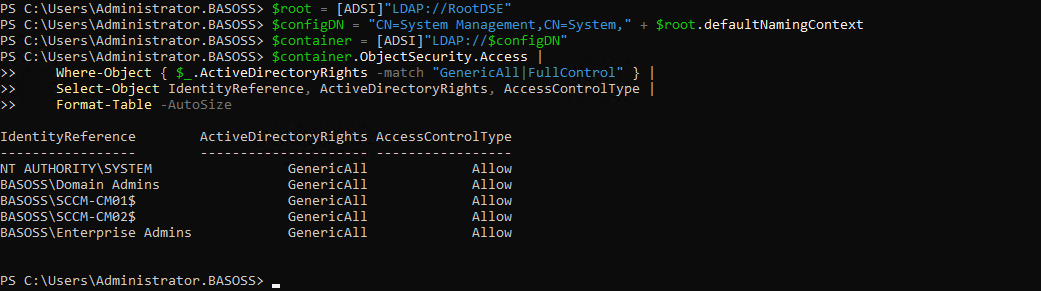 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…