
GHunt
 mxrch/ghunt
Async offensive Google framework for OSINT, enabling email/Gaia ID/Drive/geolocation reconnaissance via CLI or Python library with JSON export.
email-harvestinginformation-gatheringosint+4
19.8k6 months ago
mxrch/ghuntAsync offensive Google framework for OSINT, enabling email/Gaia ID/Drive/geolocation reconnaissance via CLI or Python library with JSON export.
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 cisagov/findcdn
Scans domains to identify which Content Delivery Network (CDN) they use by fingerprinting HTTPS headers, CNAME records, and WHOIS data, with JSON…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
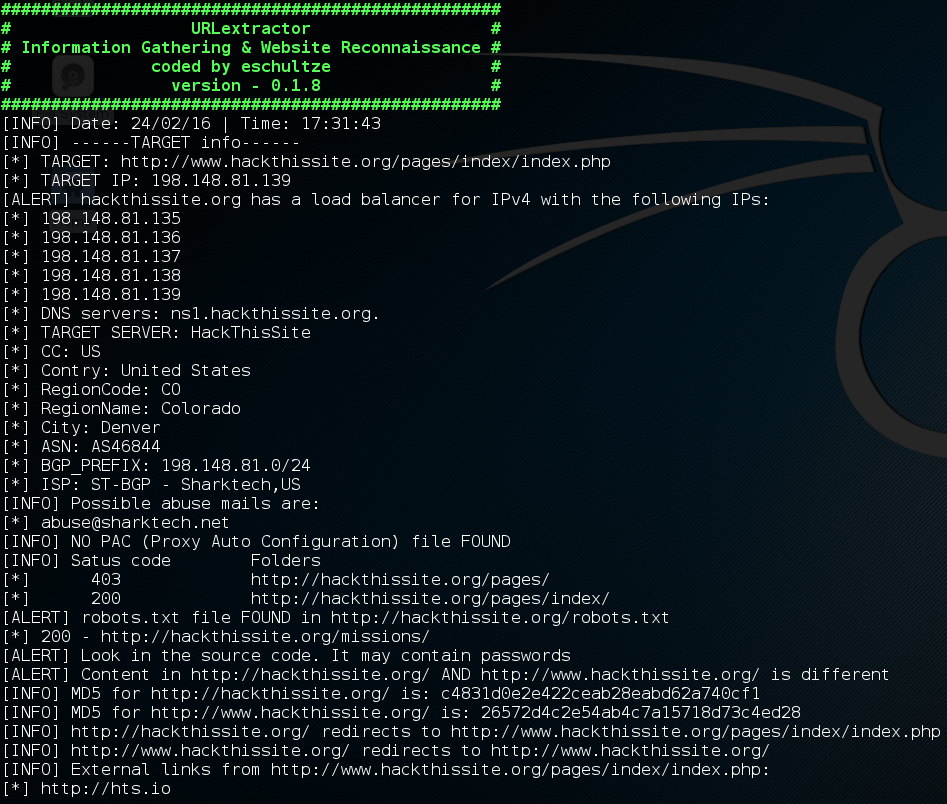 eschultze/urlextractor
Information gathering & website reconnaissance | https://phishstats.info/
 kathanp19/jsfscan.sh
Automation for javascript recon in bug bounty.
 tuhinshubhra/wpintel
Chrome extension designed for WordPress Vulnerability Scanning and information gathering!
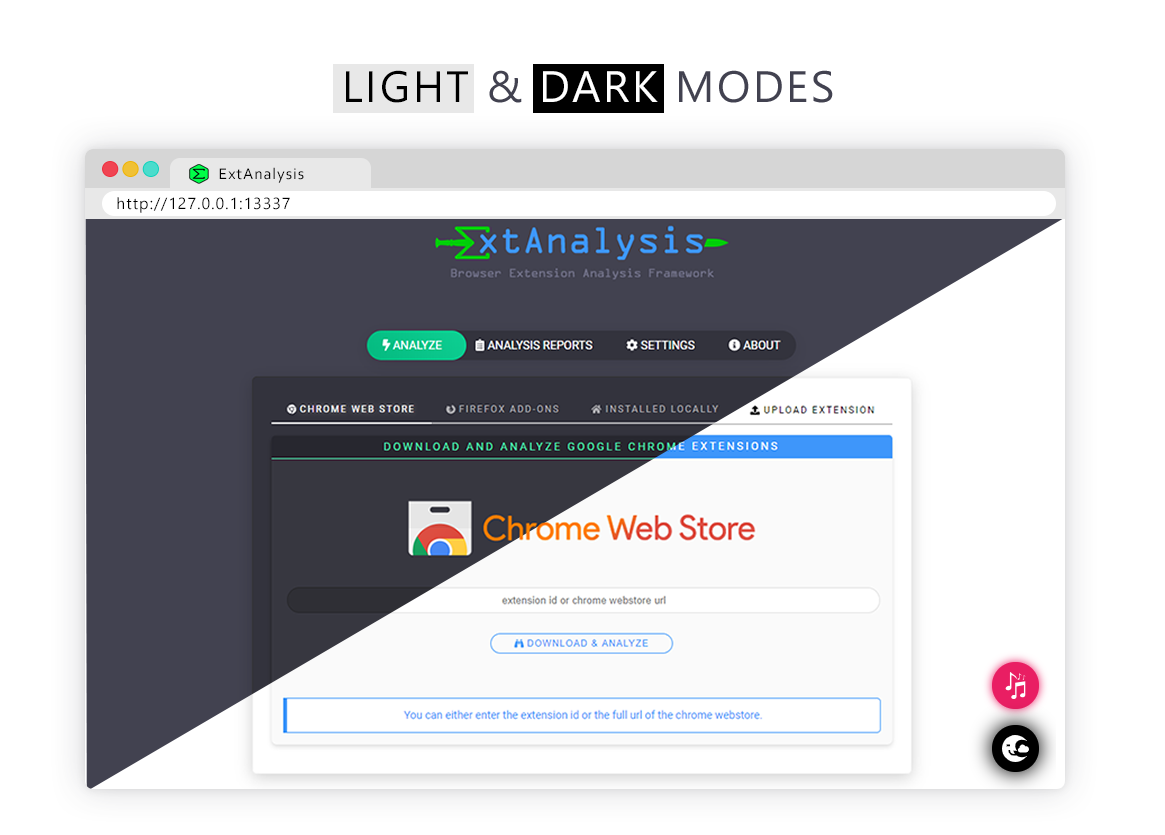 tuhinshubhra/extanalysis
Browser Extension Analysis Framework - Scan, Analyze Chrome, firefox and Brave extensions for vulnerabilities and intels
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
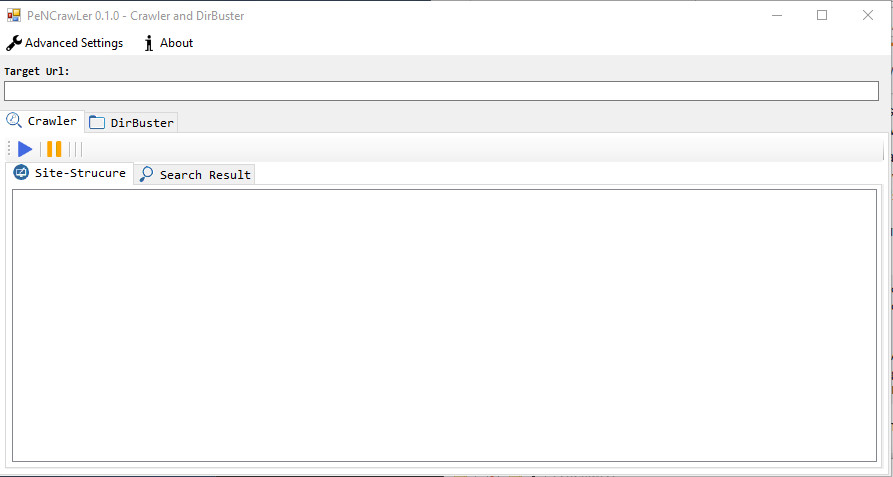 them4hd1/pencrawler
An Advanced Web Crawler and DirBuster
 eldraco/salamandra
Salamandra is a tool to find spy microphones that use radio freq to transmit. It uses SDR.
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 nullarray/autosploit
Automated Mass Exploiter
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 mverschu/adwsdomaindump
Active Directory information dumper via ADWS for evasion purposes.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 trackflaw/cve-2023-25203
CVE-2023-25203: Application Vulnerable to SSRF (Server Side Request Forgery) Attacks
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.