
CVE-2023-35078
 0nsec/cve-2023-35078
CVE-2023-35078 - Ivanti MobileIron Core Remote Unauthenticated API Access Exploit tool
exploitationinformation-gatheringpenetration-testing+3
1
0nsec/cve-2023-35078CVE-2023-35078 - Ivanti MobileIron Core Remote Unauthenticated API Access Exploit tool
 kljunowsky/cve-2023-36845
Proof-of-concept exploit for CVE-2023-36845 enabling unauthenticated remote code execution on Juniper SRX firewalls and EX switches via PHP…
 fyx1t/nse--cve-2023-22515
NSE script for checking the presence of CVE-2023-22515
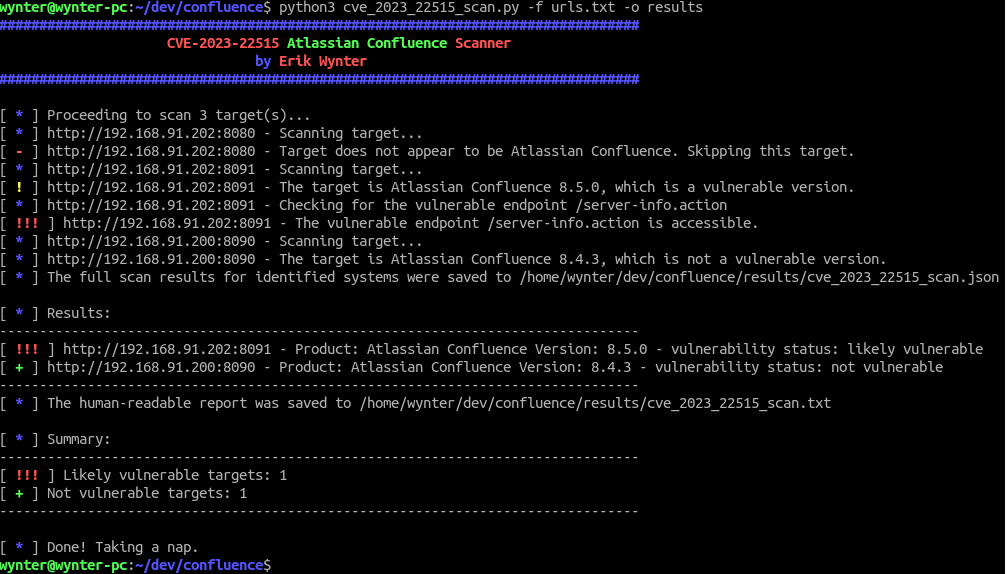 erikwynter/cve-2023-22515-scan
Scanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence
 trackflaw/cve-2023-25203
CVE-2023-25203: Application Vulnerable to SSRF (Server Side Request Forgery) Attacks
 axroux/ghost-path-traversal-cve-2023-32235-
A Directory Traversal attack (also known as path traversal) aims to access files and directories that are stored outside the intended folder.
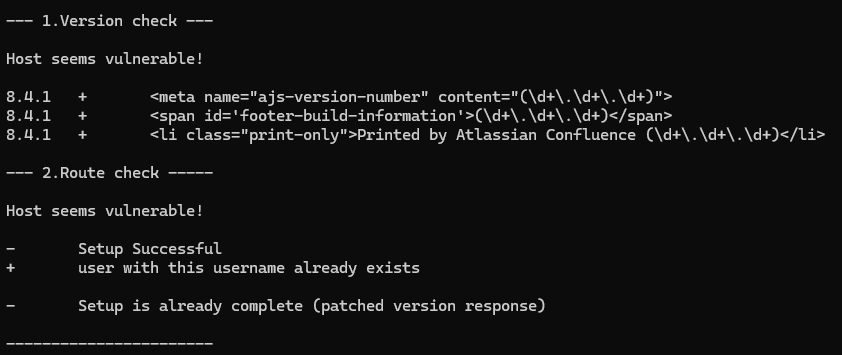 spareack/cve-2023-22515-nse
Vulnerability checking tool via Nmap Scripting Engine
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
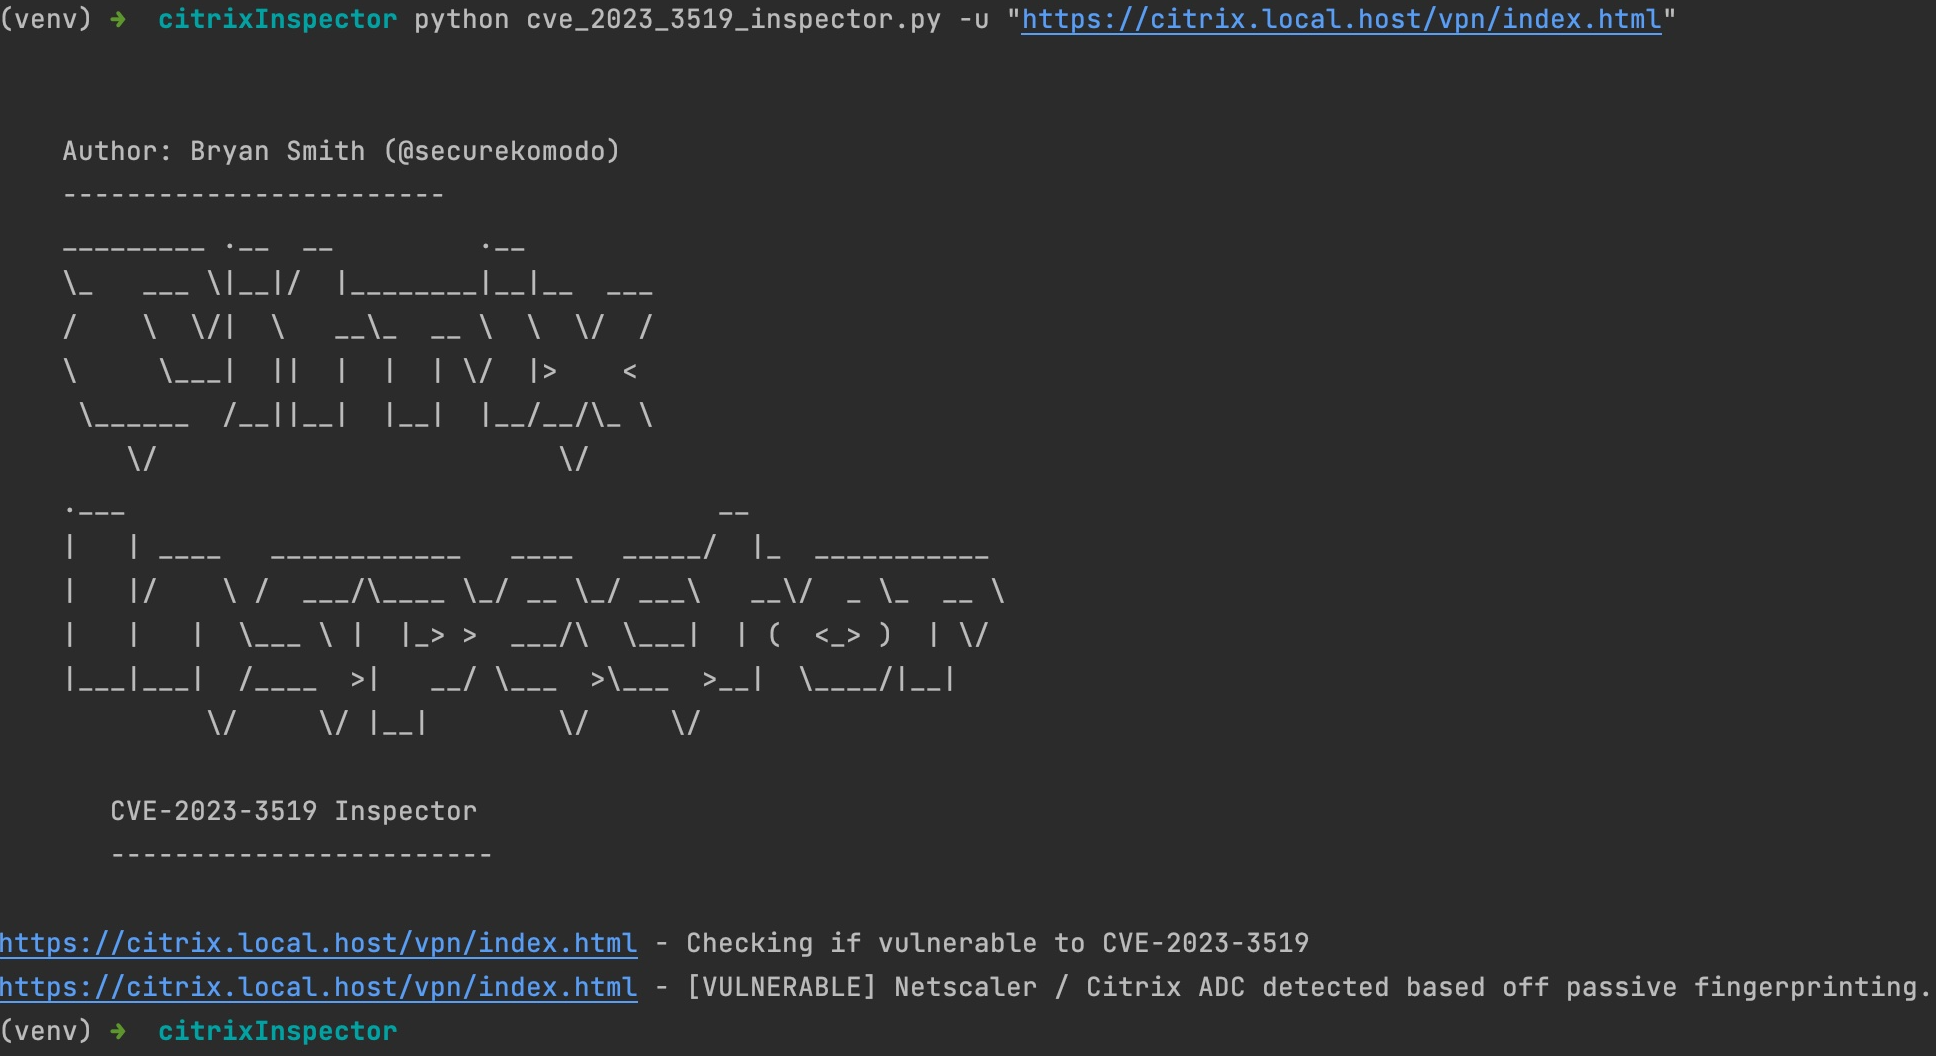 securekomodo/citrixinspector
Passively fingerprint Citrix ADC / NetScaler ADC & Gateway builds and detect known CVEs — CVE-2023-3519, CitrixBleed 2/3, CVE-2026-8452, and…
 j0ey17/exploit_cve-2023-27163
Proof of Concept exploit for Server Side Request Forgery vulnerability in Requests Basket v1.2.1 and before.
 nonosticisiguzo-command/nmap-scan-results
Found 200+ vulnerabilities on scanme.nmap.org including CVE-2023-38408 (9.8 critical)
 himori123/-cve-2023-30845
Explore CVE 2023-30845 automatically across multiple subdomains
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 samh4cks/cve-2023-27163-internalprober
A tool to perform port scanning using vulnerable Request-Baskets
 moften/cve-2022-41741-742-nginx-vulnerability-scanner
CVE-2022-41741/742 Nginx Vulnerability Scanner
 kenbuckler/ws_ftp-cve-2023-40044
Tracks impact of WS_FTP CVE-2023-40044 with affected organizations, domains, and header method analysis. Includes a news ticker for related stories.
 theopaid/cve-2023-27163-request-baskets-local-ports-bruteforcer
PoC and internal port brute-forcer for CVE-2023-27163