

moonwalk
 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
forensicspenetration-testingpost-exploitation+2
1.5k4 years ago
mufeedvh/moonwalkCover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
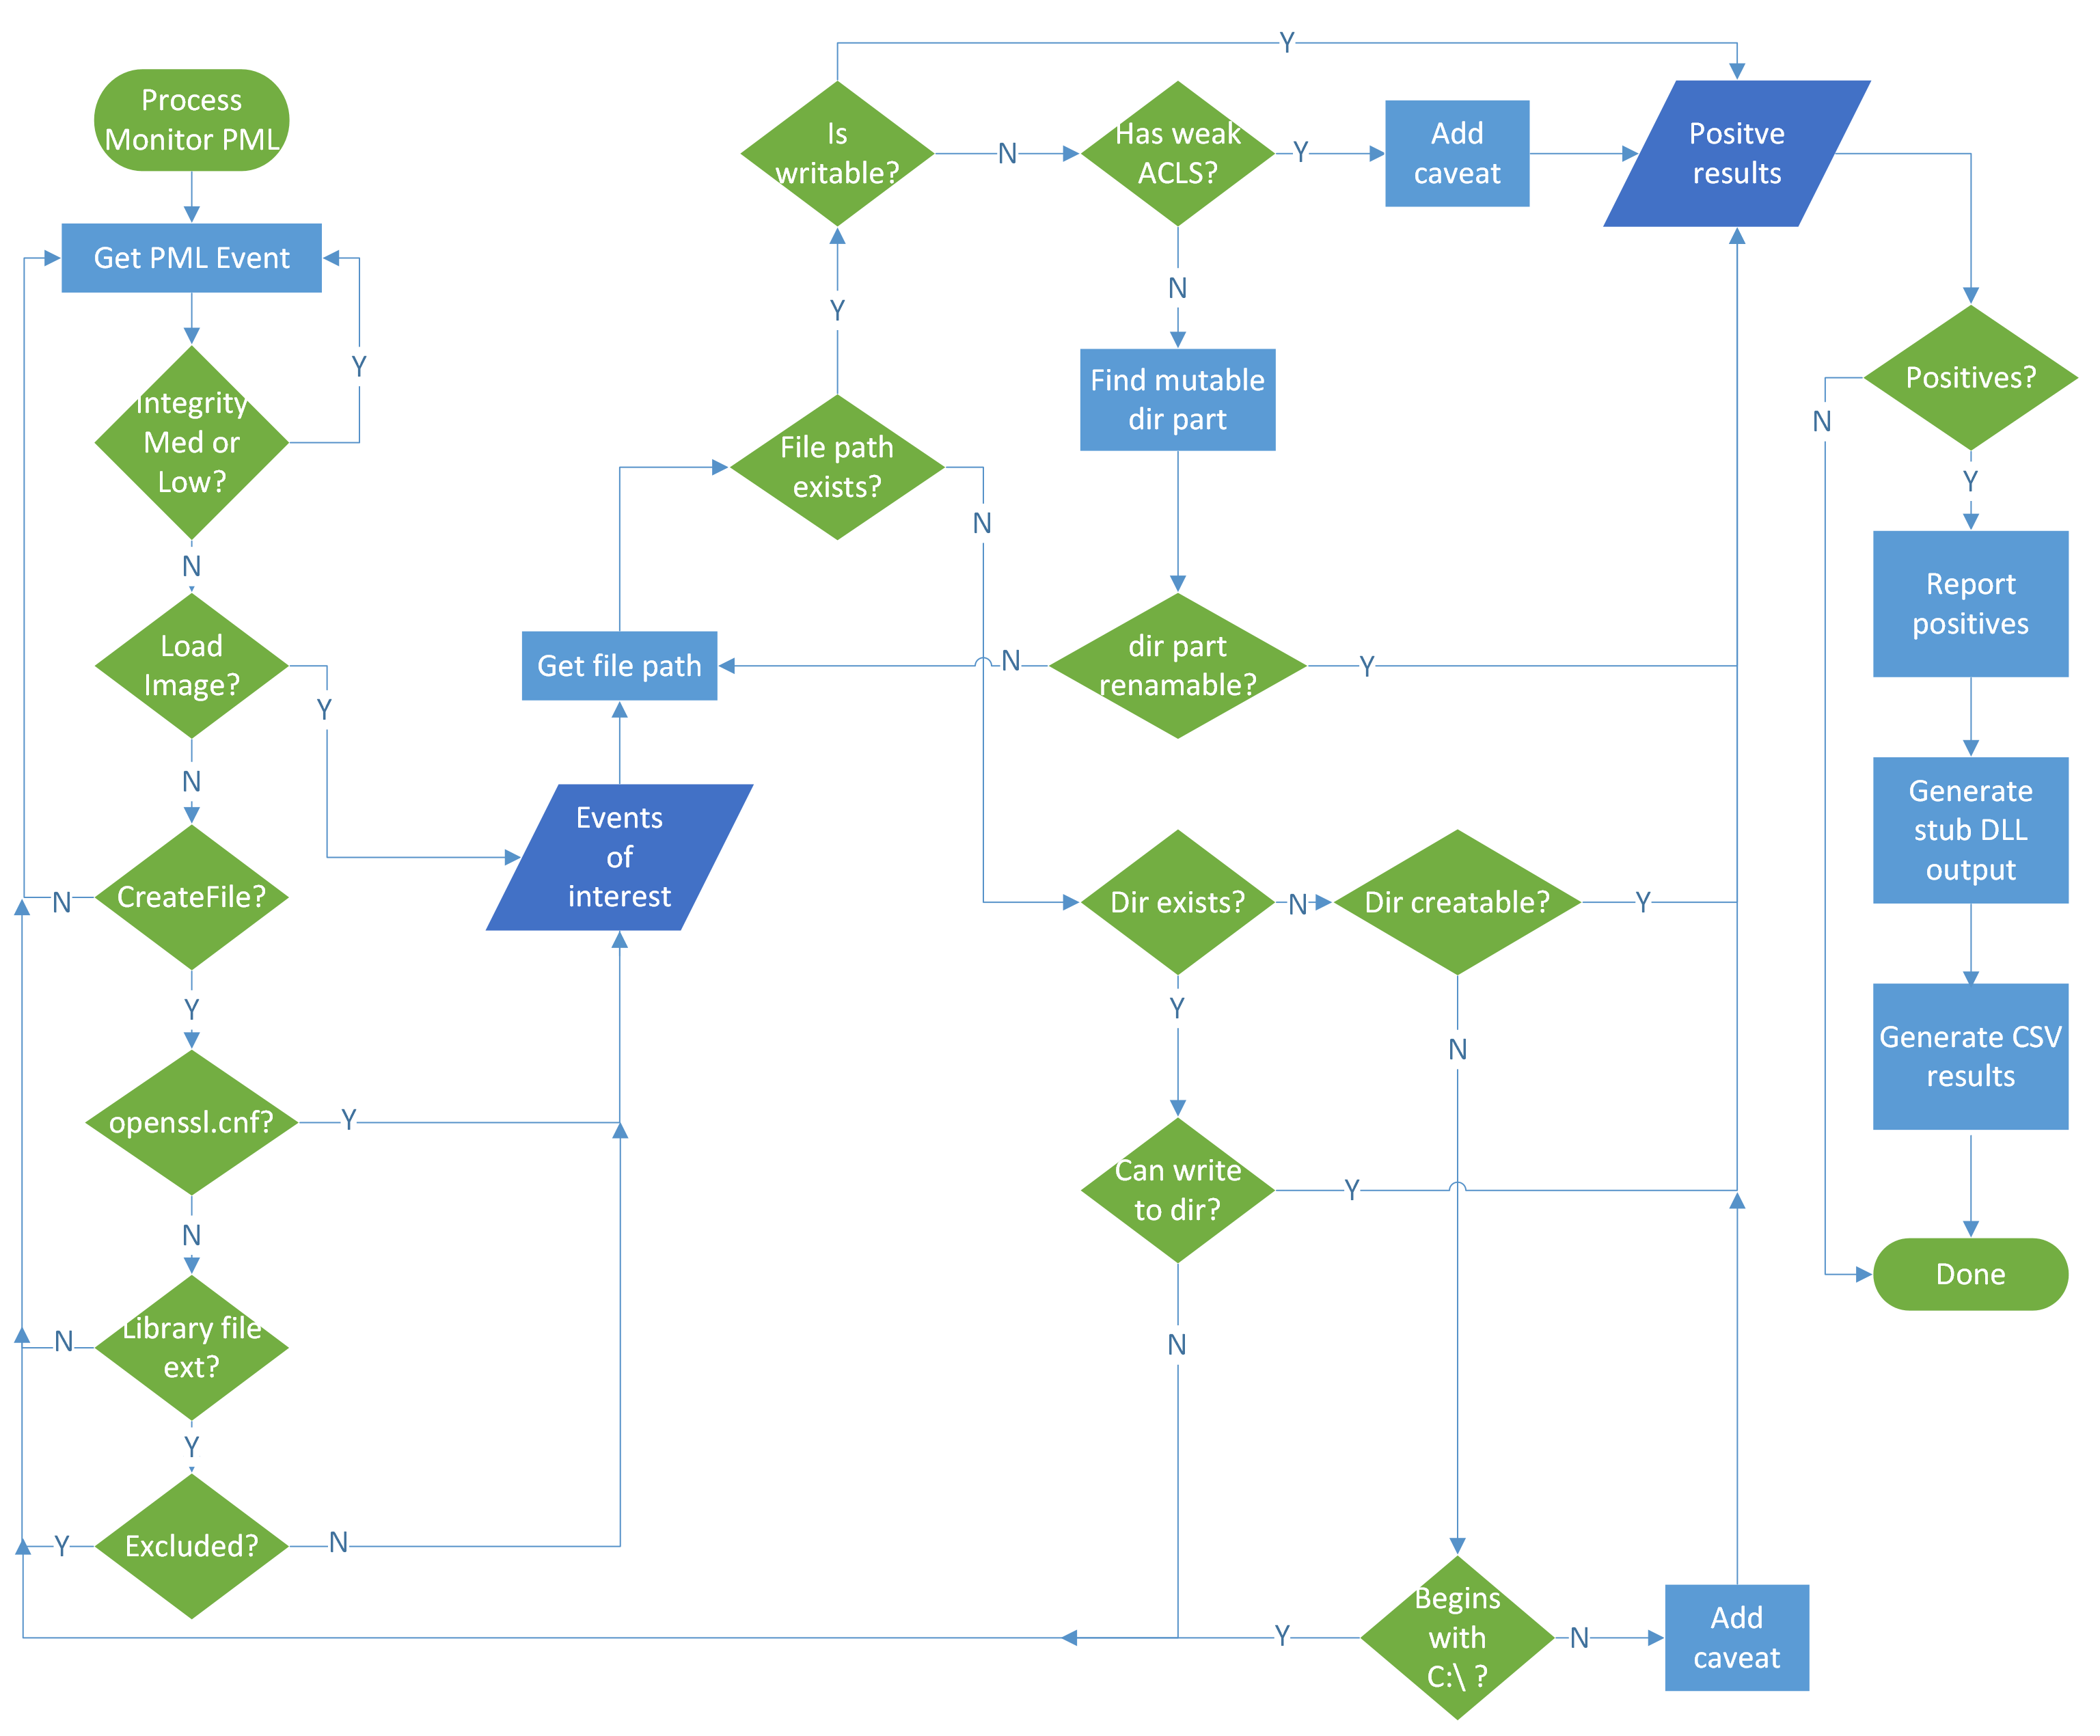 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
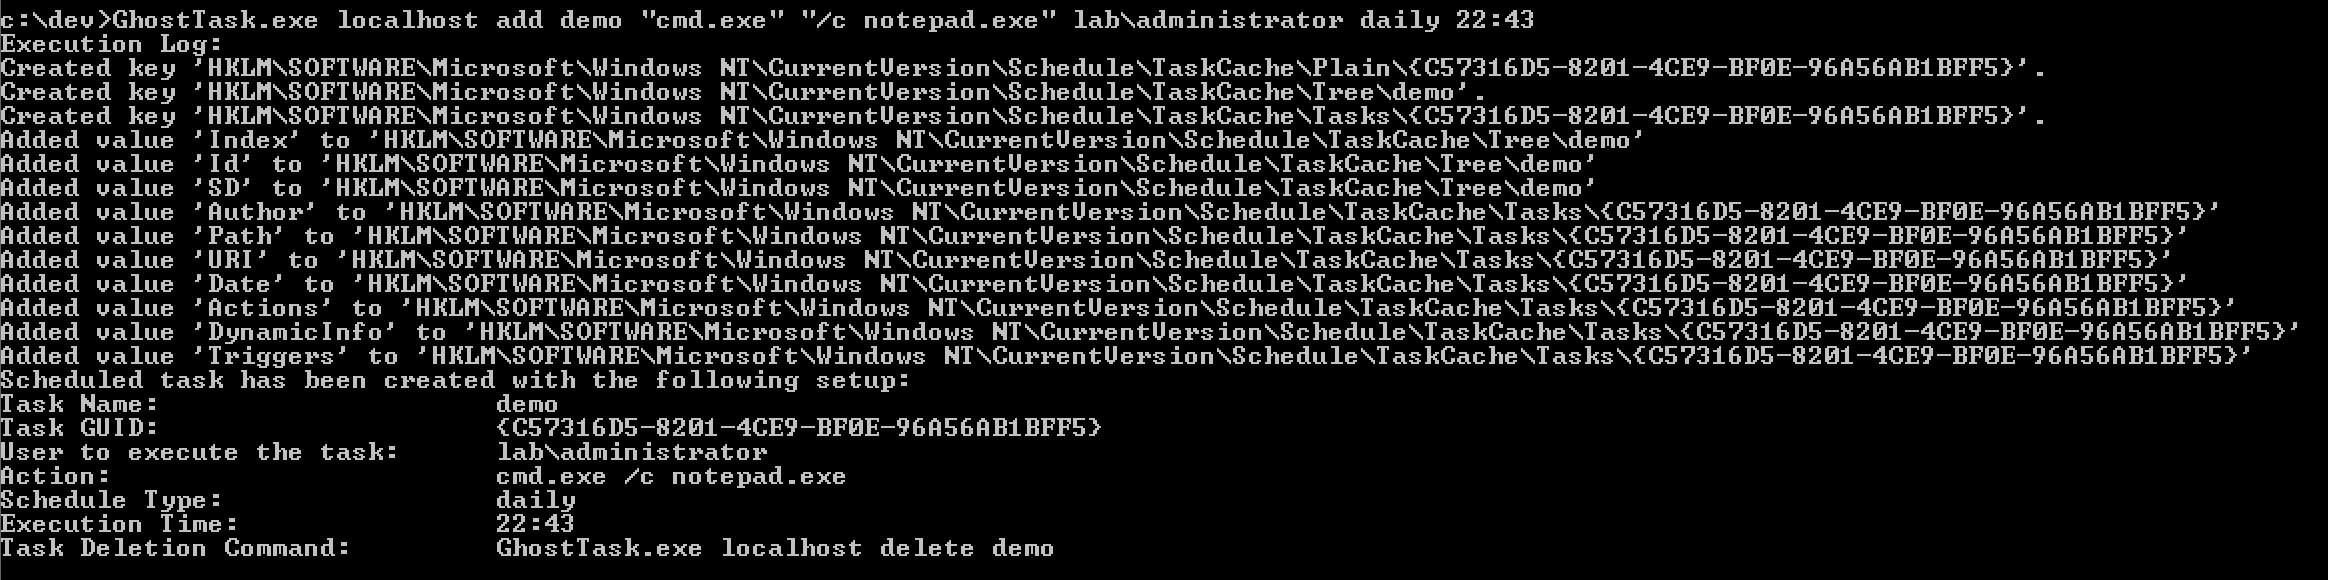 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 velessecurity/cve-2021-1675-printnightmare-analysis
Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 0xdtc/below-logger-symlink-attack_cve-2025-27591
A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…
 hxuu/moodle-cve
Web CTF challenge highlighting moodle CVE-2025-26529 (in 2 flavors)