
Lab4PurpleSec
 0xmr007/lab4purplesec
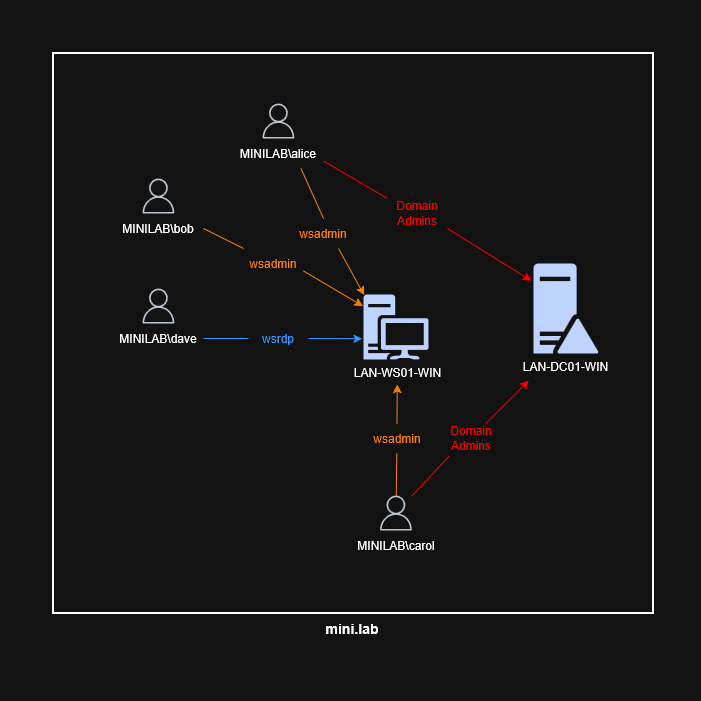
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
educationids-ips-evasionintrusion-detection+5
333
0xmr007/lab4purplesecLab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 imbas007/poc-cve-2026-58048
Security research project
 cyberharsh/apache-couchdb-cve-2017-12635
Docker-based reproduction environment for Apache CouchDB CVE-2017-12635 vertical privilege escalation via JSON parser inconsistency, enabling…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 bahartanir/wp2shell-scanner
CVE-2026-63030 / CVE-2026-60137 - WordPress pre-auth RCE scanner
 abraxas/cve-2026-81294
Proof-of-concept and lab reproduction for CVE-2026-81294, an unauthenticated privilege escalation in the WordPress Authorizer plugin via unverified…
 abraxas/cve-2026-61628
Proof-of-concept and disclosure pack for CVE-2026-61628, an unauthenticated TOCTOU privilege escalation in nginx-ignition 2.41.0 that allows admin…
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 v35hr4j/cve-2021-24545
The plugin does not sanitise the HTML allowed in the Bio of users, allowing them to use malicious JavaScript code, which will be executed when anyone…
 1h3ll/cve-2025-50363_bxss_cve
Proof-of-concept for a blind XSS vulnerability in Maid Hiring Management System v1.0, capturing admin session cookies via a crafted application form…
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 xxxtectationxxx/react2shell-cve-lab
A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 cyberw1ng/cve-2025-33053-poc
POC for CVE-2025-33053 WebDav Exploit, demonstrating how the vulnerability can be triggered in a real environment. This repository focuses on…
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.