

Ghost-In-The-Logs
 bats3c/ghost-in-the-logs
Kernel-level tool to disable Sysmon and Windows Event Logging via driver-based hook injection, enabling stealthy post-exploitation operations on…
defensive-toolsids-ips-evasionprivilege-escalation
bats3c/ghost-in-the-logsKernel-level tool to disable Sysmon and Windows Event Logging via driver-based hook injection, enabling stealthy post-exploitation operations on…
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 brl/grlh
Proof-of-concept exploiting a weakness to disable the eBPF verifier, enabling arbitrary eBPF code execution for kernel-level privilege escalation.
 duhirsch/moveedr
Permanently disable EDRs as local admin
 askyeye/cve-2018-19320
Exploiting ring0 memcpy-like functionality to disable Driver Signing Enforcement (DSE)
 perongh/badepoll-selinux-disabler
Use CVE-2026-43074 to disable SELinux on Android (Linux 6.6/6.12)
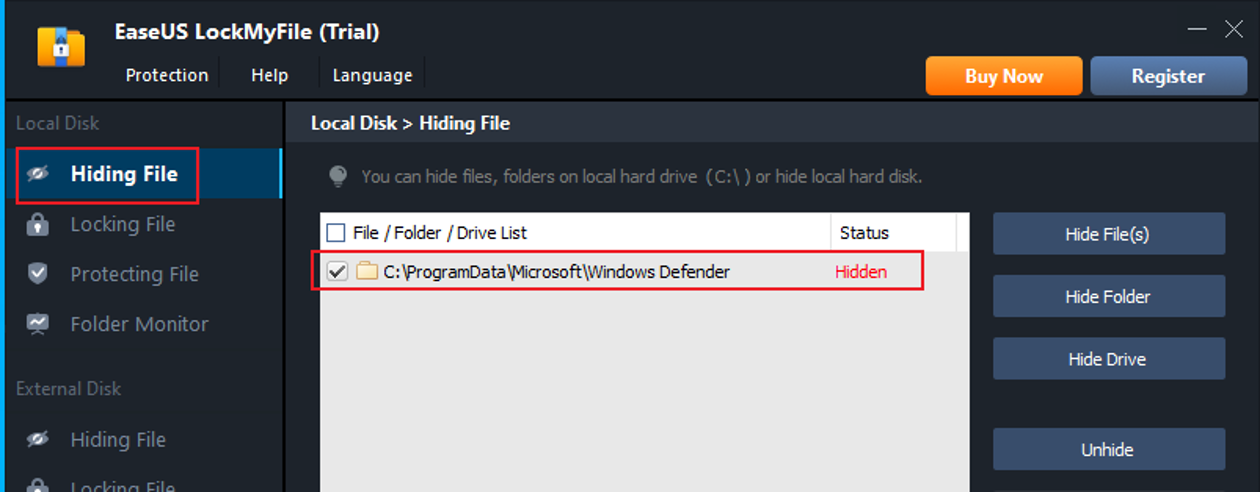 cwjchoi01/cve-2026-31321
Proof-of-concept demonstrating methods to disable or bypass Windows Defender by hiding, locking, or protecting its folders, enabling persistence…
 kukrimate/cve-2020-14372
Proof-of-concept exploit and write-up for CVE-2020-14372, demonstrating Secure Boot bypass via malicious ACPI SSDT to disable kernel lockdown and…
 bariskizilkaya/cve-2022-20186_ctxz
Exploit for CVE-2022-20186 in Arm Mali kernel driver, achieving arbitrary kernel code execution from untrusted app domain to disable SELinux and gain…
 smiletablabo/cve-2022-46395
Exploit for CVE-2022-46395, an Arm Mali kernel driver vulnerability, achieving arbitrary kernel code execution to disable SELinux and gain root on…
 smiletablabo/cve-2022-20186
Exploit for CVE-2022-20186 in the Arm Mali kernel driver, achieving arbitrary kernel code execution to disable SELinux and gain root on Google Pixel…
 kougyokugentou/cve-2021-1675
A small powershell script to disable print spooler service using desired state configuration
 annavid/cve-2020-15780-exploit
Exploits to disable kernel lockdown via ACPI table injection, targeting Ubuntu 18.04 and mainline kernels with two distinct techniques.
 blacksnufkin/byovd
BYOVD research use cases featuring vulnerable driver discovery and reverse engineering methodology. (CVE-2025-52915, CVE-2025-1055, CVE-2026-3609,…
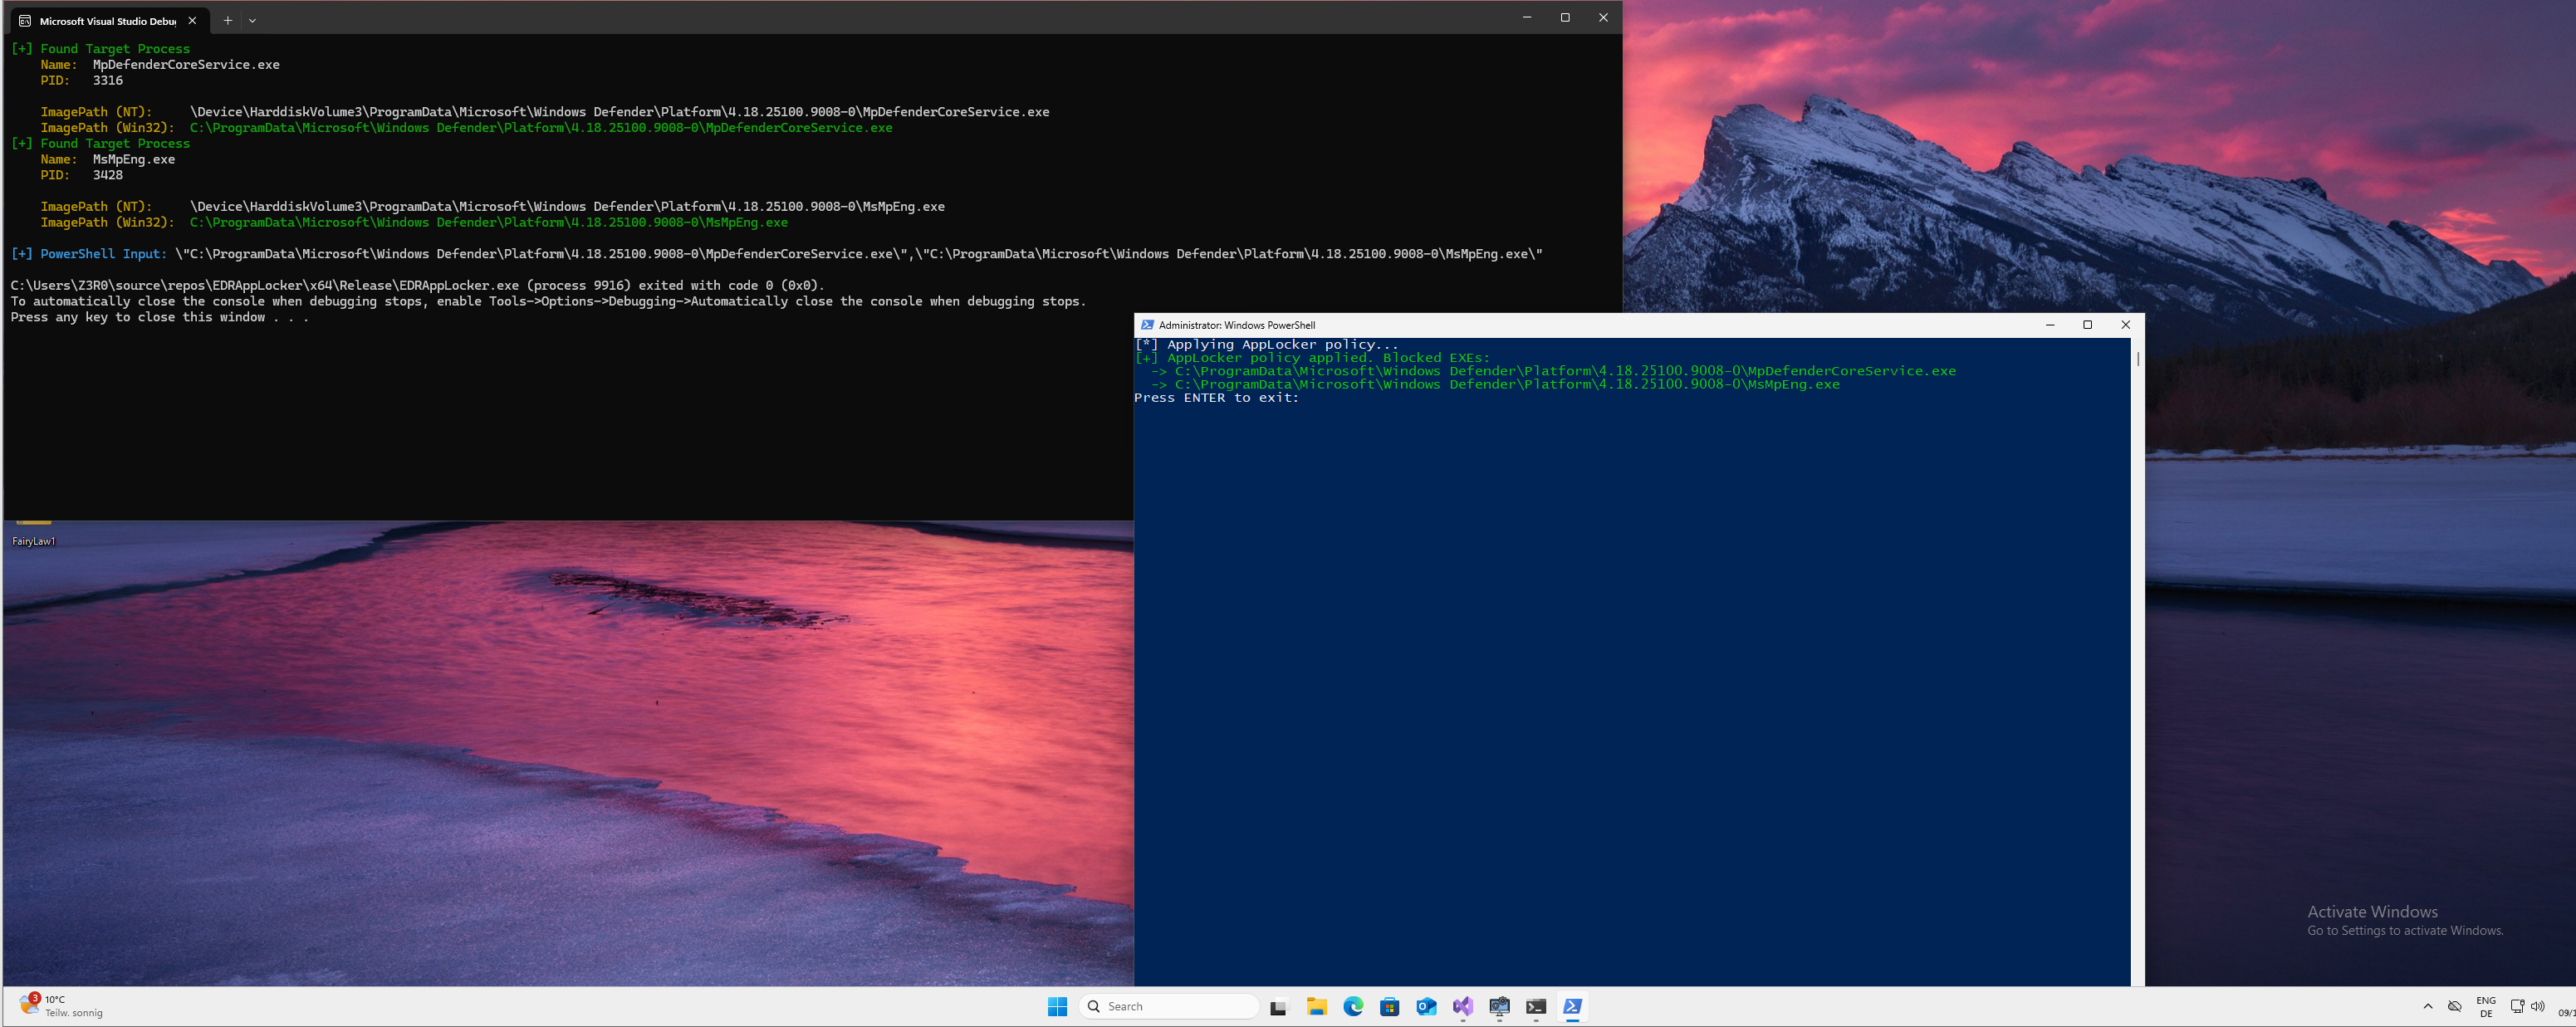 zero2504/edr-ghostlocker
AppLocker-Based EDR Neutralization
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 athos-zago/cve-2024-30973
POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN