
BadSamba
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
exploitationlateral-movementnetwork-security+3
22
strozfriedberg/badsambaThis module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 krakeneu/cve-2024-54910
Demonstrates arbitrary file write and privilege escalation in Hasleo Backup Suite Free <= 4.9.4 via symbolic links, enabling attackers to overwrite…
 xi0onamdev/winrar-cve-2025-8088-exploitation-toolkit
GUI tool for creating malicious RAR archives exploiting CVE-2025-8088 path traversal. Uses NTFS ADS stealth and RAR5 header injection for payload…
 yucaerin/cve-2025-4606
Sala - Startup & SaaS WordPress Theme <= 1.1.4 - Unauthenticated Privilege Escalation via Password Reset/Account Takeover
 yetazyyy/cve-2025-4606
Python-based scanner that tests WordPress sites for CVE-2025-4606, a privilege escalation vulnerability in the Sala theme allowing unauthenticated…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 orange-cyberdefense/p3-loader
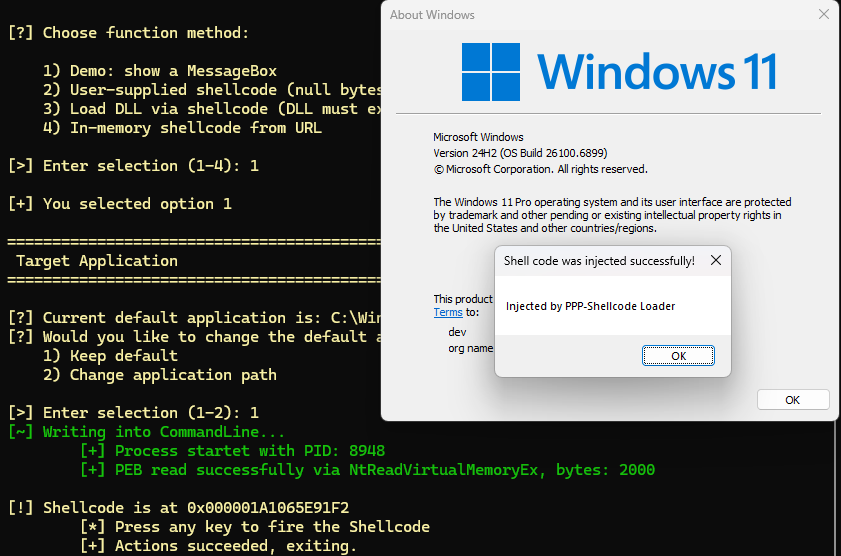
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…