
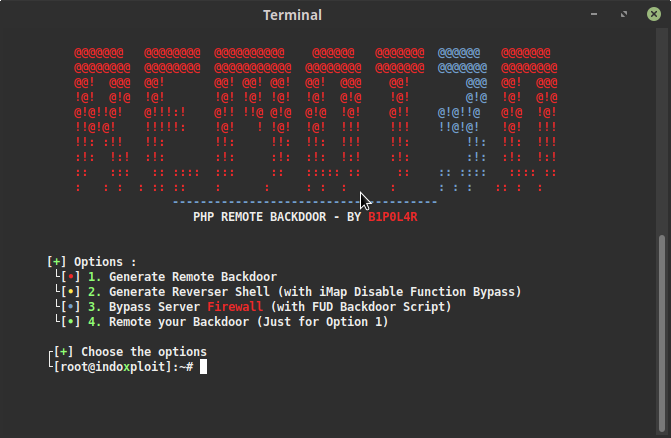
Remot3d
 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
information-gatheringpayload-generationpenetration-testing+3
18
makiraid/remot3dRemot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 maleeshaudan/wordpress-cve-2024-10924--exploit
WordPress CVE-2024-10924 Exploit for Really Simple Security plugin
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 0xgh057r3c0n/cve-2025-4334
Proof-of-concept exploit for CVE-2025-4334, a privilege escalation vulnerability in the Simple User Registration WordPress plugin (<= 6.3), allowing…
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 nxploited/cve-2025-53580
WordPress Simple Business Directory Pro Plugin < 15.6.9 is vulnerable to a high priority Privilege Escalation
 nxploited/cve-2025-4334
Simple User Registration <= 6.3 - Unauthenticated Privilege Escalation
 vinodwick/cve-2025-4334
Exploit for CVE-2025-4334, a WordPress Simple User Registration plugin privilege escalation vulnerability allowing unauthenticated attackers to…
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
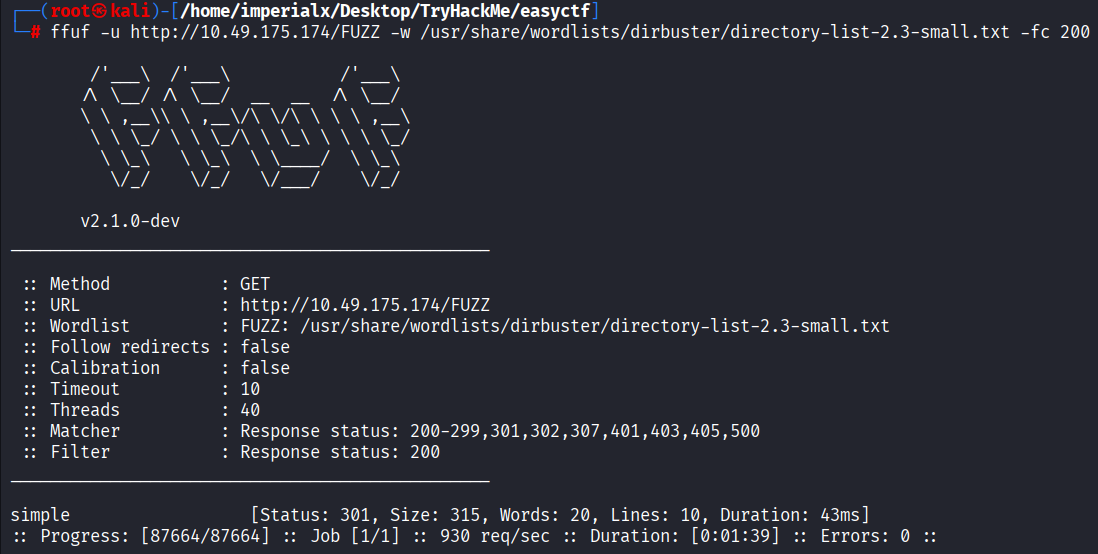 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…