
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
26 results
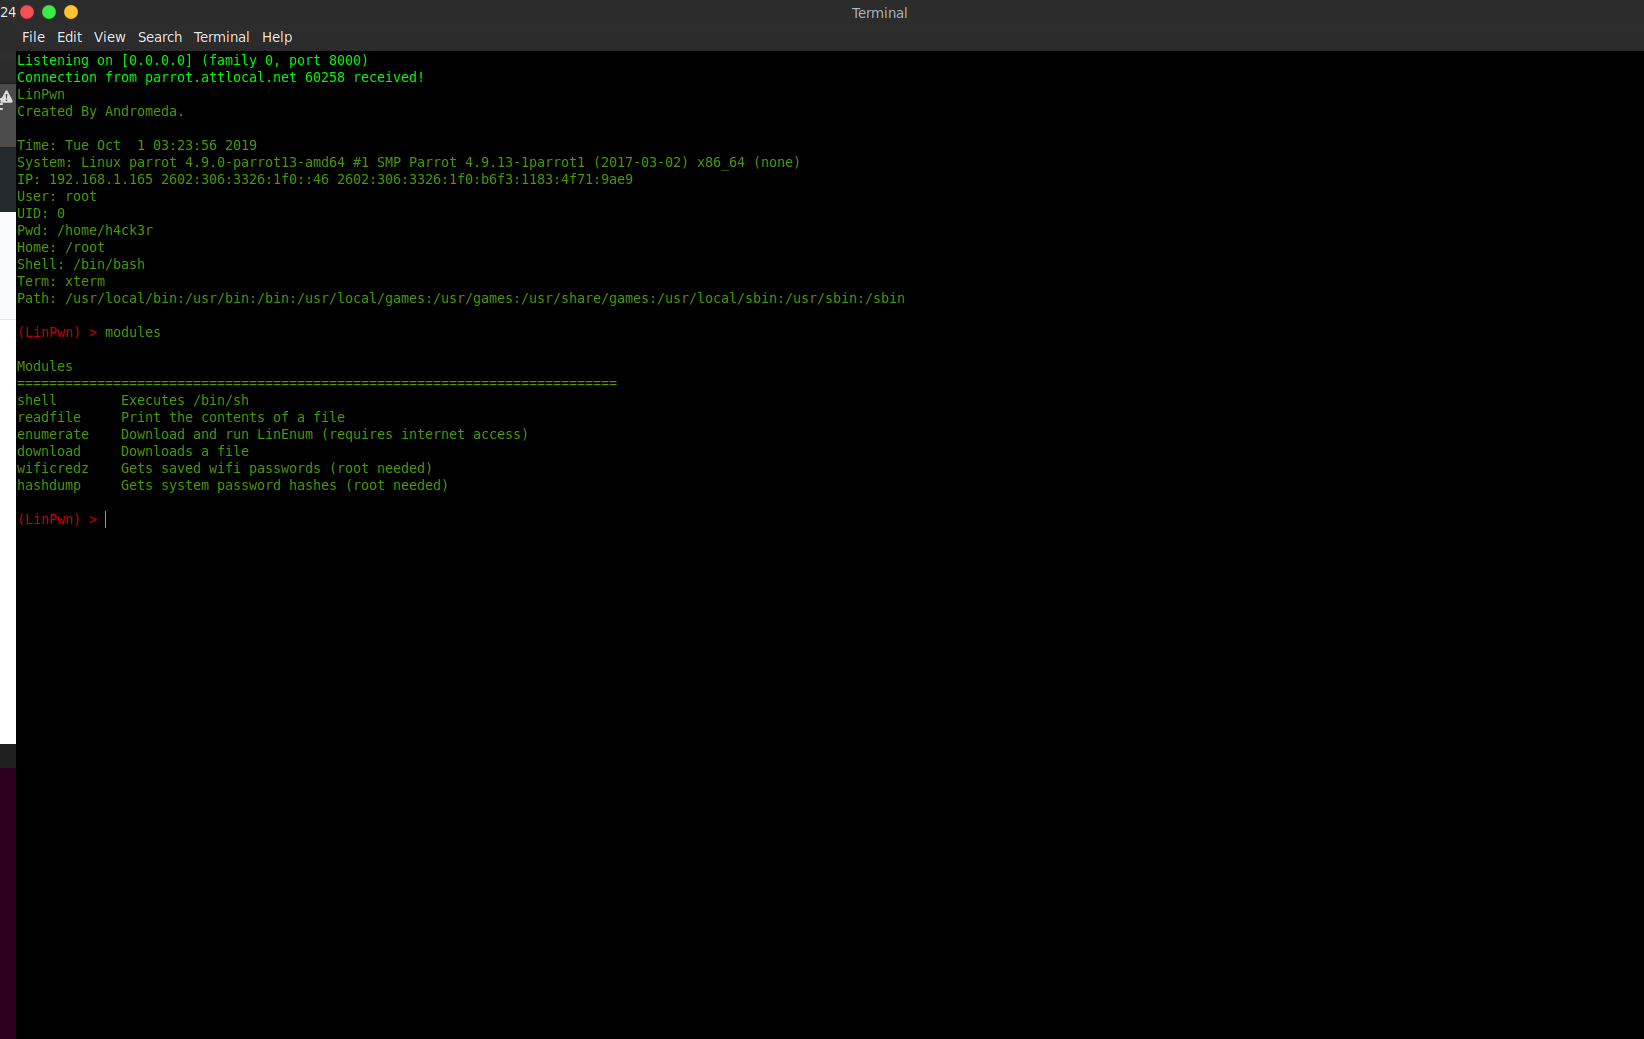
LinPwn preview

LinPwn

GitHubandromeda1957/linpwn

Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
information-gatheringpassword-crackingpenetration-testing+2
37
6 years ago
RevShell preview

RevShell

GitHubdragon56yt/revshell

A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
command-and-controldata-exfiltrationeducation+8
23 months ago
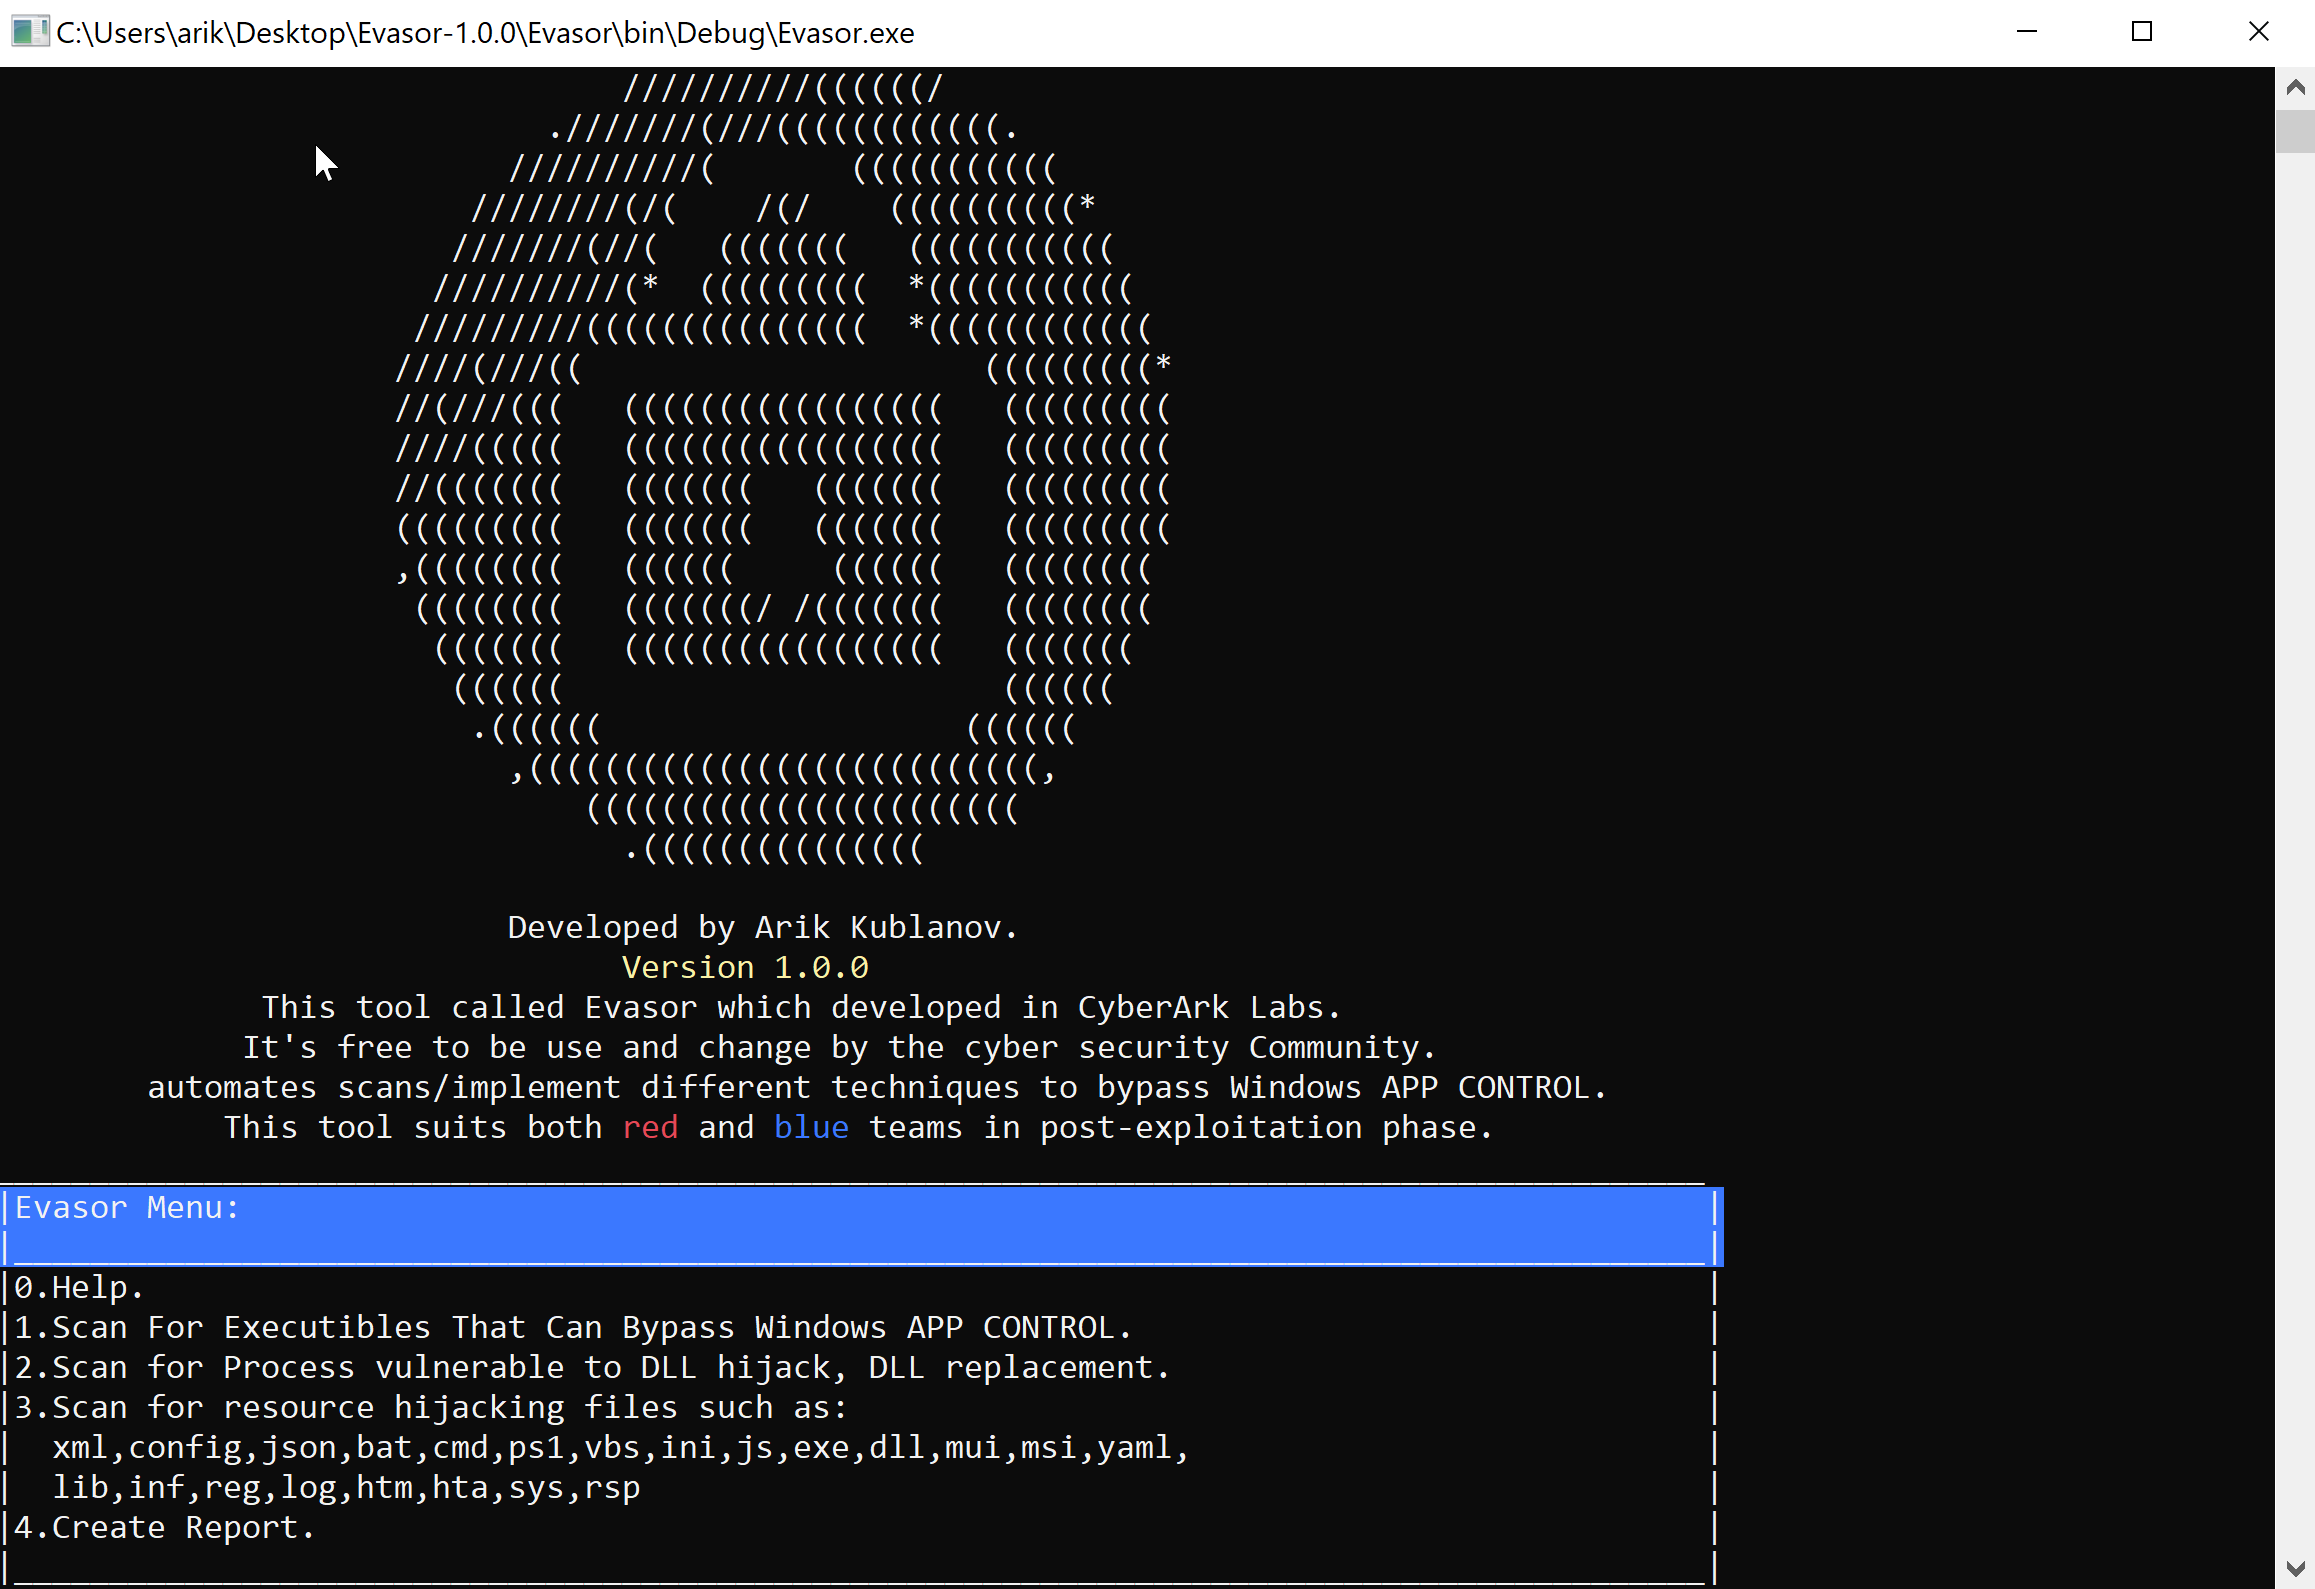
Evasor preview

Evasor

GitHubcyberark/evasor

A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies

binary-analysisdefensive-toolspenetration-testing+3
3266 years ago
DLLirant preview
Archived

DLLirant

GitHubsh0ckfr/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
binary-analysisexploitationprivilege-escalation+2
3223 years ago
SUDO_KILLER preview

SUDO_KILLER

GitHubth3xace/sudo_killer

A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…

ctfeducationexploitation+5
2.5k6 months ago
pspy preview

pspy

GitHubdominicbreuker/pspy

Monitor linux processes without root permissions
ctfinformation-gatheringpenetration-testing+2
6.2k6 months ago
path-auditor preview
Archived

path-auditor

GitHubgoogle/path-auditor

Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…

binary-analysisdynamic-code-analysisexploitation+3
2505 years ago
KSuRoot preview

KSuRoot

GitHubhmascs/ksuroot

One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
android-securitybinary-exploitationexploitation+2
759 days ago
couchdb-exploit preview

couchdb-exploit

GitHubdarabium/couchdb-exploit

Exploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…

exploitationinformation-gatheringpenetration-testing+4
2 days ago
FullBypass preview
Archived

FullBypass

GitHubsh3lldon/fullbypass

A tool which bypasses AMSI (AntiMalware Scan Interface) and PowerShell CLM (Constrained Language Mode) and gives you a FullLanguage PowerShell…
command-and-controlexploitationids-ips-evasion+5
8201 year ago
Salsa-tools preview

Salsa-tools

GitHubhackplayers/salsa-tools

Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
command-and-controlencryption-decryption-toolsexploitation+7
5896 years ago
Robber preview

Robber

GitHubmojtabatajik/robber

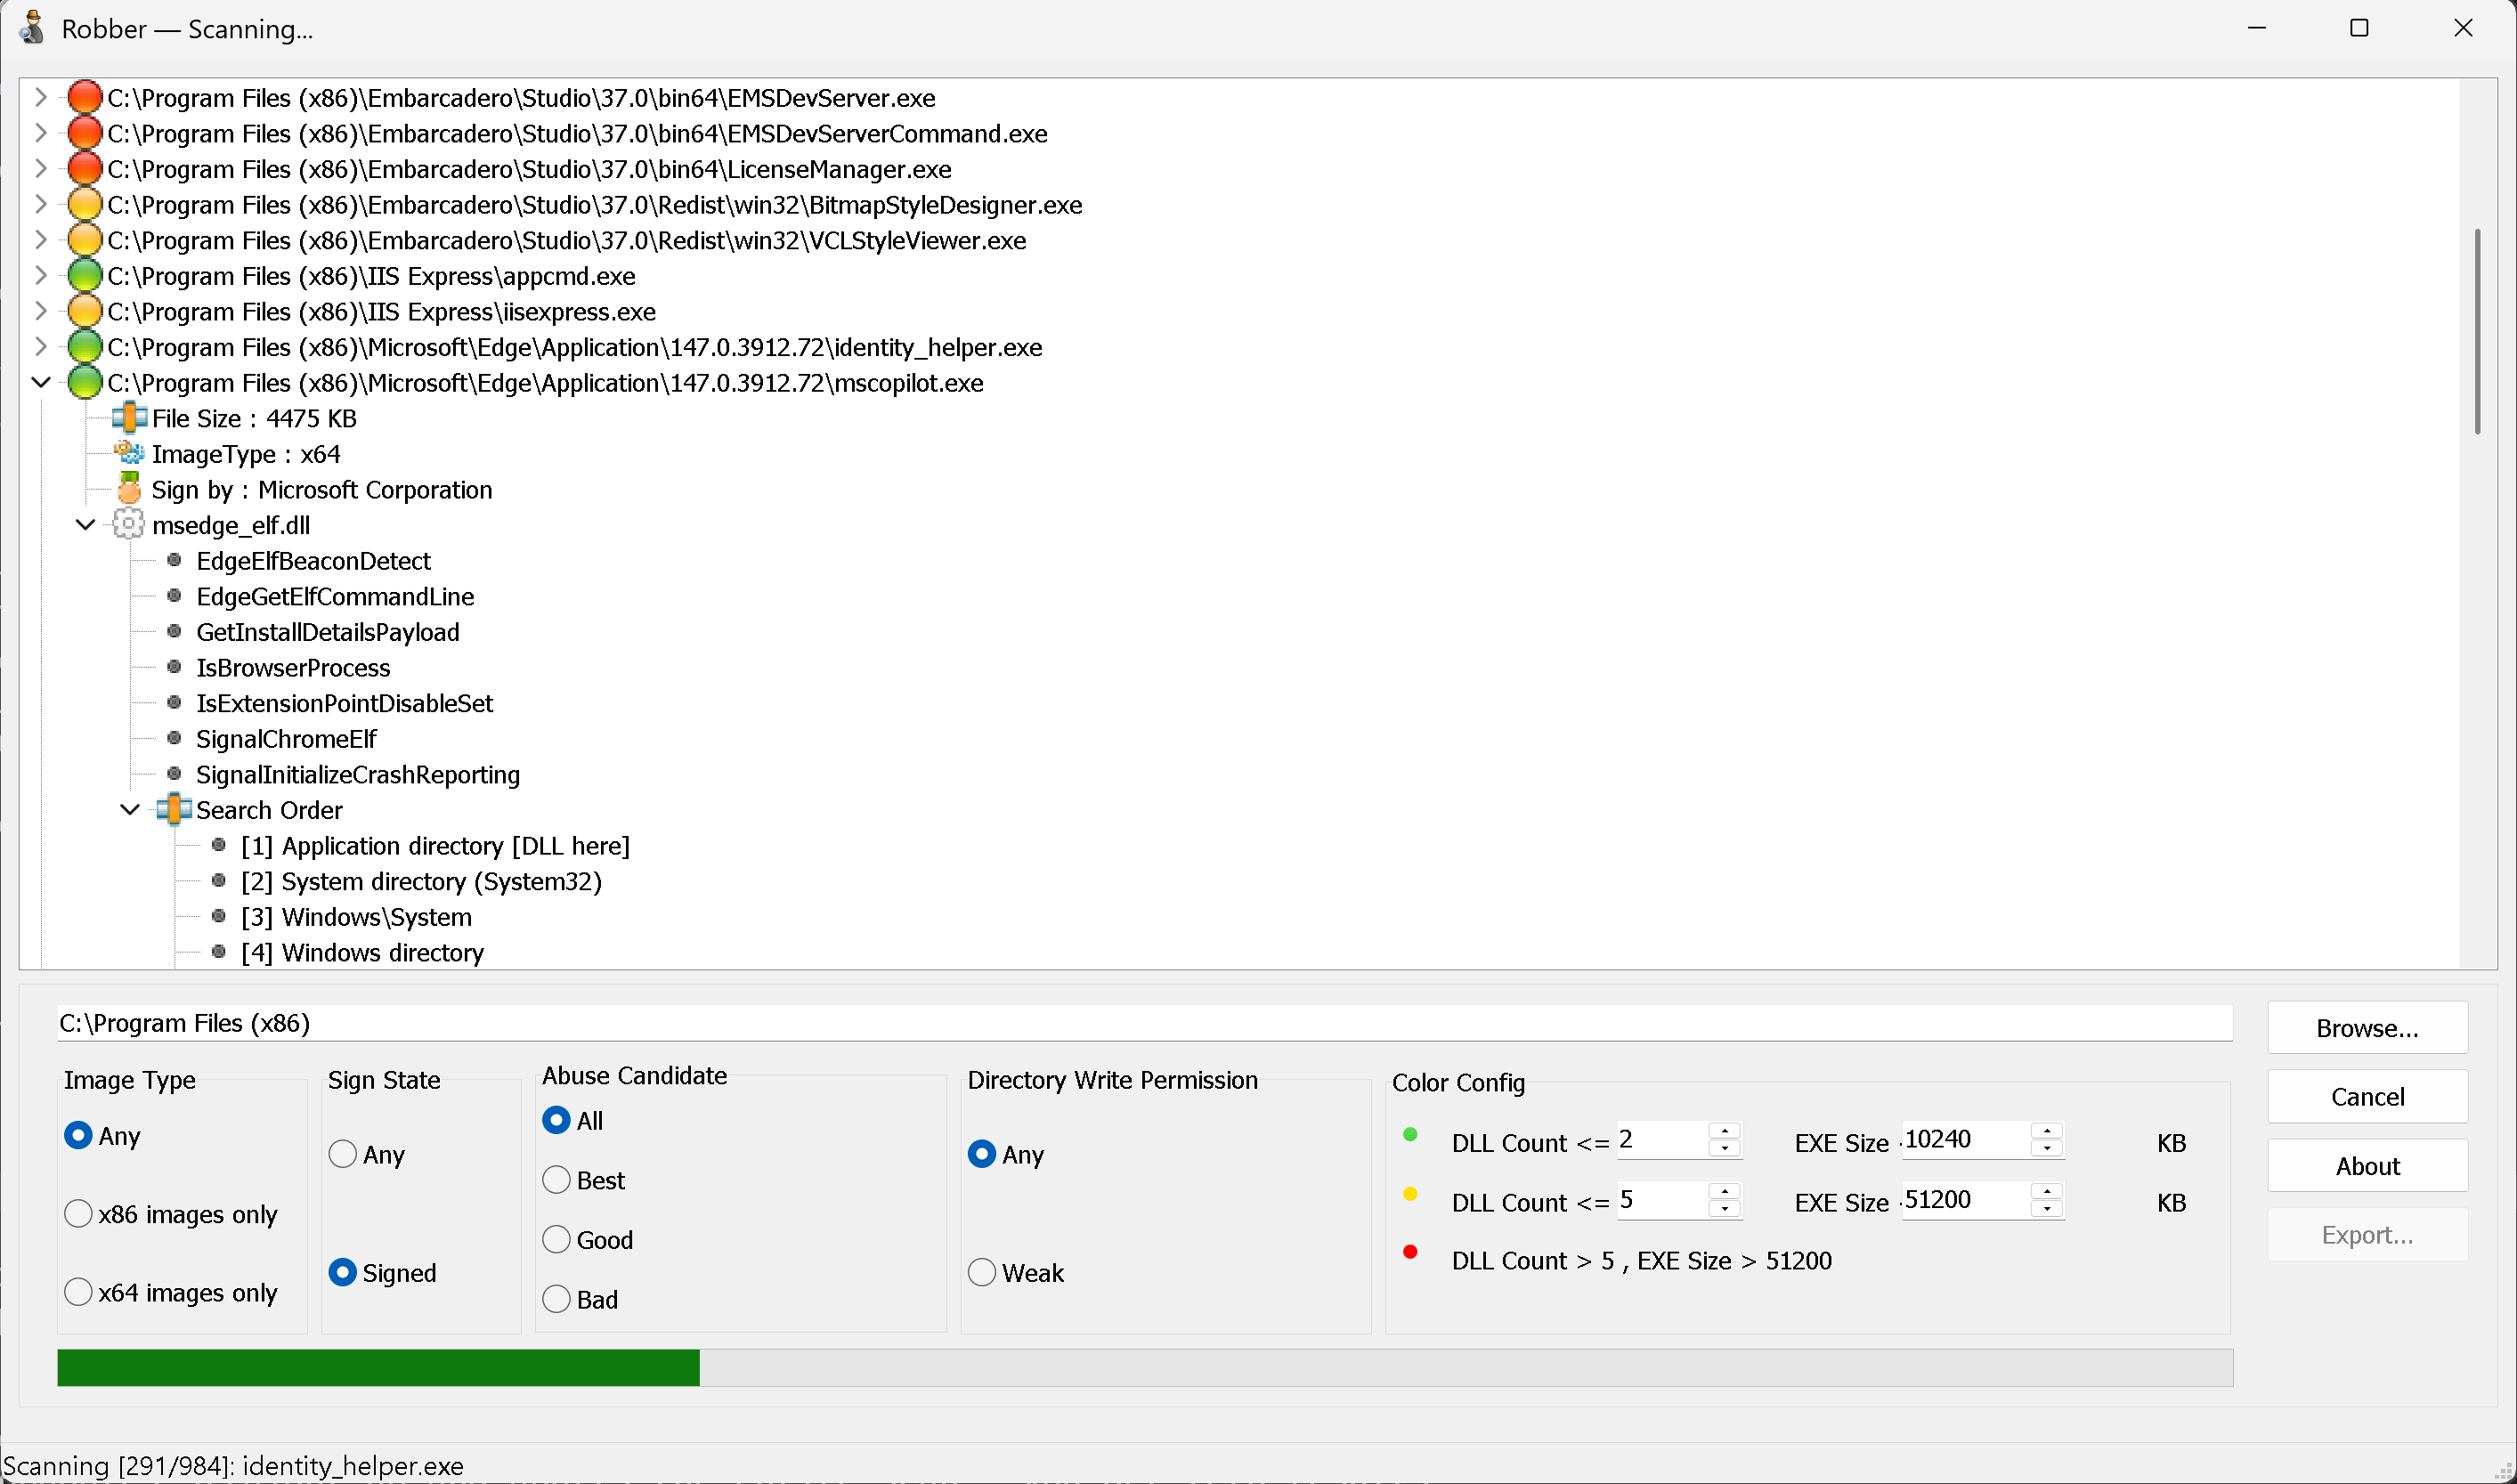
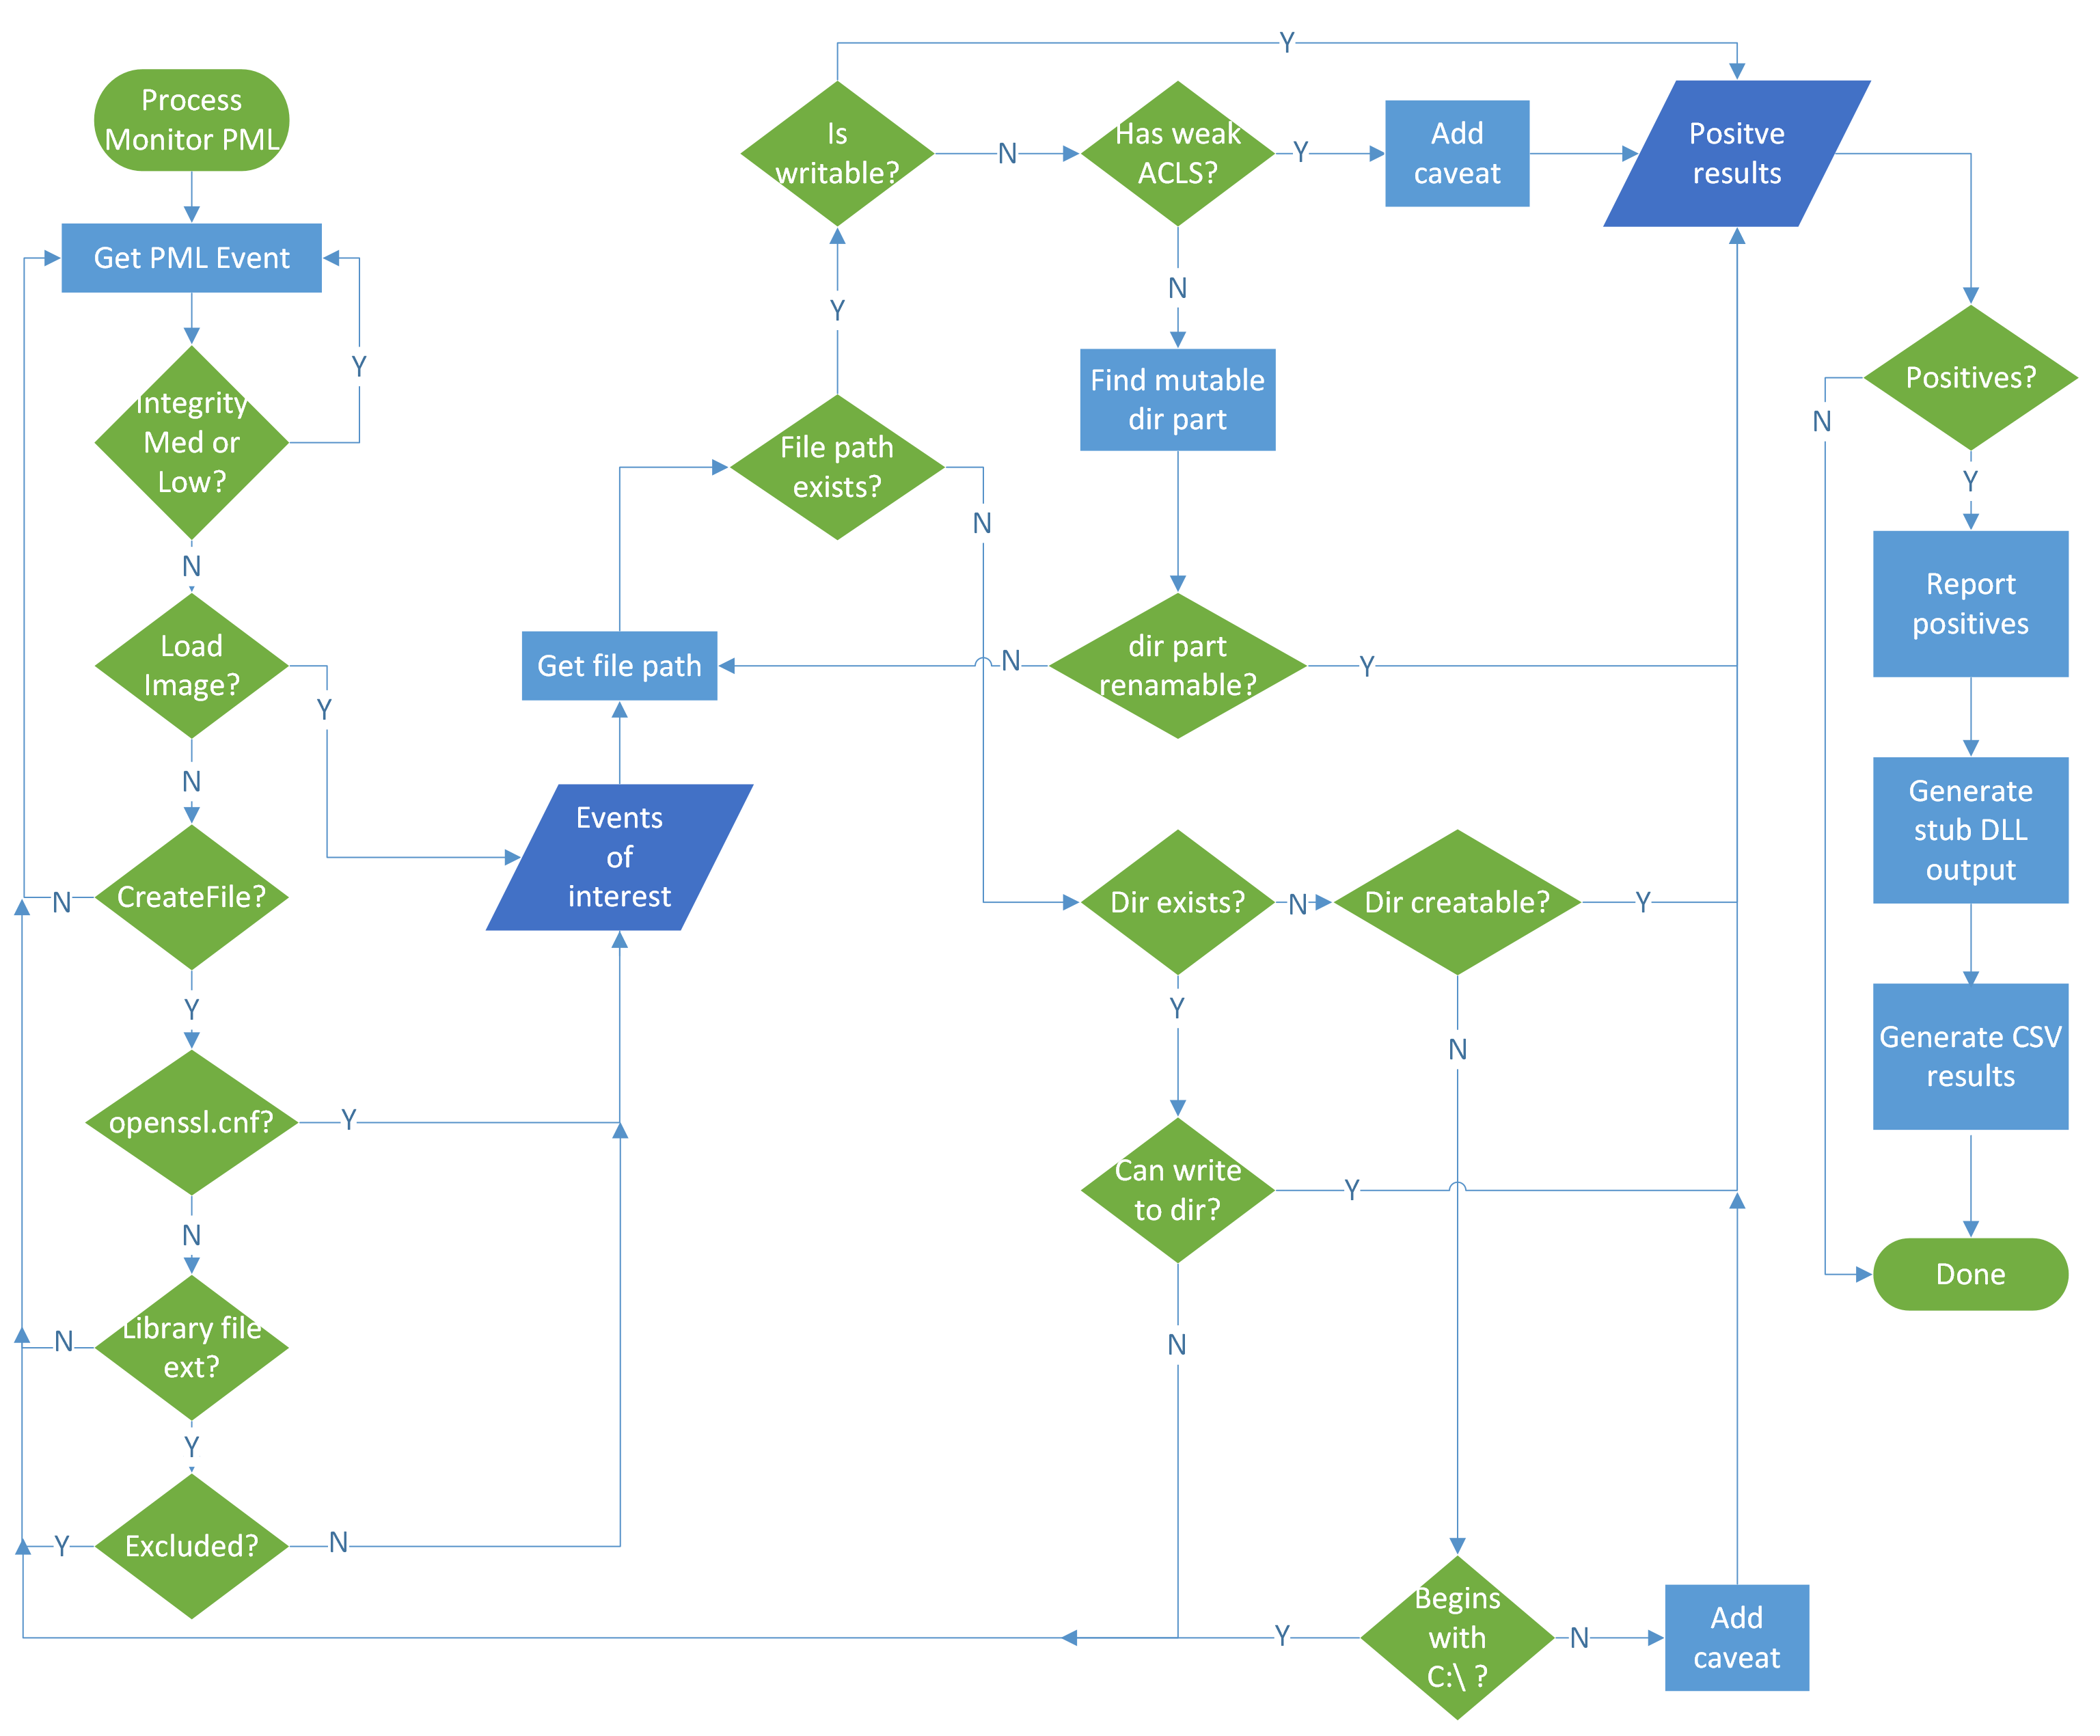
Robber is open source tool for finding executables prone to DLL hijacking
binary-analysisprivilege-escalationvulnerability-analysis+1
7994 months ago
Crassus preview

Crassus

GitHubvu-ls/crassus

Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
6327 months ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubdll00p/cve-2021-1675

Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
exploitationlateral-movementpayload-generation+4
11 year ago
siofra preview

siofra

GitHubcybereason/siofra

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
binary-analysisbinary-exploitationpayload-generation+4
5138 years ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
CVE-2025-21420_POC preview

CVE-2025-21420_POC

GitHubmoiz-2x/cve-2025-21420_poc

Proof of Concept CVE-2025-21420 (Windows Disk Cleanup Tool EoP)
binary-analysisexploitationpenetration-testing+2
561 year ago
CVE-2025-0324-axis-vapix-privesc preview

CVE-2025-0324-axis-vapix-privesc

GitHubkemrec/cve-2025-0324-axis-vapix-privesc

Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…

binary-analysisexploitationfirmware-analysis+4
20 days ago
Previous12Next