
PHP_imap_open_exploit
 bo0om/php_imap_open_exploit
Bypassing disabled exec functions in PHP (c) CRLF
exploitationprivilege-escalationvulnerability-analysis+1
403
bo0om/php_imap_open_exploitBypassing disabled exec functions in PHP (c) CRLF
 r3dteam/casper-shell
Casper@shell:~# is an enhanced, more user-friendly version of p0wny shell with many new features.
 joffr3y/polkit-cve-2021-4034-hlp
Polkit CVE-2021-4034 exploitation in High-Level Programming Language
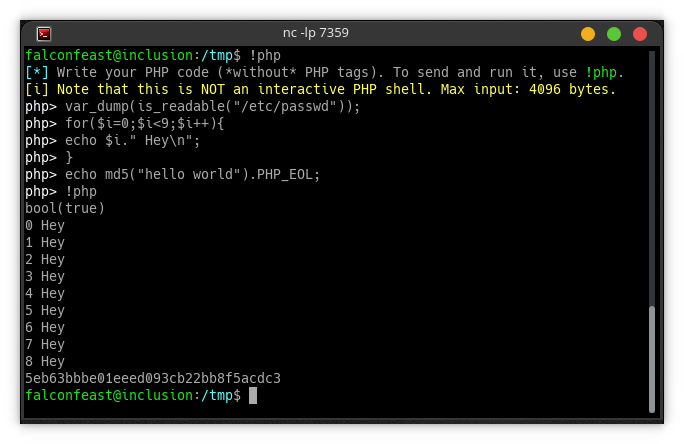 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 xiphosresearch/exploits
Miscellaneous exploit code
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
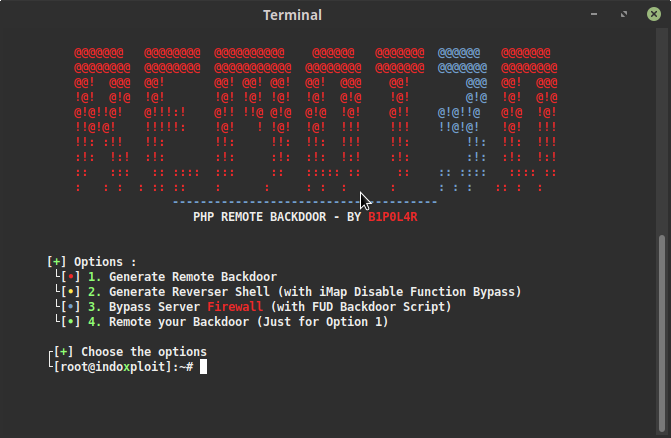 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 im-hanzou/msaper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2023-3076 - MStore API < 3.9.9 - Unauthenticated Privilege Escalation (Mass Add…
 martinpham/copy-fail-cve-2026-31431-php
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail) in PHP, demonstrating privilege escalation to root on vulnerable systems.
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 jeanback1/cve-2019-0211-exploit
Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
 druxter-x/php-cve-2023-2023-2640-poc-escalation
PHP proof-of-concept exploit for CVE-2023-2640 and CVE-2023-32629 privilege escalation vulnerabilities on Ubuntu systems. Intended for educational…
 hood3drob1n/mysql-fu.rb
MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819