

r77-rootkit
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k
bytecode77/r77-rootkitFileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 t3l3machus/eviltree
A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 whotwagner/logrotten
Logrotate race condition exploit that enables privilege escalation by writing arbitrary files, such as reverse shell payloads, into system…
 sndav/cve-2026-31431-advanced-exploit
Exploit for CVE-2026-31431, a Linux kernel AF_ALG AEAD page-cache write vulnerability enabling unprivileged arbitrary 4-byte writes to readable files…
 praetorian-inc/swarmer
A tool to convert windows registry export files into windows hive files that can be used to replace NTUSER.MAN
 febinrev/dirtypipez-exploit
Local privilege escalation exploit for Linux kernel vulnerability CVE-2022-0847 (Dirty Pipe), allowing non-privileged users to overwrite data in…
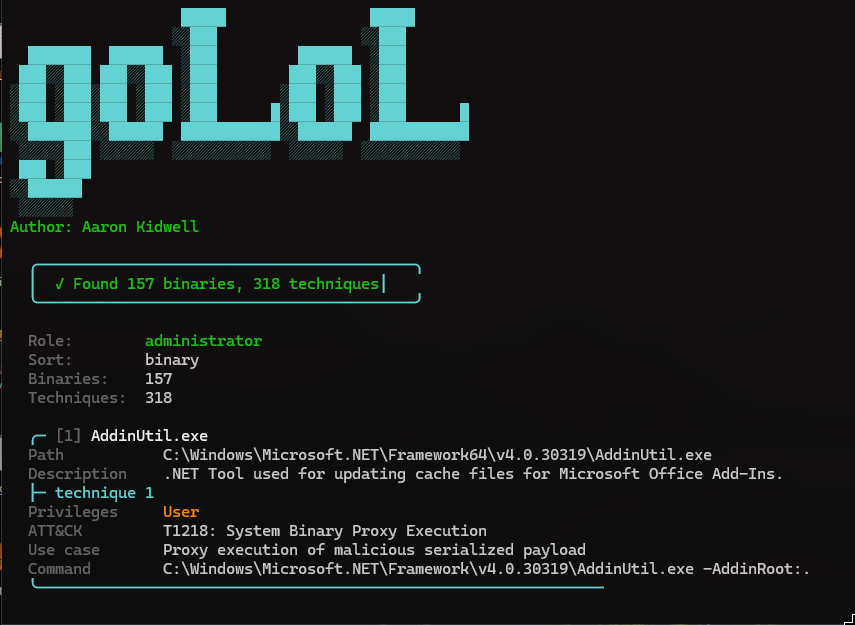 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 irsl/cve-2020-0728
Proof-of-concept exploit for CVE-2020-0728 demonstrating local privilege escalation via Windows TrustedInstaller COM service abuse to bypass file…
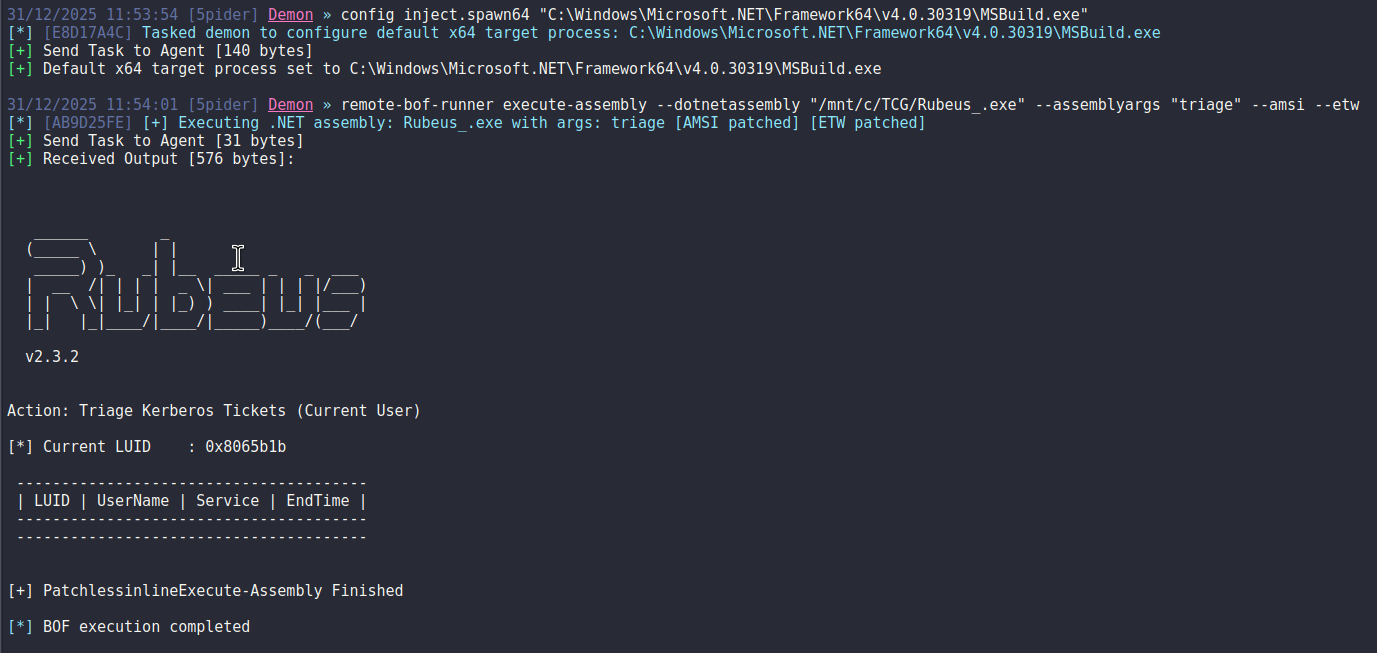 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 karollooool/cve-2026-83991-writeup-and-poc
Proof-of-concept demonstrating a Windows Cloud Files access-check bypass (CVE-2026-83991) that converts a read-only file into a cloud placeholder via…
 adpunisher/ownershipstealer
Command-line utility for Windows that enables SeTakeOwnershipPrivilege and modifies file ownership to the current user, granting access to otherwise…
 nccgroup/diskwalker
Python script to efficiently find files on UNIX like file systems with specific properties (quicker than find)
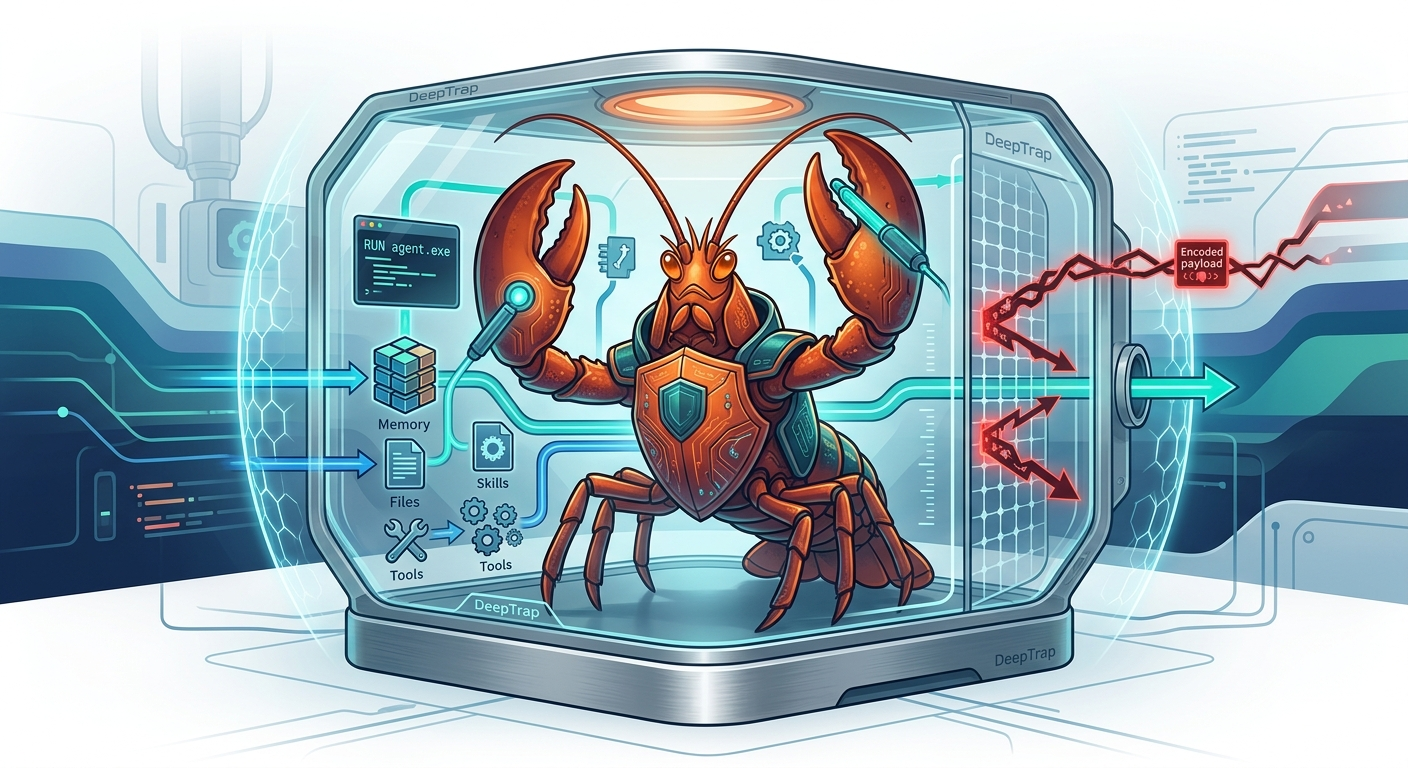 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…