
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
OffensiveNim preview

OffensiveNim

GitHubbyt3bl33d3r/offensivenim

My experiments in weaponizing Nim (https://nim-lang.org/)
binary-exploitationcode-analysiscommand-and-control+8
3.1k
2 years ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

binary-exploitationexploitationpersistence-mechanisms+2
5555 years ago
Openbsd-Privilege-Escalation preview

Openbsd-Privilege-Escalation

GitHubretrymp3/openbsd-privilege-escalation

Script that automates the process of escalating privileges on openbsd system (CVE-2019-19520) by exploiting the xlock binary and againing it's sgid…
authenticationexploitationpenetration-testing+2
21 year ago
RootHelper preview

RootHelper

GitHubnullarray/roothelper

A Bash script that downloads and unzips scripts that will aid with privilege escalation on a Linux system.

exploitationinformation-gatheringpayload-generation+6
5045 years ago
postenum preview

postenum

GitHubmostaphabahadou/postenum

A lightweight, portable, and modular tool for Linux enumeration and privilege escalation.
information-gatheringpenetration-testingpost-exploitation+1
2958 months ago
IAMActionHunter preview

IAMActionHunter

GitHubrhinosecuritylabs/iamactionhunter

An AWS IAM policy statement parser and query tool.
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
2001 year ago
PoolParty preview

PoolParty

GitHubsafebreach-labs/poolparty

A set of fully-undetectable process injection techniques abusing Windows Thread Pools
exploitationpayload-developmentpost-exploitation+3
1.3k2 years ago
clrinject preview

clrinject

GitHubjonatan1024/clrinject

Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
exploitationlateral-movementpenetration-testing+3
2387 years ago
CVE-2026-66804-CrossDevice-LPE preview

CVE-2026-66804-CrossDevice-LPE

GitHubdavidcarliez/cve-2026-66804-crossdevice-lpe

Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…

binary-exploitationexploitationprivilege-escalation+1
121 month ago
Tokenizer preview
Archived

Tokenizer

GitHubzeromemoryex/tokenizer

Kernel Mode Driver for Elevating Process Privileges
exploitationpost-exploitationprivilege-escalation+1
1303 years ago
POSTDump preview

POSTDump

GitHubyolop0wn/postdump

C# tool for LSASS minidump with multiple evasion techniques including indirect syscalls, ETW patching, and PPL bypass via driver or WER fault.…
post-exploitationprivilege-escalationred-teaming
3462 months ago
CVE-2026-74939-escape-the-mac-n-cheese-box preview

CVE-2026-74939-escape-the-mac-n-cheese-box

GitHubsneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box

Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
binary-exploitationexploitationexploit-frameworks+3
124 days ago
CVE-2020-11492 preview

CVE-2020-11492

GitHubcrackercat/cve-2020-11492

Proof-of-concept exploit for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Uses named pipe impersonation to steal SYSTEM token…
container-securityexploitationprivilege-escalation+1
26 years ago
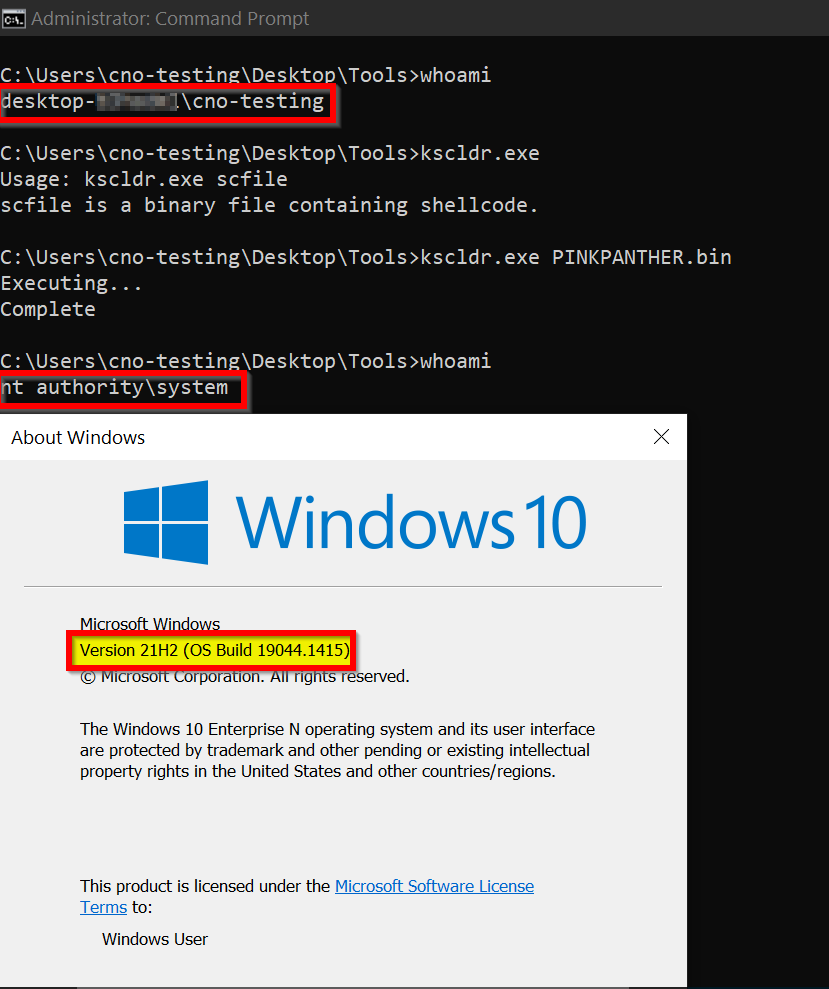
PINKPANTHER preview

PINKPANTHER

GitHubwinterknife/pinkpanther

Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
5192 years ago
docker_lightman_exploit preview

docker_lightman_exploit

GitHubthekevinday/docker_lightman_exploit

Docker CVE-2022-37708

container-escapecontainer-securityexploitation+3
33 years ago
invoker preview
Archived

invoker

GitHubivan-sincek/invoker

Penetration testing utility and antivirus assessment tool.
binary-analysiseducationexploitation+6
3123 years ago
PPLcontrol preview

PPLcontrol

GitHubitm4n/pplcontrol

Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.

defensive-toolsexploitationprivilege-escalation+1
4063 years ago
CVE-2019-16098 preview

CVE-2019-16098

GitHub0xdivyanshu-new/cve-2019-16098

Exploits CVE-2019-16098 in the RTCore64.sys driver to escalate from a low-privileged account to SYSTEM by copying the System process token.

binary-exploitationexploitationprivilege-escalation+1
63 years ago
Previous1234Next