
SneakyEXE
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
exploitationpayload-developmentprivilege-escalation+1
974 years ago
hackernese/sneakyexeAutomatic UAC-Bypassing for custom payloads during privilege escalation testing
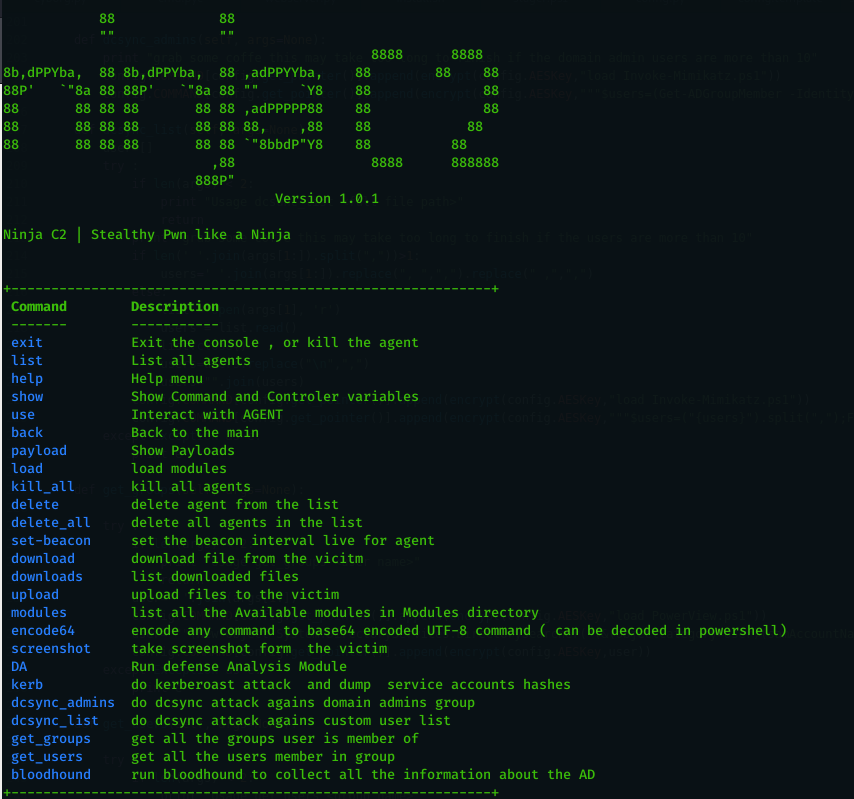 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 maleeshaudan/wordpress-cve-2024-10924--exploit
WordPress CVE-2024-10924 Exploit for Really Simple Security plugin
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 orinimron123/cve-2026-40369-exploit
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 spiralbl0ck/cve-2025-0087-
CVE-2025-0087 EoP full PoC
 cube0x0/cve-2020-1472
Python exploit for CVE-2020-1472 (Netlogon Elevation of Privilege) targeting domain controllers to achieve full domain compromise.
 gergelykalman/cve-2023-38571-a-macos-tcc-bypass-in-music-and-tv
macOS TCC bypass exploit leveraging insecure file rename in Music and TV apps to gain Full Disk Access by overwriting the TCC database via a symlink…
 ally-petitt/cve-2024-48990-exploit
My exploit for CVE-2024-48990. Full details of how I made this are on my blog.
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
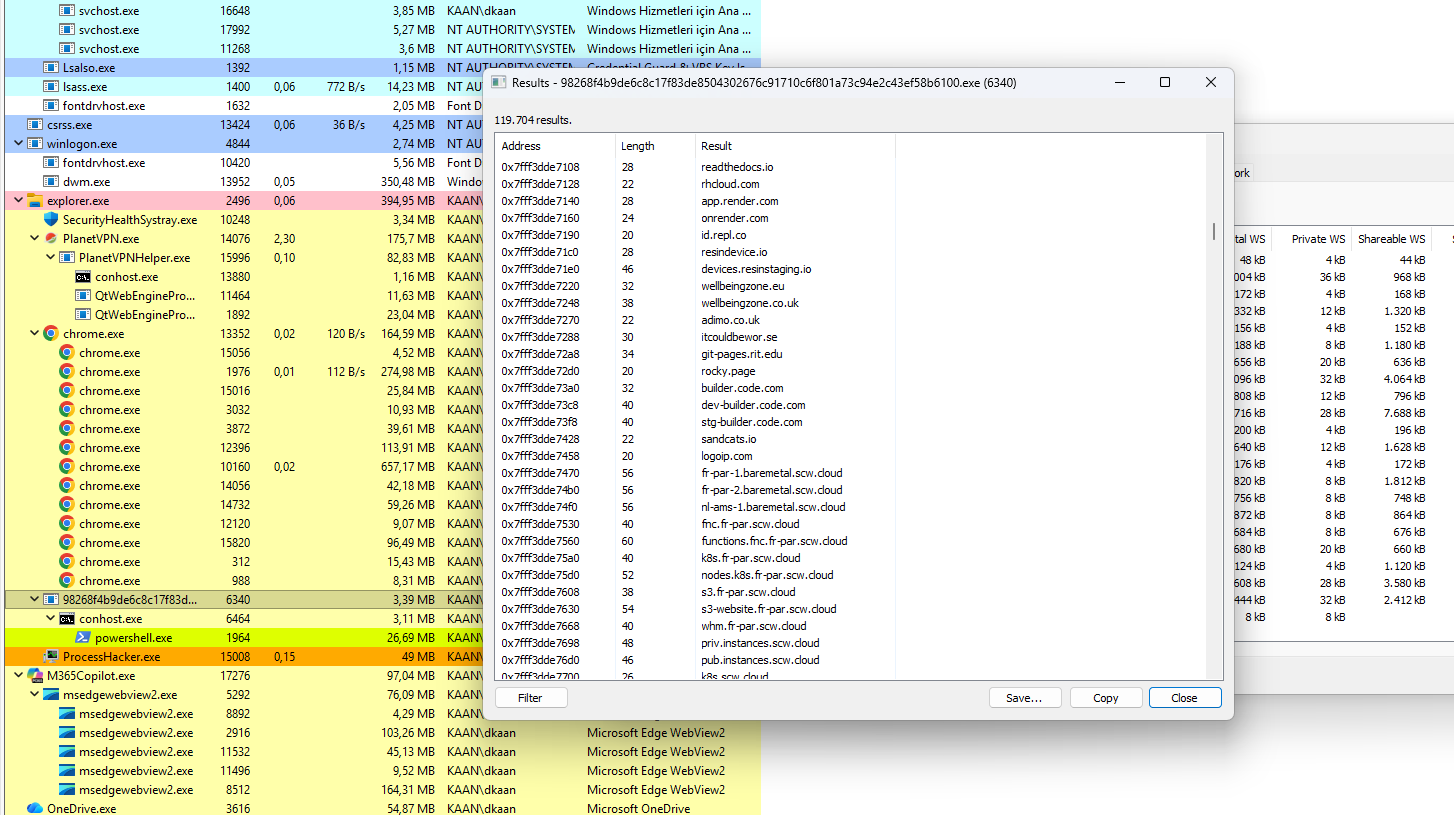 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…