
cve-2016-6662
 boompig/cve-2016-6662
Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.
database-securityexploitationpayload-development+3
1
boompig/cve-2016-6662Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.
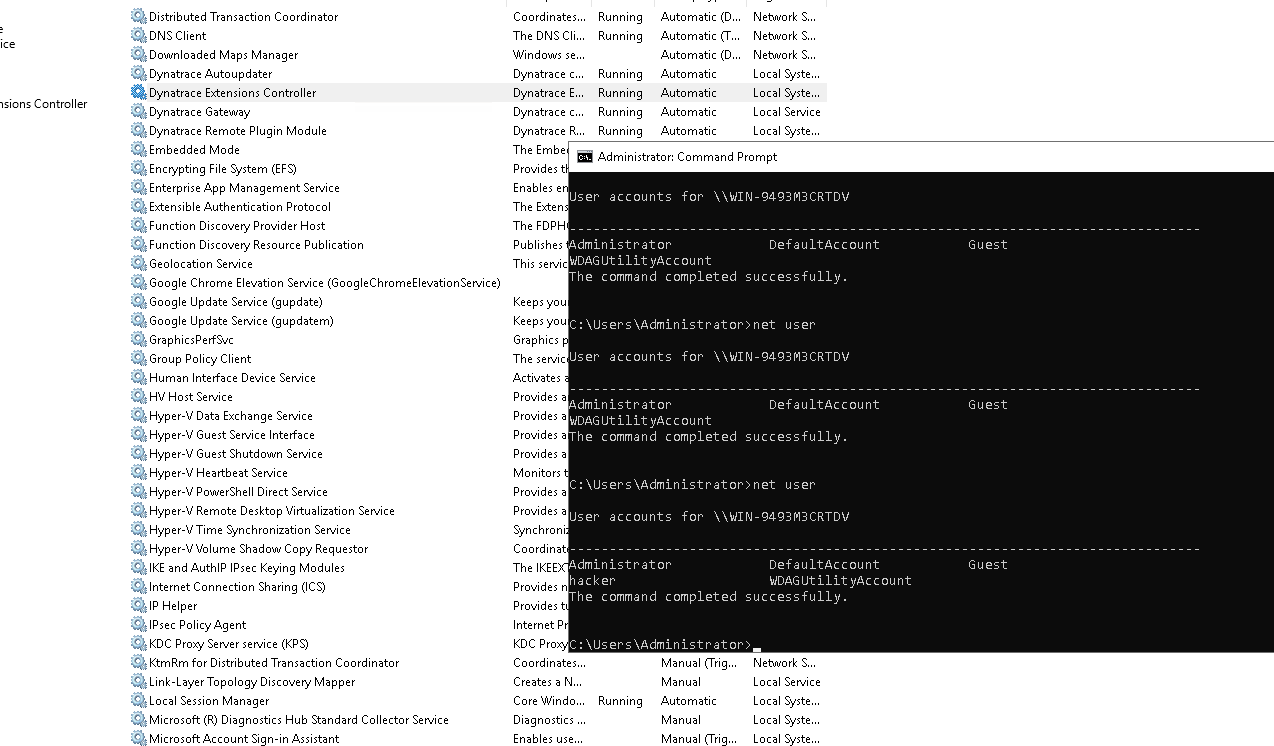 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
 joelgmsec/autordpwn
The Shadow Attack Framework
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
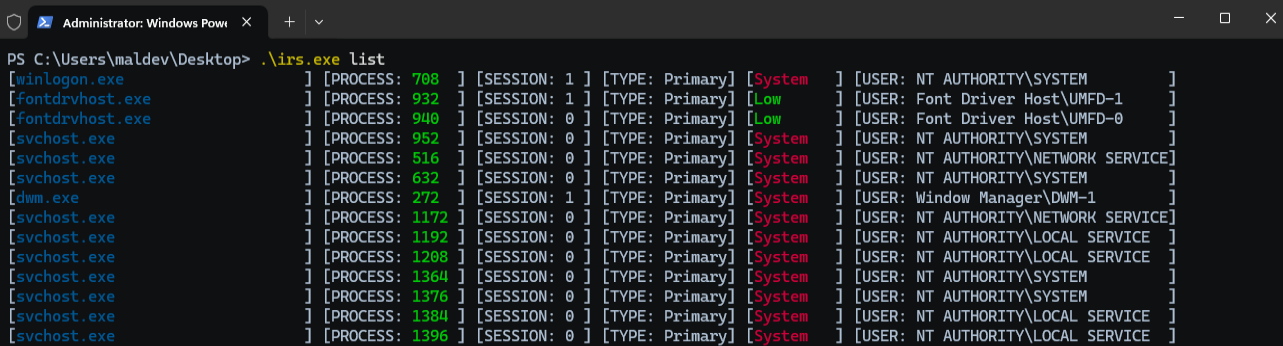 zblurx/impersonate-rs
Rusty Impersonate
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 bad3r/cve-2021-3156-without-ip-command
fork of worawit/CVE-2021-3156 exploit_nss.py modified to work with ifconfig instead of the ip command
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 omergunal/hackerbot
Chat with hacker assistant
 dzonerzy/acunetix_0day
Acunetix 0day RCE
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
 labdookhtegan/cve-2020-0796-exp
CVE-2020-0796-EXP
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386