
cve-2021-1675
 000tonio/cve-2021-1675
PowerShell exploit for CVE-2021-1675 PrintNightmare that disables AMSI and creates a local administrator account on vulnerable Windows systems.
exploitationpayload-generationpenetration-testing+2
000tonio/cve-2021-1675PowerShell exploit for CVE-2021-1675 PrintNightmare that disables AMSI and creates a local administrator account on vulnerable Windows systems.
 b5null/invoke-badsuccessor.ps1
PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
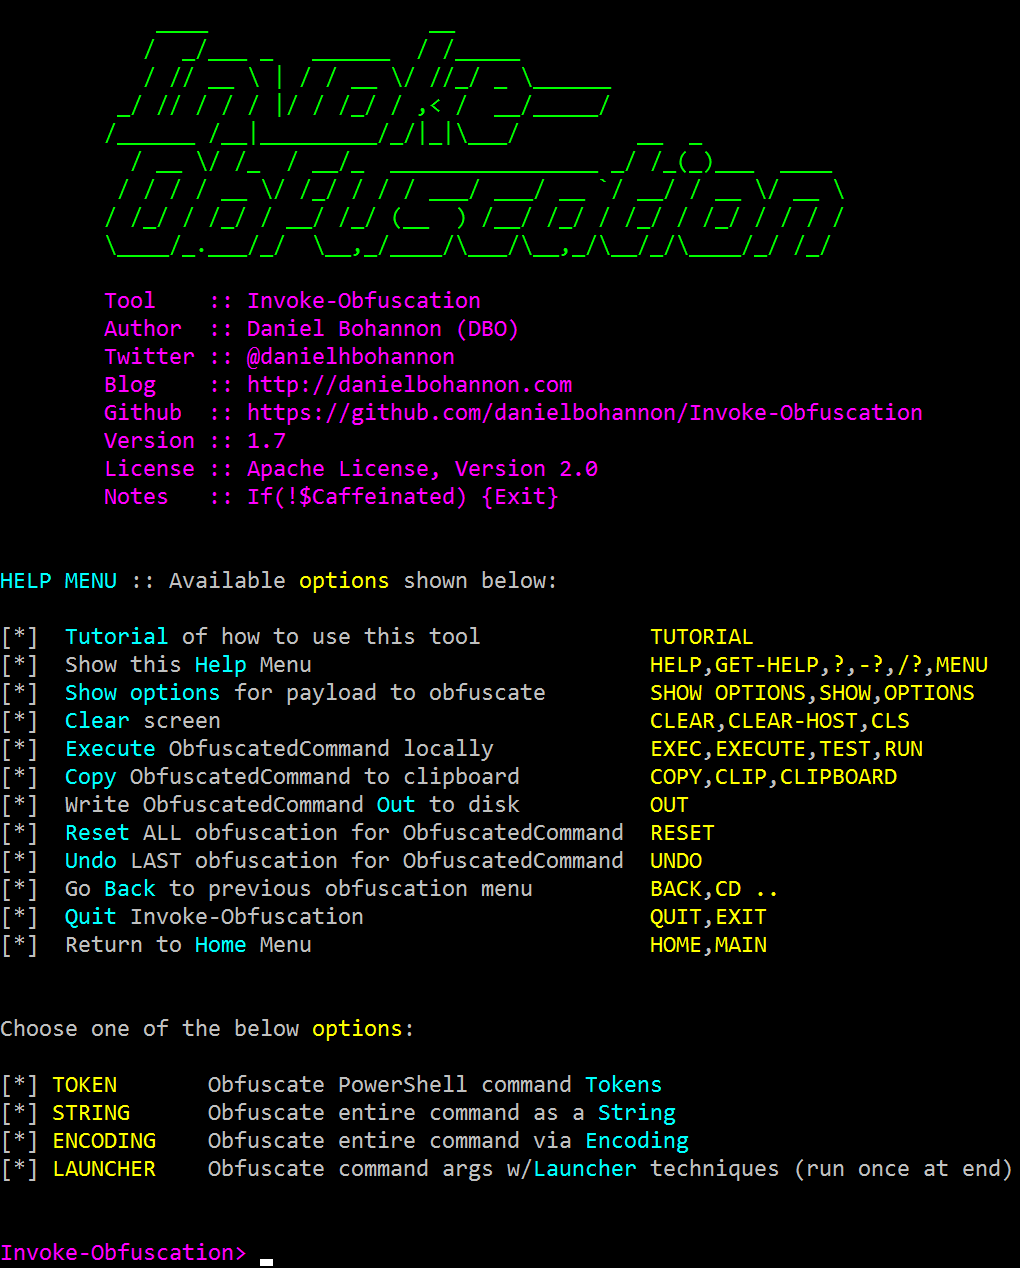 empireproject/empire
Empire is a PowerShell and Python post-exploitation agent.
 0xqn/clsidfinder
PowerShell enumeration script for discovering service-backed COM objects via CLSID/AppID correlation and activation testing.
 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…
 gabriel-lacorte/cve-2025-7771
Arbitrary Function Call Exploit using the ThrottleStop driver
