

spydir
 z3apa3a/spydir
Spydir is a small utility to monitor file changes in Windows directory regardless of subdirectory and files permissions (exploits CVE-2007-0843)
exploitationgeneral-purpose-utilitiesprivilege-escalation+1
9
z3apa3a/spydirSpydir is a small utility to monitor file changes in Windows directory regardless of subdirectory and files permissions (exploits CVE-2007-0843)
 kkevsterrr/backdoorme
powerful auto-backdooring utility
 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 nccgroup/gtfoblookup
Offline command line lookup utility for GTFOBins (https://github.com/GTFOBins/GTFOBins.github.io), LOLBAS (https://github.com/LOLBAS-Project/LOLBAS),…
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
 nccgroup/ncloader
A session-0 capable dll injection utility
 anonymous941/zygote-injection-toolkit
A command-line utility to exploit Android Zygote injection (CVE-2024-31317)
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
 adpunisher/ownershipstealer
Command-line utility for Windows that enables SeTakeOwnershipPrivilege and modifies file ownership to the current user, granting access to otherwise…
 sideeffect42/rootpipetester
RootPipe (CVE-2015-1130) and Phoenix (CVE-2015-3673) vulnerability testing utility for Mac OS X 10.2.8 and later
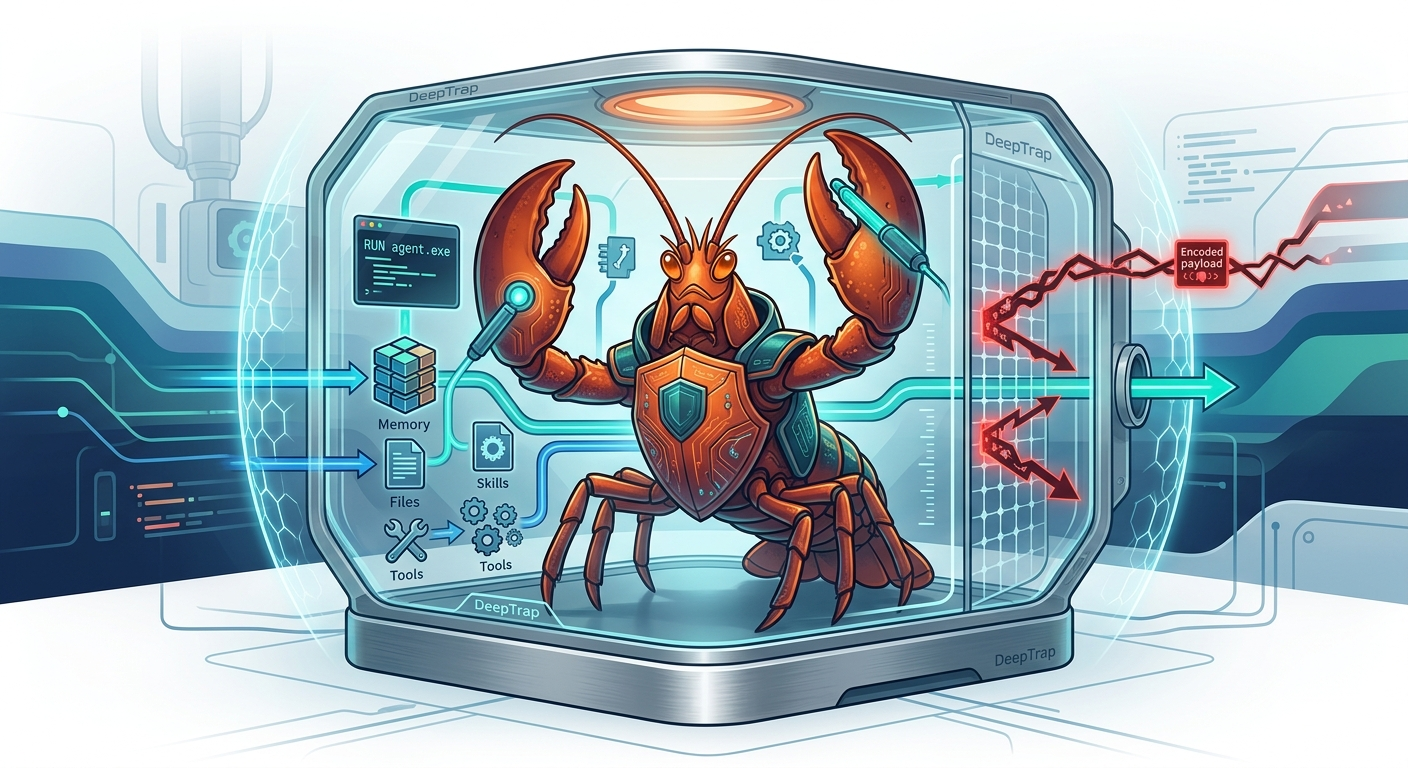 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 sideeffect42/dirtycowtester
Dirty COW (CVE-2016-5195) vulnerability testing utility for Linux-based systems.
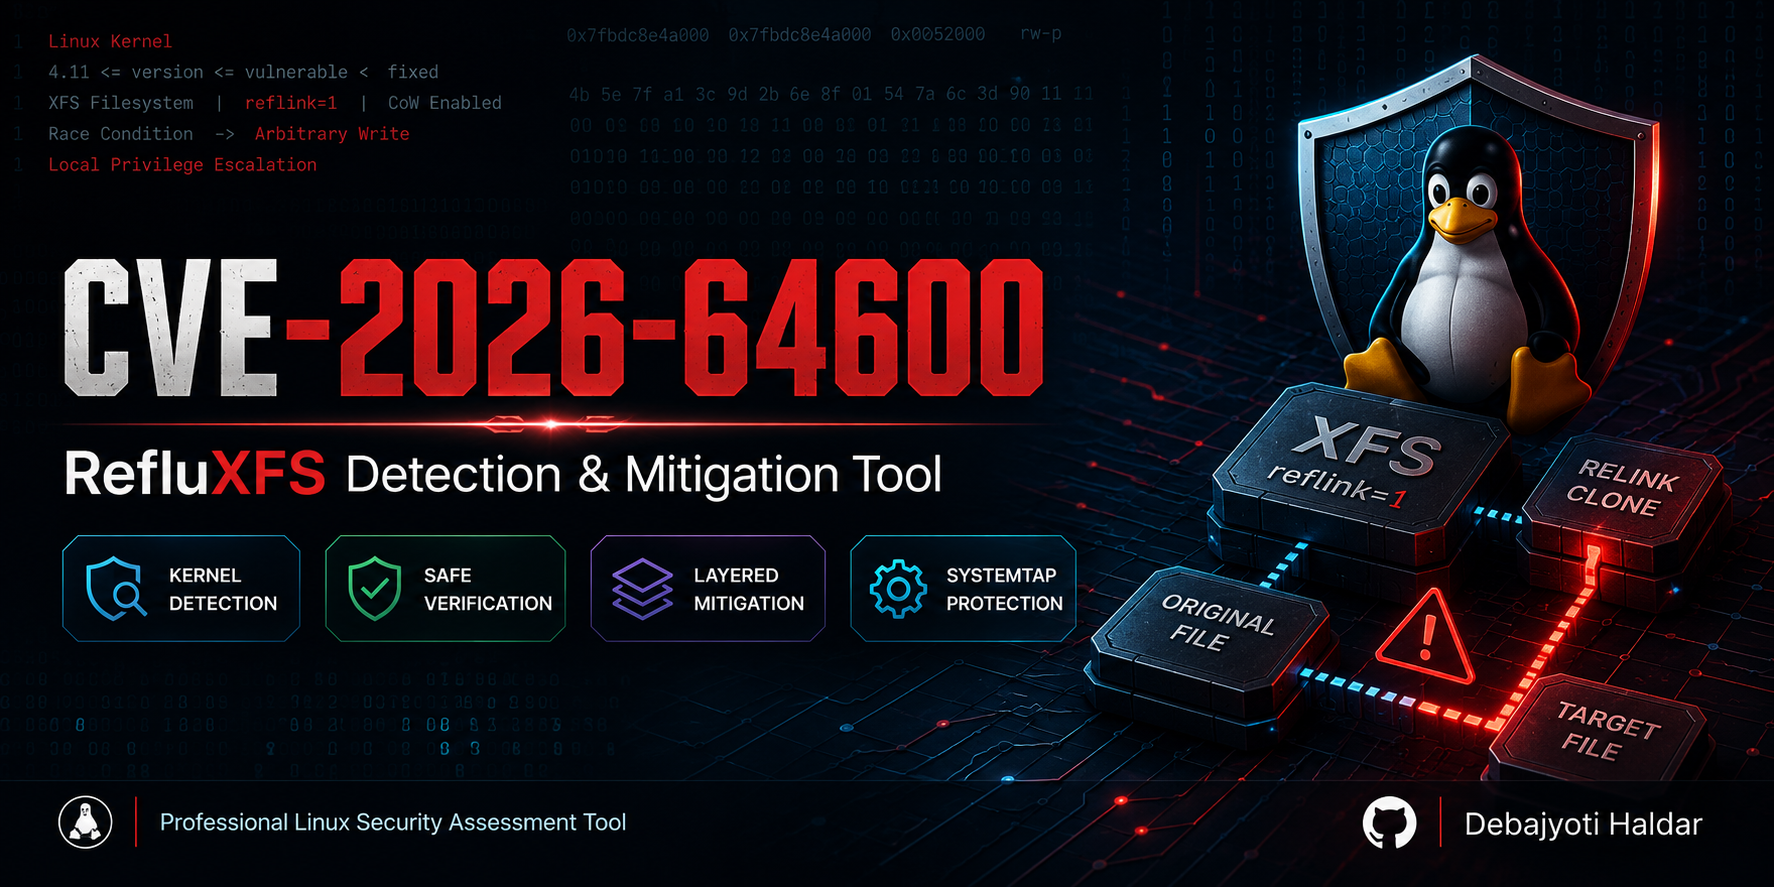 debajyoti0-0/cve-2026-64600
A C-based Linux security utility for detecting, safely verifying (Proof of Concept), and mitigating CVE-2026-64600 (RefluXFS). It provides kernel…
 skimask1690/wisedelete
Windows utility that uses the vulnerable WiseDelfile64.sys driver affected by CVE-2025-66680 to enable kernel-assisted file deletion.
 cwjchoi01/cve-2025-66678
Proof-of-concept exploit for CVE-2025-66678 demonstrating arbitrary MSR and physical memory read/write via a vulnerable hardware utility driver to…
 anilkashyap01/binary-exploitation-and-kernel-escalation
Secured root-level access by identifying and exploiting misconfigurations and outdated software. Buffer overflow vulnerability in an outdated version…