

Inspector
 graniet/inspector
The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…
information-gatheringpenetration-testingprivilege-escalation+1
120
graniet/inspectorThe Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386
 kasunpriyashan/y2s1-project-linux-exploitaion-using-cve-2016-5195-vulnerability
Educational Linux privilege escalation exploit targeting CVE-2016-5195 (Dirty COW) to demonstrate kernel vulnerability exploitation and root access…
 binderlabs/dircreate2system
Weaponizing to get NT SYSTEM for Privileged Directory Creation Bugs with Windows Error Reporting
 homjxi0e/cve-2017-1000367
Proof-of-concept exploit for CVE-2017-1000367, a local privilege escalation vulnerability in Sudo's get_process_ttyname() on Linux, allowing…
 vaginessa/cve-2014-7912
exp for cve-2014-7911 which can get system privillage
 koozxcv/cve-2014-7911-cve-2014-4322_get_root_privilege
CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
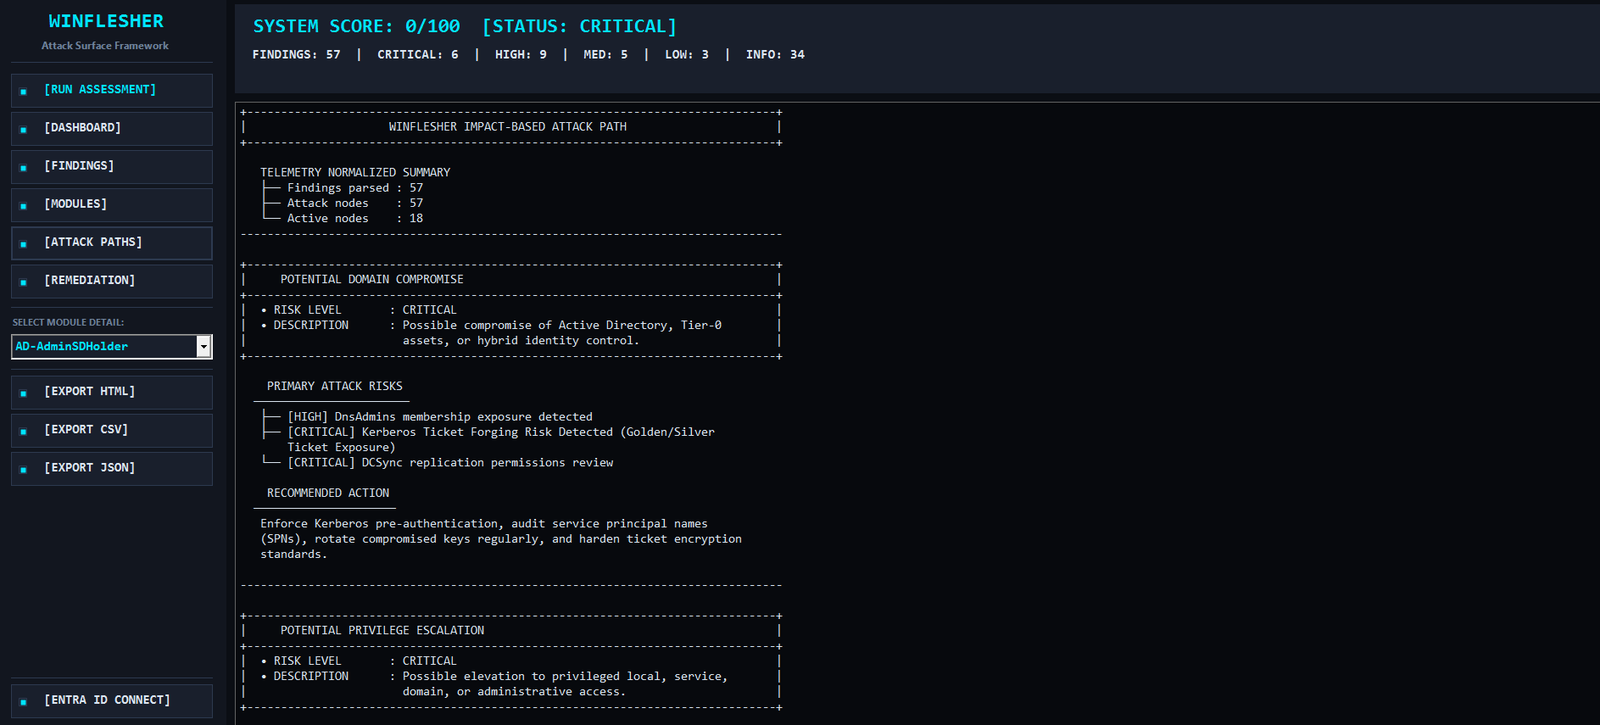 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 ethancunt/cve-2022-45600
Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 zephrfish/copyfail-cve-2026-31431
Linux kernel LPE exploit (CVE-2026-31431) using AF_ALG + splice to overwrite setuid-binary page cache for root. No race conditions, works on all…
 shubham0d/cve-2020-3153
POC code for CVE-2020-3153 - Cisco anyconnect path traversal vulnerability
 gugronnier/cve-2017-16995
Exploit adapted for a specific PoC on Ubuntu 16.04.01