
adPEAS
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
authenticationexploitationinformation-gathering+6
61106960/adpeasPowershell tool to automate Active Directory enumeration.
 uber-common/metta
An information security preparedness tool to do adversarial simulation.
 leoloobeek/lapstoolkit
Tool to audit and attack LAPS environments
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
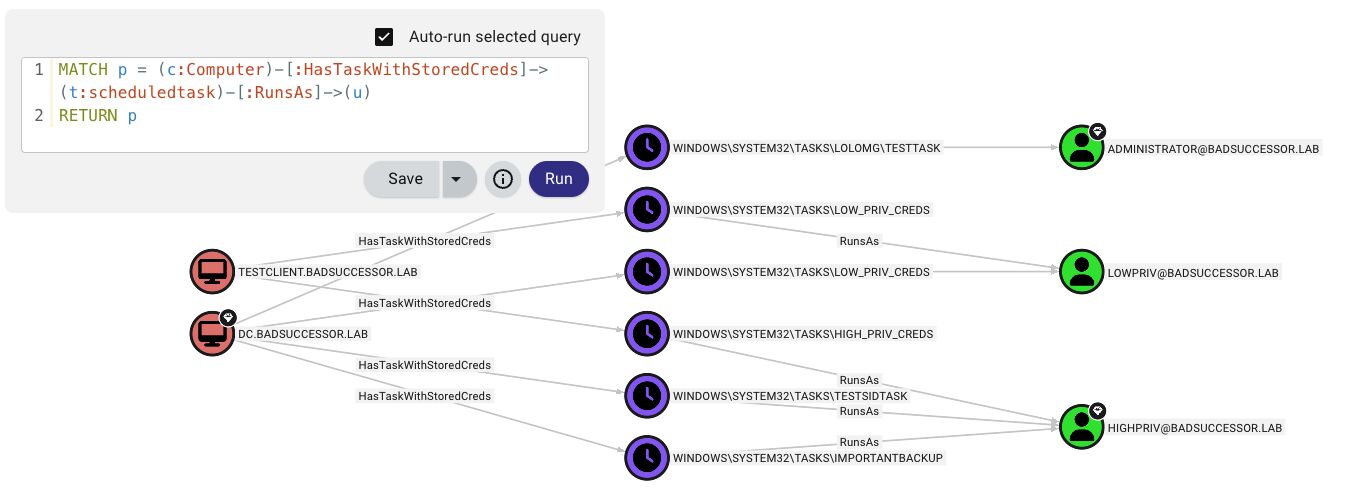 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
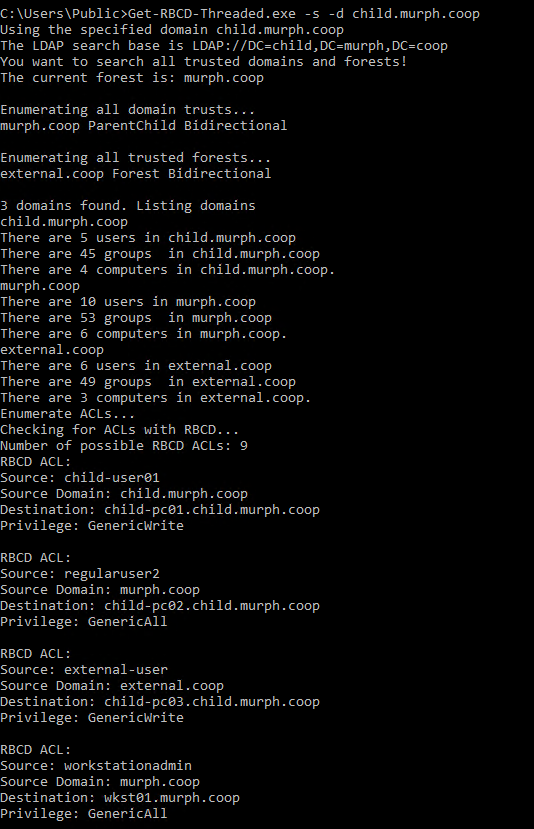 fatrodzianko/get-rbcd-threaded
Tool to discover Resource-Based Constrained Delegation attack paths in Active Directory environments
 garrettfoster13/aced
Parses and resolves a single Active Directory principal's DACL to identify inbound access privileges, resolve SIDs, and log LDAP attributes for…
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 depthsecurity/relayking-depth
Dominate the domain. Relay to royalty.
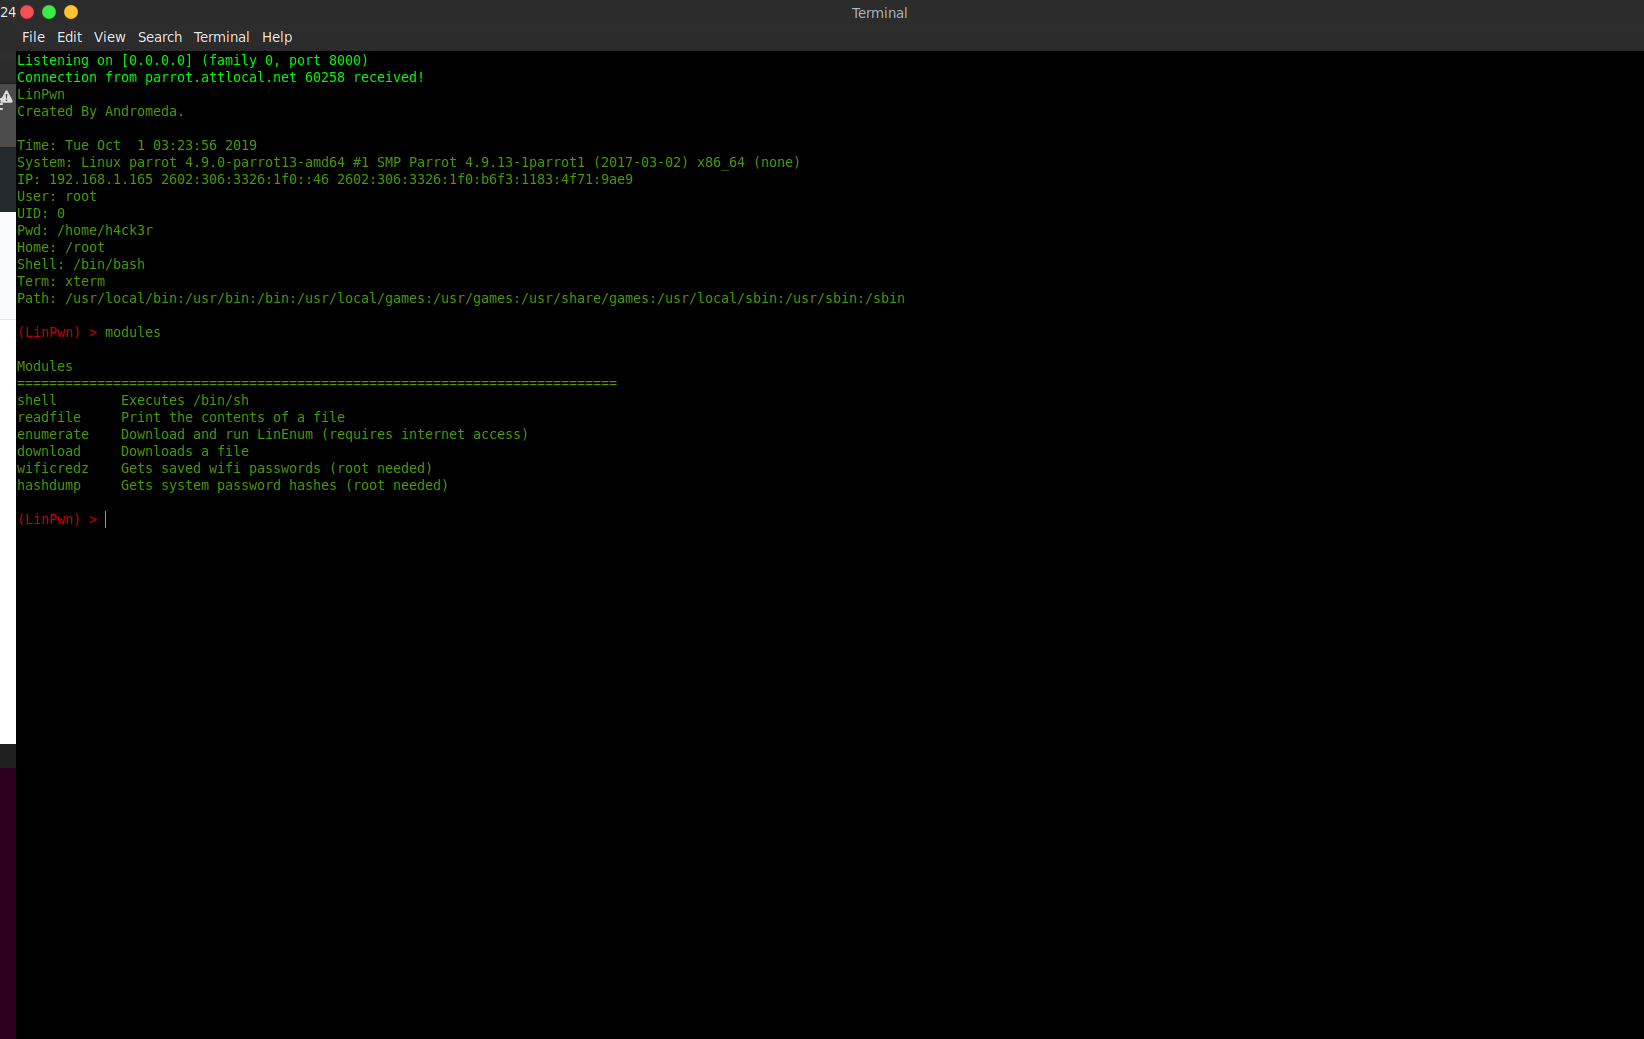 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
 dominicbreuker/pspy
Monitor linux processes without root permissions
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 rasta-mouse/watson
Enumerate missing KBs and suggest exploits for useful Privilege Escalation vulnerabilities
 dafthack/check-localadminhash
Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…