
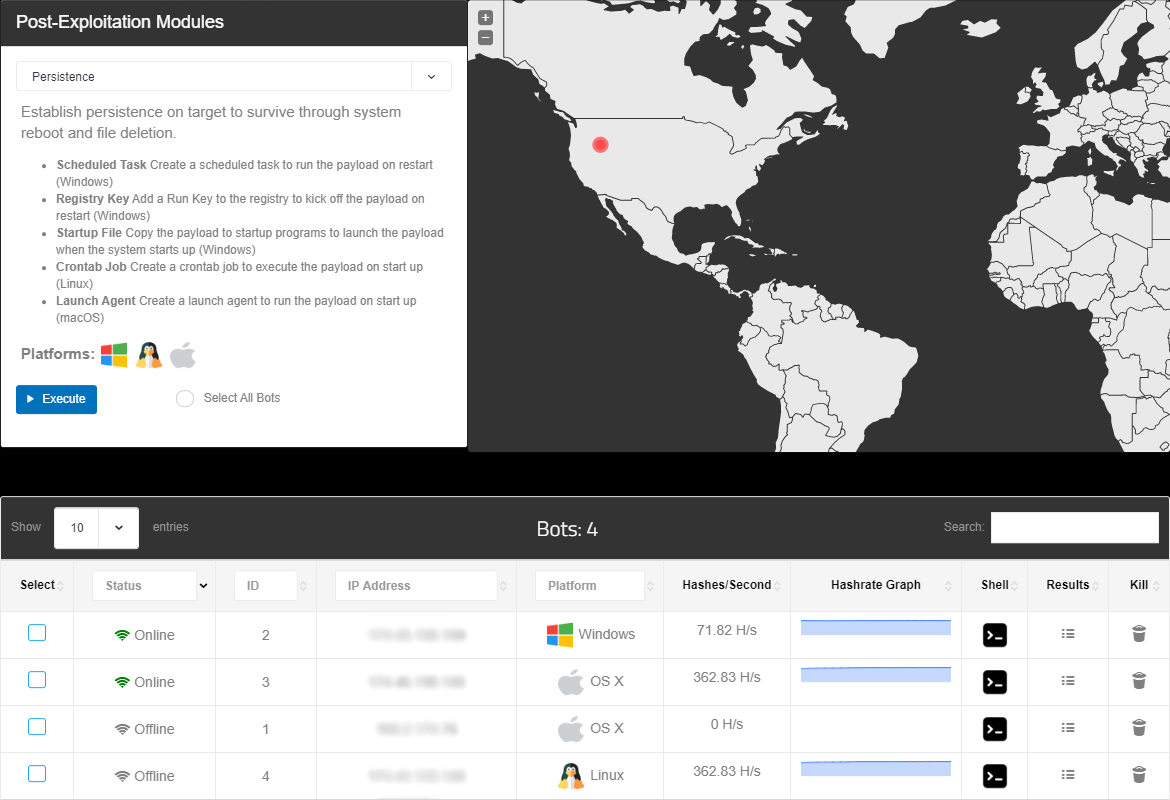
byob
 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
command-and-controleducationpacket-sniffing-analysis+6
malwaredllc/byobAn open-source post-exploitation framework for students, researchers and developers.
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 somhm-solutions/shell-shock
*CVE-2014-6271* Unix Arbitrary Code Execution Exploit commonly know as Shell Shock. Examples, Docs, Incident Response and Vulnerability/Risk…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…