

DSE-Patcher
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
binary-exploitationdefensive-toolsexploitation+2
29
gmh5225/dse-patcherWindows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
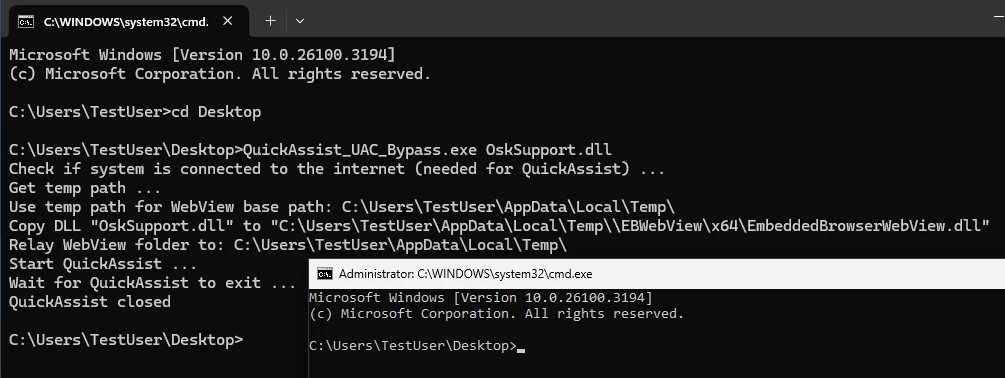 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
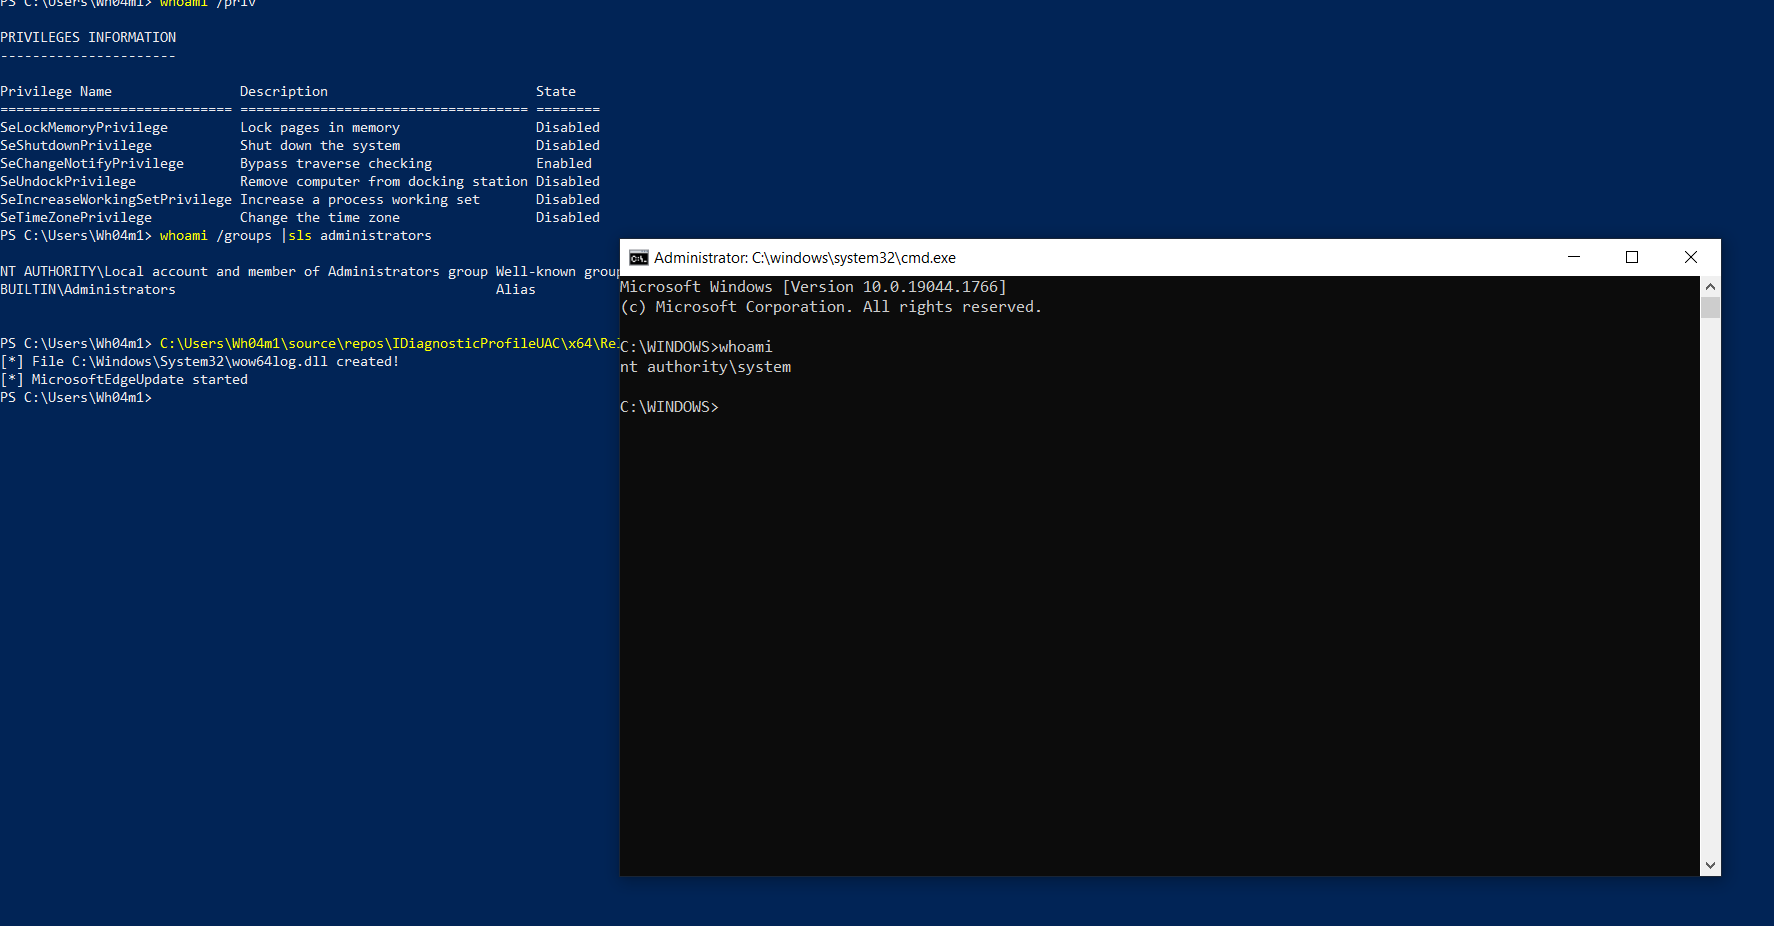 wh04m1001/idiagnosticprofileuac
Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…
 wh04m1001/cve-2022-3368
Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 ethanevans92/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation in sudo. Demonstrates chroot-based NSS manipulation to load a malicious…
 robbert1978/cve-2025-32463_poc
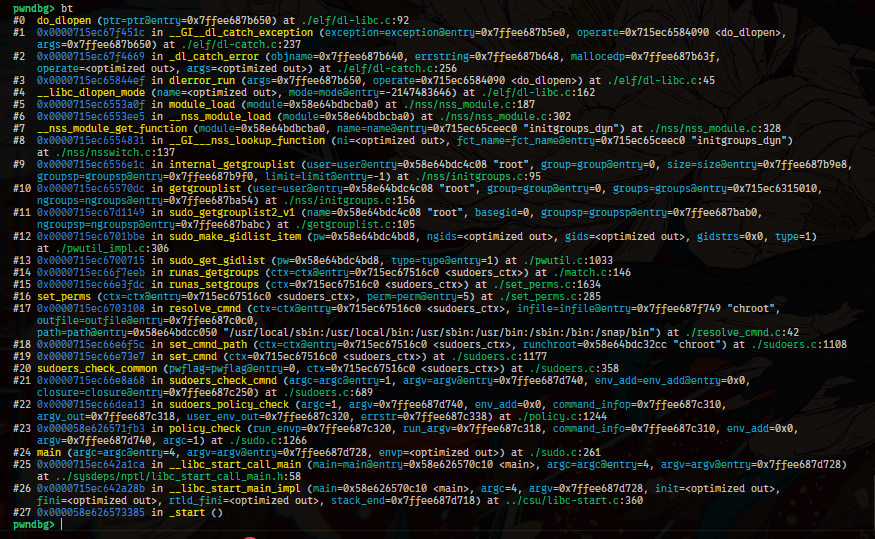
Proof-of-concept exploit for CVE-2025-32463, demonstrating privilege escalation via chroot and nsswitch.conf manipulation to load libnss_systemd.so.2.
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 woshimaniubi8/cve-2026-43499-root-kernelsu
基于内核漏洞CVE-2026-43499的本地提权适配,集成嵌入式 KernelSU.CVE-2026-43499+KernelSU越狱模式
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 everyoneexe/root-s24-e1s
Galaxy S24 SM-S921B S921BXXSDCZB2 RAM-only KernelSU Next + Root S24 app
 fusiondrive/cve-2026-43499-a36
Standalone CVE-2026-43499 port for Galaxy A36 5G SM-A366W A366WVLS3AYG1 with KernelSU late-load
 mbadanoiu/cve-2022-20818
CVE-2022-20818: Local Privilege Escalation via Partial File Read in Cisco SD-WAN