
cve-2022-24644
 gar-re/cve-2022-24644
Proof-of-concept exploit for CVE-2022-24644, demonstrating unauthenticated remote code execution via DNS spoofing against KeyMouse Windows 3.08…
dns-analysisexploitationprivilege-escalation+3
1
gar-re/cve-2022-24644Proof-of-concept exploit for CVE-2022-24644, demonstrating unauthenticated remote code execution via DNS spoofing against KeyMouse Windows 3.08…
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 bigherocenter/cve-2022-41082-poc
Post-authentication remote code execution exploit for Microsoft Exchange Server (CVE-2022-41082) with a PowerShell privilege escalation script for…
 estimated1337/lenovo_exec
CVE-2022-3699 with arbitrary kernel code execution capability
 sinsinology/cve-2022-26503
Proof-of-concept exploit for CVE-2022-26503, a local privilege escalation vulnerability in Veeam Agent for Windows via .NET deserialization, enabling…
 joeymeech/cve-2022-0847-exploit-implementation
Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.
 bariskizilkaya/cve-2022-20186_ctxz
Exploit for CVE-2022-20186 in Arm Mali kernel driver, achieving arbitrary kernel code execution from untrusted app domain to disable SELinux and gain…
 smiletablabo/cve-2022-46395
Exploit for CVE-2022-46395, an Arm Mali kernel driver vulnerability, achieving arbitrary kernel code execution to disable SELinux and gain root on…
 smiletablabo/cve-2022-20186
Exploit for CVE-2022-20186 in the Arm Mali kernel driver, achieving arbitrary kernel code execution to disable SELinux and gain root on Google Pixel…
 ruia-ruia/cve-2022-29582-exploit
Exploit for CVE-2022-29582 targeting Google's Kernel CTF
 iamdarshana/cve-2022-49186-research
Security research and proof-of-concept exploit for CVE-2022-49186, a Linux kernel privilege escalation vulnerability in the Visconti clock driver,…
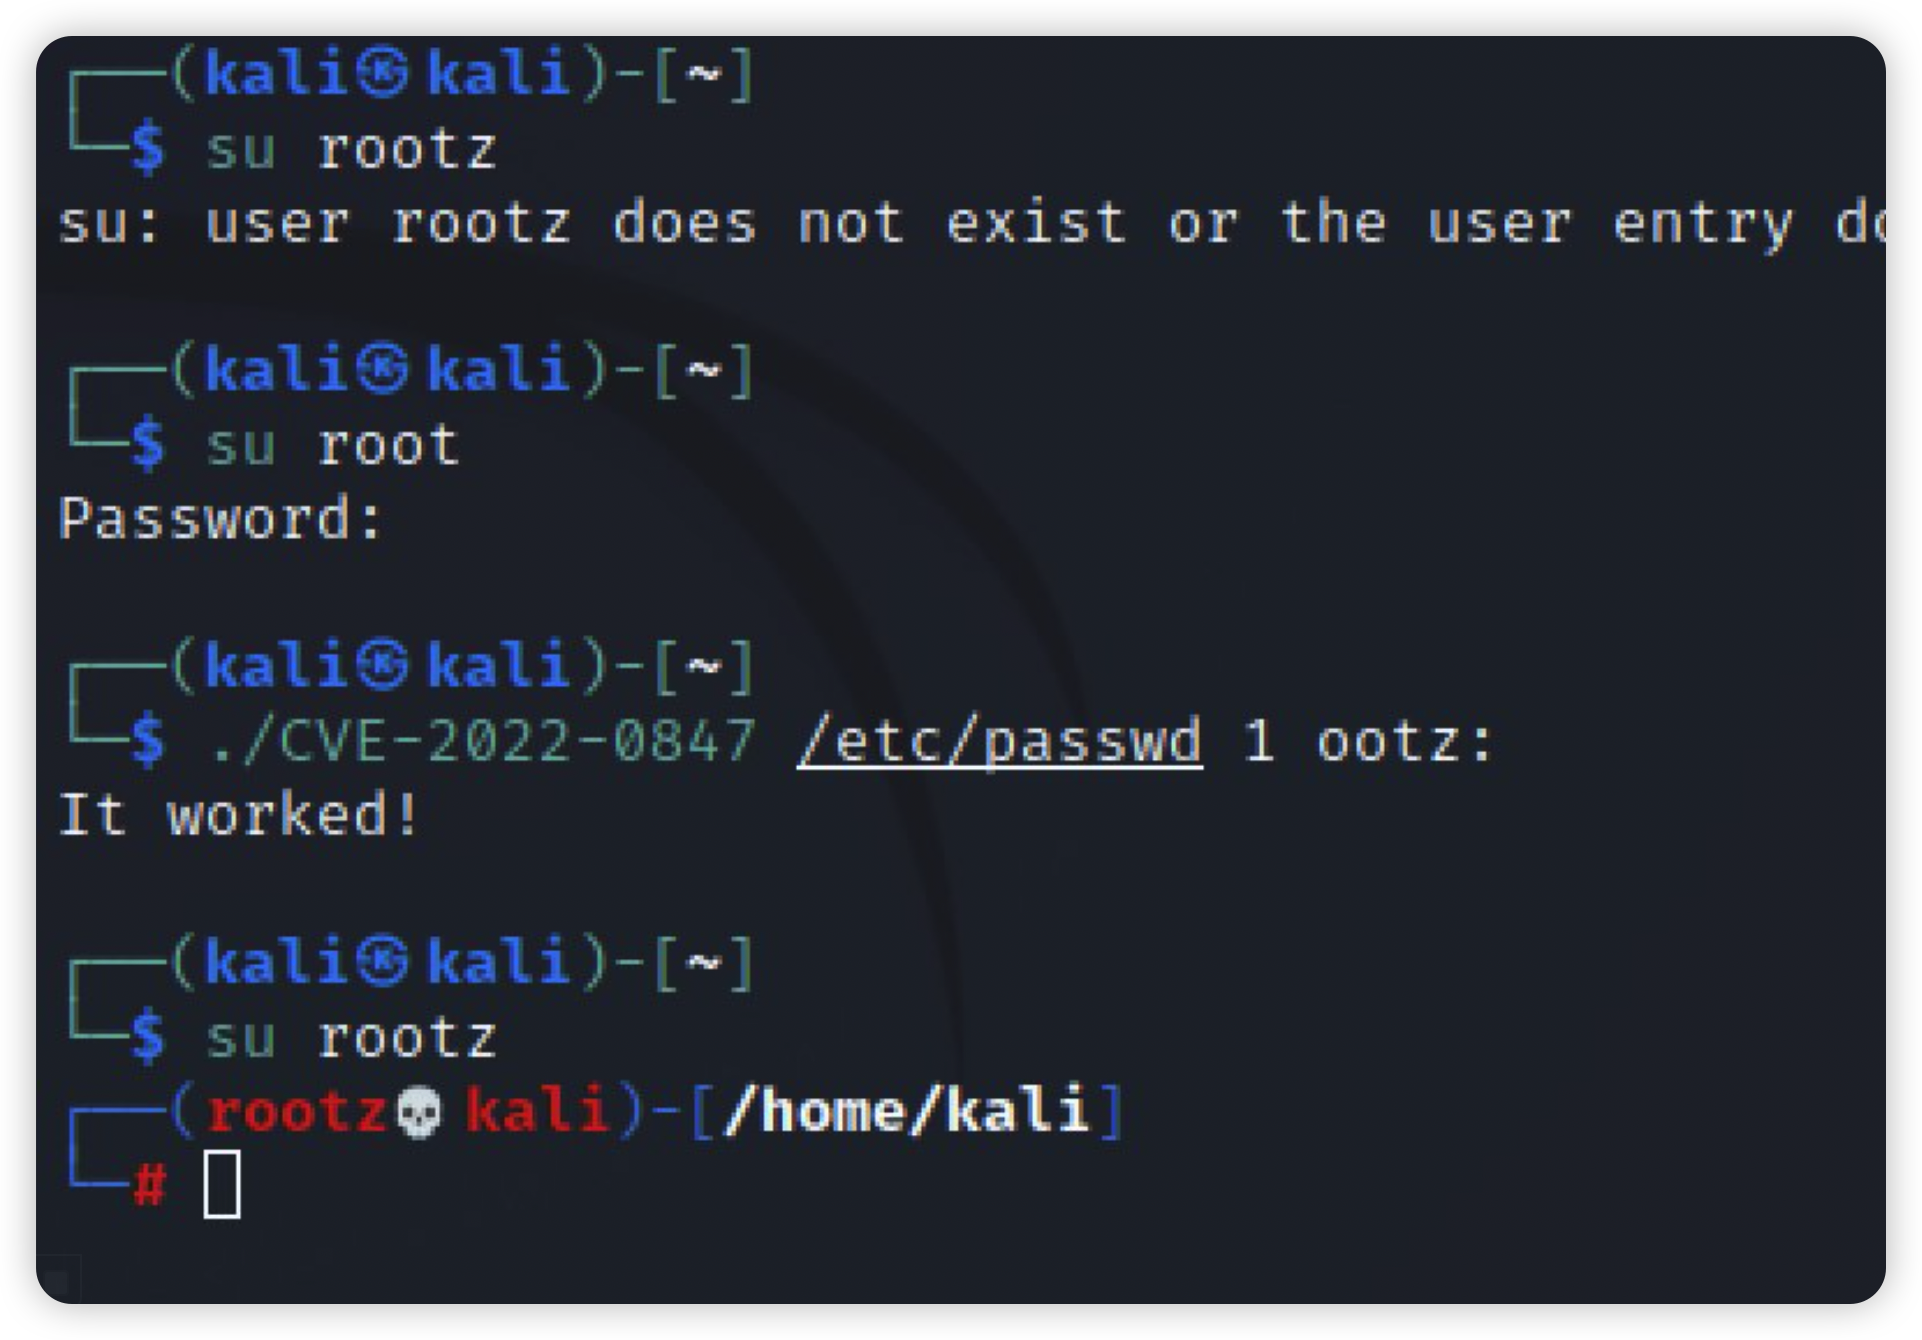 lucksec/cve-2022-0847
Linux kernel privilege escalation exploit for CVE-2022-0847 (Dirty Pipe). Provides a root shell by overwriting arbitrary read-only files. Includes…
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 albocoder/cve-2022-27666-exploits
There are 2 exploitation methods that exploit CVE-2022-27666. For more info on how to use these code bases please check my blog.
 iamz24/cve-2021-3493_cve-2022-3357
Research repository with source code and documentation for CVE-2021-3493 (privilege escalation) and CVE-2022-3357 (RCE), demonstrating combined…
 balki97/owassrf-cve-2022-41082-poc
PoC for the CVE-2022-41080 , CVE-2022-41082 and CVE-2022-41076 Vulnerabilities Affecting Microsoft Exchange Servers
 0xirongoat/dirty-pipe
Implementation of Max Kellermann's exploit for CVE-2022-0847
 faisalfs10x/webmin-cve-2022-0824-revshell
Post-authentication reverse shell exploit for Webmin <=1.984 leveraging CVE-2022-0824 File Manager privilege escalation. Downloads and executes a CGI…