
CVE-2024-0507_CVE-2024-0200-github
 convisolabs/cve-2024-0507_cve-2024-0200-github
Exploits for GitHub Enterprise CVE-2024-0507 and CVE-2024-0200
exploitationpenetration-testingprivilege-escalation+2
convisolabs/cve-2024-0507_cve-2024-0200-githubExploits for GitHub Enterprise CVE-2024-0507 and CVE-2024-0200
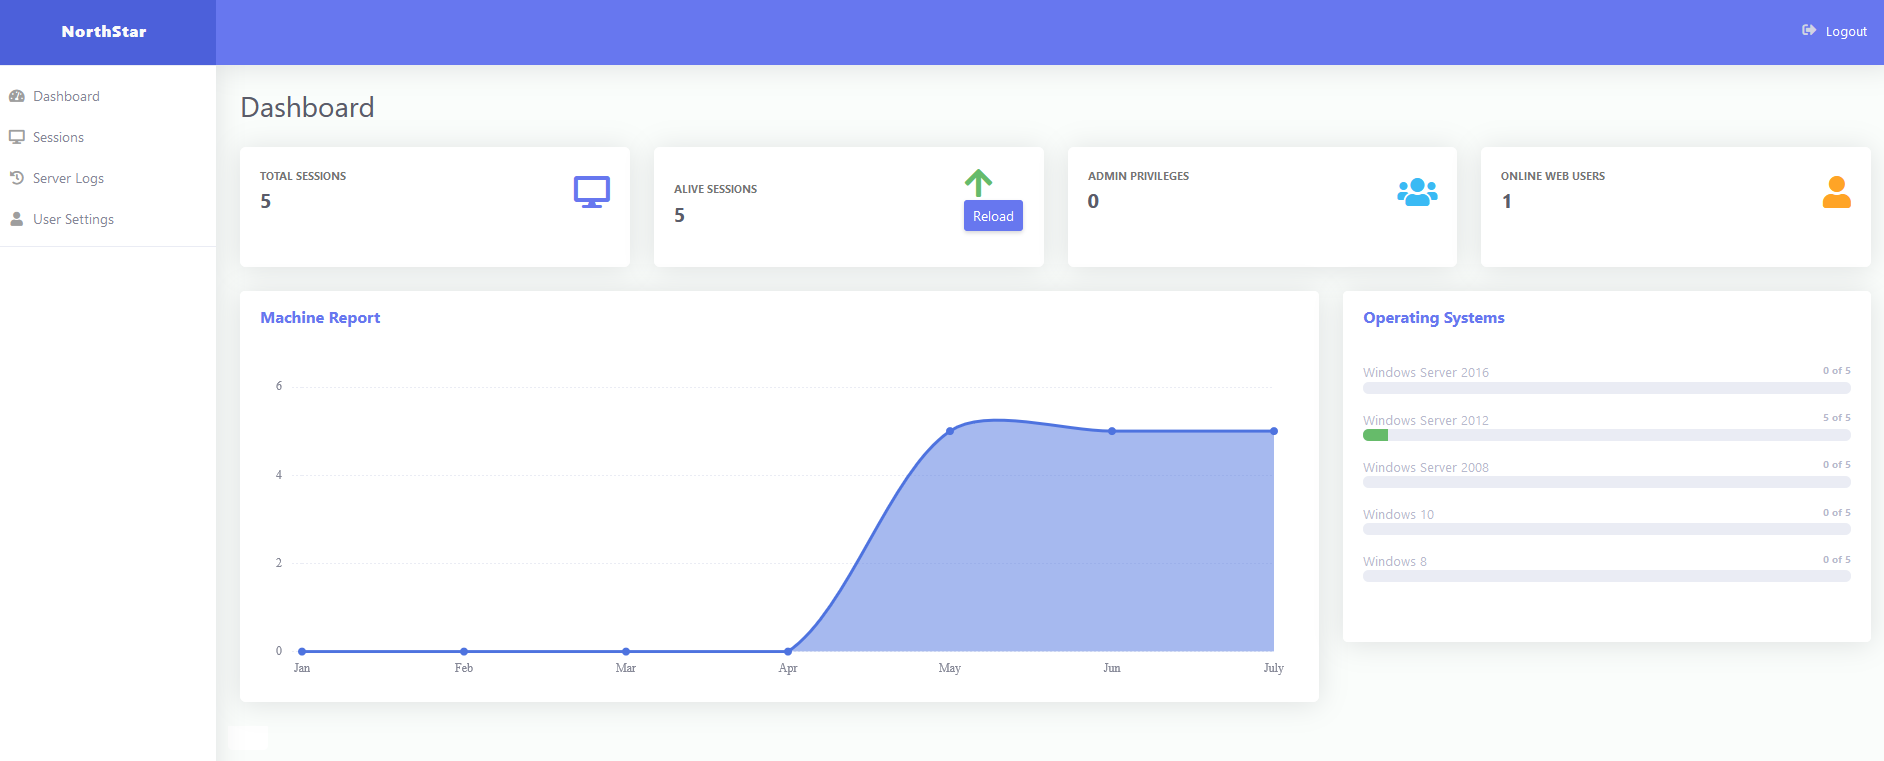 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
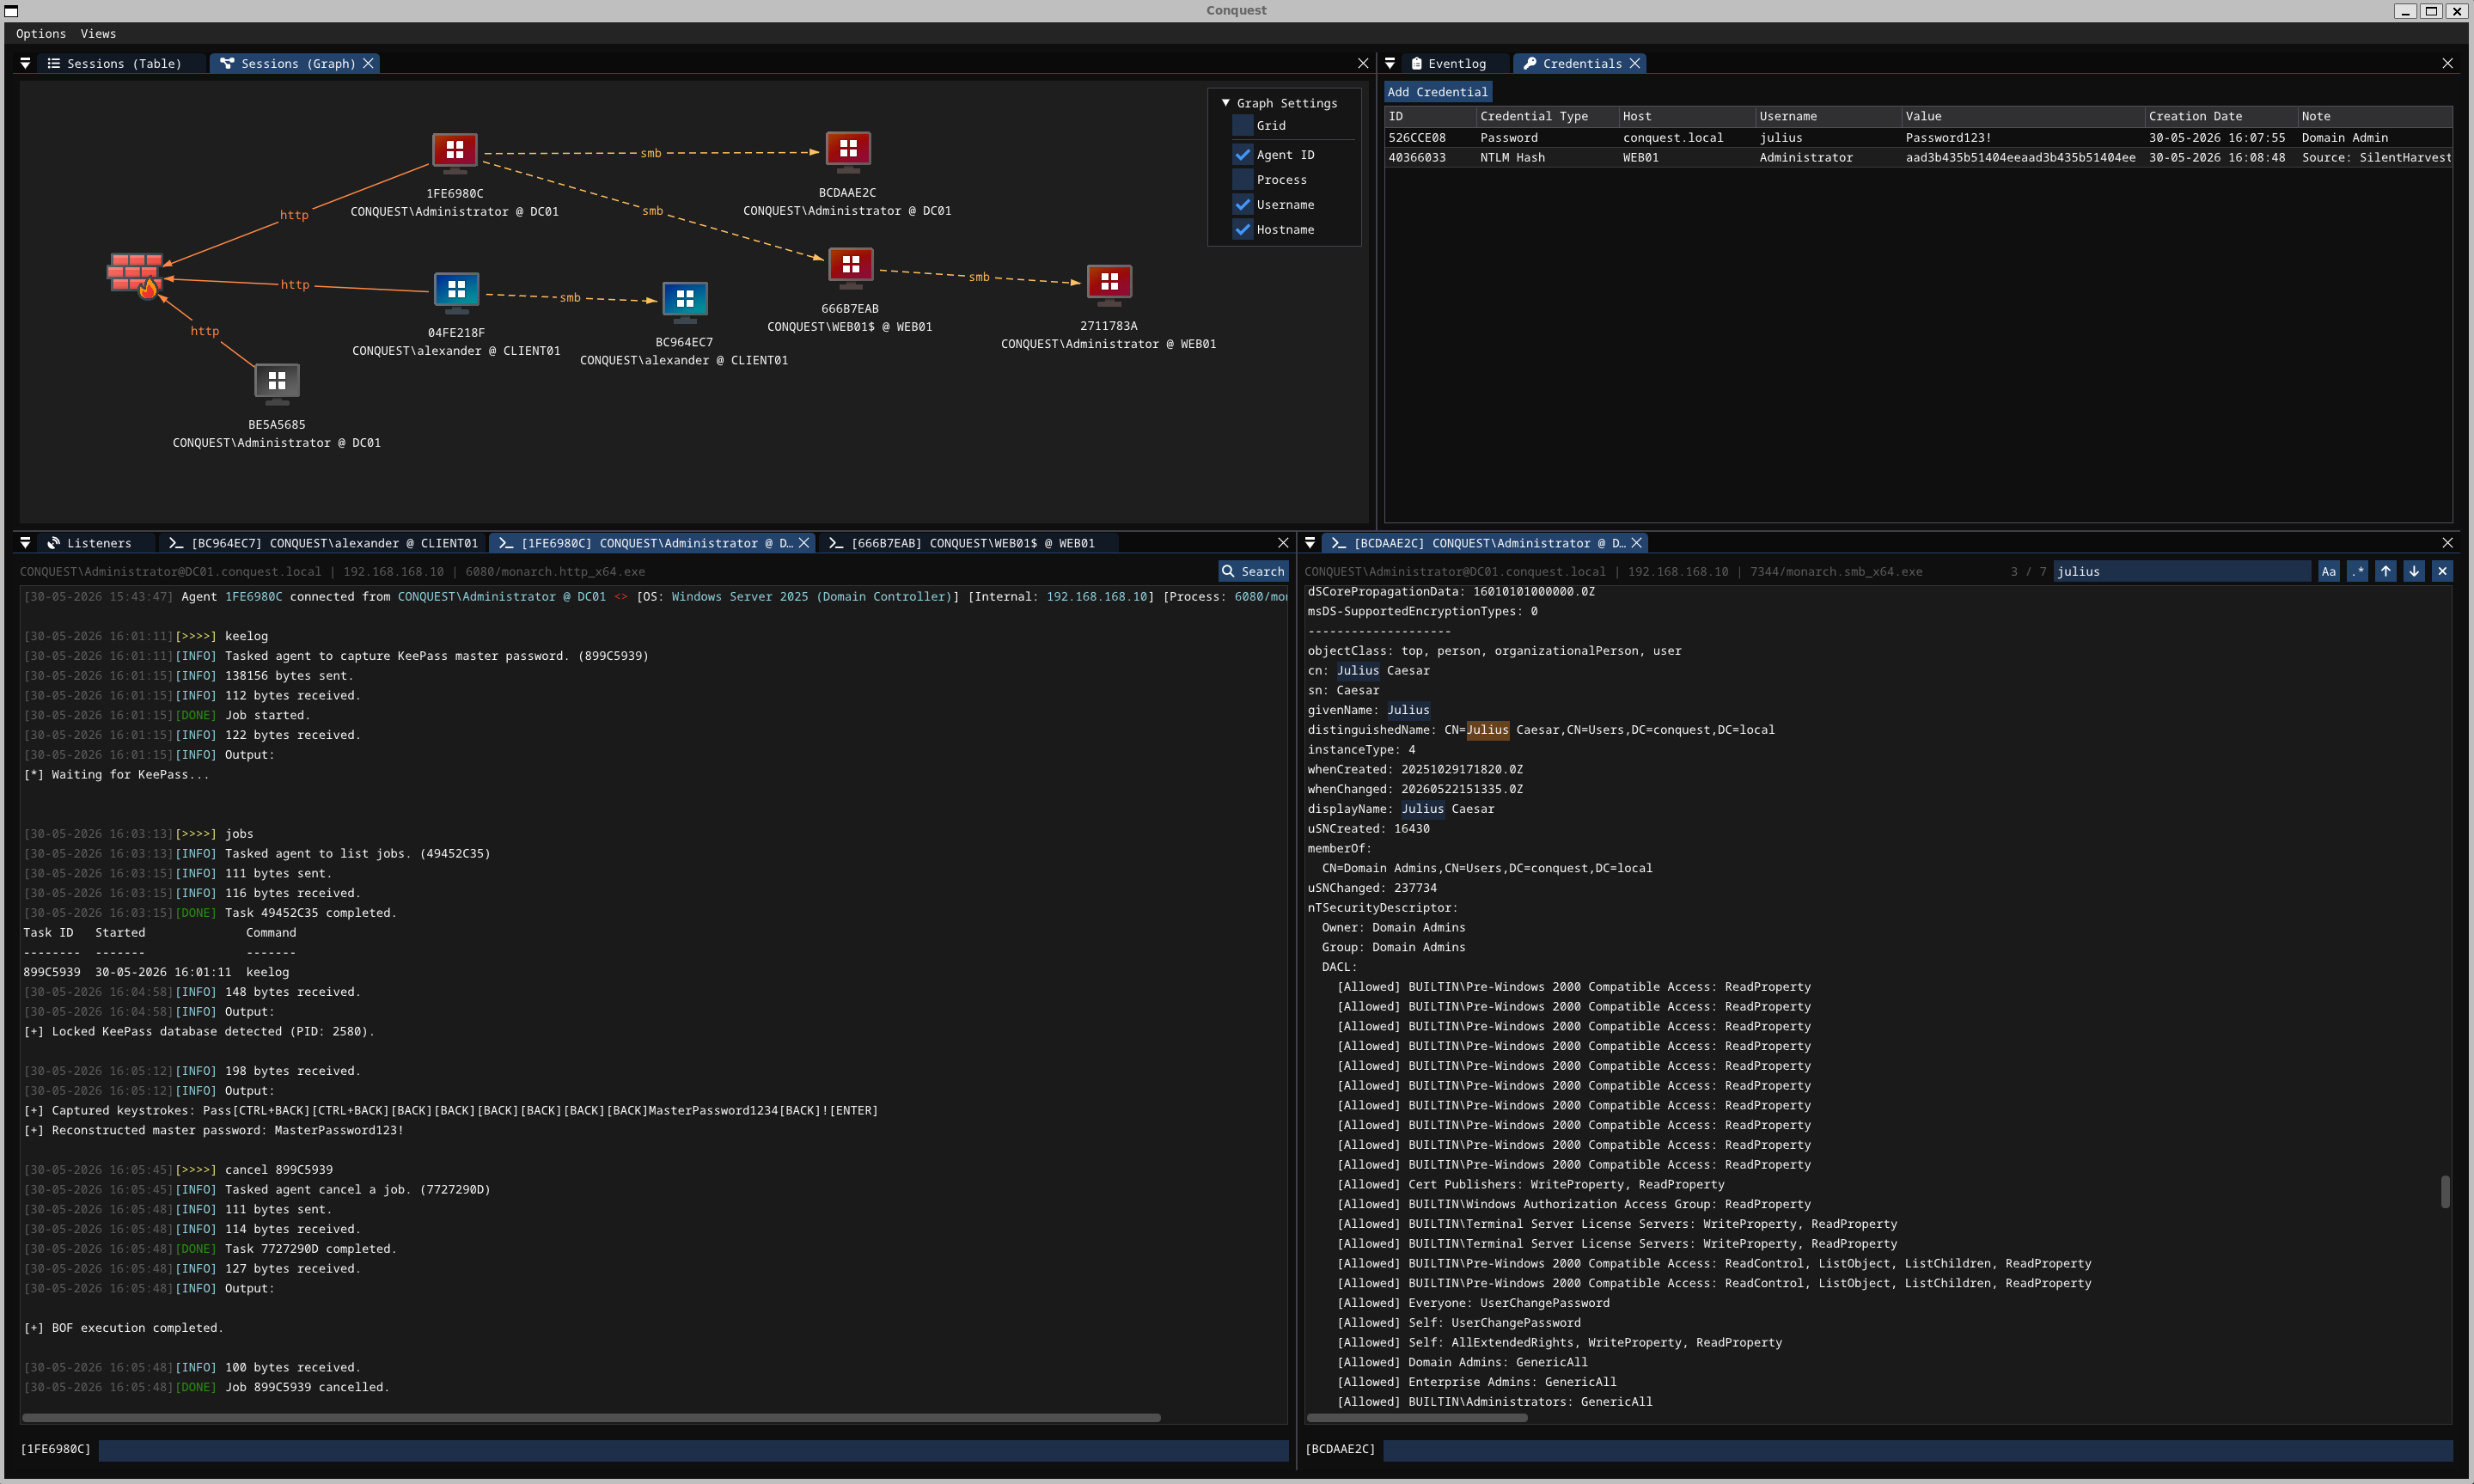 jakobfriedl/conquest
Conquest is a feature-rich and malleable command & control/post-exploitation framework developed in Nim.
 green-avocado/cve-2023-4911
https://www.qualys.com/2023/10/03/cve-2023-4911/looney-tunables-local-privilege-escalation-glibc-ld-so.txt
 mranonymous234/sandbox-escape-ios-18.0-26.0
This uses CVE-2025-43407 as exploit and still testing working not gauranteed.
 n1et/cve-2019-18634
An Python Exploit for Sudo vulnerability CVE-2019-18634
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 r3nhat/grat2
We developed GRAT2 Command & Control (C2) project for learning purpose.
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 cisc0-gif/kitt
Python-Based Pentesting Framework
 sfrdevelopment/windows-smb-vulnerability-framework-cve-2025-33073
Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…
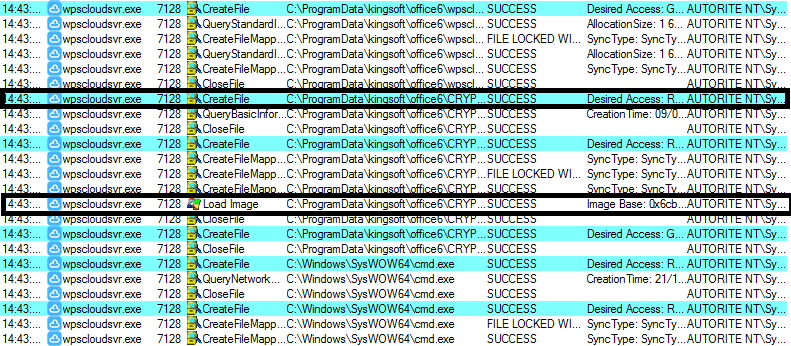 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
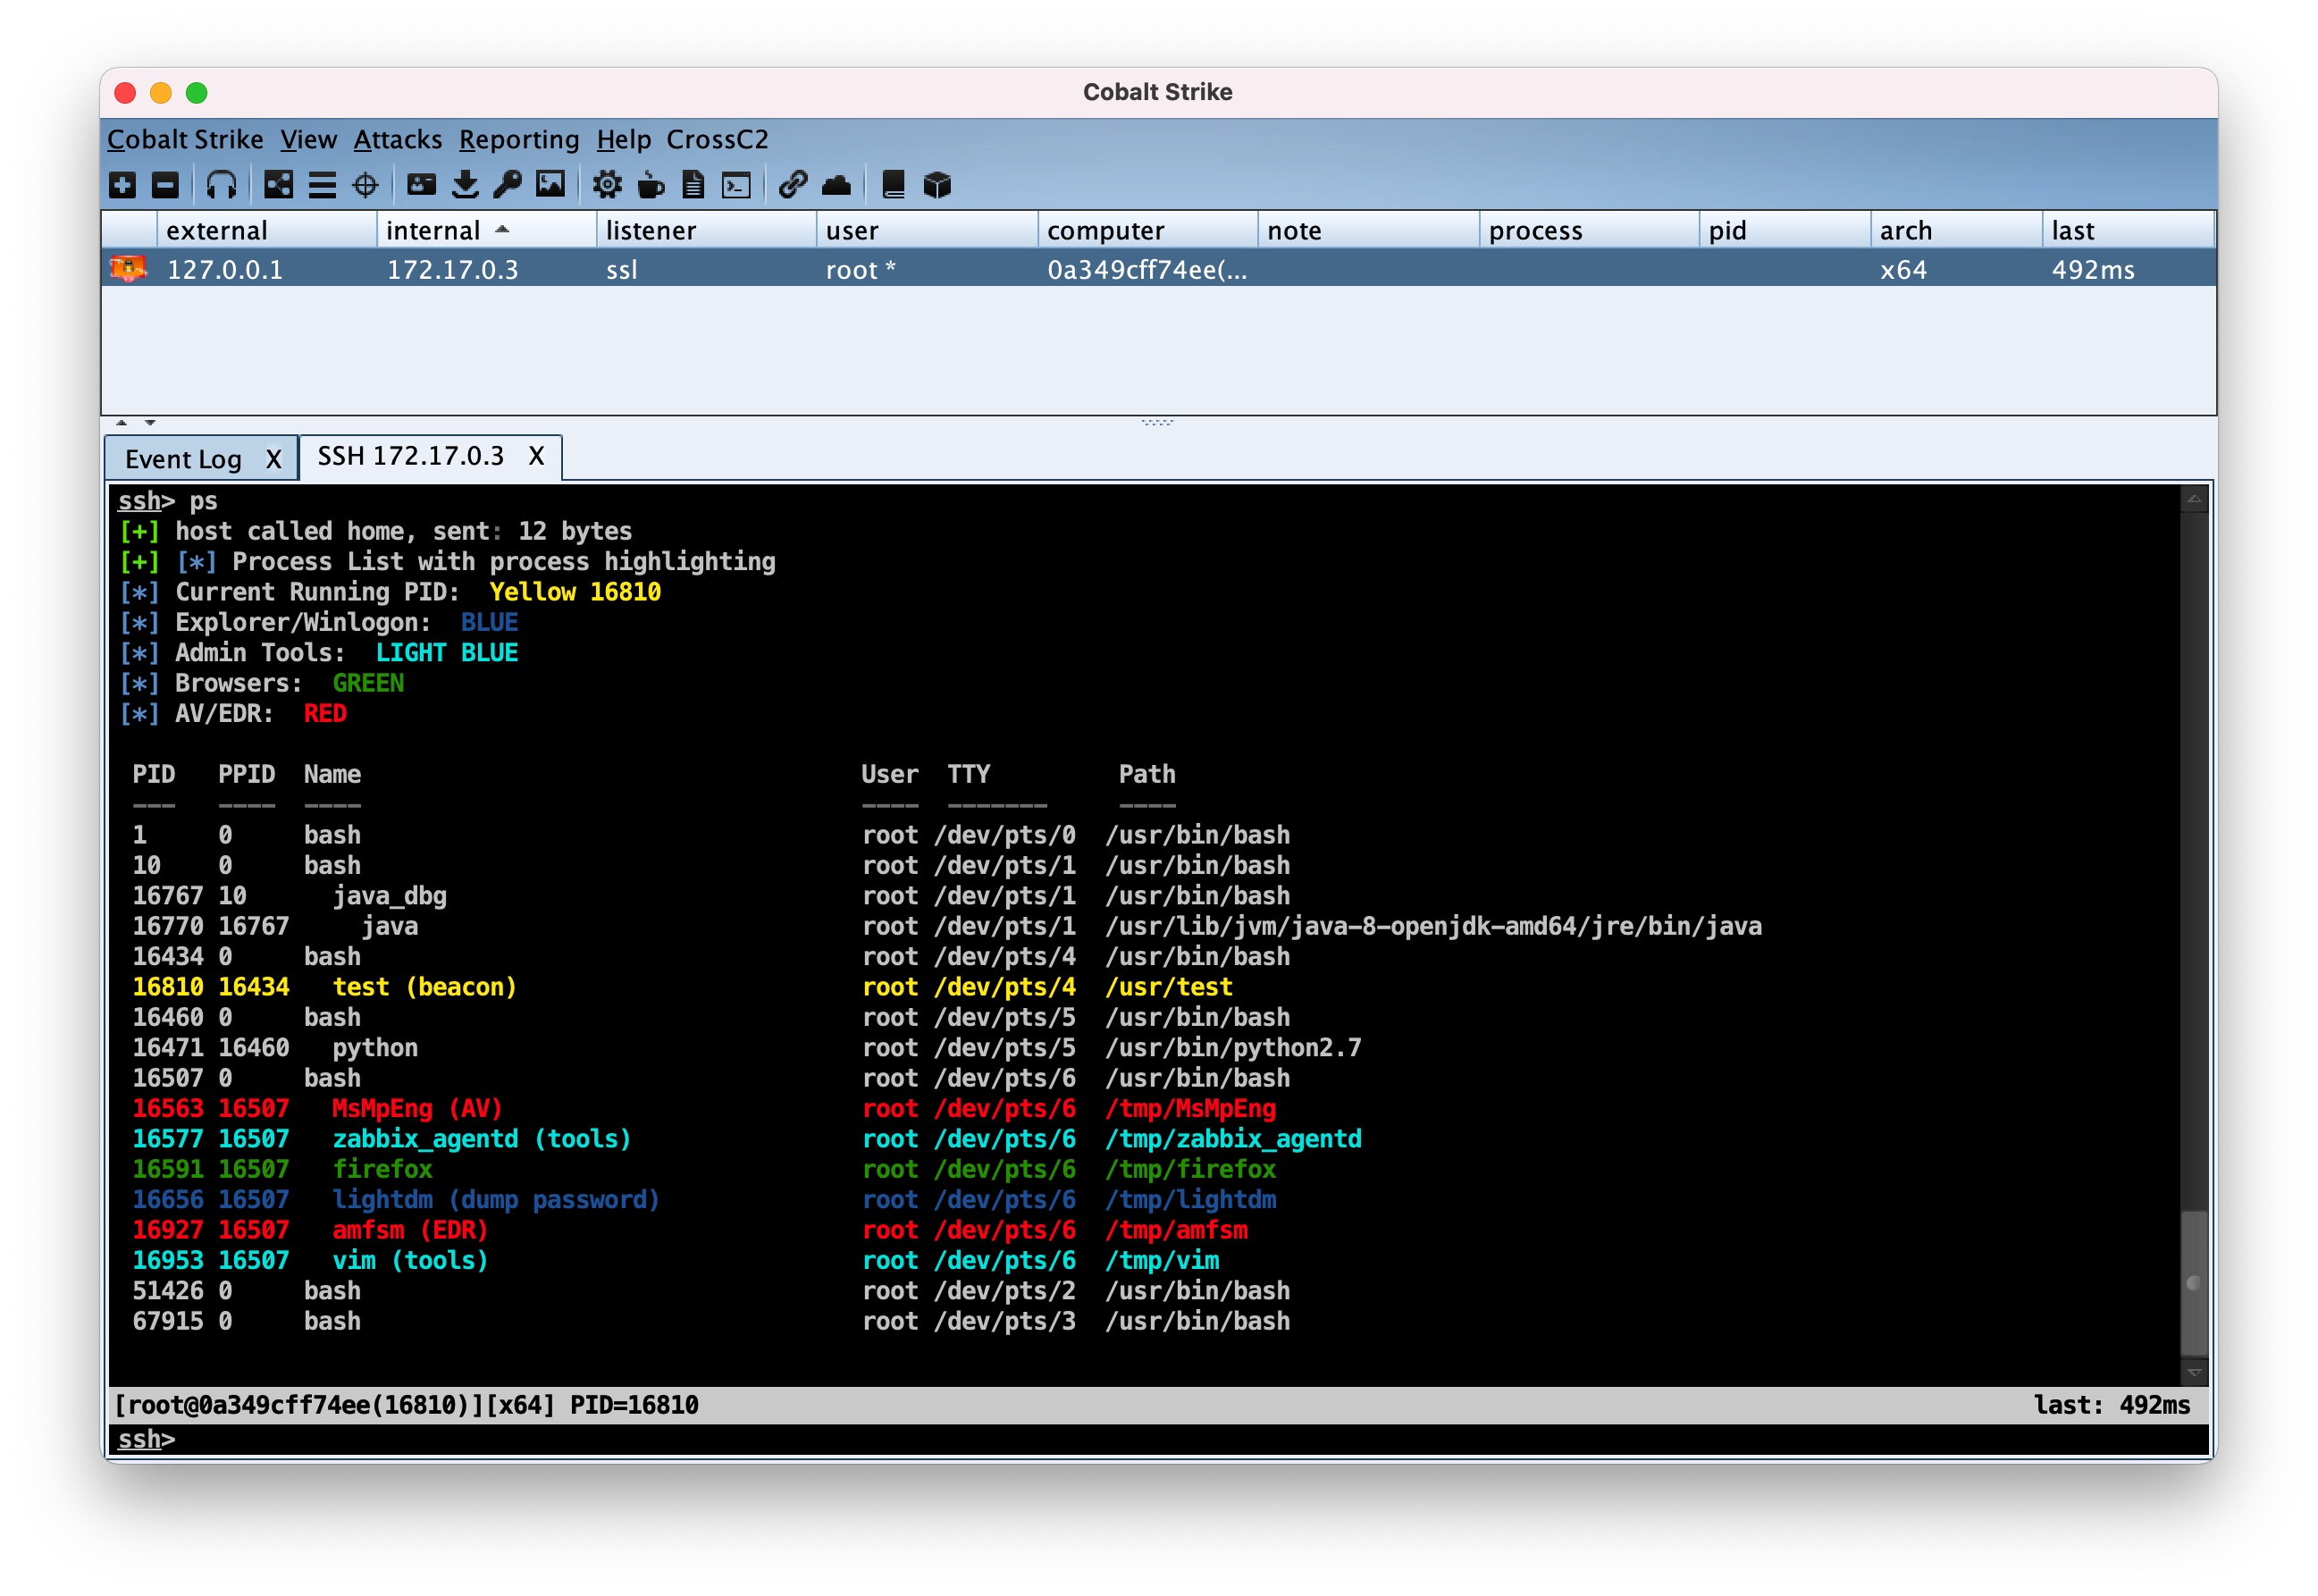 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
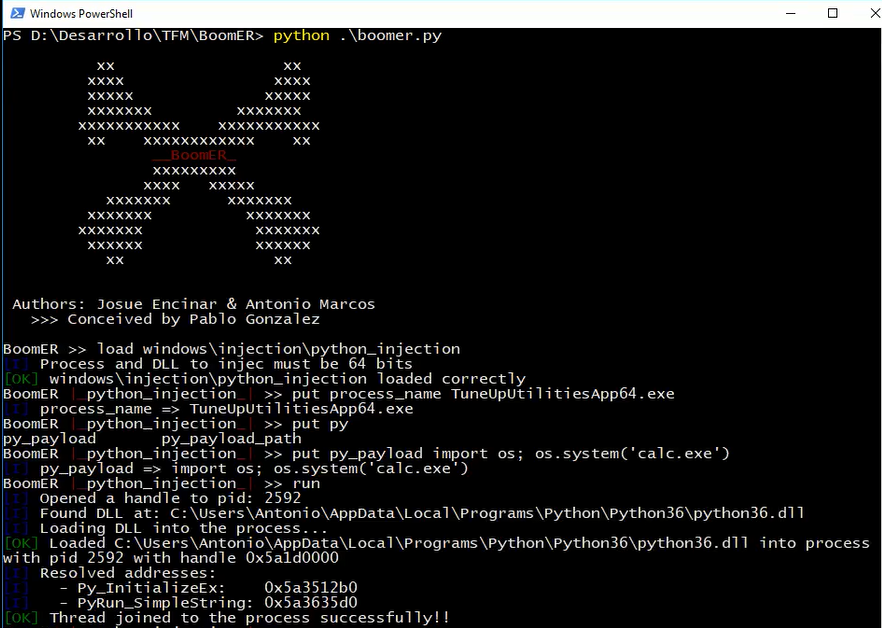 josue87/boomer
Framework for exploiting local vulnerabilities
 vinukalana/dirtypipe-cve-2022-0847
This repository is developed to analysis and understand DirtyPipe exploit CVE-2022-0847
 watchtowrlabs/connectwise-screenconnect_auth-bypass-add-user-poc
Proof-of-concept exploit for authentication bypass in ConnectWise ScreenConnect, enabling addition of administrative user as first step to Remote…