
SkyArk
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
cloud-securityidentity-access-managementinformation-gathering+3
9101 year ago
cyberark/skyarkSkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 0x4d31/honeybits
A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
 rhinosecuritylabs/gcpbucketbrute
A script to enumerate Google Storage buckets, determine what access you have to them, and determine if they can be privilege escalated.
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
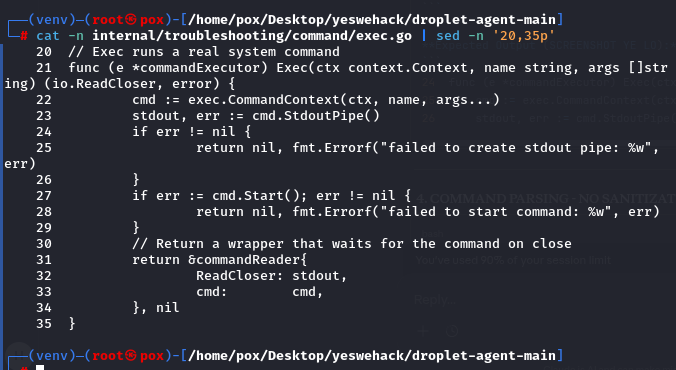 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 dagrz/aws_pwn
A collection of AWS penetration testing junk
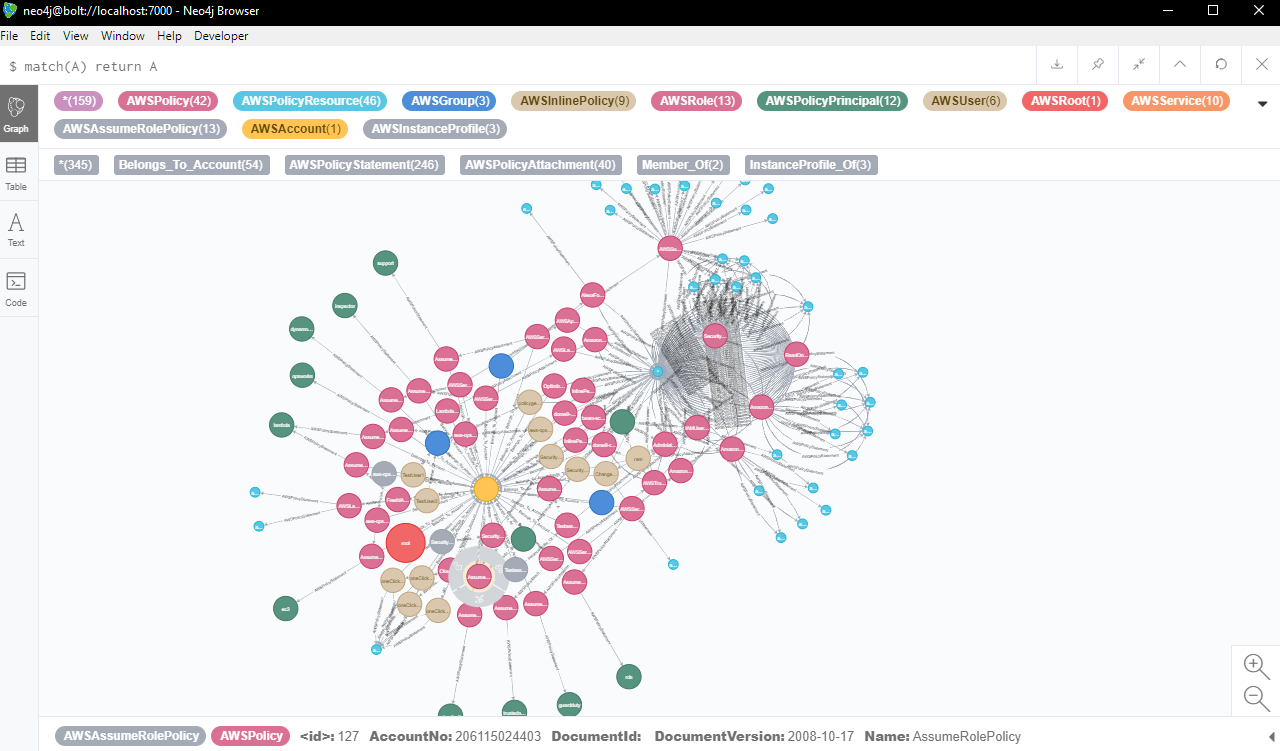 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 rhinosecuritylabs/iamactionhunter
An AWS IAM policy statement parser and query tool.
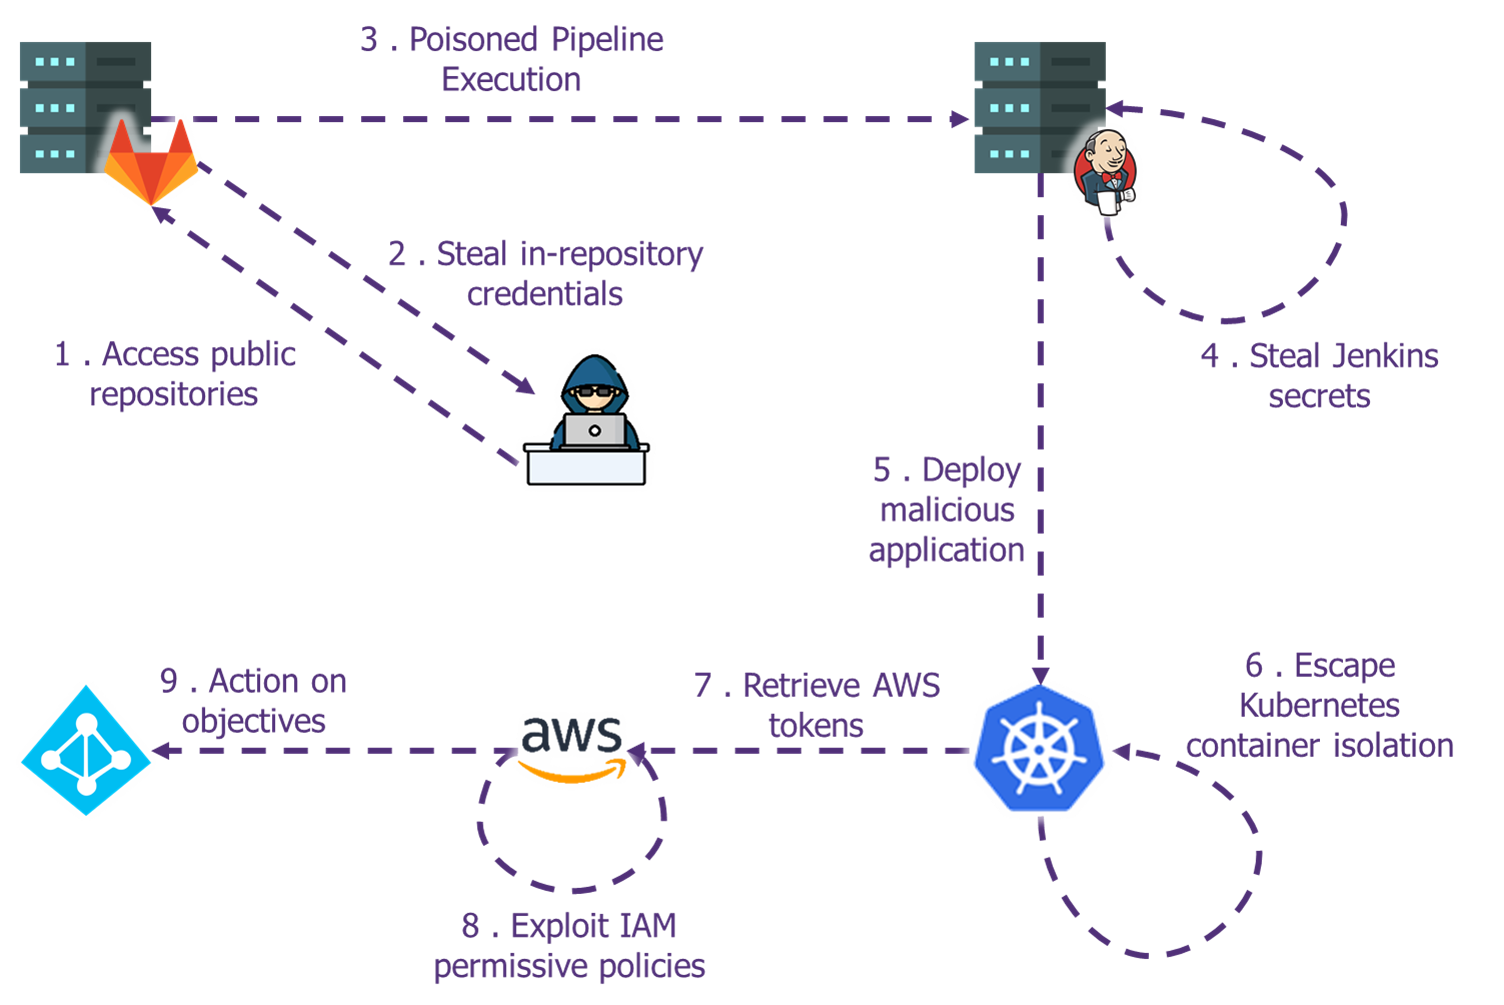 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…