

Windows-11-24h2-Kernel-Exploit
 enessakircolak/windows-11-24h2-kernel-exploit
Windows 11 24h2 LPE Kernel Exploitation. CVE-2020-12446(eneio64.sys)
binary-exploitationexploitationprivilege-escalation+1
6
enessakircolak/windows-11-24h2-kernel-exploitWindows 11 24h2 LPE Kernel Exploitation. CVE-2020-12446(eneio64.sys)

 nanabingies/driver-rw
Page Table Manipulation -- CVE-2018-19321
 sfrdevelopment/windows-smb-vulnerability-framework-cve-2025-33073
Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…
 f4t1h21/cve-2021-3560-polkit-dbus
f4T1H's PoC script for CVE-2021-3560 Polkit D-Bus Privilege Escalation
 jndok/tpwn-bis
simple poc for cve-2015-5932 / cve-2015-5847 / cve-2015-5864
 d0rb/cve-2023-42931
The exploit targets a critical privilege escalation vulnerability in macOS versions Monterey, Ventura, and Sonoma.
 r0binak/cve-2024-0132
CVE-2024-0132 – Fully Weaponized NVIDIA Container Toolkit Exploit
 m4fiab0y/cve-2023-22809
Local privilege escalation exploit for sudo 1.8.0-1.9.12p1 via sudoedit, allowing attackers to gain root shell by manipulating the sudoers file.
 waterrr/nopac
Exploiting CVE-2021-42278 and CVE-2021-42287
 quaerendir/cve-2026-46331-audit
cve-2026-46331-audit script
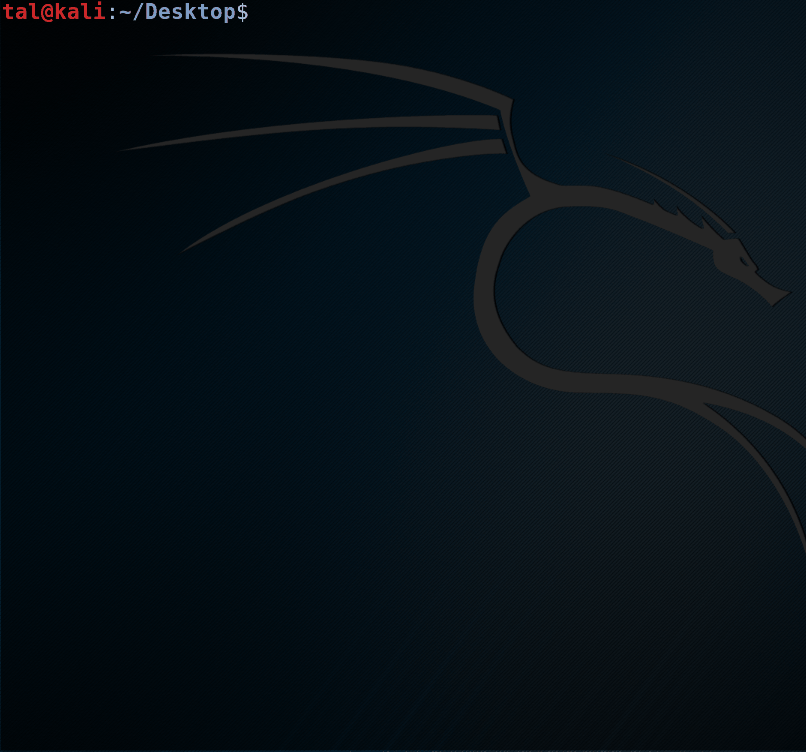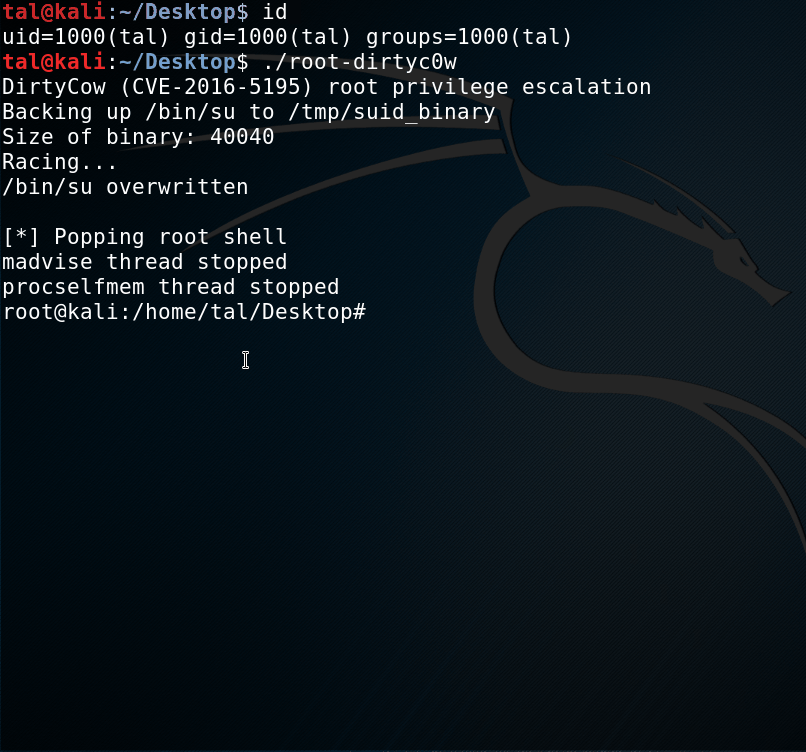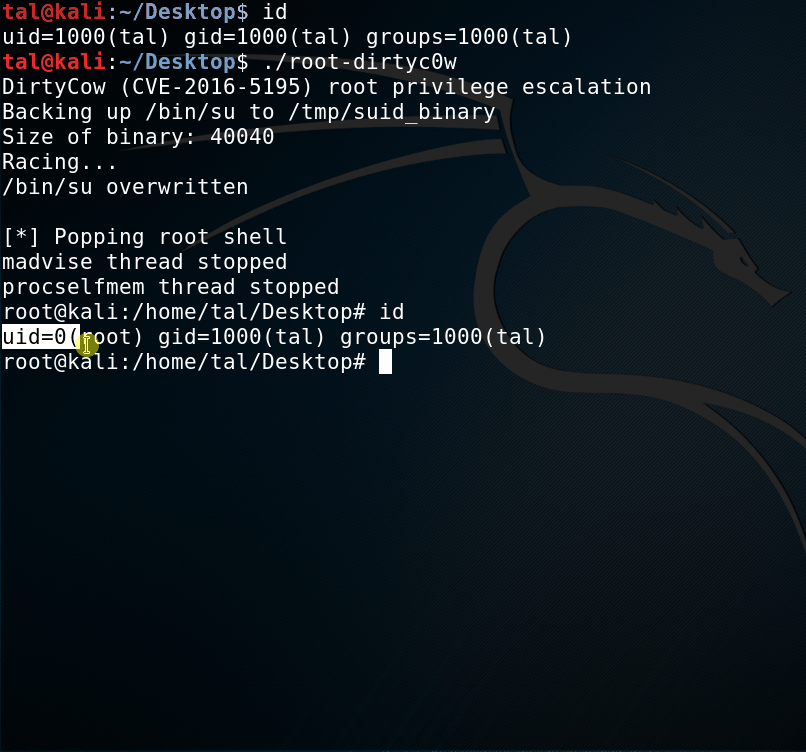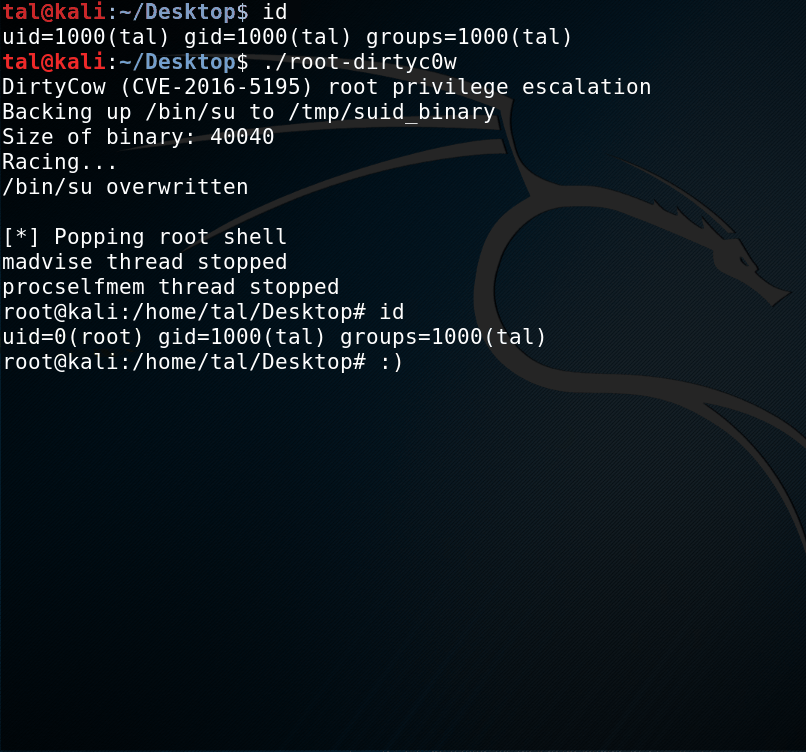 talsim/root-dirtyc0w
DirtyCow root privilege escalation (CVE-2016-5195)
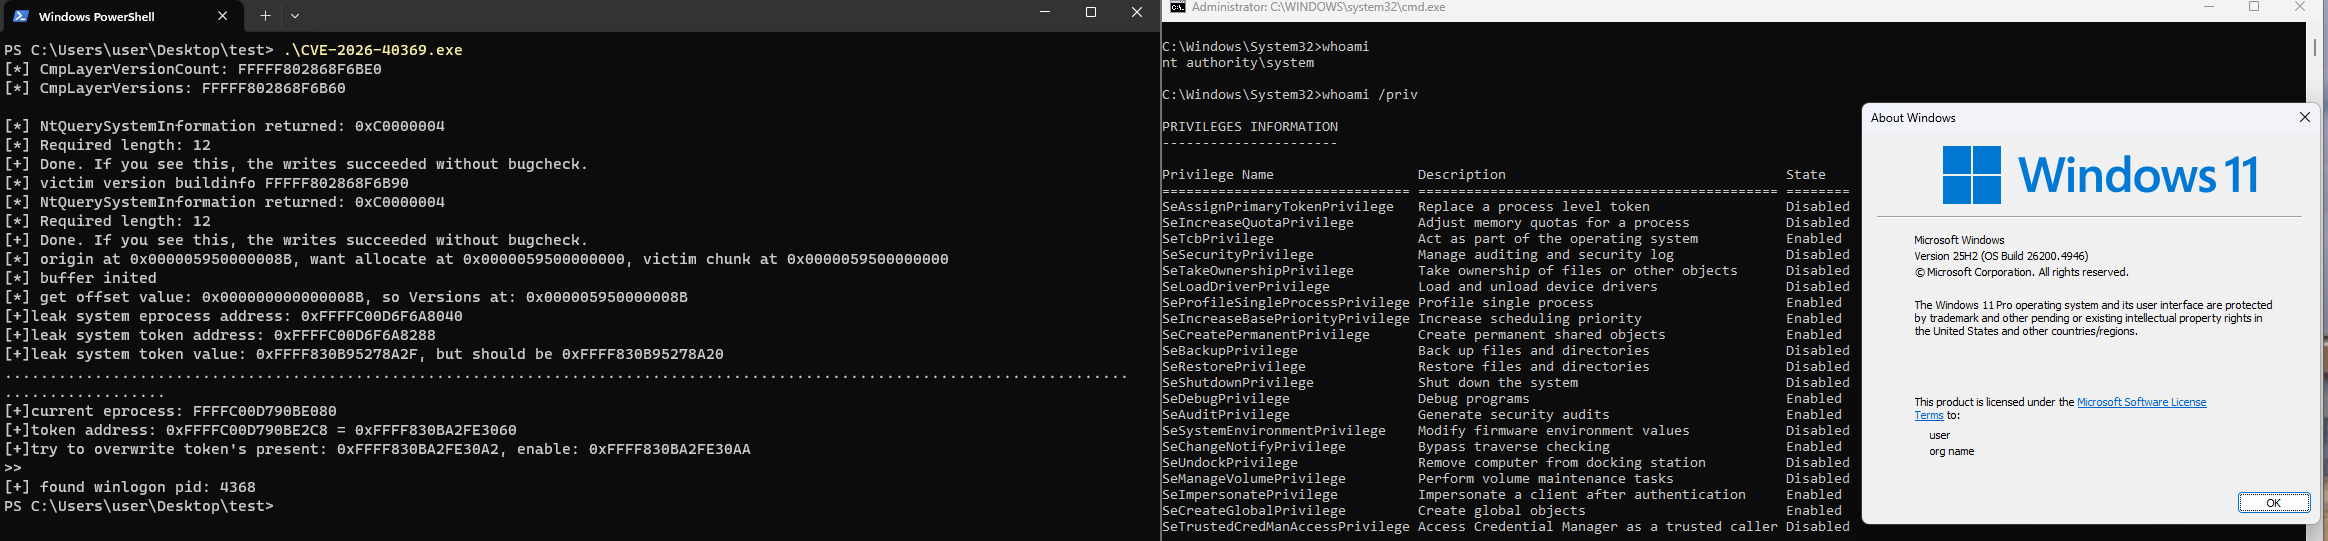 joe1sn/cve_2026_40369
Exploit PoC for CVE-2026-40369 targeting Windows kernel; includes kASLR bypass, heap grooming, remote thread injection, and per-build offsets.
 3ndg4me/liferay-xss-7.2.1ga2-poc-report-cve-2020-7934
Authenticated Stored XSS in LifeRay 7.2.0 GA1 via MyAccountPortlet executed by Search Results
 mhackiori/cve-2021-3156
Visualization, Fuzzing, Exploit and Patch of Baron Samedit Vulnerability
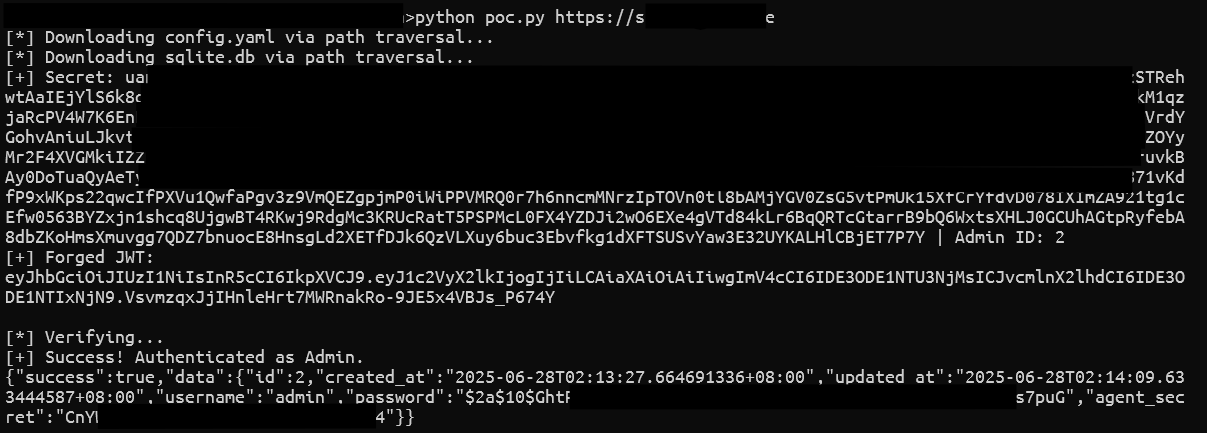 tar-xz/cve-2026-53519-poc
PoC exploit for CVE-2026-53519.
 randomrobbiebf/cve-2024-49328
WP REST API FNS <= 1.0.0 - Privilege Escalation
 le1a/cve-2023-22515
Confluence Data Center & Server 权限提升漏洞 Exploit